

traitor
 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
container-escapeexploitationpenetration-testing+4
7.2k
liamg/traitor:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
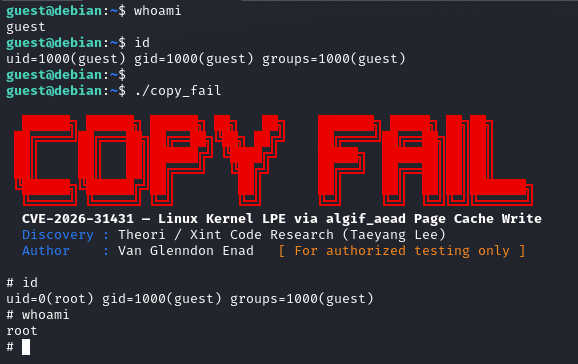 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 sgkdev/page_inject
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
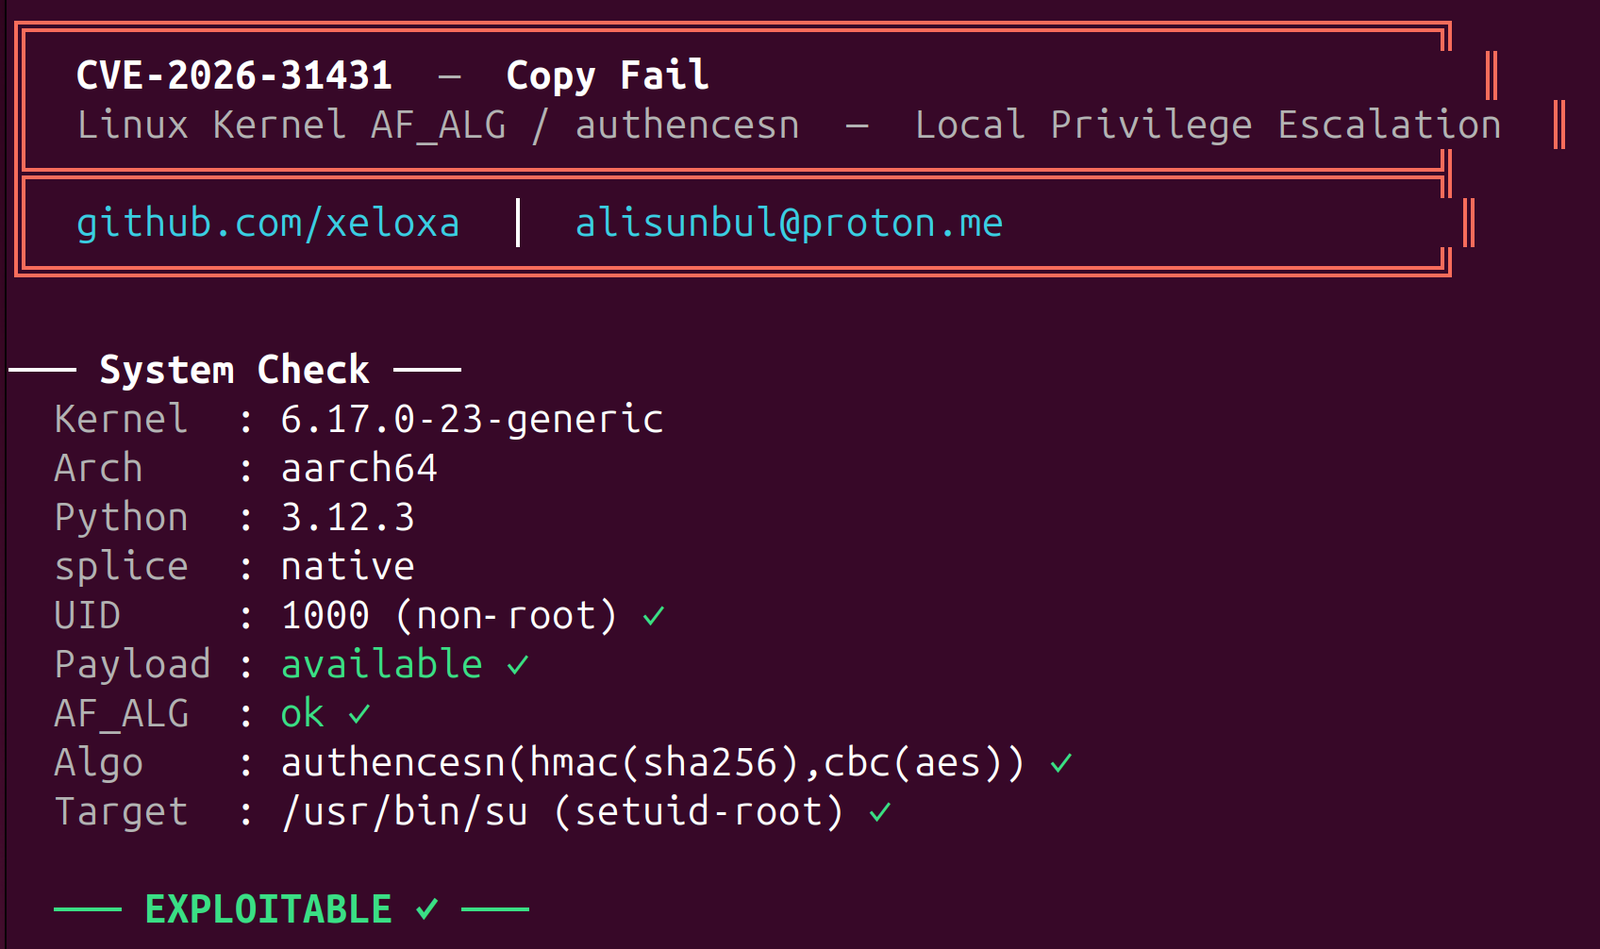 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 0xfuffm3/cve-2026-31431-copyfail
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP