

traitor
 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
container-escapeexploitationpenetration-testing+4
7.2k
liamg/traitor:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 cyberark/pipeviewer
A tool that shows detailed information about named pipes in Windows
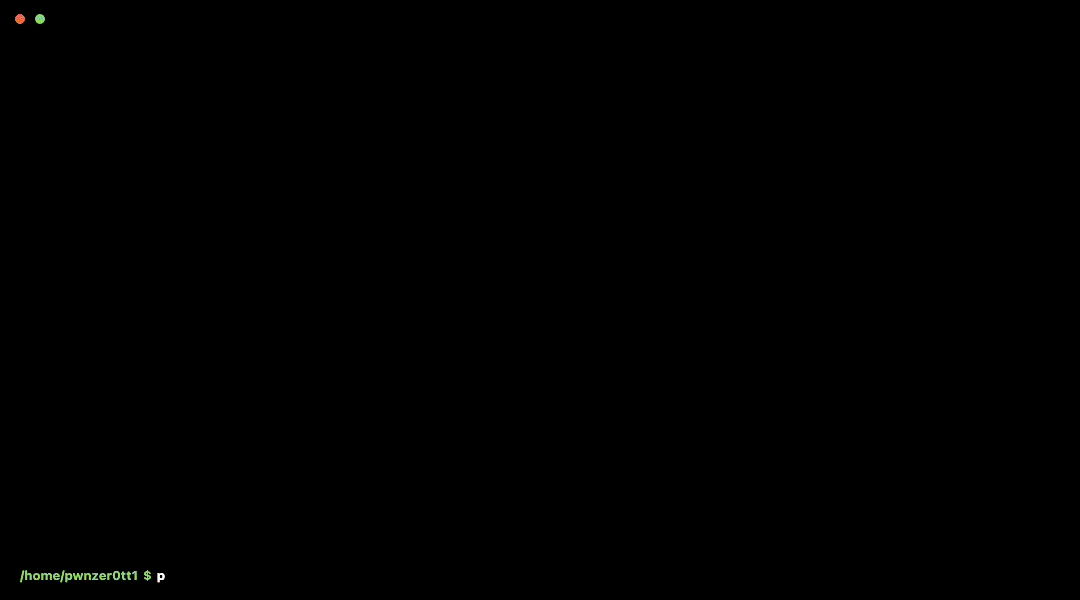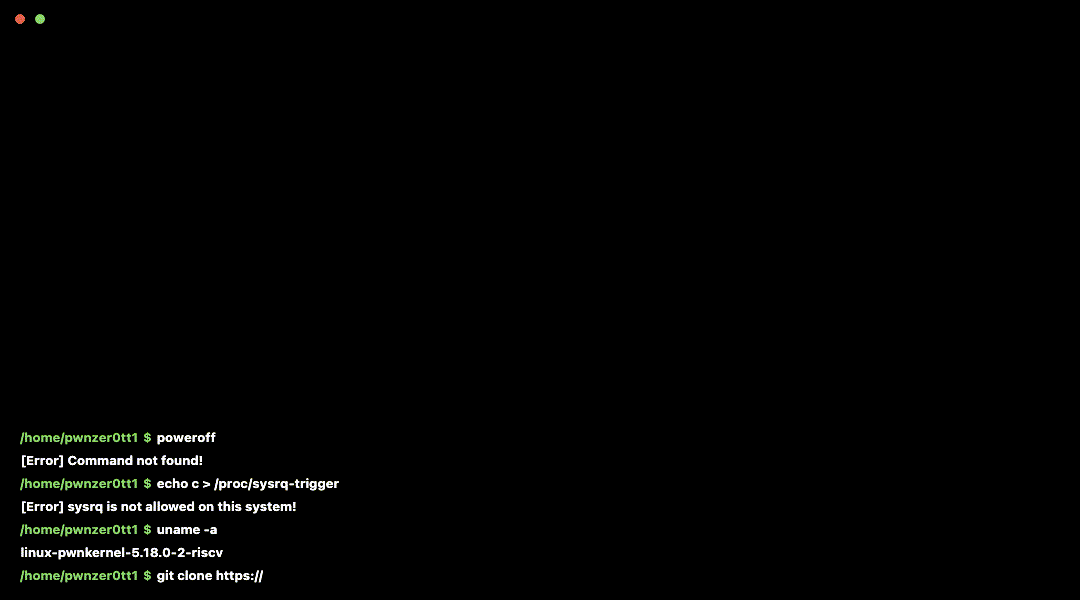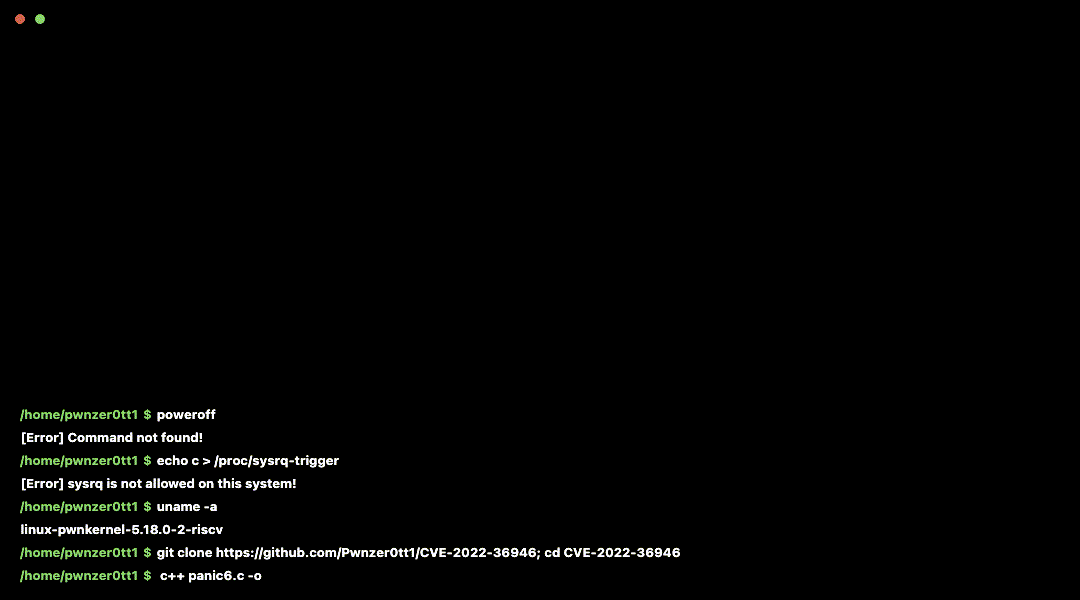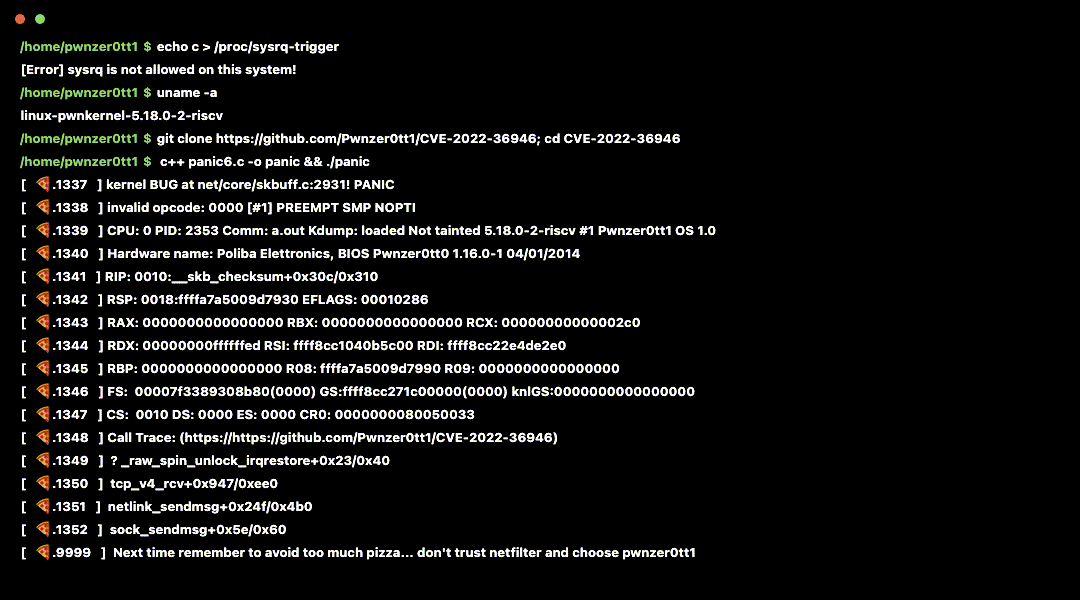 pwnzer0tt1/cve-2022-36946
CVE-2022-36946 linux kernel panic in netfilter_queue
 jlsakuya/cve-2022-0847-container-escape
A simple exploit that uses dirtypipe to inject shellcode into runC entrypoint to implement container escapes.
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit
 mindasy/cve-2025-23266-migration-bypass
cve-2025-23266-migration-bypass
 gmeghnag/test-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 demonstrating container escape and privilege escalation in OpenShift environments.