
React2Shell
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
command-and-controlcontainer-escapedata-exfiltration+7
4nuxd/react2shellR2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
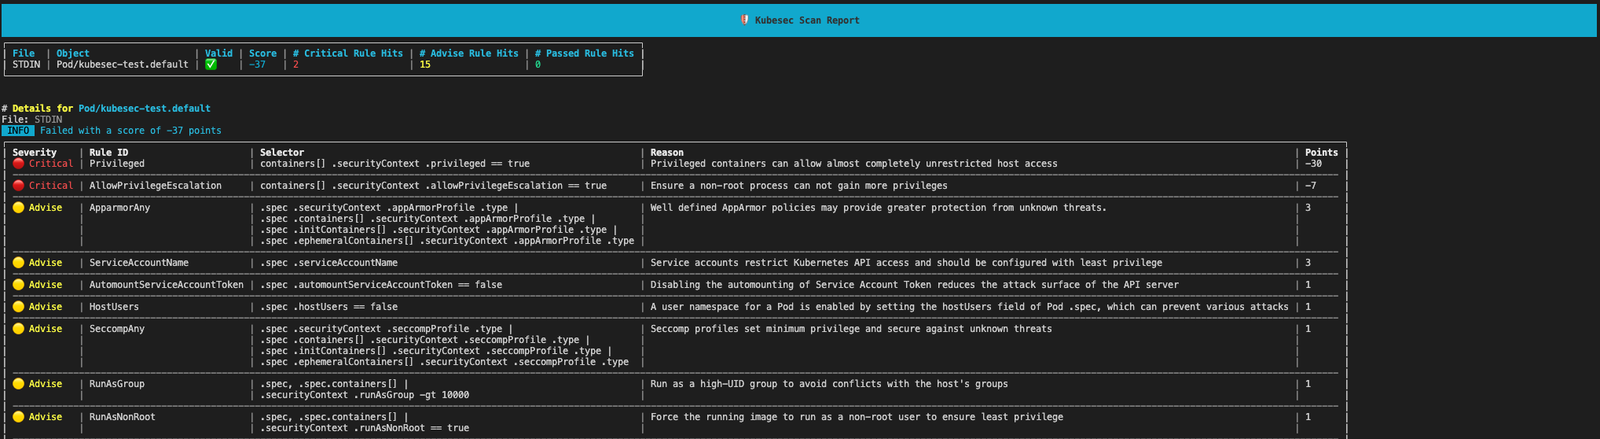 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 hackspeak/cve-2026-17106
PoC for Docker `docker cp` arbitrary file write, exploiting symlink and tar extraction flaws to overwrite host binaries or launch agents for…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 0xfuffm3/cve-2026-31431-copyfail
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…
 nicetop1027/cve-2026-d0cker
Proof-of-concept exploit for critical runC container escape vulnerability (CVE-2026-Pending) with symlink race condition, including Go PoC, analysis,…
 rubby2001/cve-2025-1974-go
Exploit CVE-2025-1974 with a single file.
 zpxlz/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…
 wenura17125/cve-2025-49131-poc
Proof-of-concept exploit for CVE-2025-49131, a sandbox escape in FastGPT allowing arbitrary file read/write, import bypass, and remote code execution…
 george0papasotiriou/cve-2026-5555-container-escape-via-proc-self-fd-symlink-in-shared-volume
Proof-of-concept exploit for CVE-2026-5555, demonstrating container escape via /proc/self/fd symlink in rshared volumes to overwrite host files and…
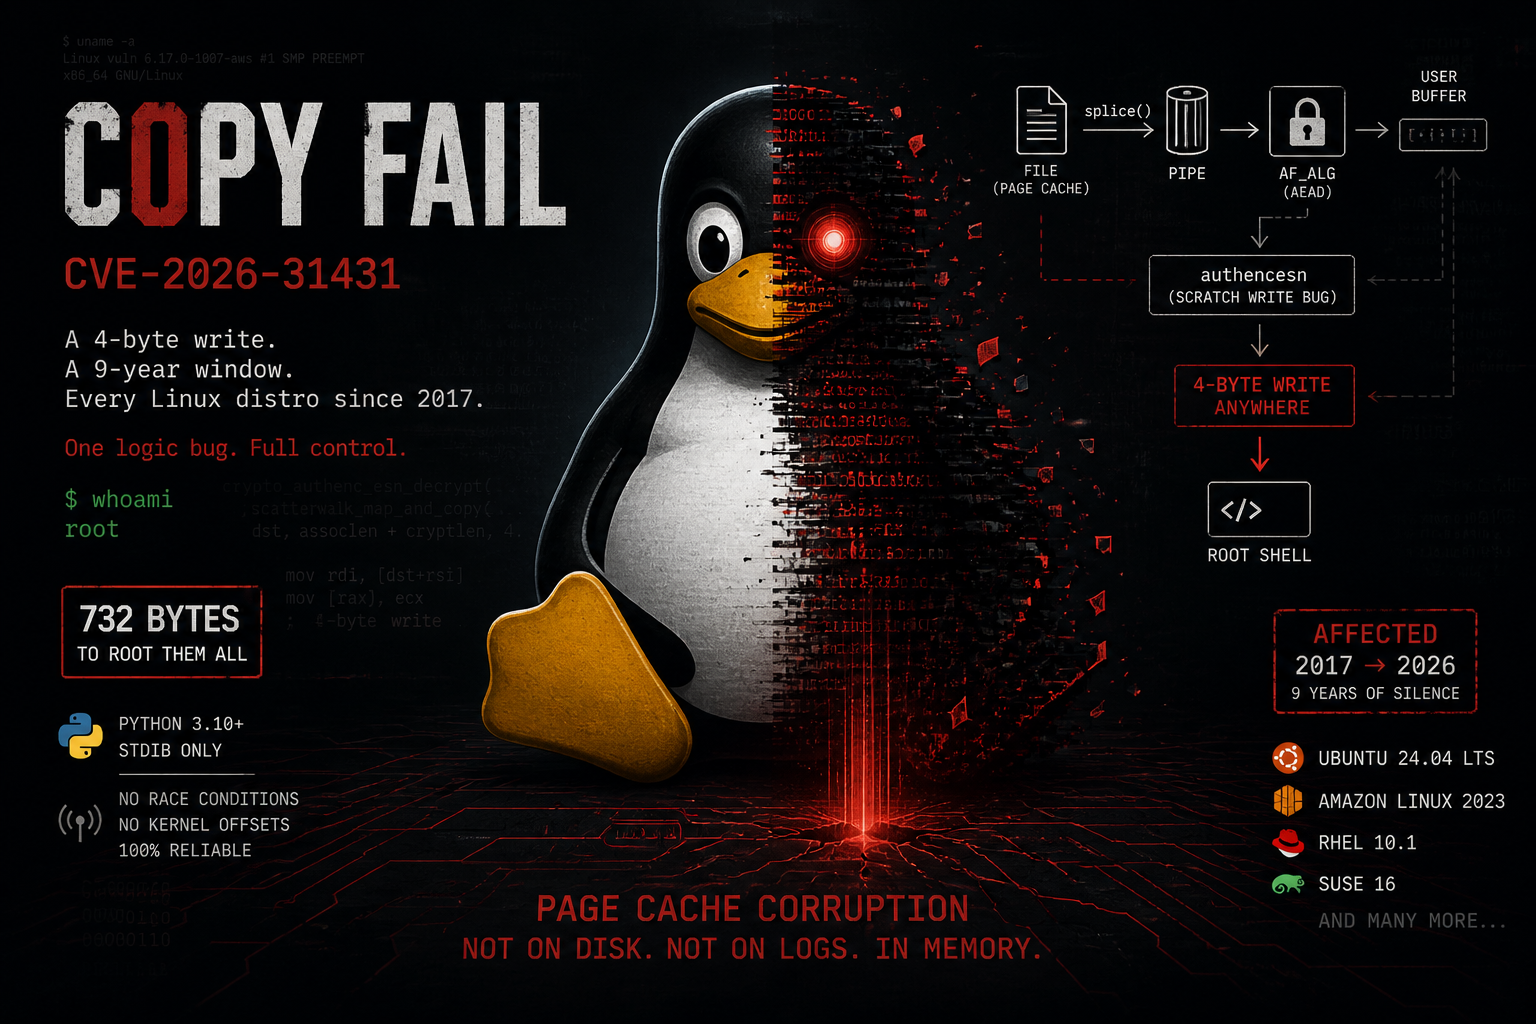 themalwareguardian/cve-2026-31431
A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…
 skysbsb/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in Docker/runc. Demonstrates file descriptor manipulation to break out…
 ssst0n3/docker-cve-2022-39253-poc
Proof-of-concept exploit for CVE-2022-39253 demonstrating Docker container escape via malicious Git repository build, enabling host file system read…
 zhangguanzhang/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626, a runc container escape vulnerability allowing host file system access via crafted working directory in…
 davidrxchester/cve-2026-5843
Docker Container Escape POC via mlx-metal importlib