
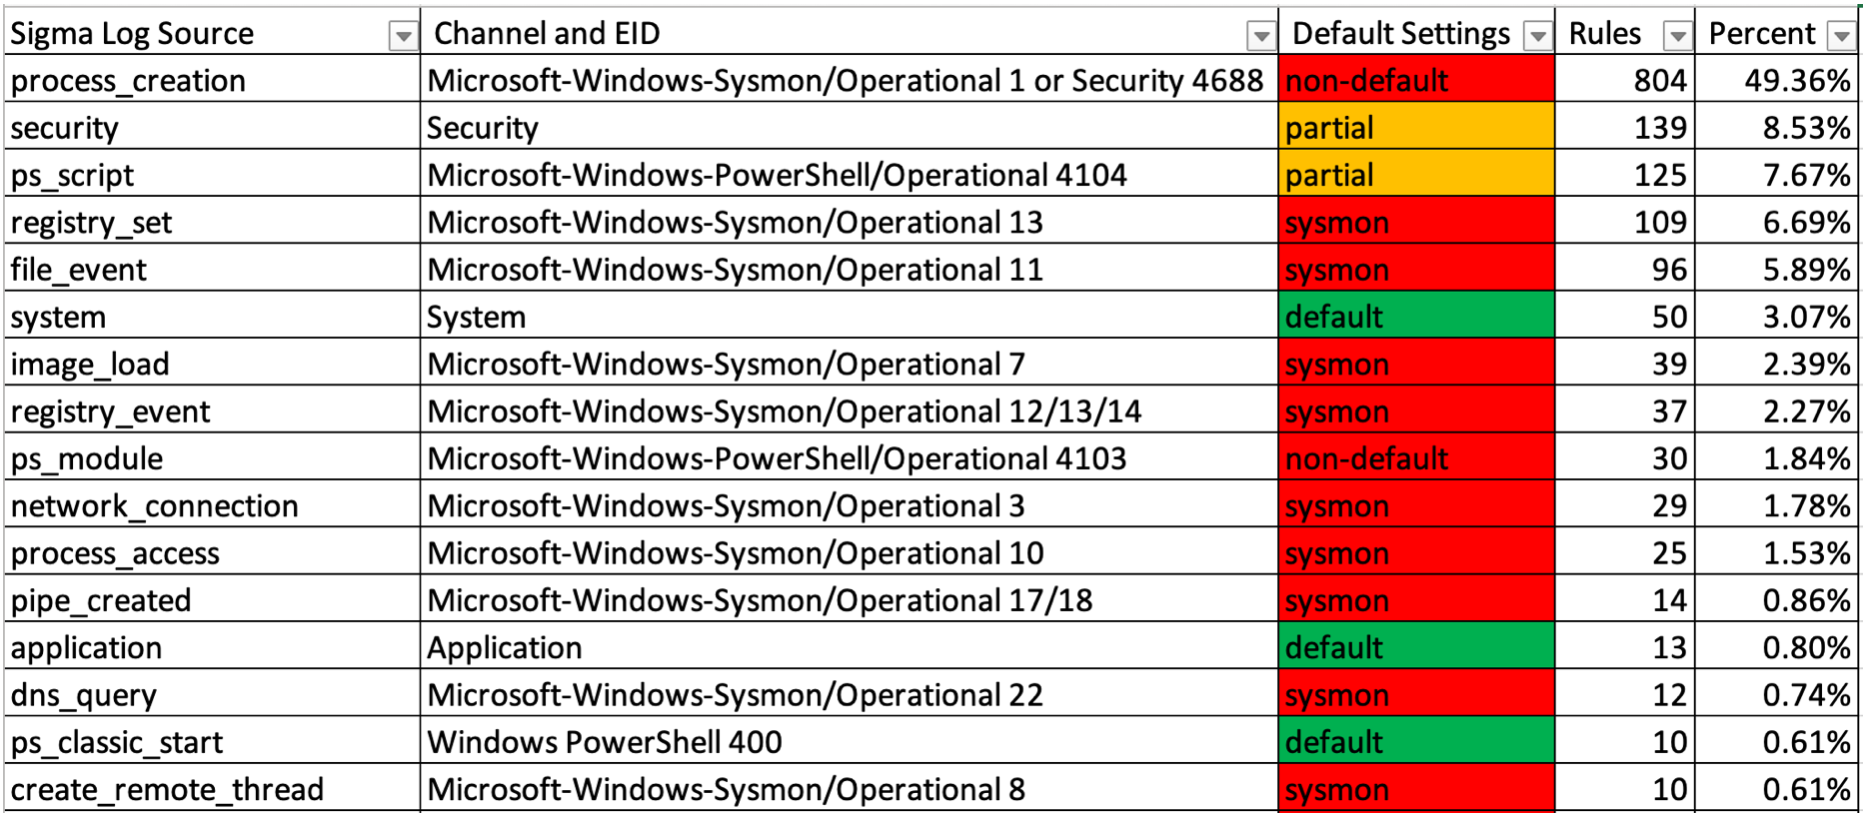
EnableWindowsLogSettings
 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
configuration-auditingdefensive-toolsdigital-forensics+3
723
yamato-security/enablewindowslogsettingsDocumentation and scripts to properly enable Windows event logs.
 metablaster/windowsfirewallruleset
PowerShell scripts to automatically create rules for Windows firewall
 boostedchaos/fleet-cve-scanner
An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…
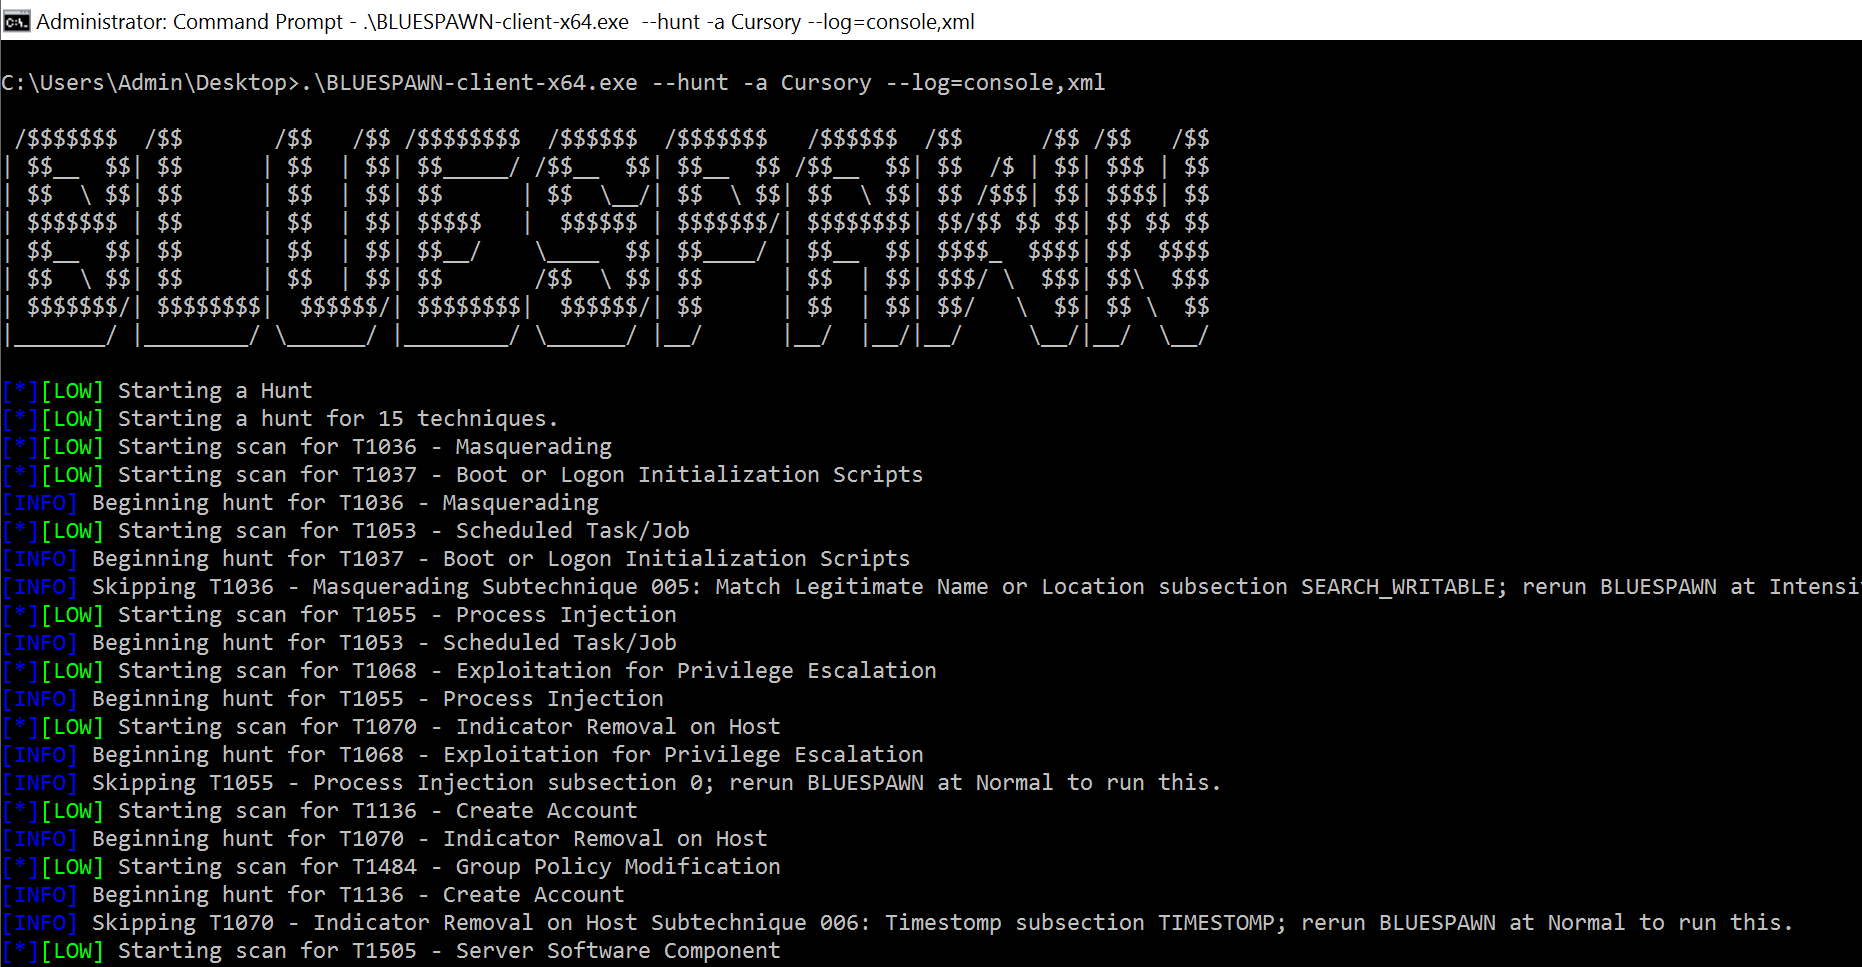 ion28/bluespawn
An Active Defense and EDR software to empower Blue Teams
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 zenzue/cve-2025-50154
PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…
 espressocake/defender_exclusions-bof
A BOF to determine Windows Defender exclusions.
 yamato-security/wela
Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
 avwolferen/sitecore.solr-log4j-mitigation
This repository contains a script that you can run on your (windows) machine to mitigate CVE-2021-44228
 sabecomoeh/cve-2022-0001
This script checks for Administrator privileges and then sets the necessary DWord values in the Windows registry to enable the hardware-level…
 markuszehnle/cve-2020-0601
PowerShell script to check Windows hotfix status for CVE-2020-0601 and detect exploitation attempts. Includes XML import for ControlUp Script-Based…
 tylermontneyacc/updatewindowsre-cve-2022-41099
Script to update Windows Recovery Environment to patch against CVE-2022-41099
 malindarathnayake/intel-cve-2018-3639-mitigation_registryupdate
PowerShell script to apply Windows registry mitigation for CVE-2018-3639 (Speculative Store Bypass), enabling automated security hardening against…
 blackhillsinfosec/eventlogging
Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.
 siberanka/rdp-guard
Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…
 invaderslabs/cve-2024-20666
Guide and automated PowerShell scripts to resolve CVE-2024-20666 patch failures in Windows Recovery Environment by resizing recovery partitions and…
 tomparte/printnightmare
To fight against Windows security breach PrintNightmare! (CVE-2021-34527, CVE-2021-1675)
 mckinnonit/zabbix-template-cve-2020-1472
Zabbix Template to monitor for Windows Event Viewer event's related to Netlogon Elevation of Privilege Vulnerability - CVE-2020-1472. Monitors event…