
ScoutSuite
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+5
7.8k
nccgroup/scoutsuiteMulti-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 netwrix/pingcastle
Active Directory security risk assessment tool that evaluates vulnerabilities, misconfigurations, and maturity using a streamlined methodology,…
 salesforce/cloudsplaining
Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report.
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 kubesphere/kubeeye
Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
 leo4j/invoke-adenum
Automated Active Directory auditing and enumeration tool that generates detailed HTML audit reports with CSV/XLSX export, designed for security…
 batfish/pybatfish
Python client for Batfish, a network configuration analysis tool that validates security, reliability, and compliance by modeling network behavior…
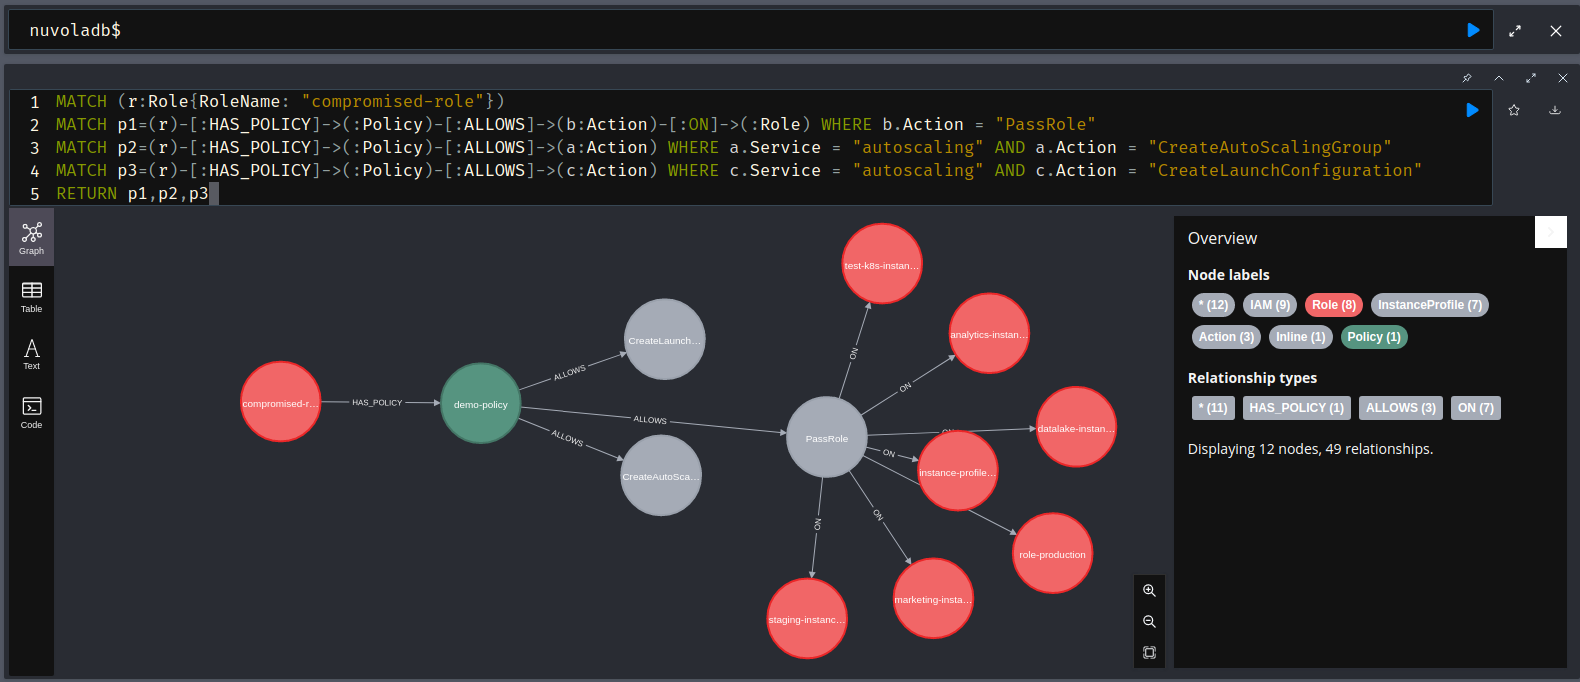 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
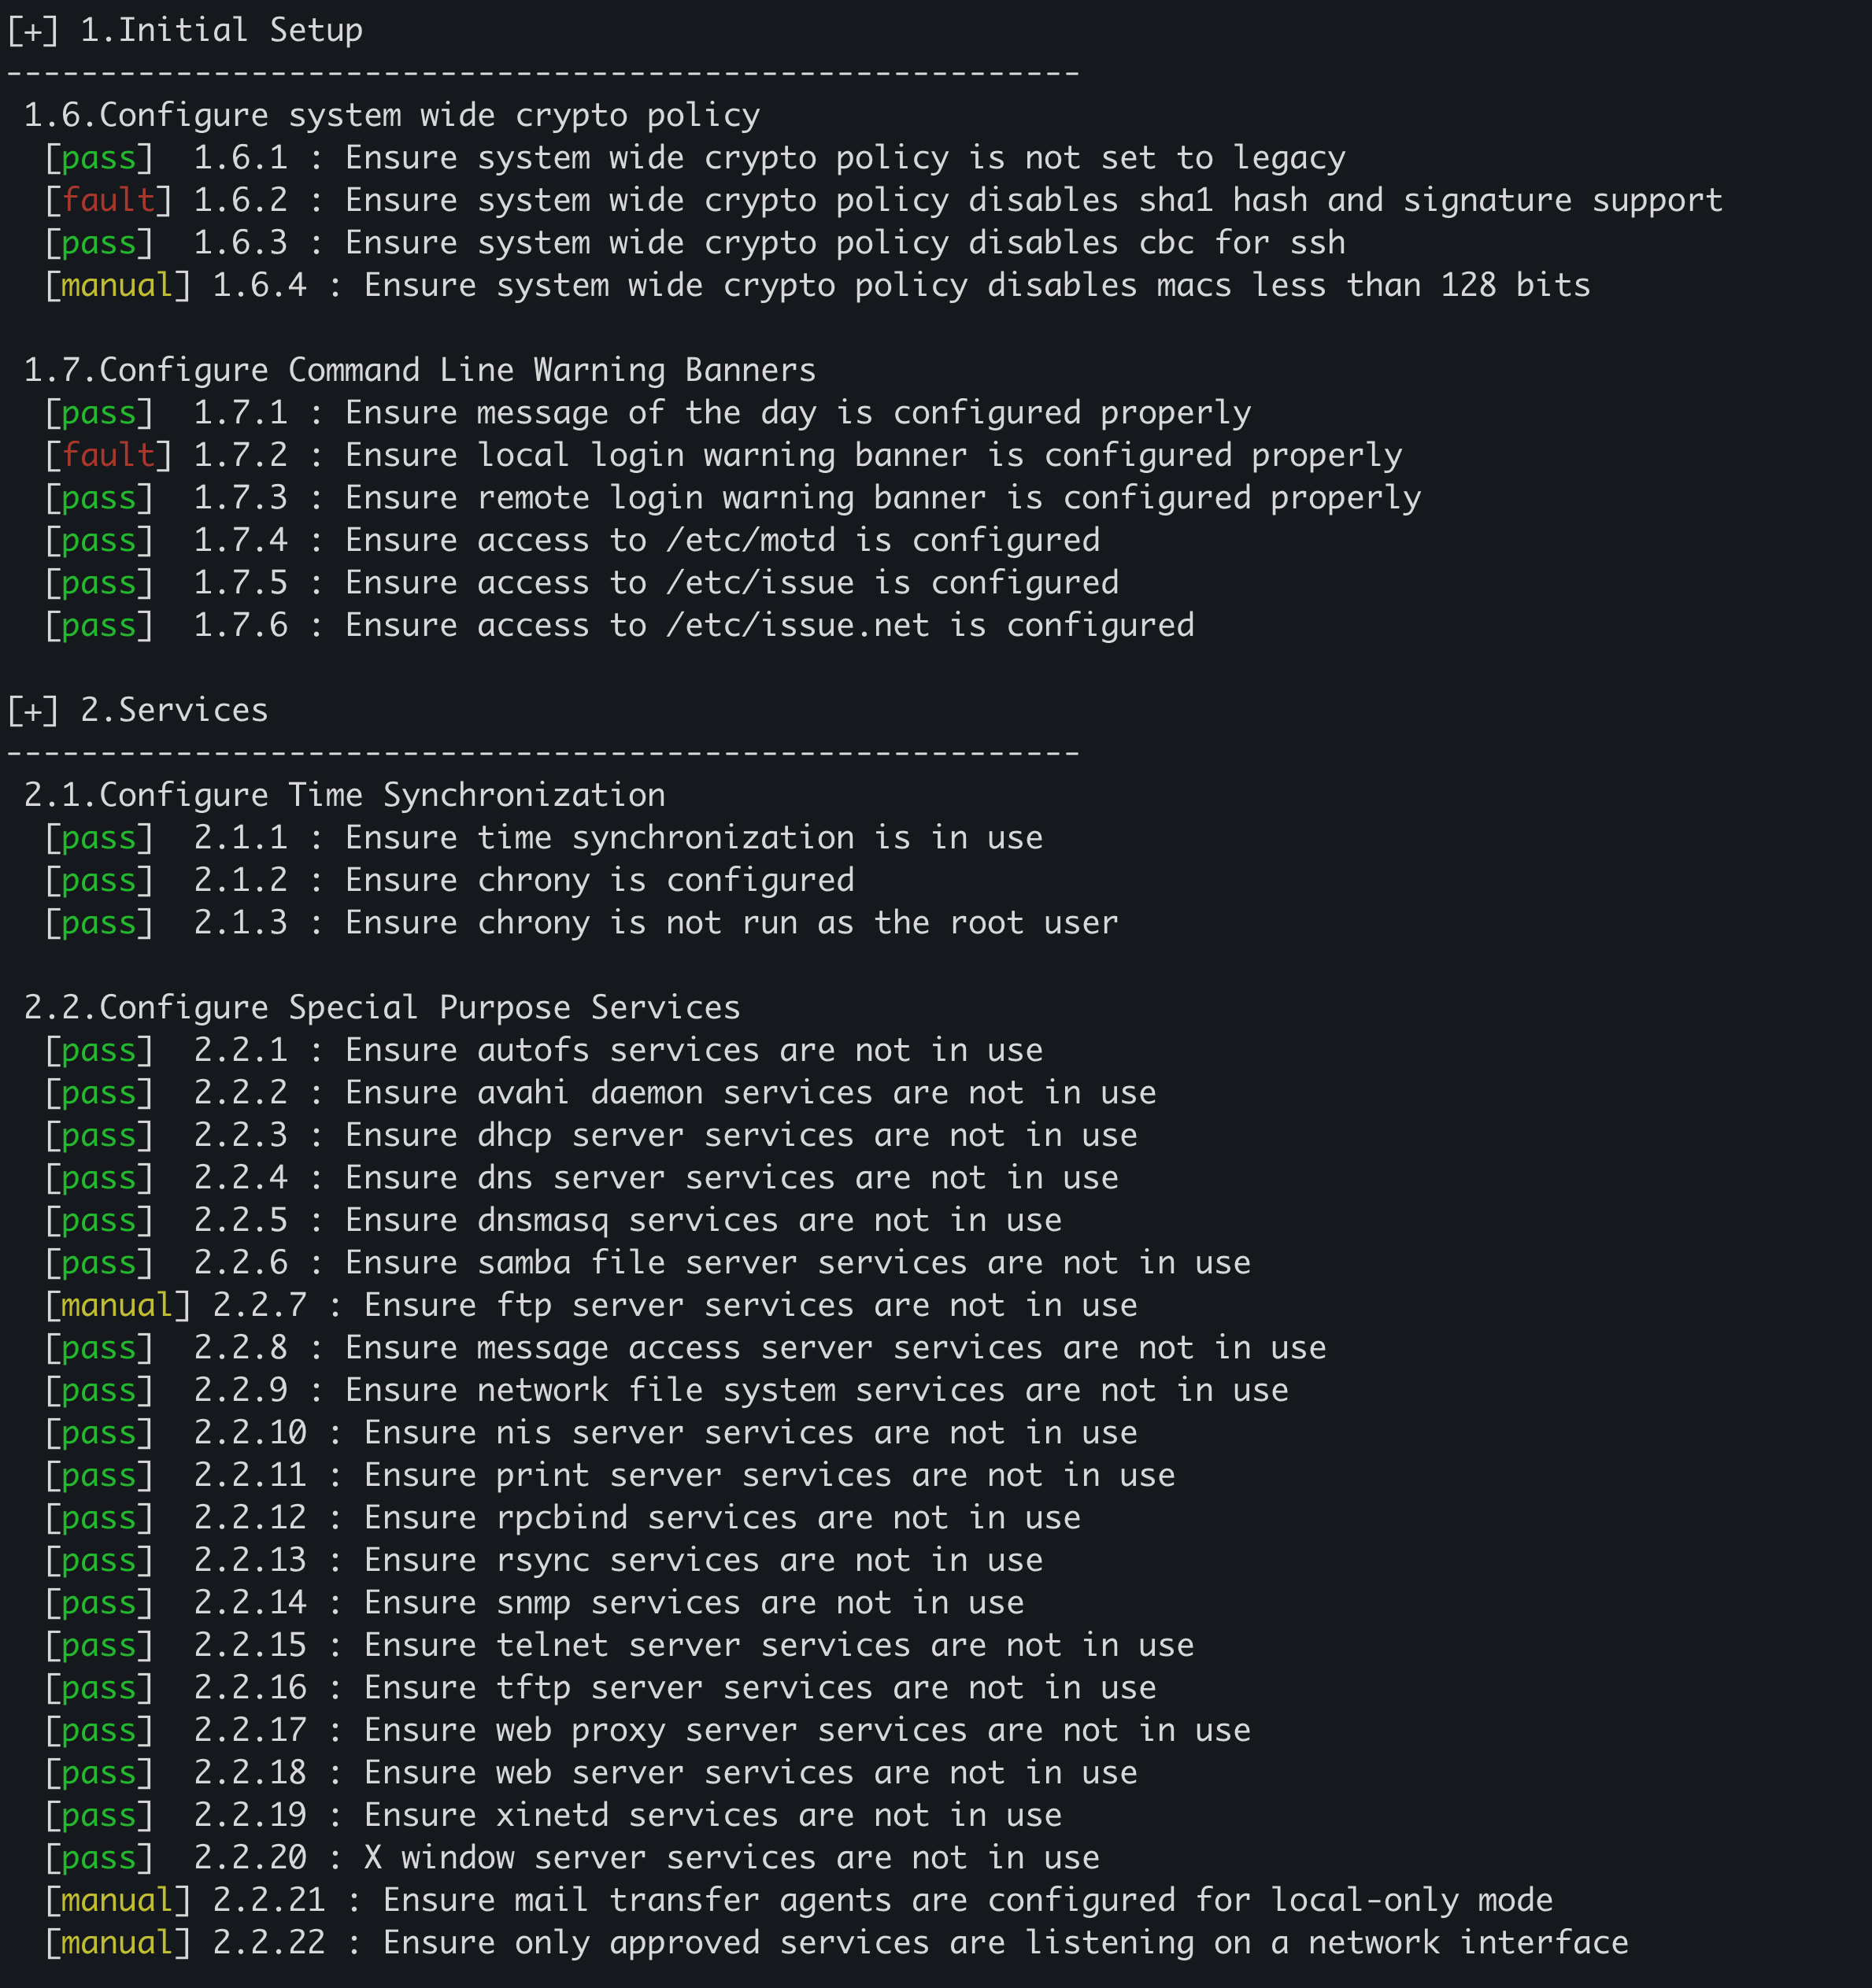 password123456/linux-security-audit
Automated Linux security auditing tool that checks 130+ CIS benchmark items for RHEL-based systems, generating detailed XML reports on system…
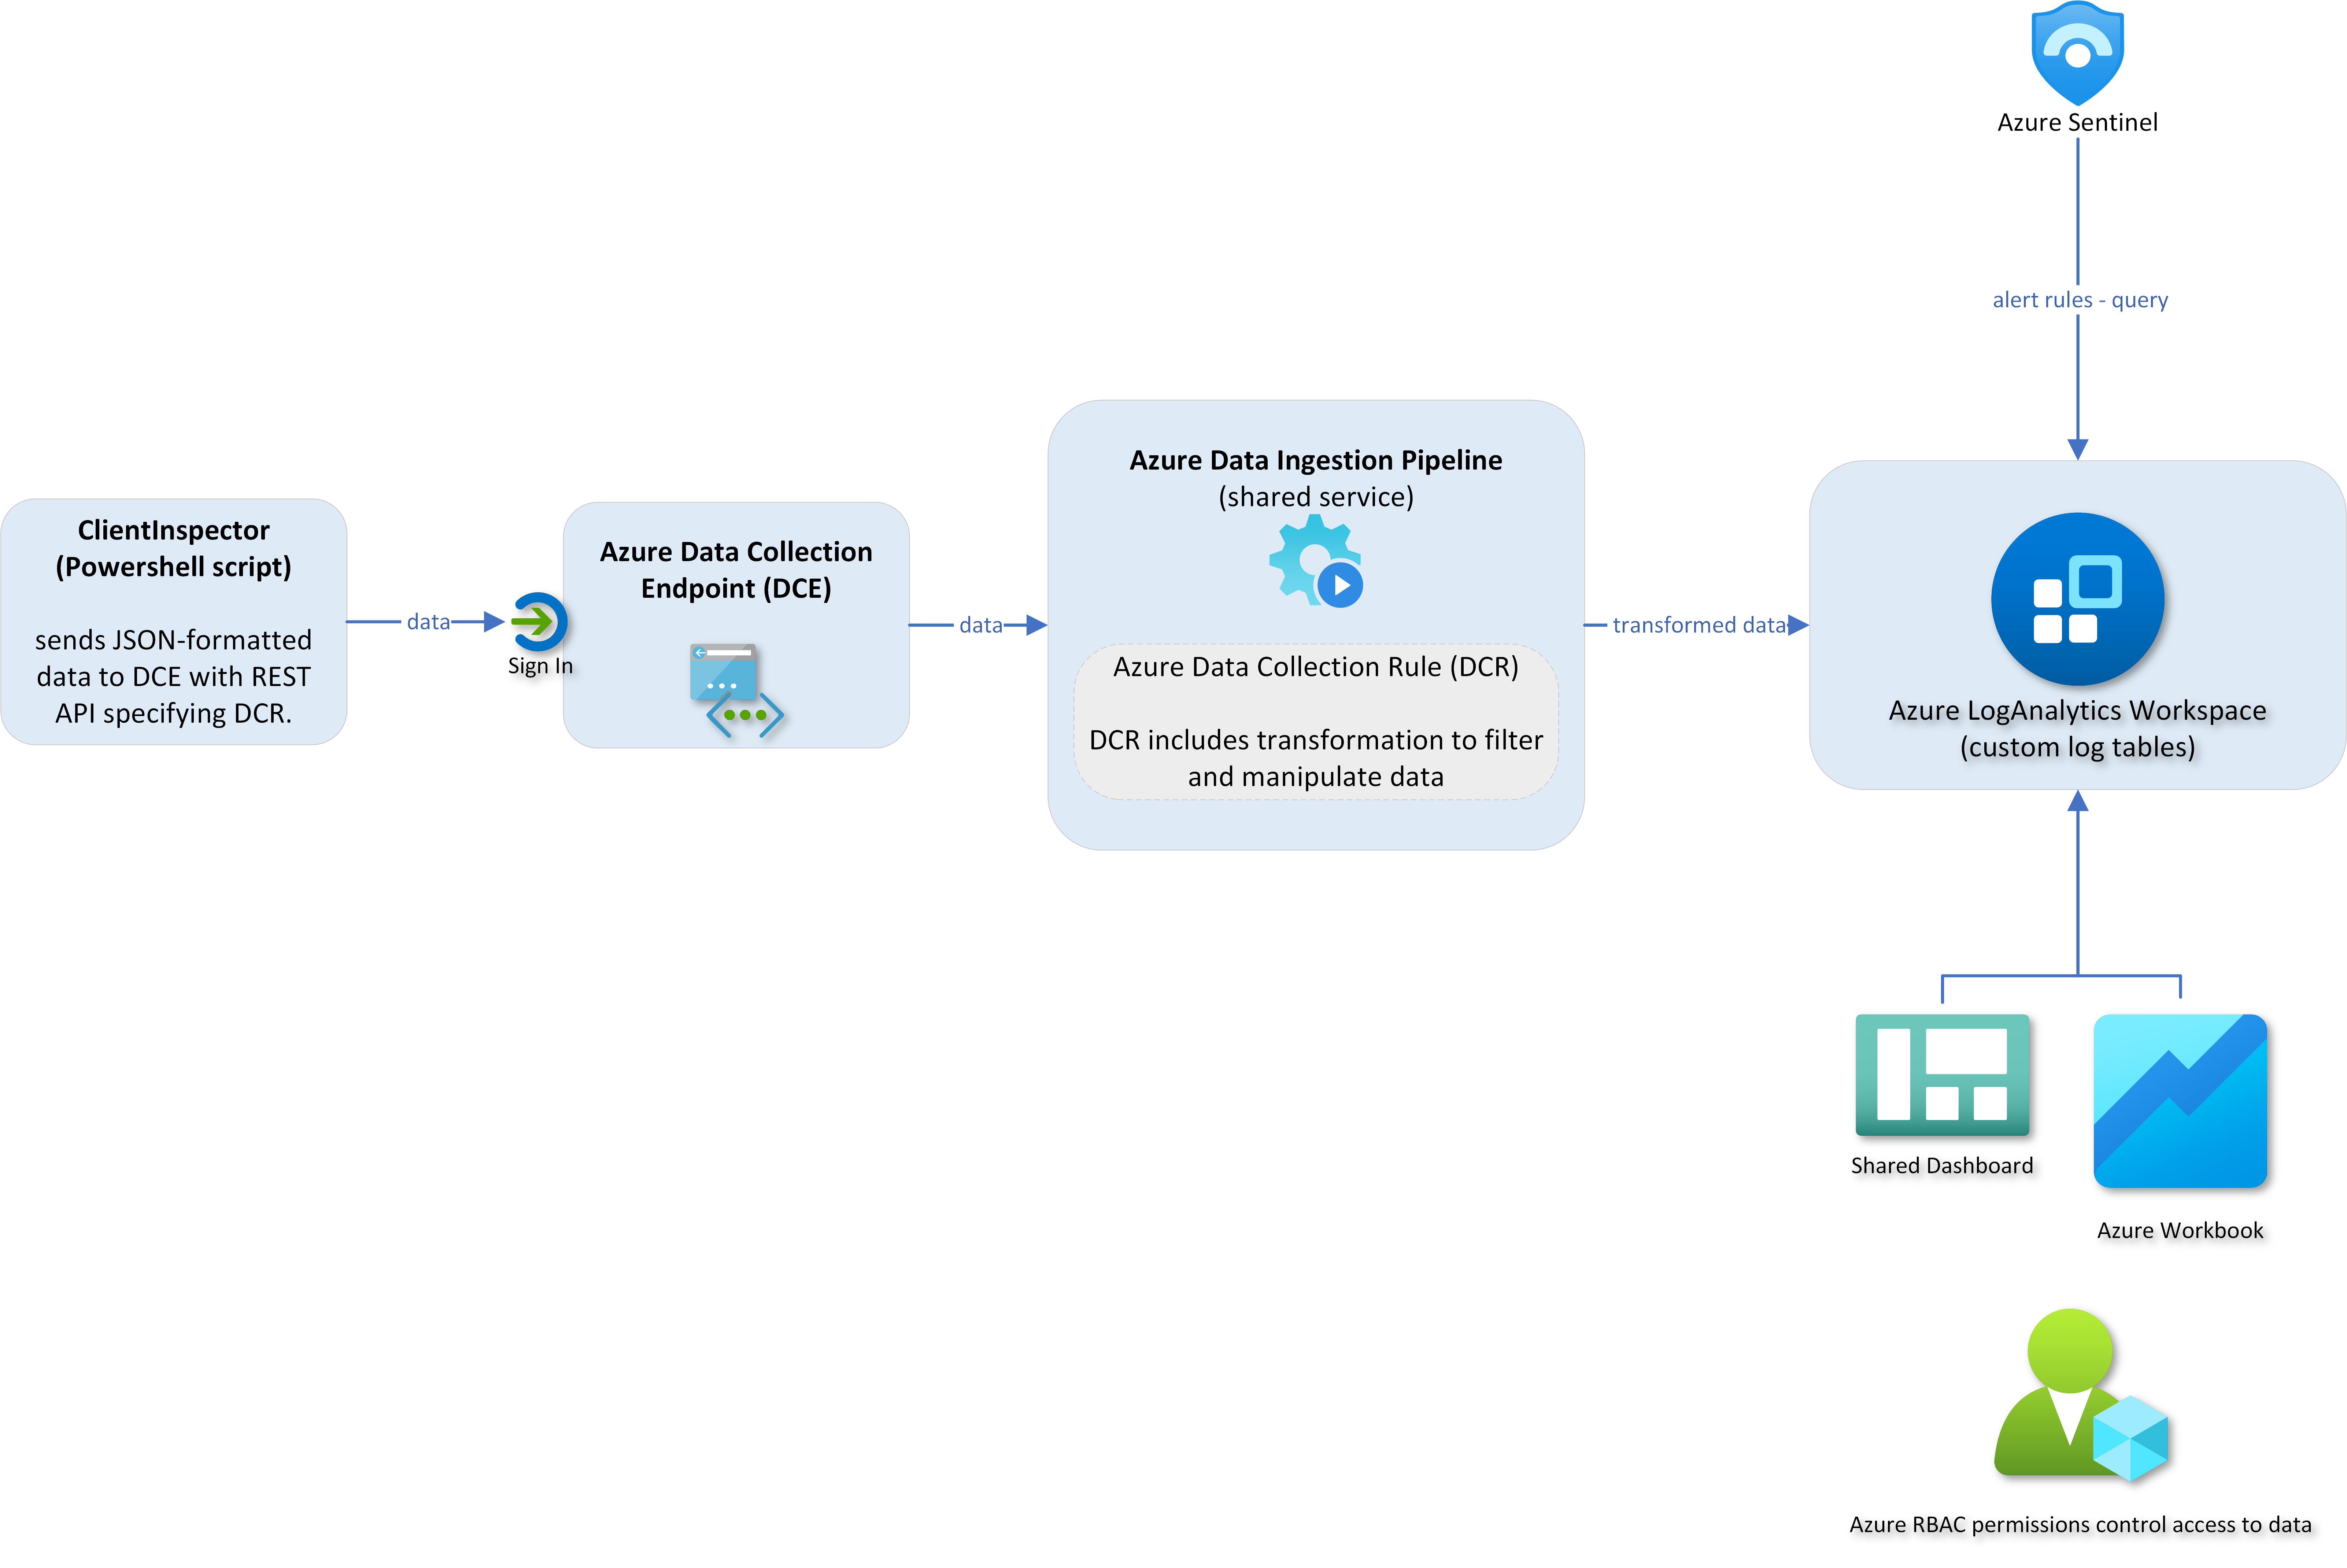 knudsenmorten/clientinspectorv2
Azure-based client inventory and drift detection tool that collects Windows configuration data (antivirus, patching, Bitlocker) into LogAnalytics for…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 xiaoqimikko/netty-http2-check
Offline Java tool that scans jars and versions to determine exposure to seven netty-codec-http2 CVEs, recommending the single patched version that…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…