
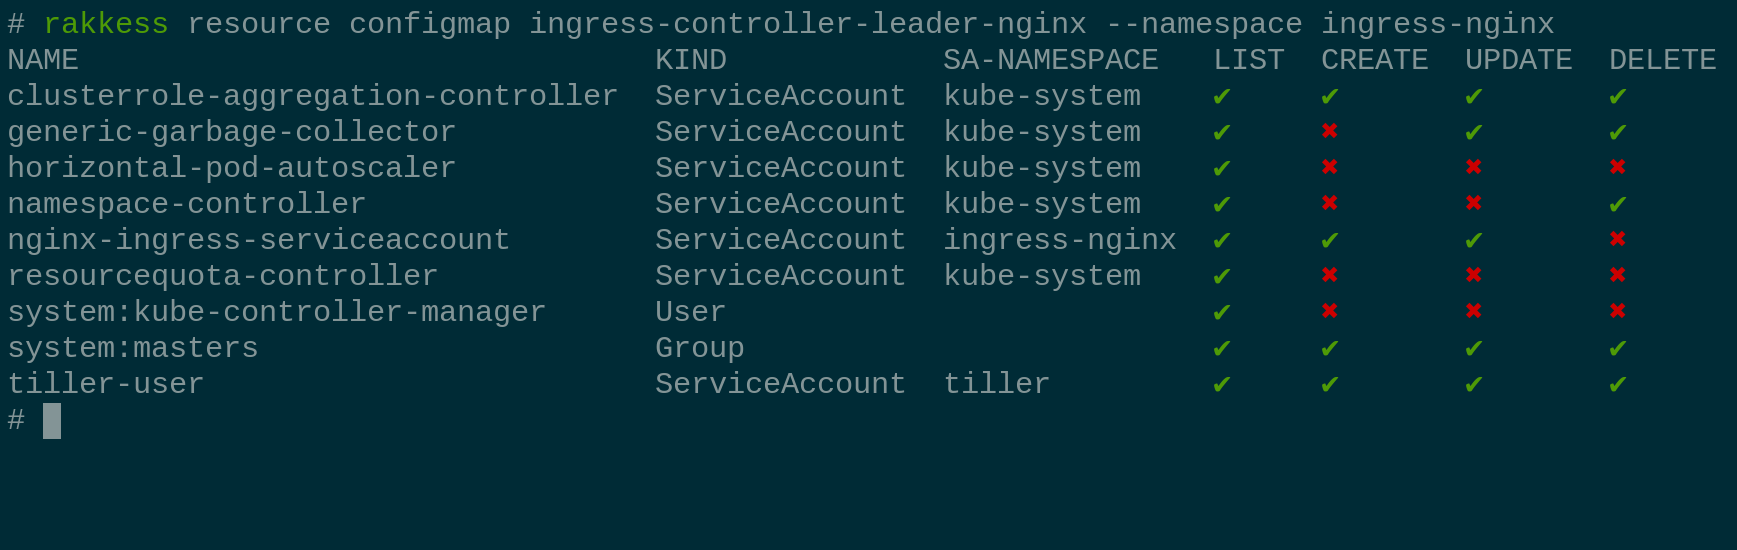
rakkess
 corneliusweig/rakkess
Review Access - kubectl plugin to show an access matrix for k8s server resources
authentication-authorizationcloud-infrastructure-securitycloud-security+2
1.4k
corneliusweig/rakkessReview Access - kubectl plugin to show an access matrix for k8s server resources
 aquasecurity/trivy-plugin-aqua
Plugin for integrating Trivy with Aqua Security platform to scan IaC, pipelines, and dependencies for vulnerabilities and misconfigurations.
 usdag/sncscan
Tool for analyzing SAP Secure Network Communications (SNC).
 disrex-group/stylesmuggler-adobe-patches
composer require delivery of Adobe's official APSB26-146 (CVE-2026-75650) fix for Magento, via cweagans/composer-patches. Auto-selects the patch for…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 intrinsec/comission
White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…
 renanvicente/puppet-shellshock
This module determine the vulnerability of a bash binary to the shellshock exploits (CVE-2014-6271 or CVE-2014-7169) and then patch that where…
 tlwebdesign/joomla-3.10.12-languagehelper-hotfix
Plugin to fix security vulnerability CVE-2023-40626 in Joomla 3.10.12
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 opnsense/core
OPNsense GUI, API and systems backend
 3ele-projects/cve-2026-39440-funnelforms-fix
Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
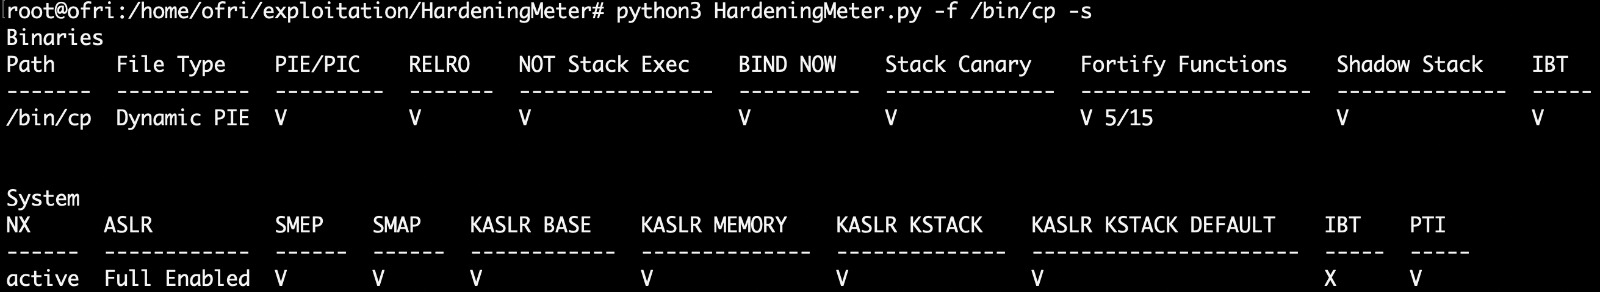 ofriouzan/hardeningmeter
HardeningMeter is an open-source Python tool carefully designed to comprehensively assess the security hardening of binaries and systems.
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources