Detecting-the-patch-of-CVE-2018-1010

C++ utility that checks Windows OS version and detects whether the patch for CVE-2018-1010 is installed using systeminfo and wmic commands.

C++ utility that checks Windows OS version and detects whether the patch for CVE-2018-1010 is installed using systeminfo and wmic commands.


Pulled Pork for Snort and Suricata rule management (from Google code)

Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.

Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…

OpenSSF Scorecard - Security health metrics for Open Source

ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.

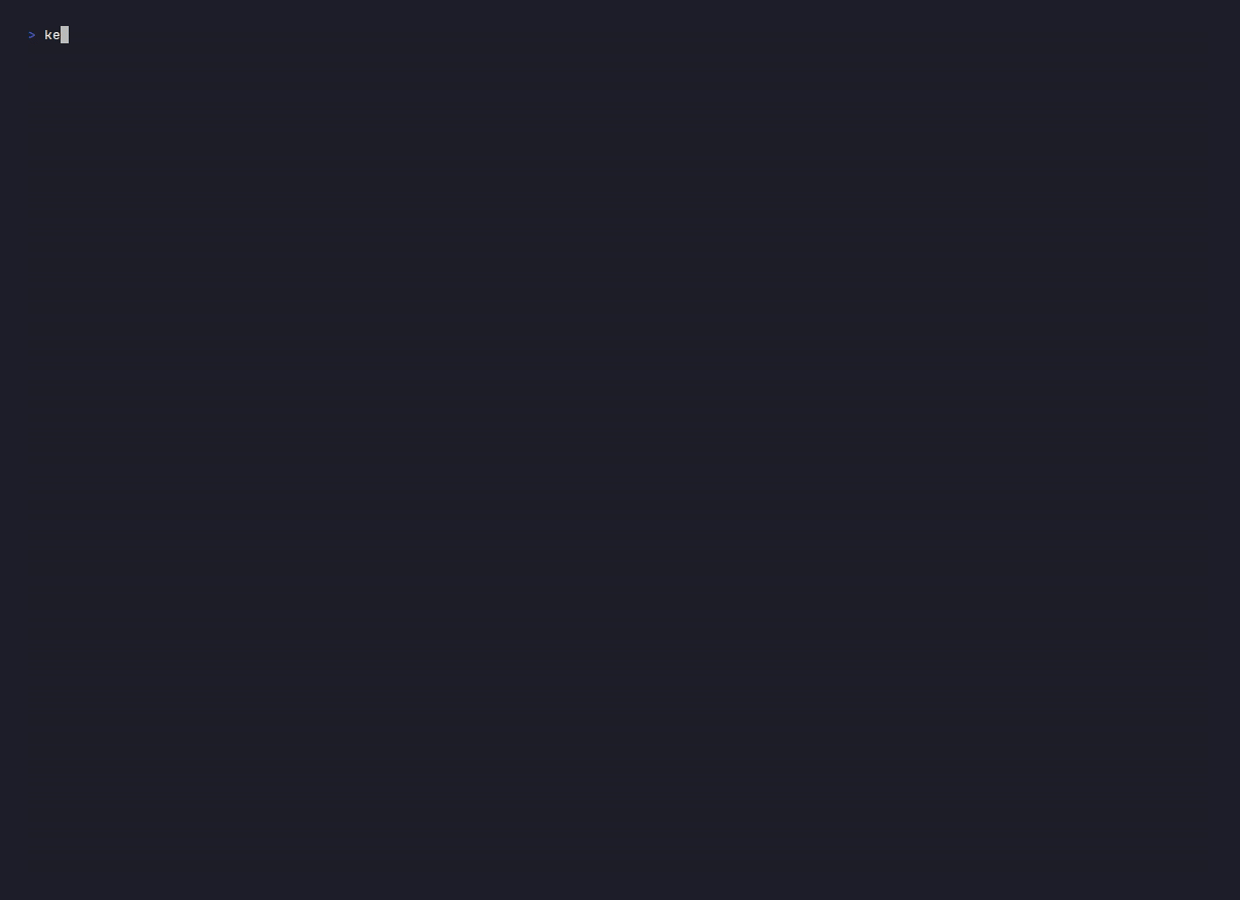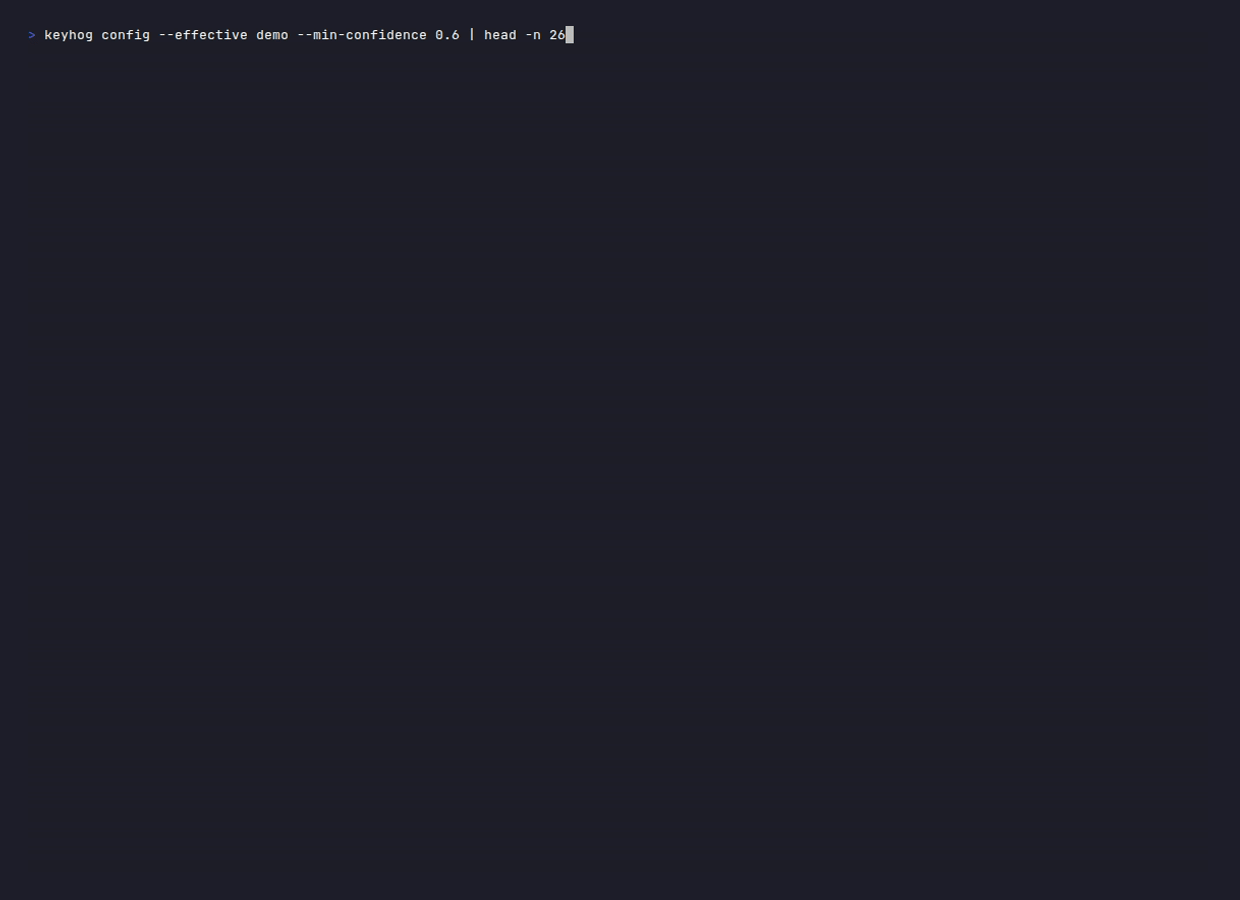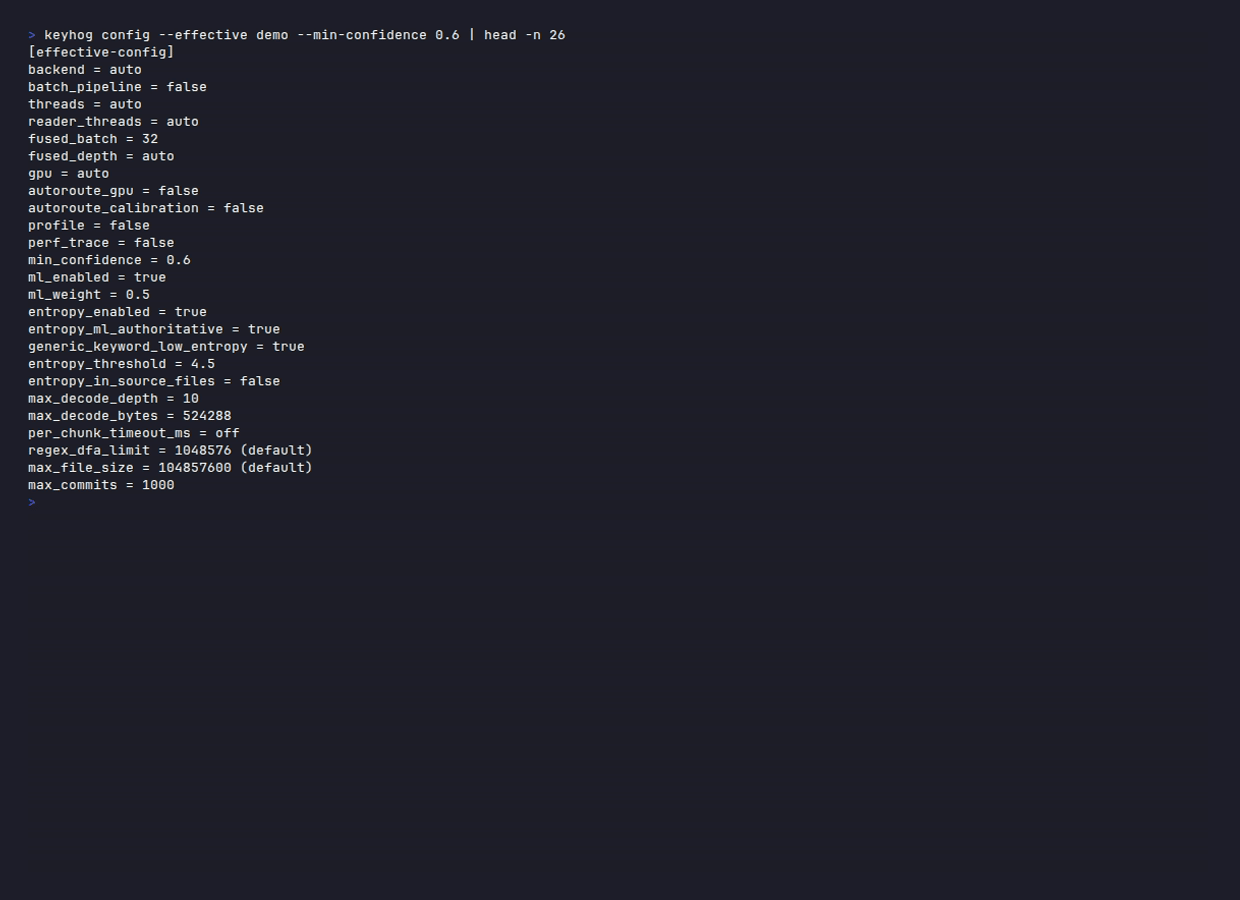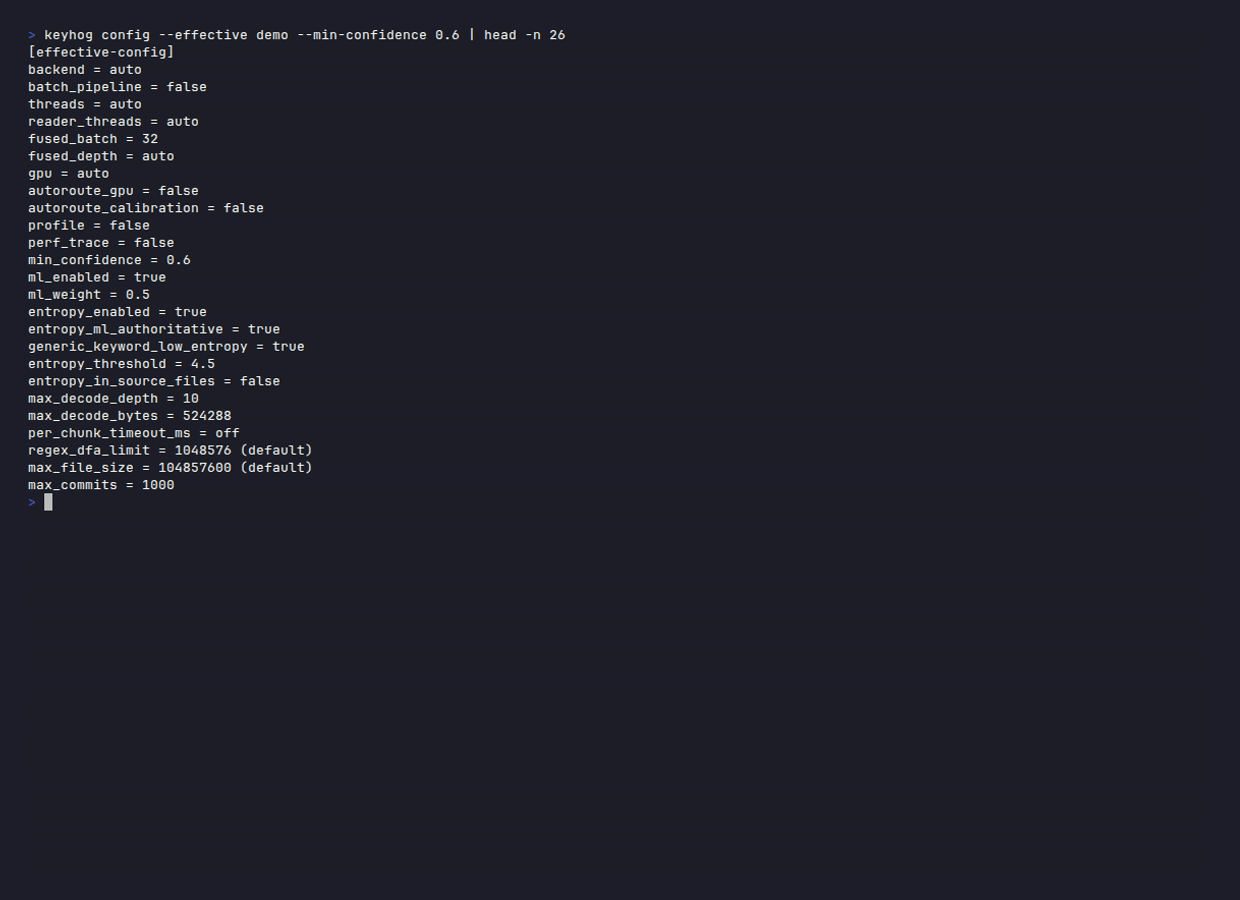
Open-source secret scanner in Rust

SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)

Apache RAT (Release Audit Tool) Gradle Plugin

PowerShell script to apply Microsoft's recommended registry-based workaround for CVE-2023-36884, mitigating remote code execution risk on Windows…

An open source, cloud-native security to protect everything from build to runtime

Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…

DSC resources to simplify administration of certificates on a Windows Server.

Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…

YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…