
KubiScan
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
authentication-authorizationcloud-securityconfiguration-auditing+8
1.4k1 year ago
cyberark/kubiscanA tool to scan Kubernetes cluster for risky permissions
 dev-2null/adcollector
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
 trimstray/otseca
Open source security auditing tool to search and dump system configuration. It allows you to generate reports in HTML or RAW-HTML formats.
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
 lxkxc/vmxnet3hunter
Use this tool to prioritize cluster patching for the recent VMware advisory VMSA-2018-0027 related to CVE-2018-6981 and CVE-2018-6982.
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
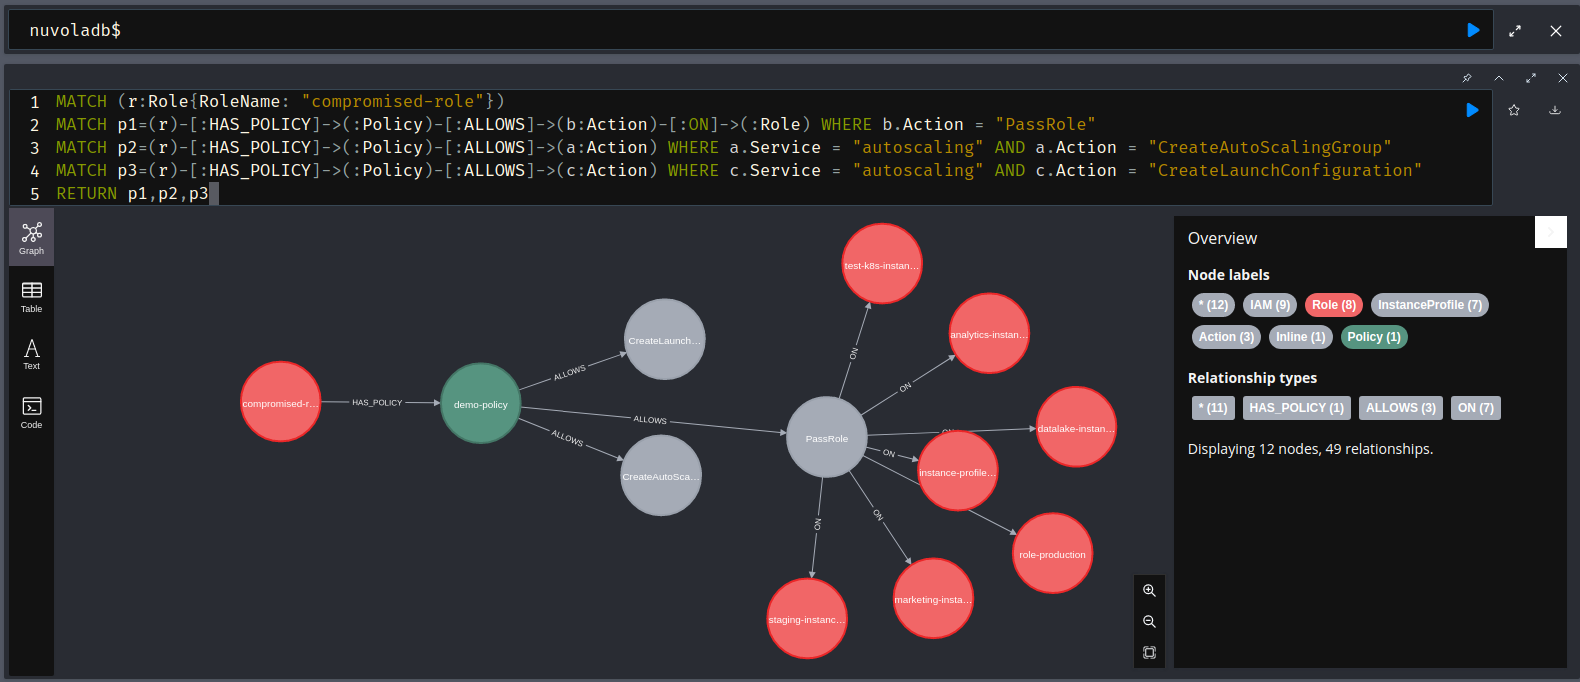 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.
 leo4j/invoke-adenum
Automated Active Directory auditing and enumeration tool that generates detailed HTML audit reports with CSV/XLSX export, designed for security…
 0zer0d4y/fuegotest
A CLI tool for detecting CVE-2023-20048 vulnerability in Cisco Firepower Management Center.
 fortalice/modifycerttemplate
ADCS cert template modification and ACL enumeration
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 sreejaputhan/cpanel-control-plane-exposure-check
Defensive exposure assessment tool for identifying externally accessible cPanel, WHM, and Webmail management interfaces related to CVE-2026-41940.
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data