
KubiScan
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
authentication-authorizationcloud-securityconfiguration-auditing+8
cyberark/kubiscanA tool to scan Kubernetes cluster for risky permissions
 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 owasp/kubelight
OWASP Kubernetes security and compliance tool [WIP]
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
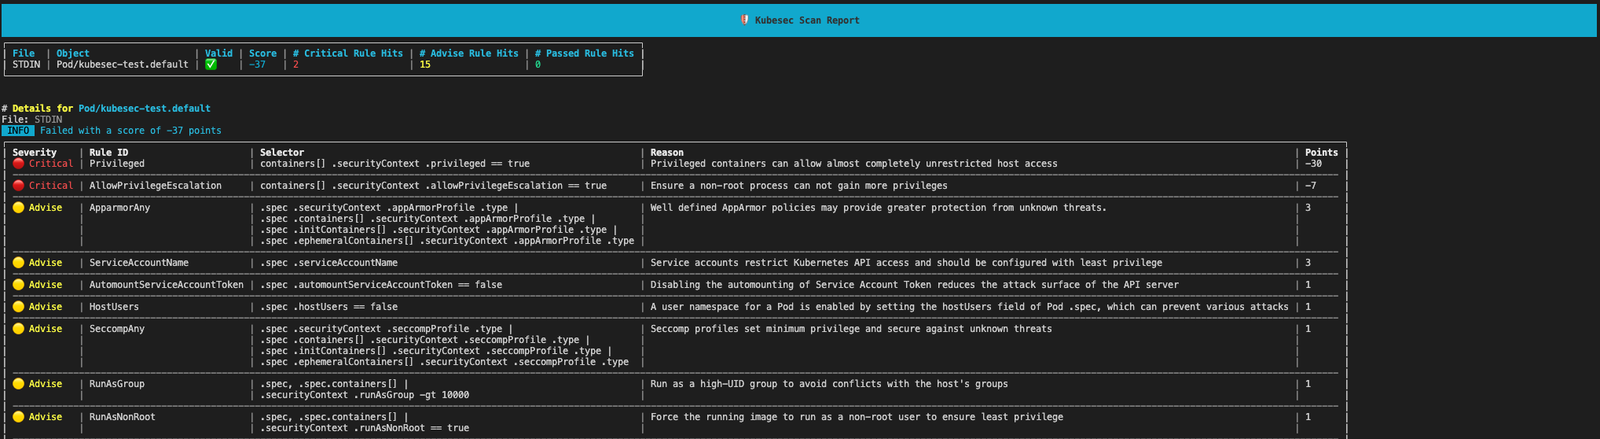 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 santhreal/keyhog
Open-source secret scanner in Rust
 chen-keinan/kube-beacon
Open Source runtime scanner for k8s cluster and perform security audit checks based on CIS Kubernetes Benchmark specification
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 hirokiii/cve-2023-44487
Educational environment for LTAT.04.022 Homework 4.
 melonlonmeo/cve-2025-49132
Poc - CVE-2025-49132
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…