
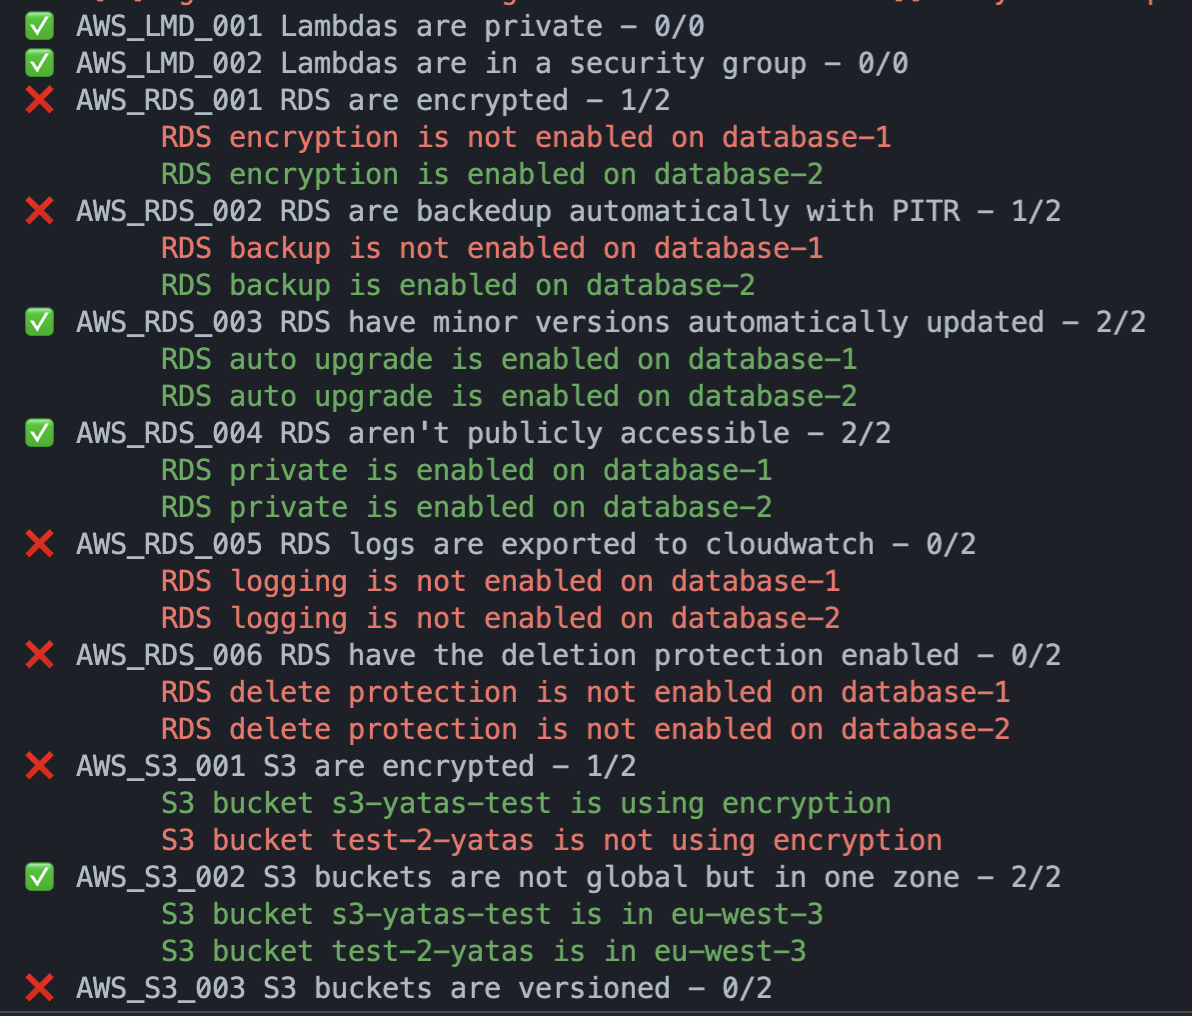
yatas
 padok-team/yatas
:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
cloud-infrastructure-securitycloud-securityconfiguration-auditing+3
343
padok-team/yatas:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
 trimstray/otseca
Open source security auditing tool to search and dump system configuration. It allows you to generate reports in HTML or RAW-HTML formats.
 optiopay/klar
Integration of Clair and Docker Registry
 synacktiv/bissap
A new open-source tool to quickly audit SAP permissions.
 k3rnix/portguard
USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
 wadesweaponshed/check-point-trusted-access-review
Local web app for conducting a Check Point Trusted Access Review. This scanner is built specifically to look for configuration issues around…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 shoucheng3/apache__jspwiki_cve-2019-10077_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…
 shoucheng3/apache__jspwiki_cve-2019-10078_2_11_0_m4_fixed
Exploit testing repository for Apache JSPWiki CVE-2019-10078, demonstrating a cross-site scripting vulnerability in a Java-based wiki platform with…
 shoucheng3/apache__jspwiki_cve-2019-10089_2-11-0-m4
Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…
 shoucheng3/apache__jspwiki_cve-2019-10076_2-11-0-m3
Java-based wiki platform with JAAS security integration, access control, and detailed configuration auditing. Includes documentation for…
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…
 noxxi/p5-ssl-tools
Perl scripts for SSL/TLS analysis: check protocol and cipher support, verify certificates, test OCSP, and detect Heartbleed across SMTP, HTTPS, and…
 rancher/externalip-webhook
CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs
 atomics-hub/exposecheck
Defensive single-target self-check for Langflow CVE-2025-3248 exposure
 almogopp/openssh-cve-2024-6387-fix
A Bash script to mitigate the CVE-2024-6387 vulnerability in OpenSSH by providing an option to upgrade to a secure version or apply a temporary…