

CanaryHunter
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
adversarial-attackcloud-infrastructure-securityconfiguration-auditing+4
c0axx/canaryhunterCanary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 anvilsecure/dawgmon
dawg the hallway monitor - monitor operating system changes and analyze introduced attack surface when installing software
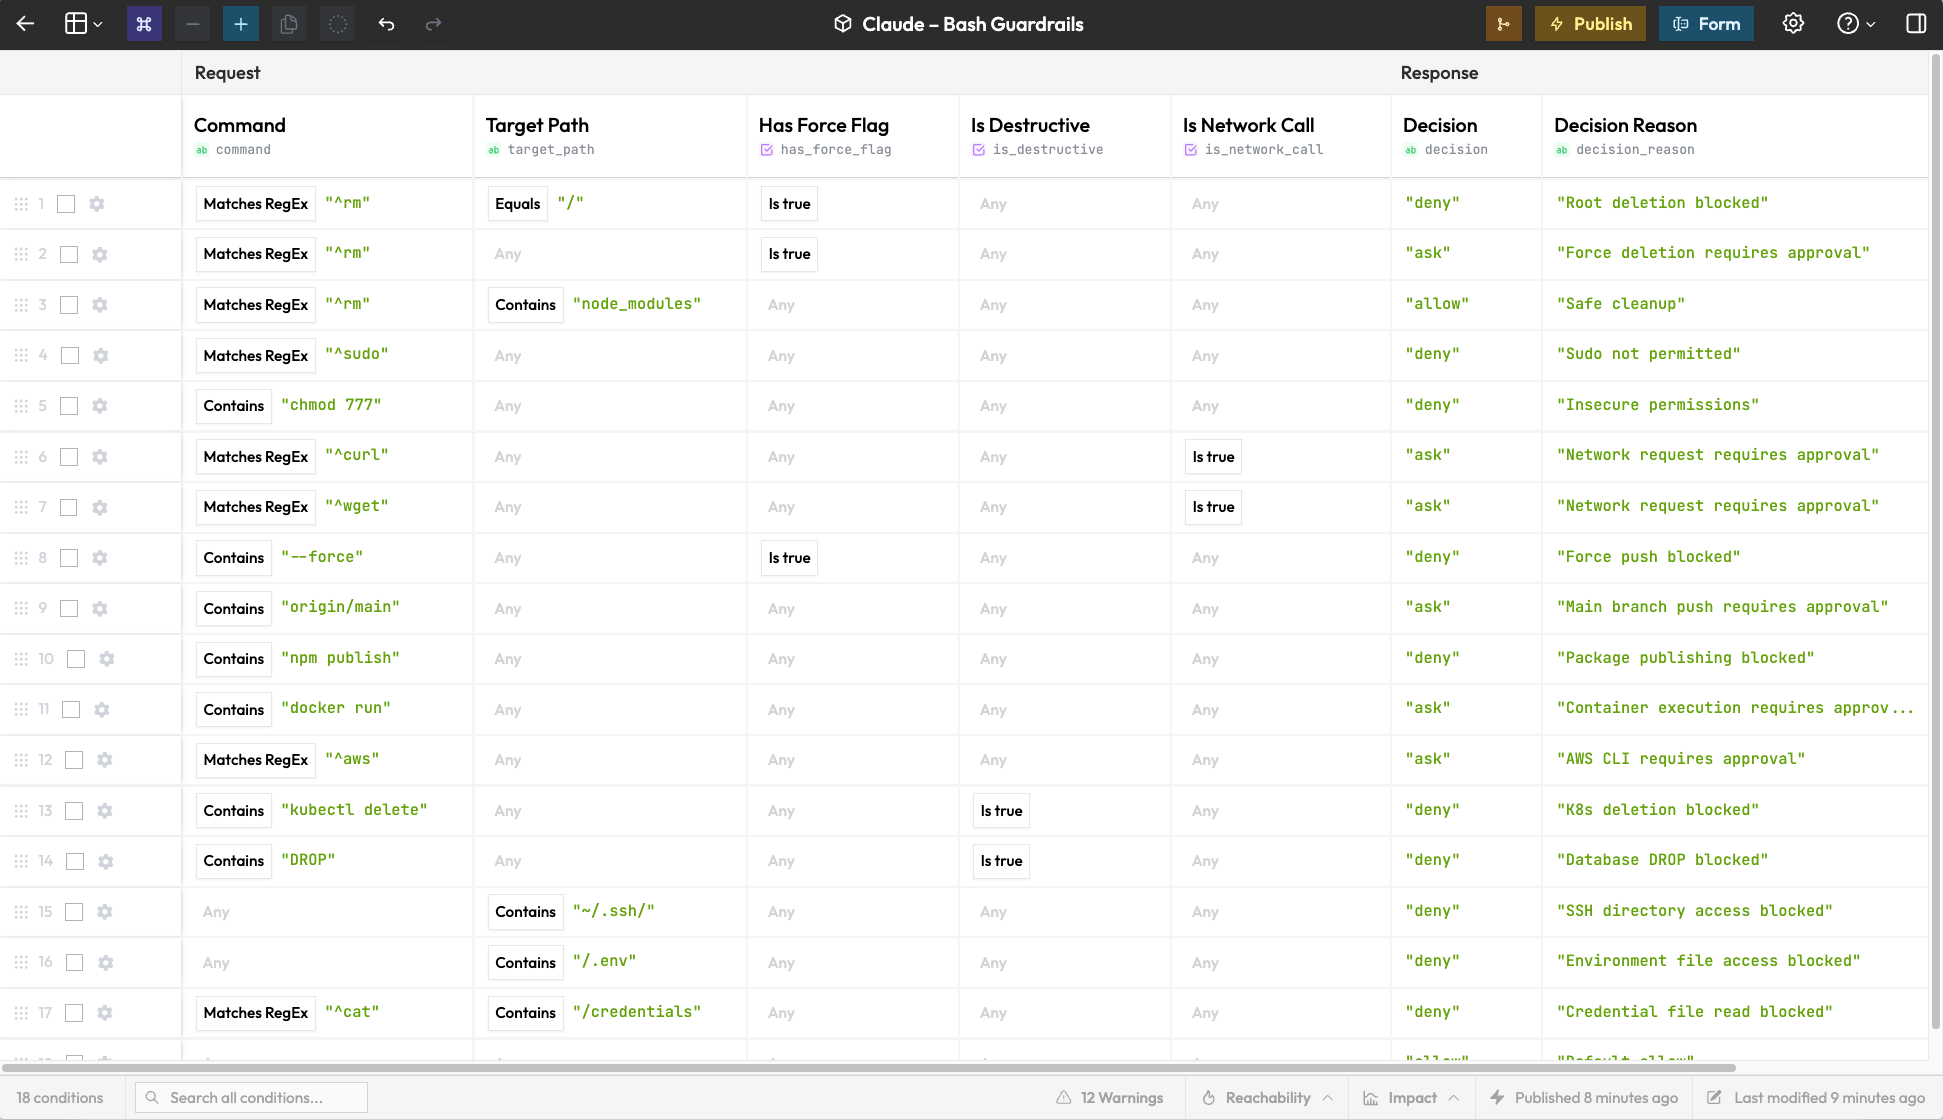 rulebricks/claude-code-guardrails
Real-time guardrails for Claude Code tool calls.
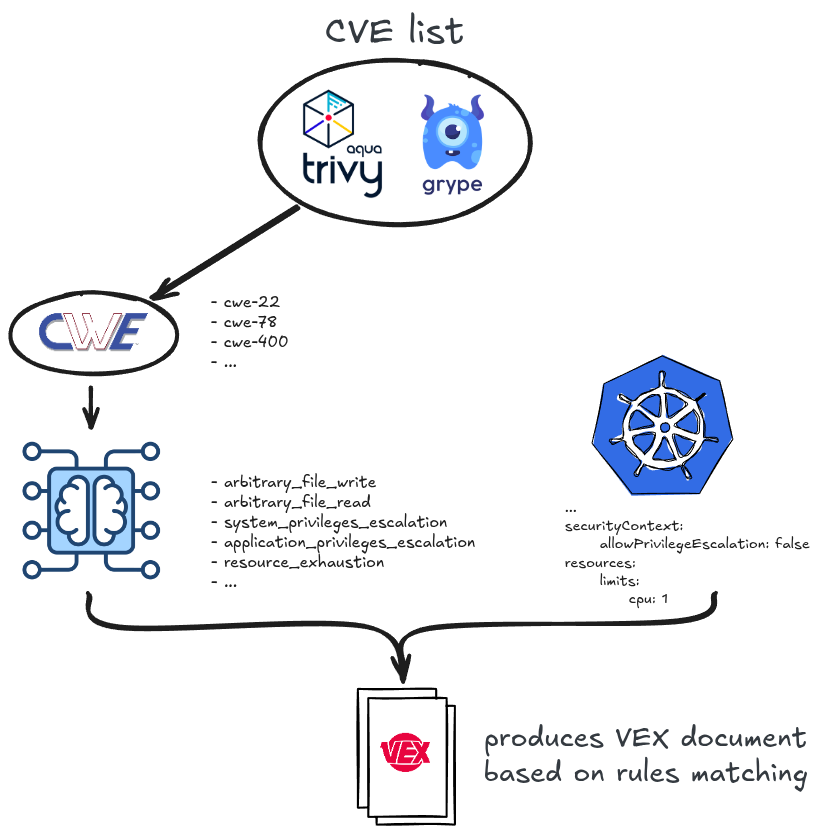 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 mthbernardes/heimdall_webserver
It's a tool to manage vulnerables packages in your *nix server, in a centralized way
 rclone/passwordcheck
Check rclone config files for insecure passwords
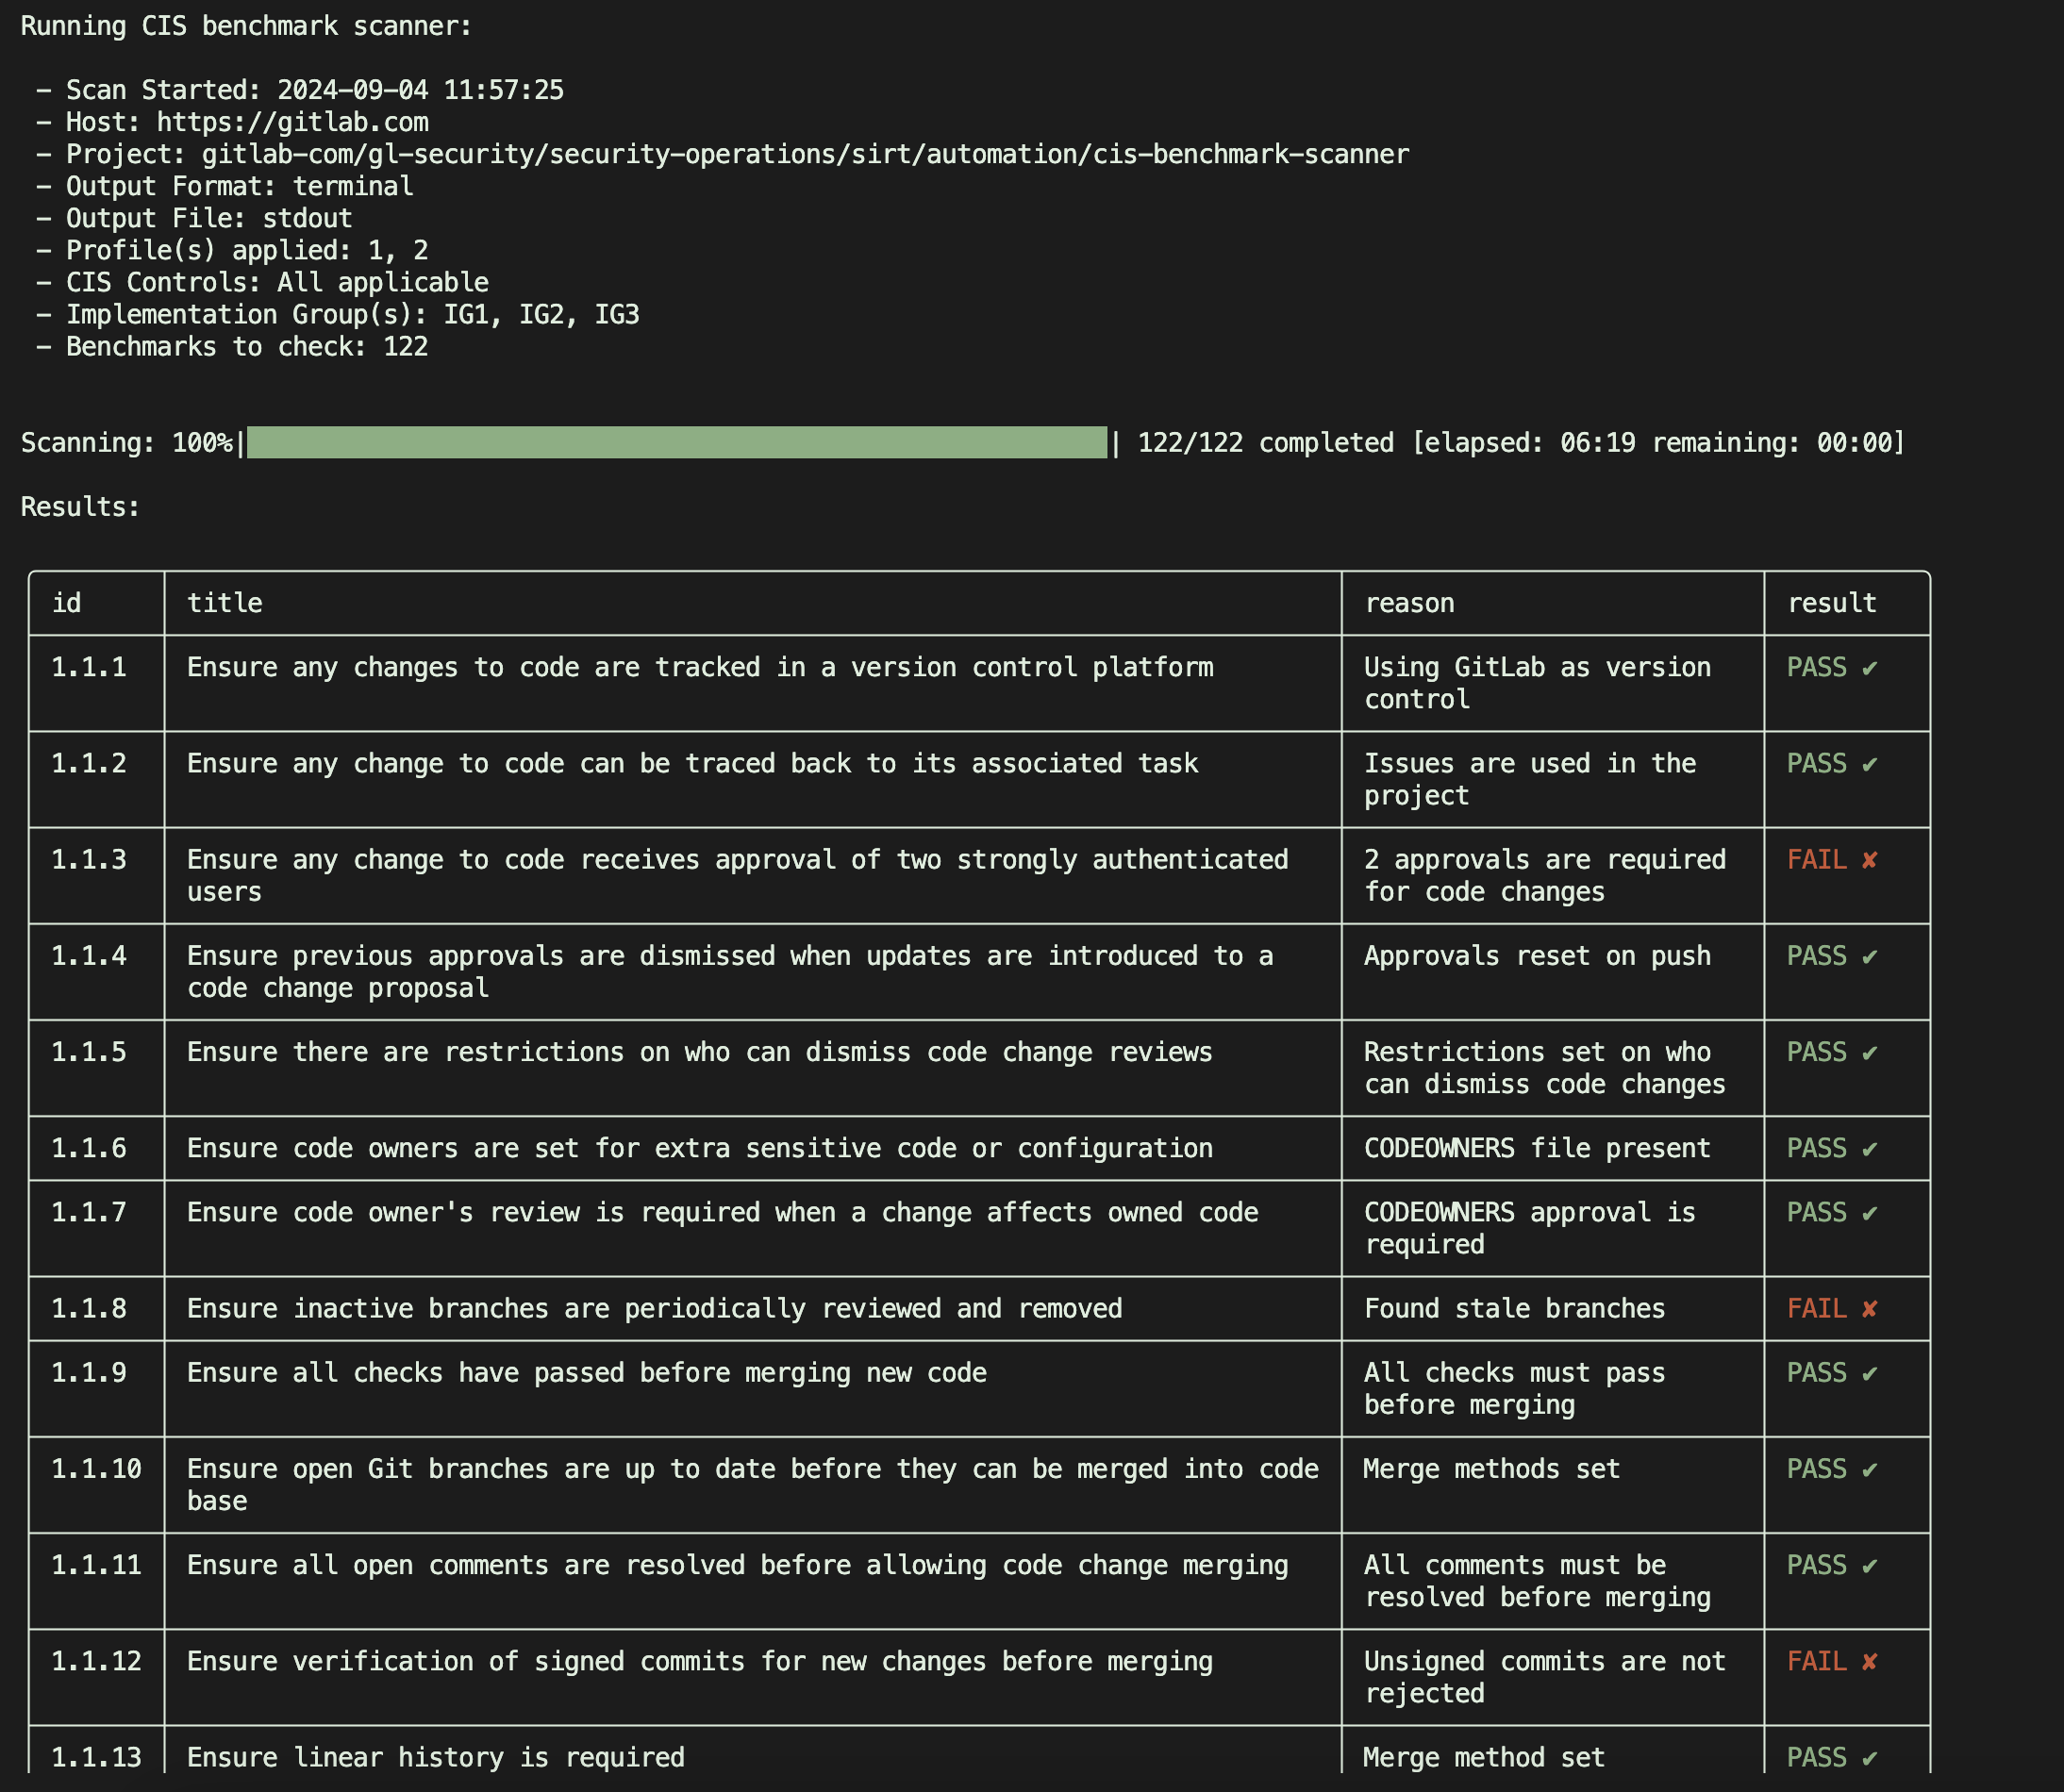
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 bplinux/chackd
Daemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696
 mmotti/reset-inetpub
Restore the integrity of the parent 'inetpub' folder following security implications highlighted by CVE-2025-21204.
 d4gh0s7/cve-2018-19788
Ansible role to audit and test systems for CVE-2018-19788 (PolicyKit privilege escalation) with automated user provisioning and exploit verification.
 vinnimarcon/log4j-updater
Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
 0xirison/printnightmare-patcher
A patch for PrintNightmare vulnerability that occurs to print spooler service for Windows machines [CVE-2021-34527]
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 code-with-amitk/centos7_cve-2021-3712_remediation
Production Ready Steps for Remediating a openssl CVE(https://nvd.nist.gov/vuln/detail/cve-2021-3712) on EOL CentOS7 box
 sammyfung/openssl-heartbleed-fix
OpenSSL Heartbleed (CVE-2014-0160) Fix script