
policy_sentry
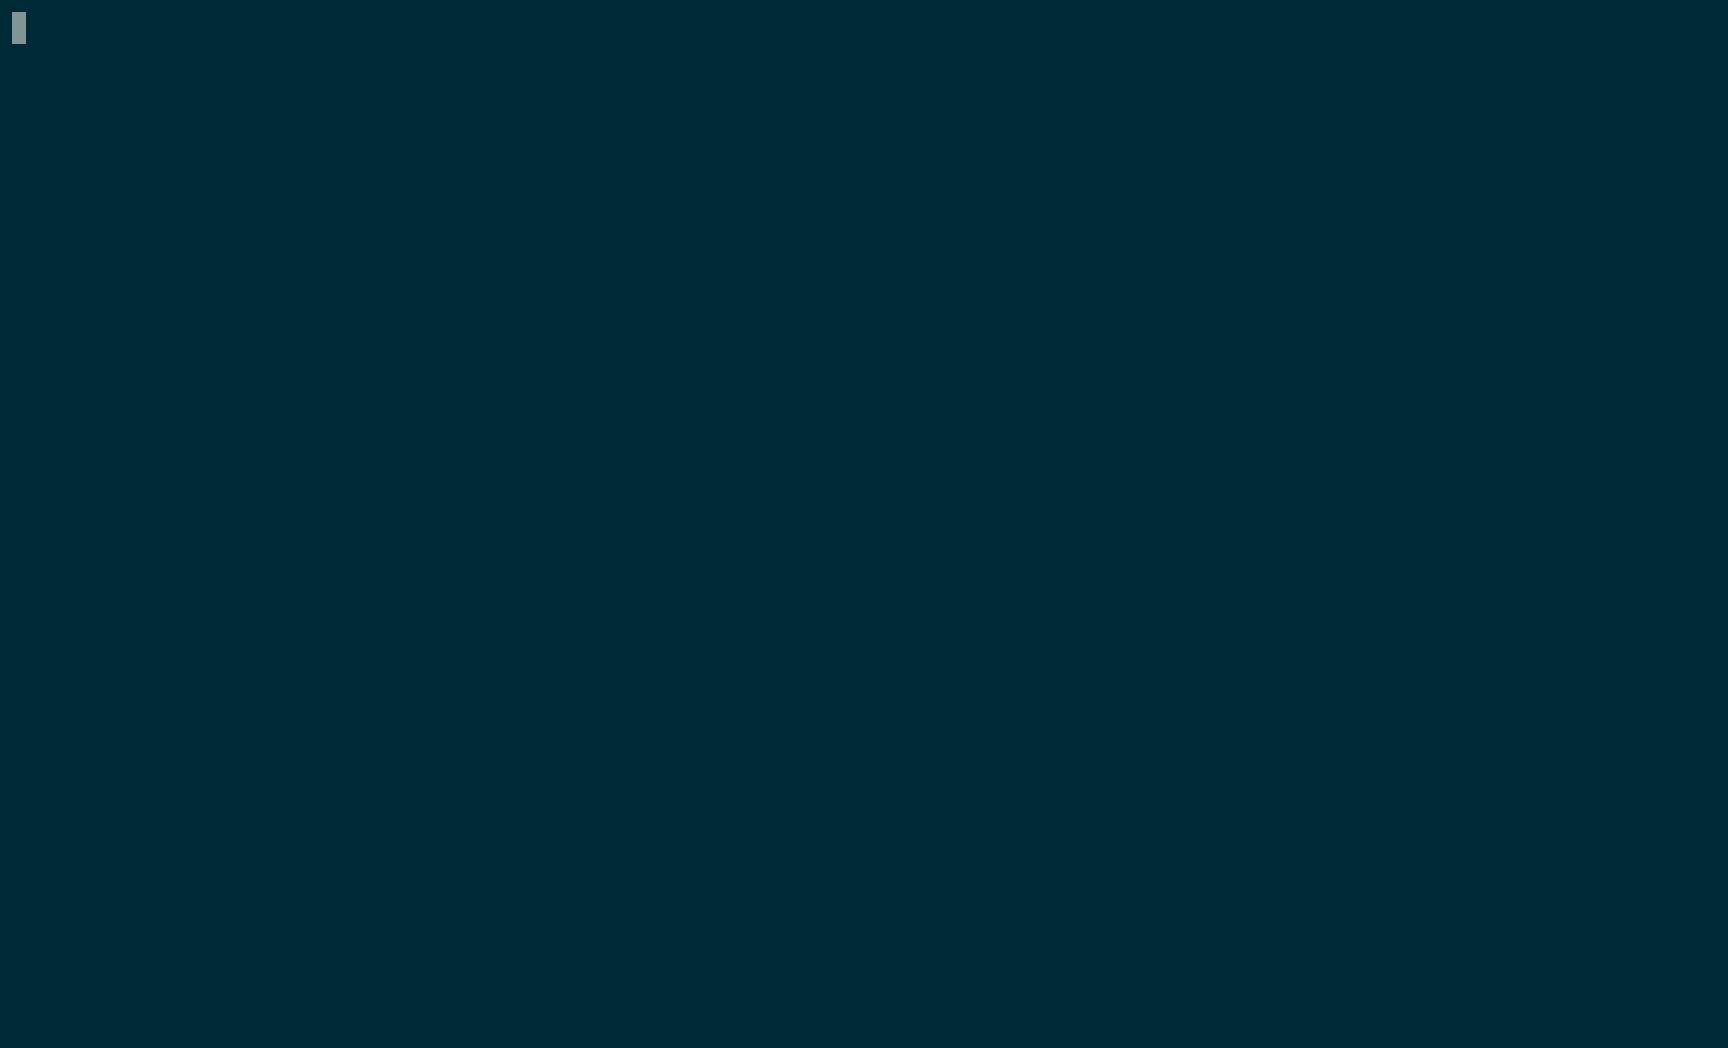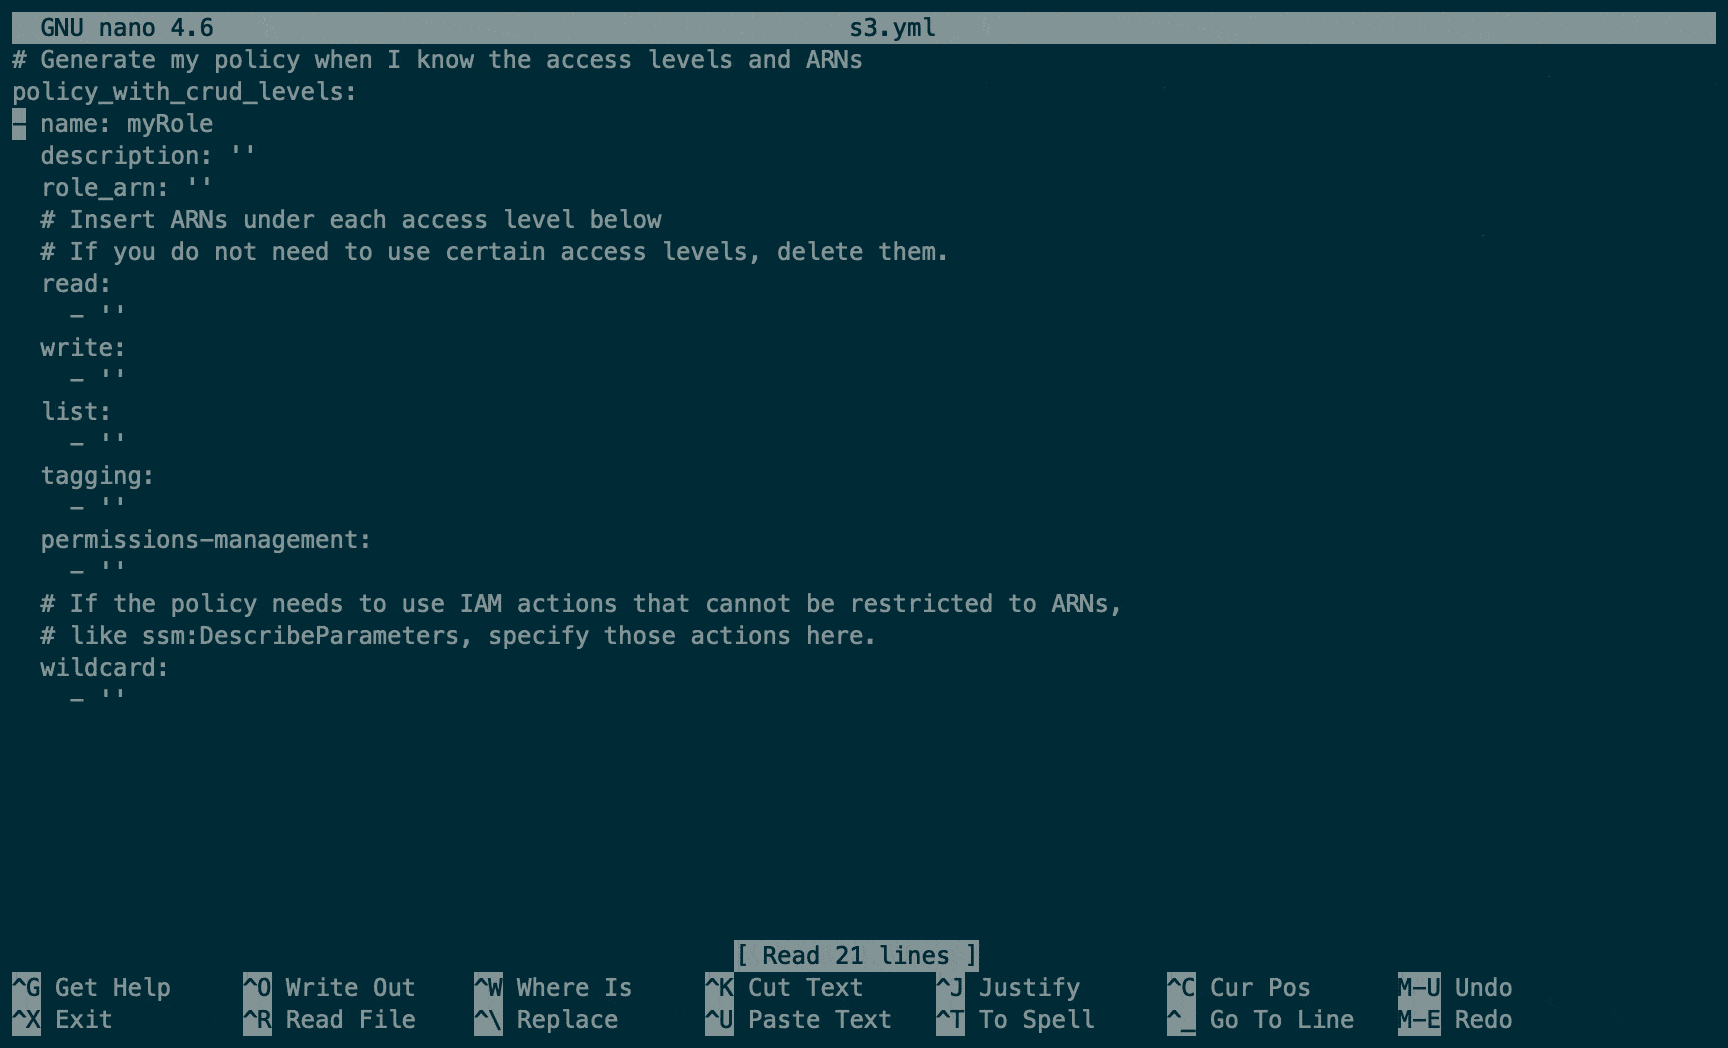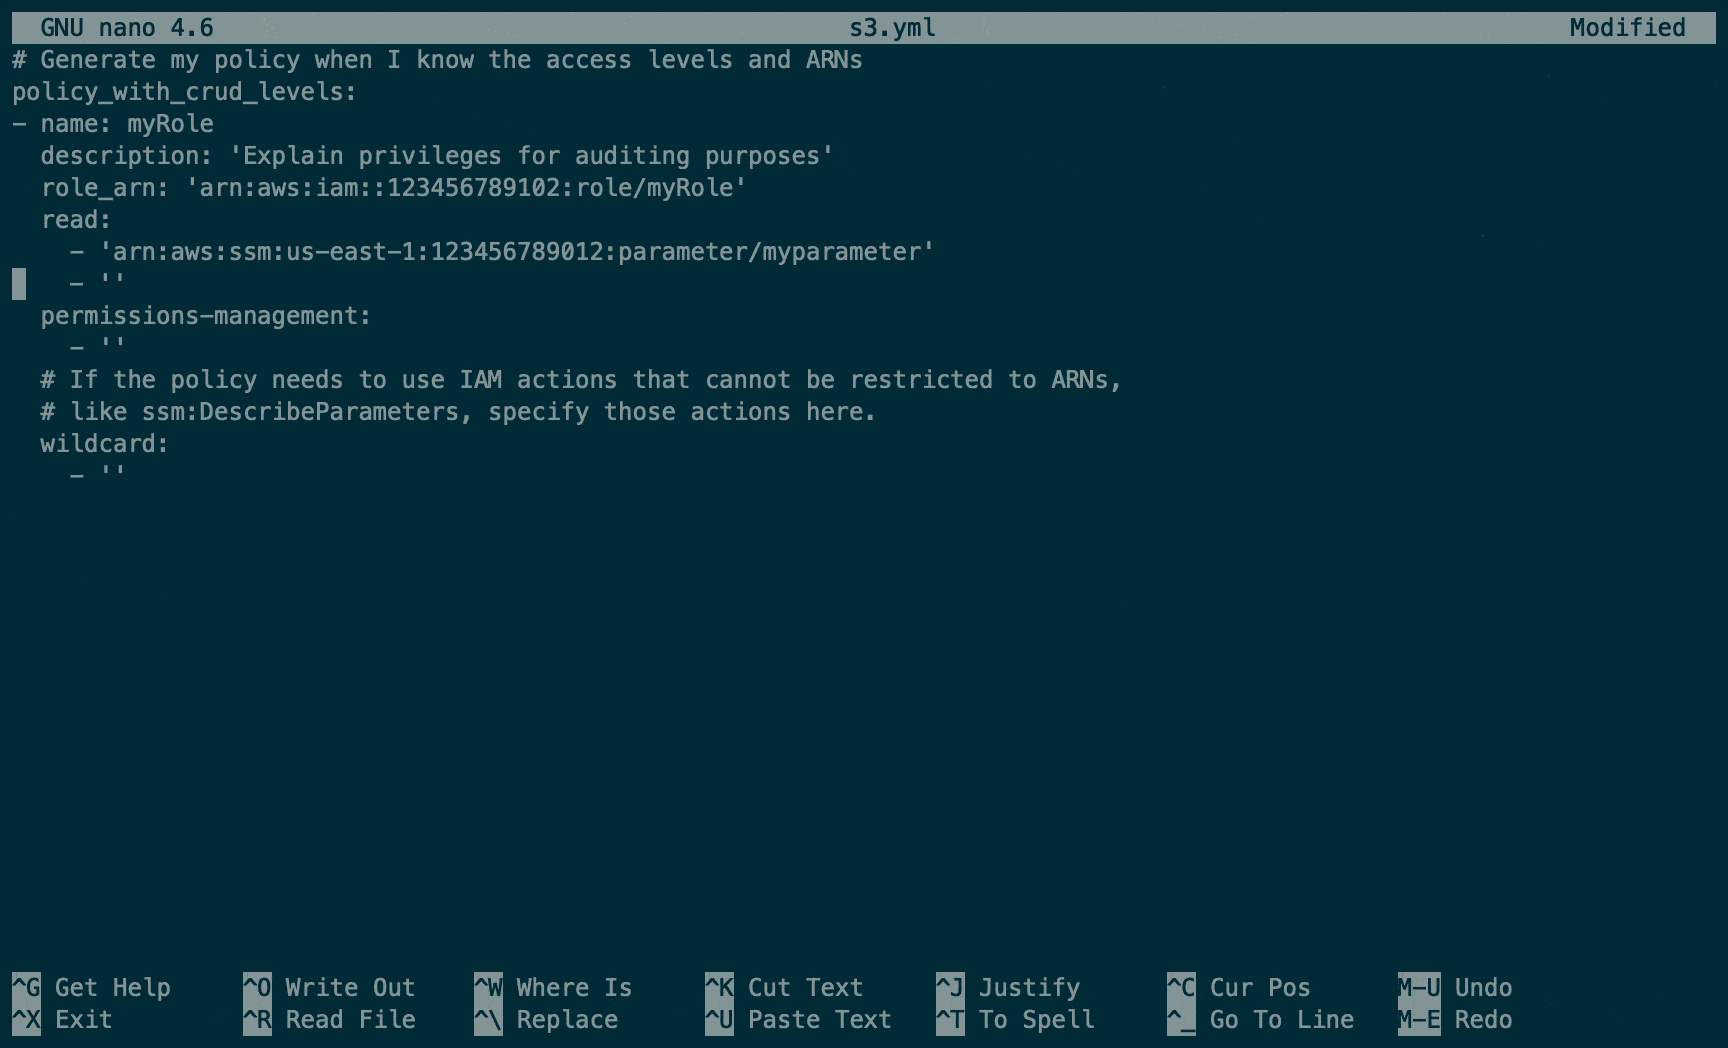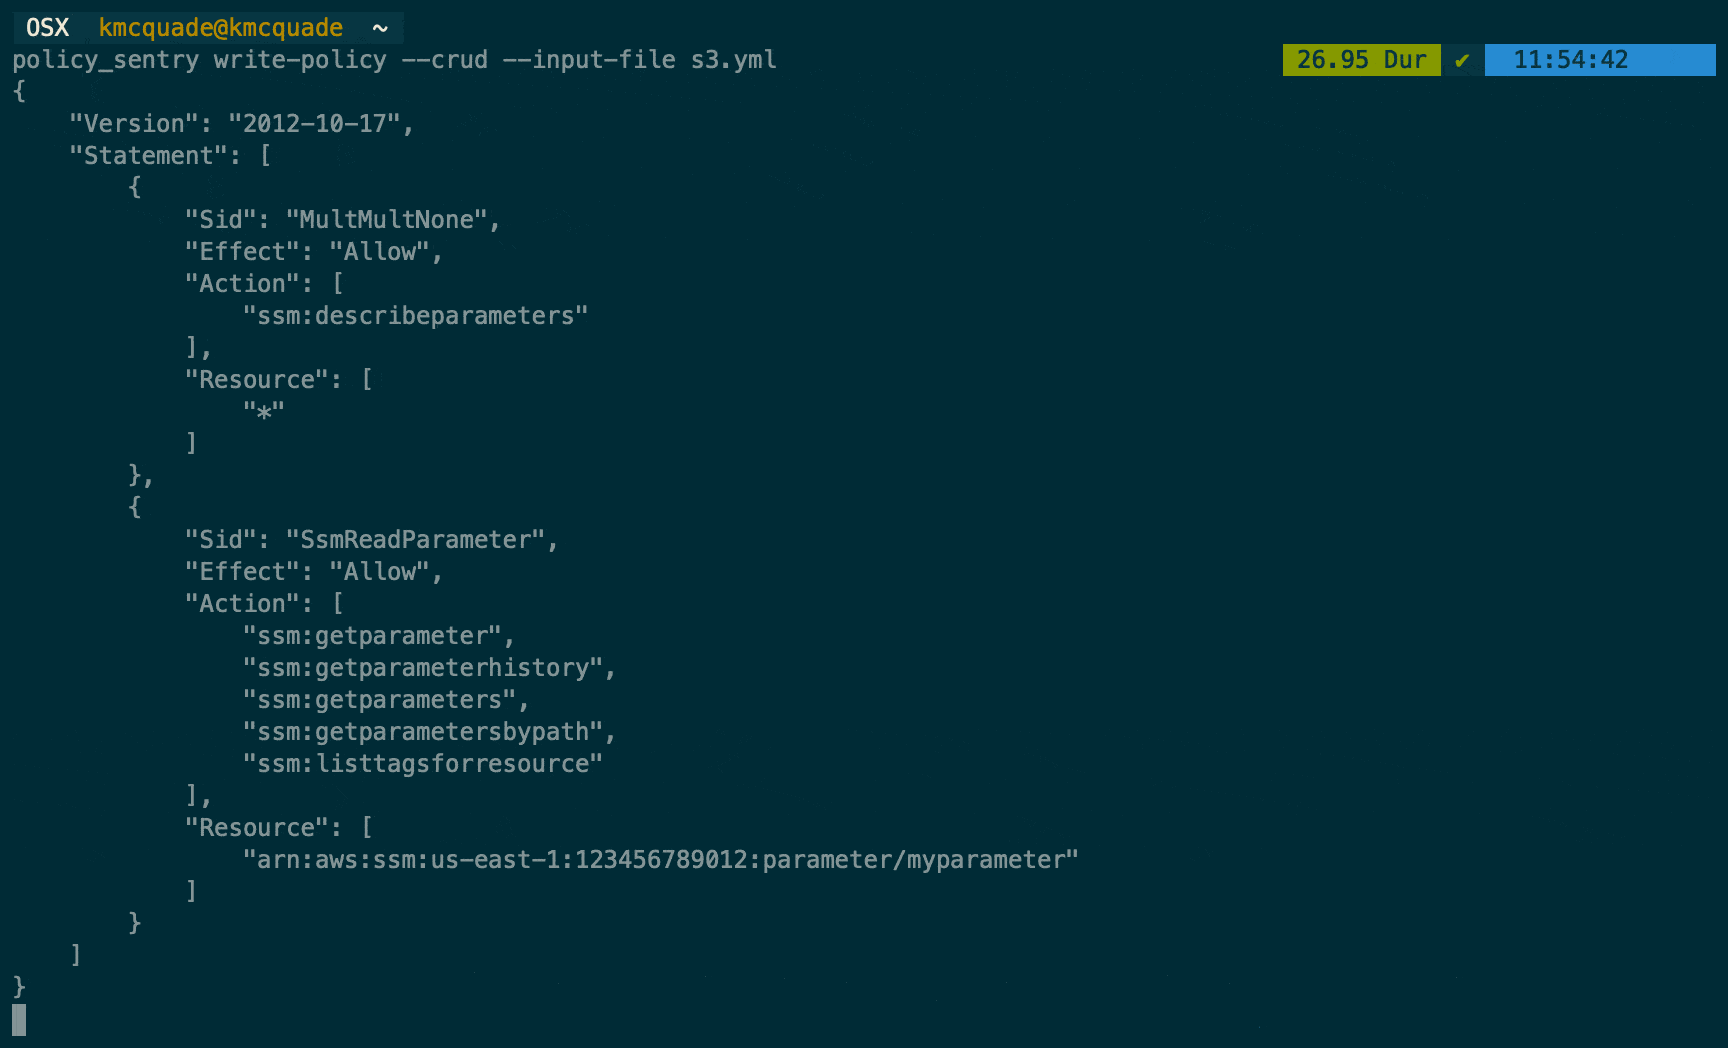
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Scans systems for CVE-2026-31431 (CopyFile vulnerability), enumerates system details, evaluates exposure, reports vulnerable status, and optionally…

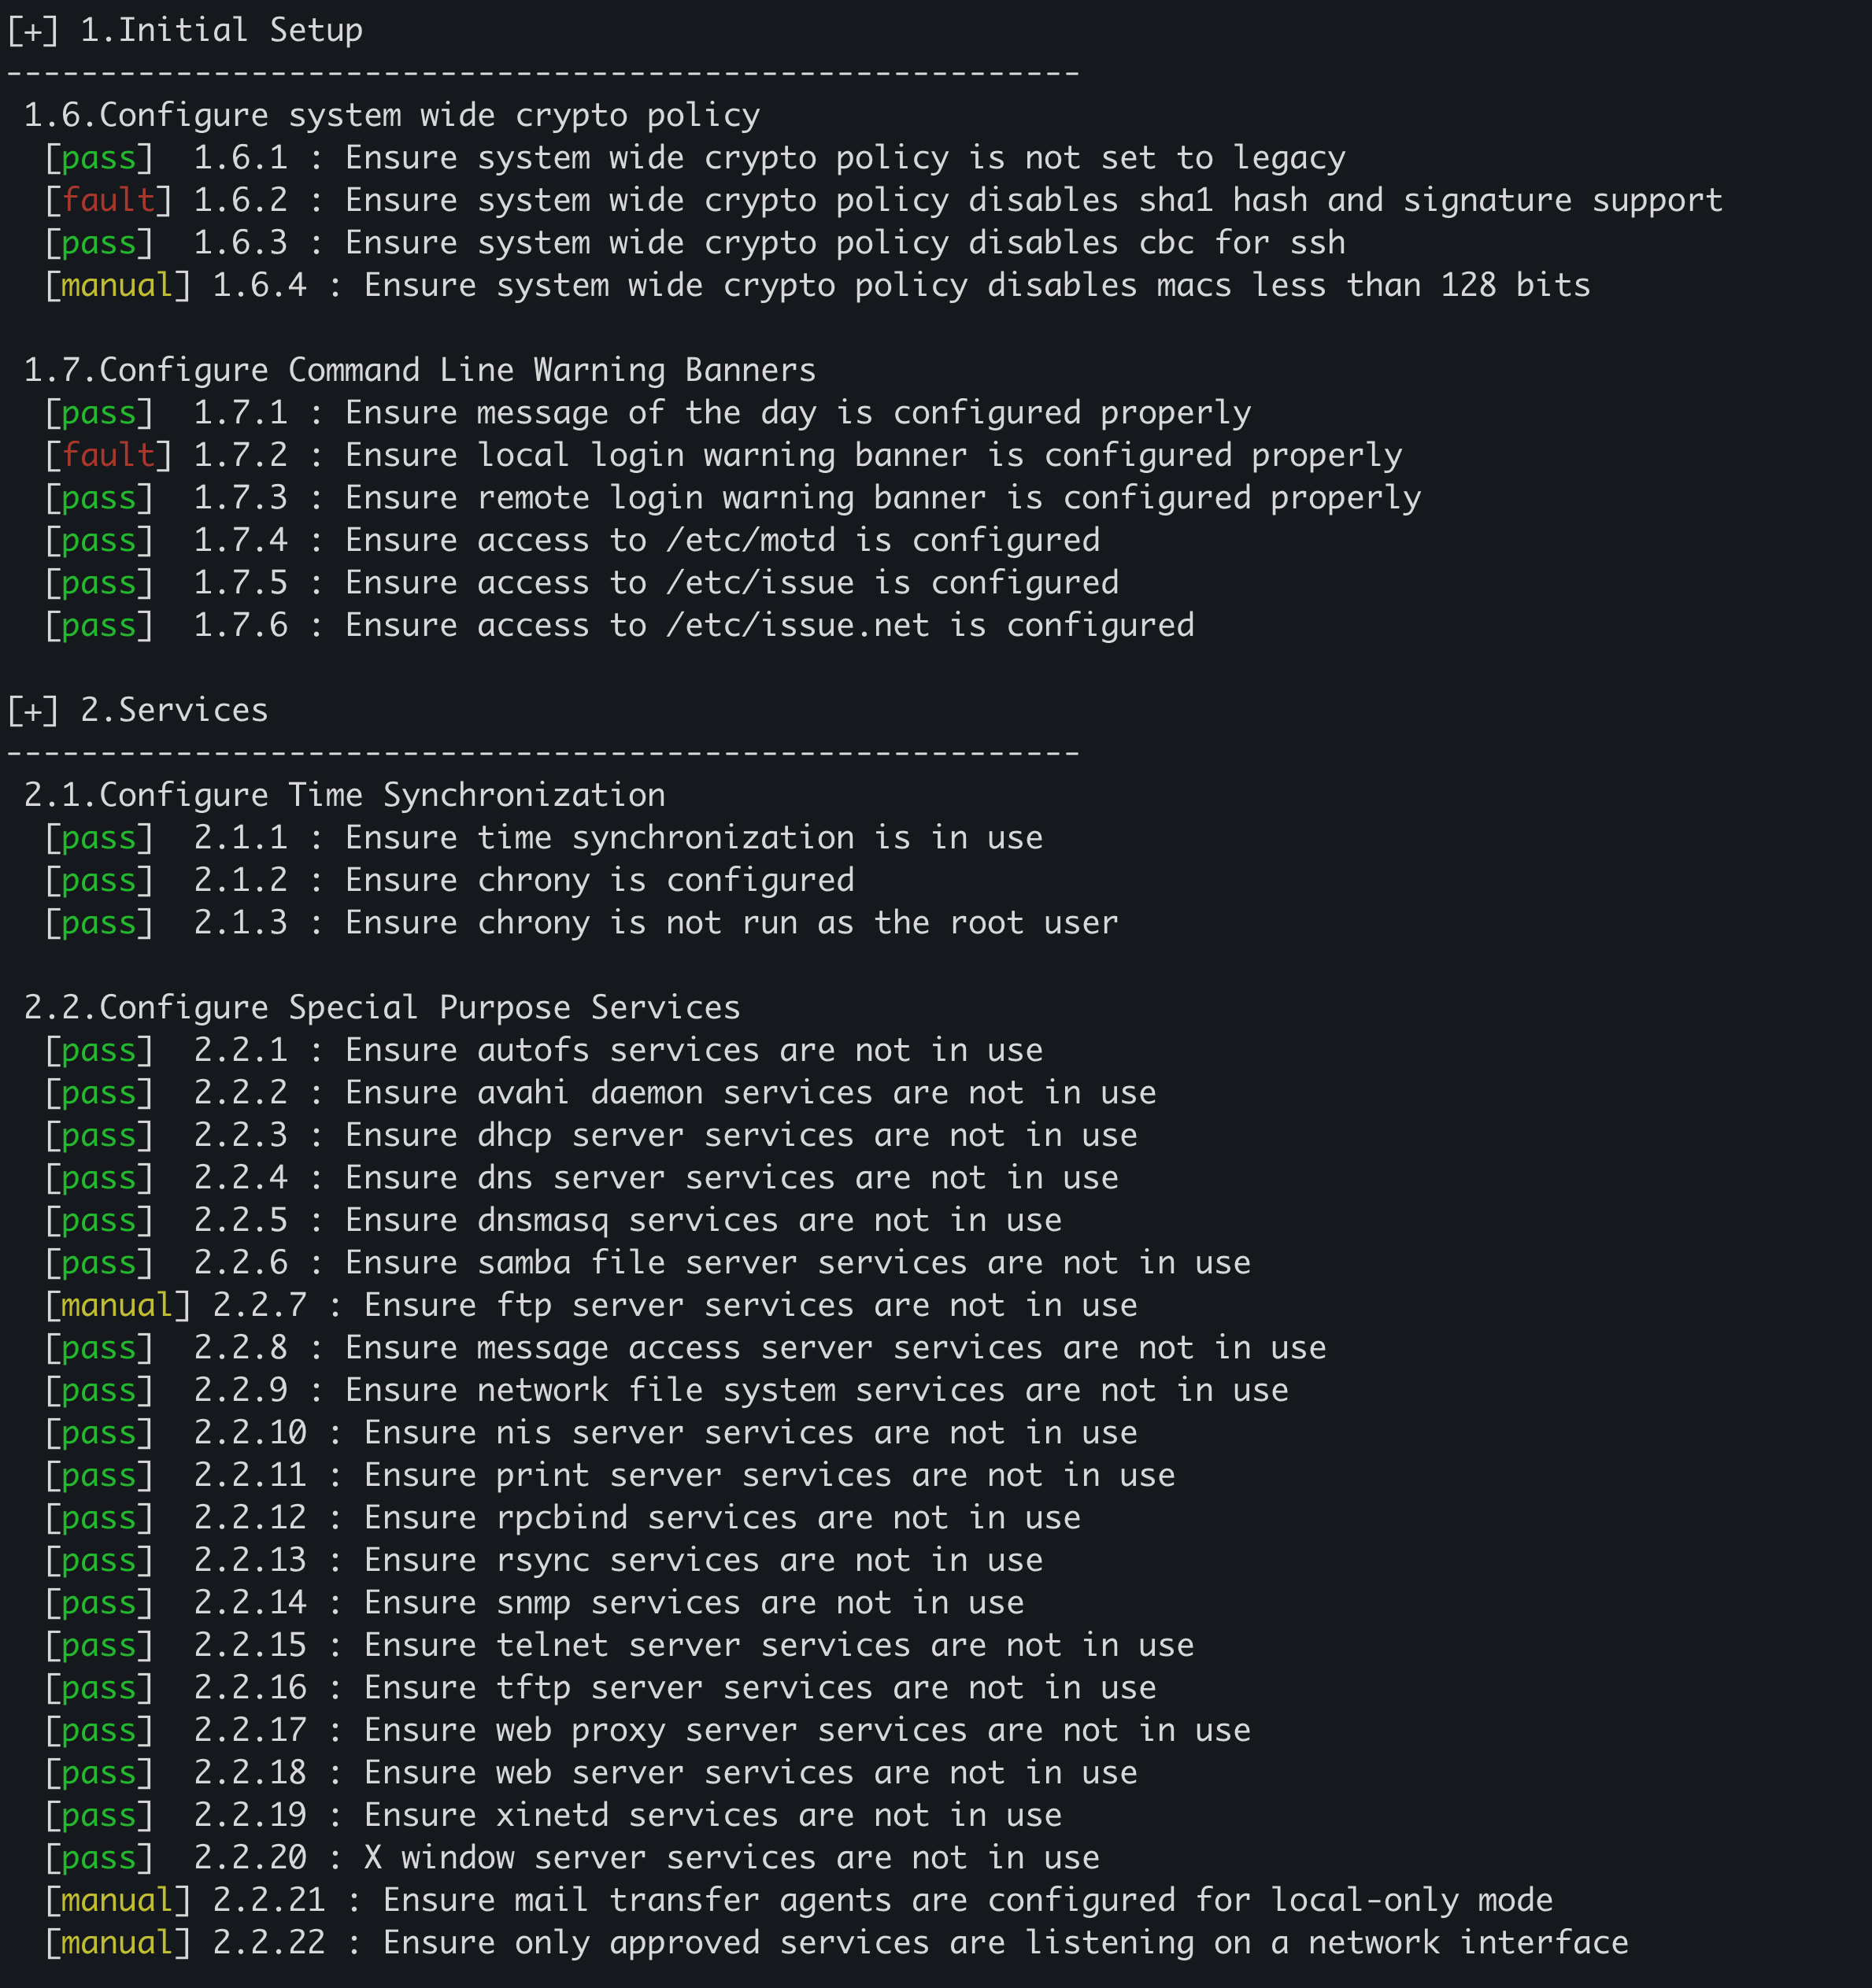
A UNIX security auditing tool based on several security frameworks

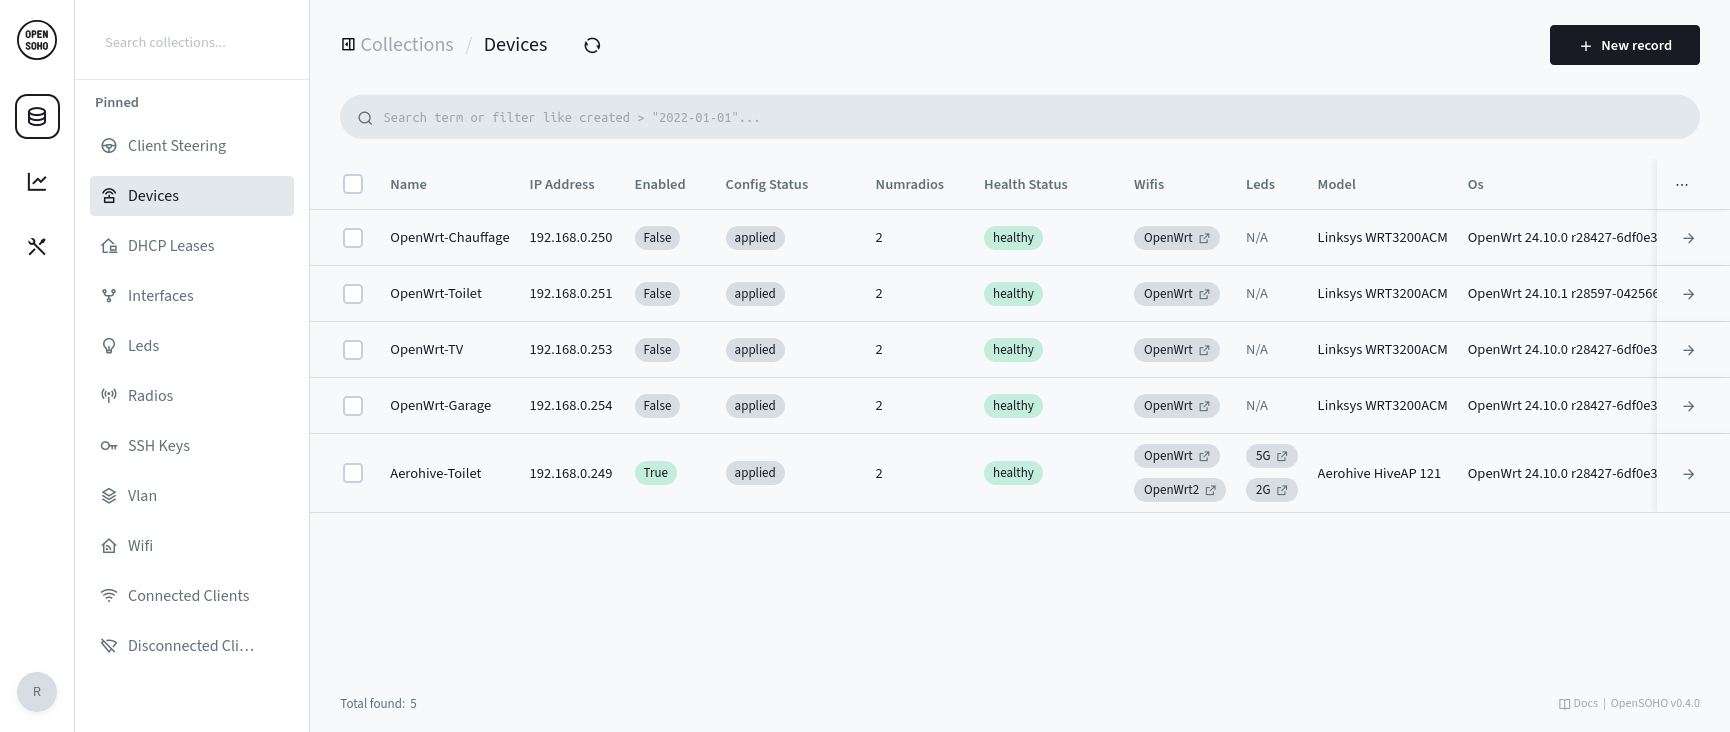
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…

Audit Preference Pane and Log Reader for OS X

Automated Linux security auditing tool that checks 130+ CIS benchmark items for RHEL-based systems, generating detailed XML reports on system…

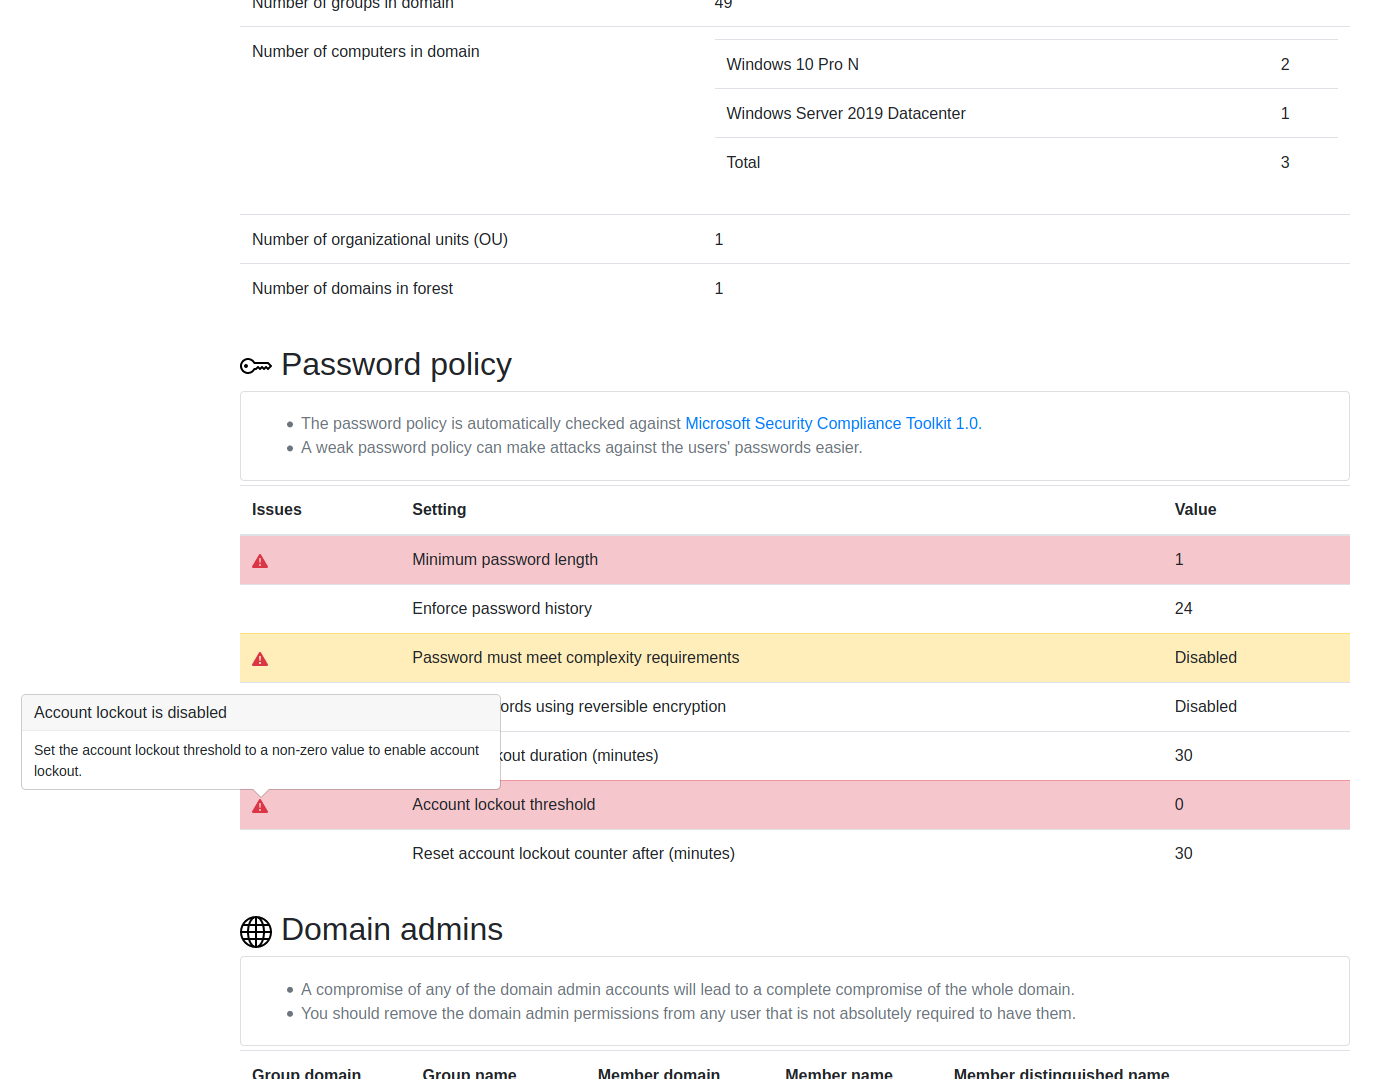
Tiuku is a tool for scanning various kinds of systems and environments for security related information and displaying the results in a browser-based…

🛡️ Script to test for NGINX CVE-2026-42945

Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…

Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…

Browser-based network connectivity checker for testing firewall rules, access restrictions, and corporate policy compliance. Supports HTTP Fetch and…

PowerShell script that applies a temporary registry-based mitigation for CVE-2026-21509, a Microsoft Office security feature bypass, with backup and…

Dockerized lab for training on NGINX rewrite vulnerability (CVE-2026-42945) with vulnerable and patched instances, benign test scripts, and…

Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…

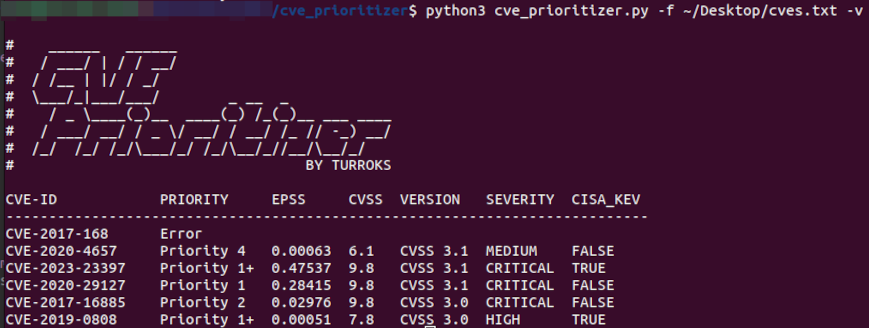
Streamline vulnerability patching with CVSS, EPSS, and CISA's Known Exploited Vulnerabilities. Prioritize actions based on real-time threat…

Vulnerability scanner based on vulners.com audit API

eBPF LSM based Mandatory Access Control and jailer

A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing