macOS-enterprise-privileges

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…

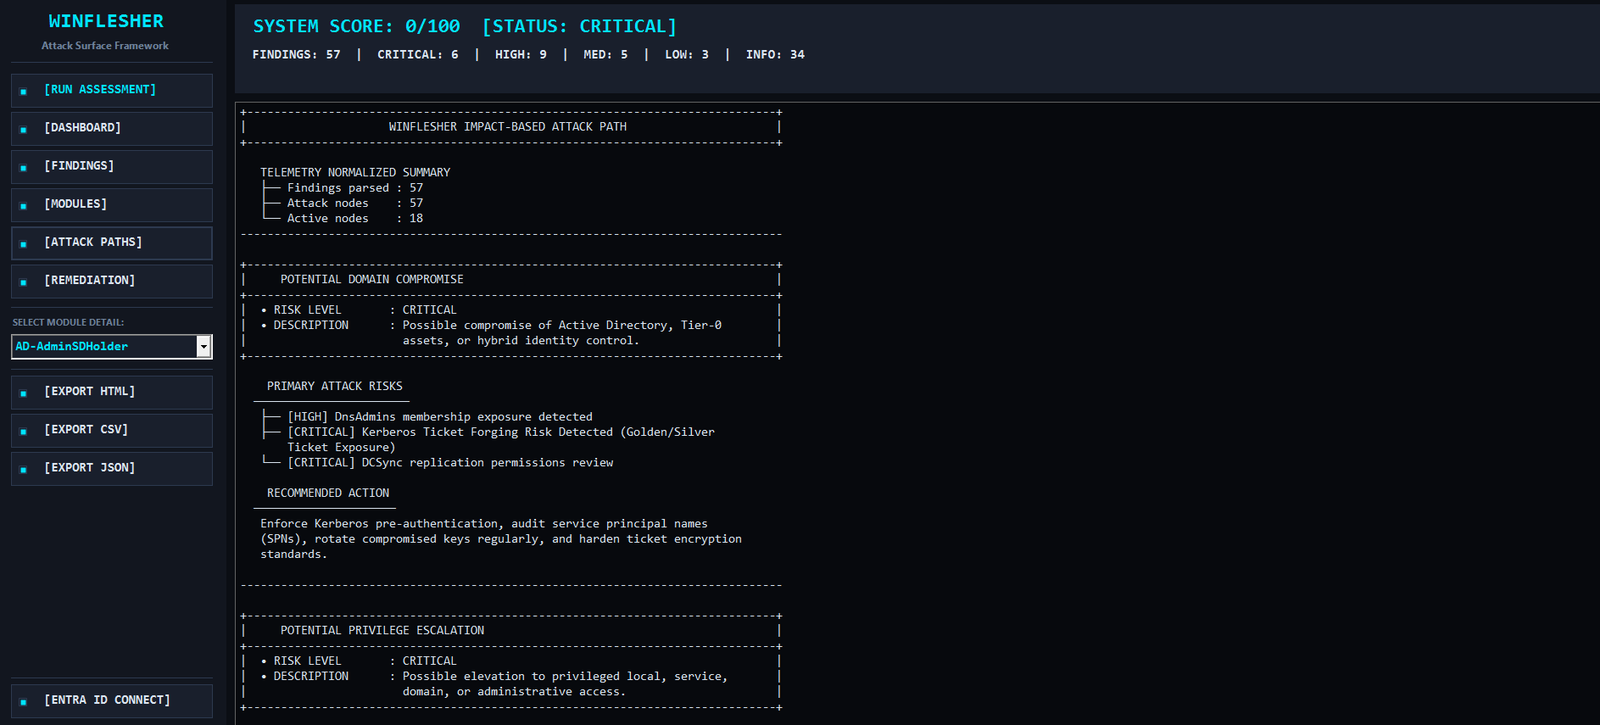
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…

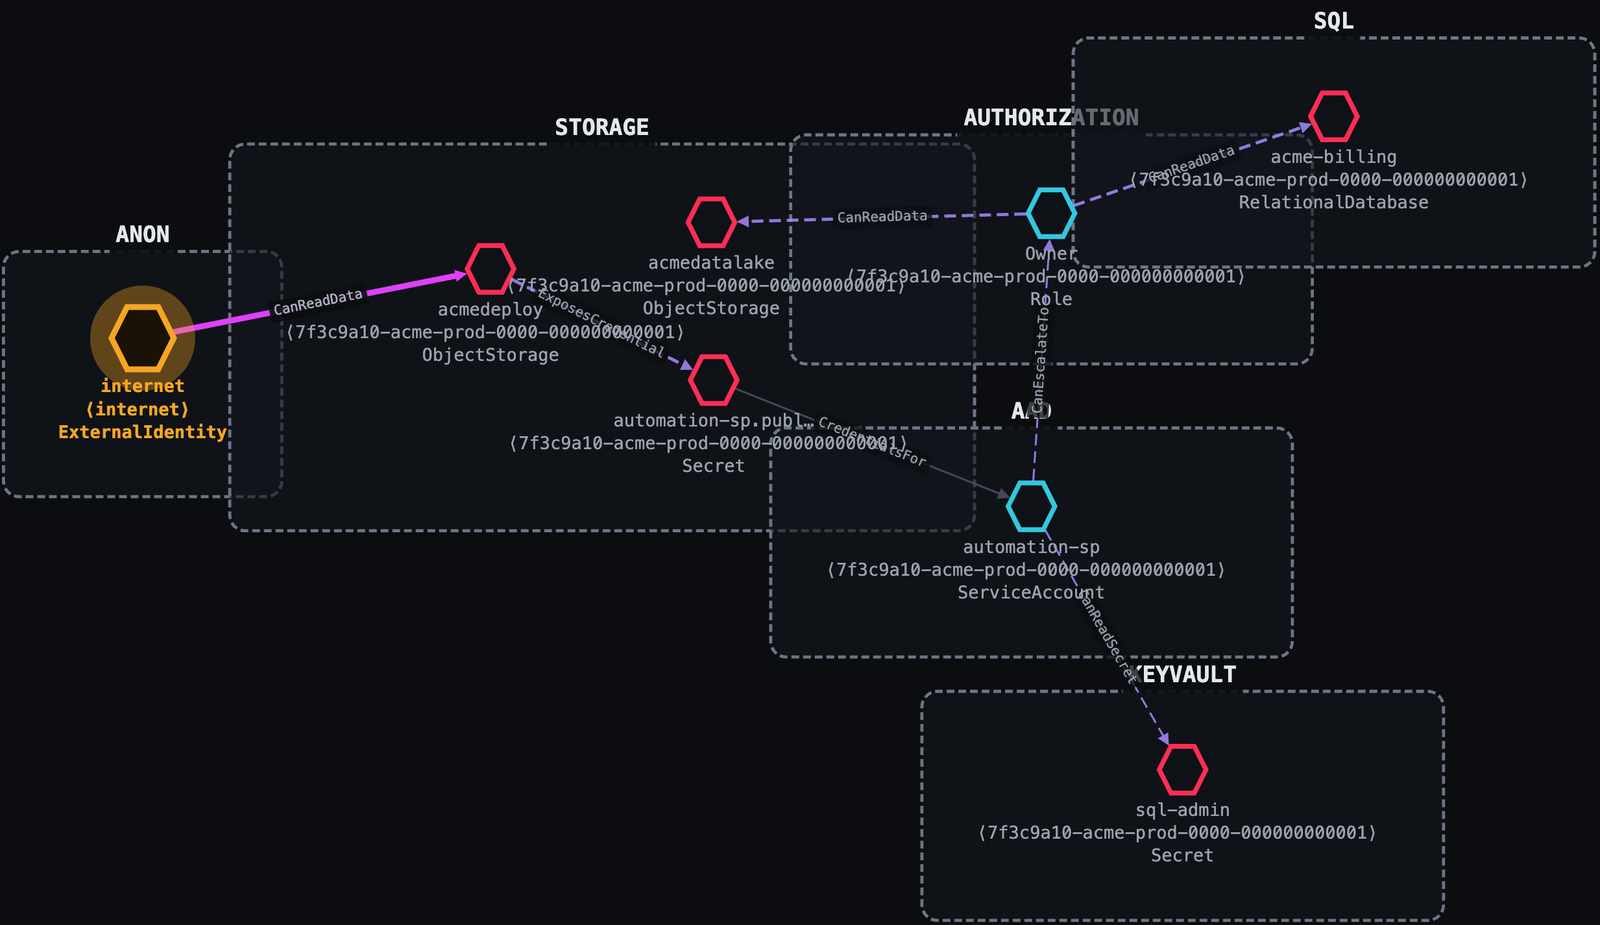
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

a guard that blocks catastrophic agent actions

Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.

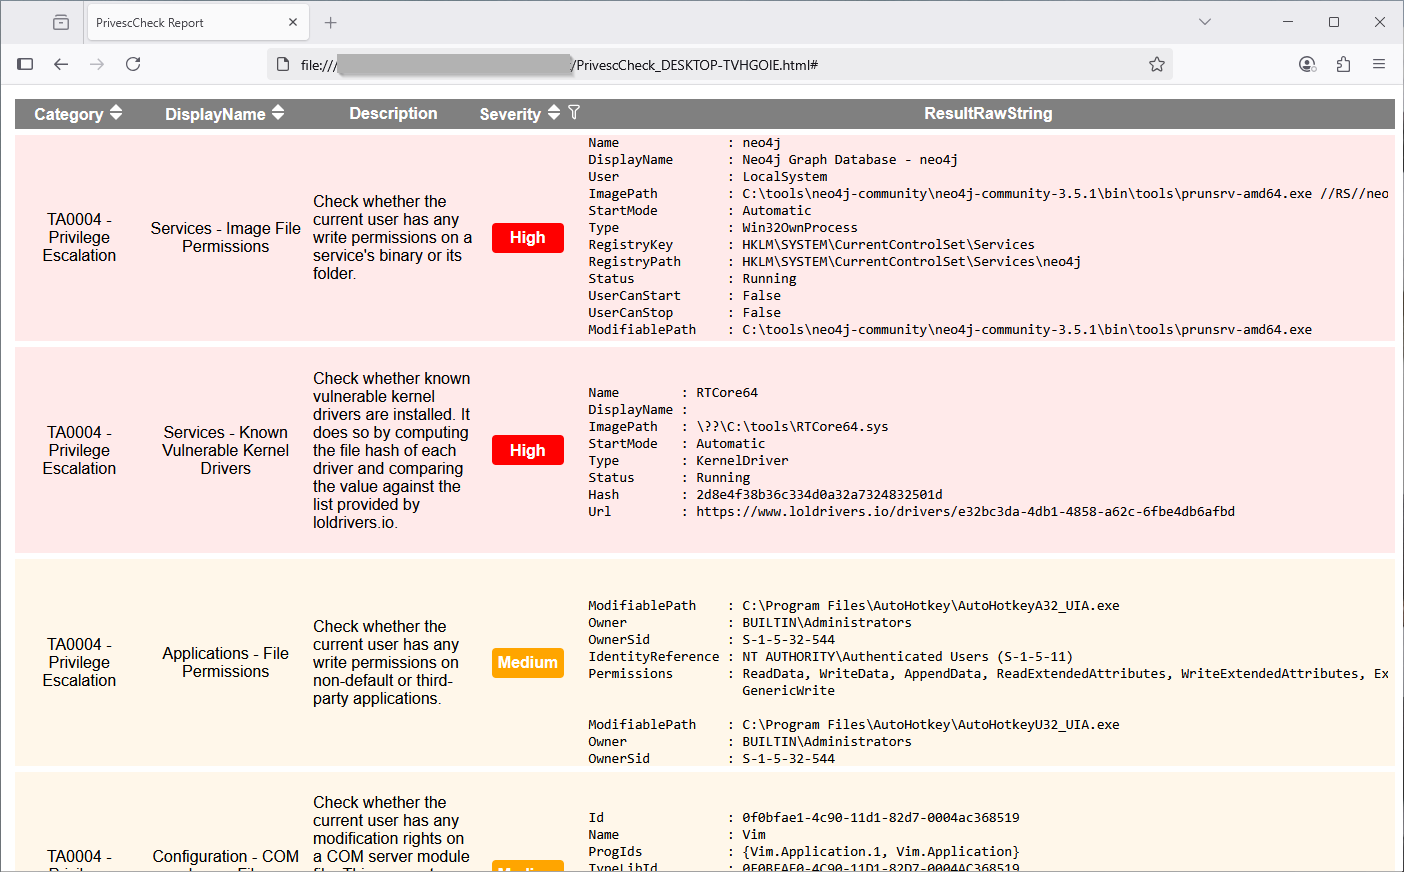
Privilege Escalation Enumeration Script for Windows

A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily

Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…

A C-based Linux security utility for detecting, safely verifying (Proof of Concept), and mitigating CVE-2026-64600 (RefluXFS). It provides kernel…

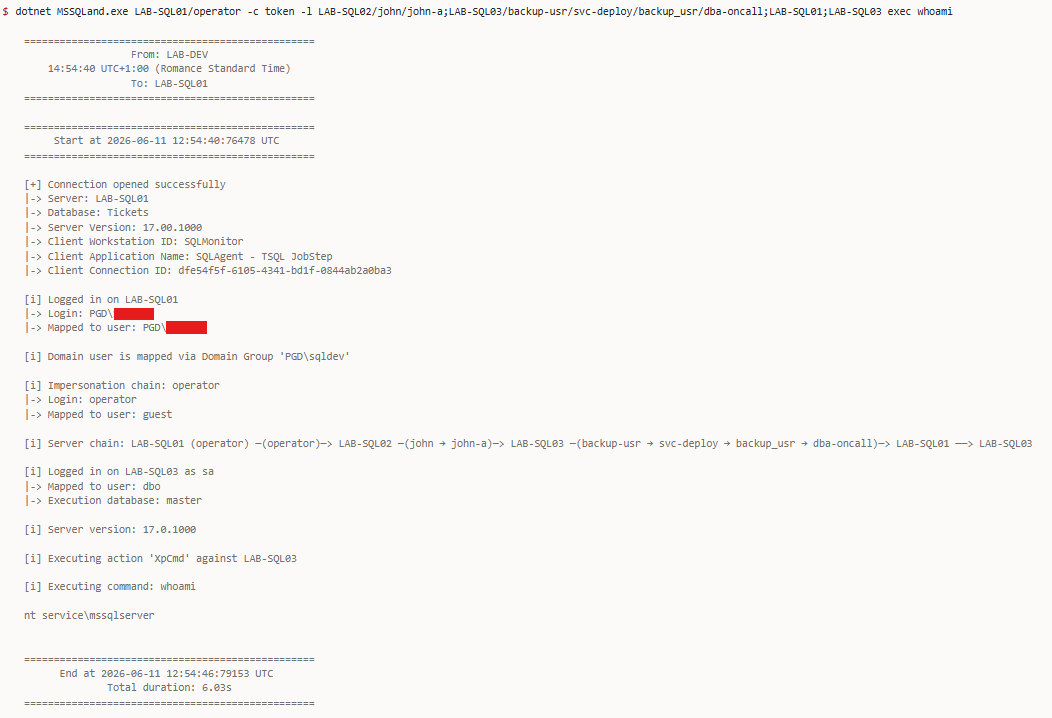
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…

Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data

A collection of scripts for assessing Microsoft Azure security

Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…

Proof-of-concept tool leveraging WinGet Configuration COM API to apply DSC configurations through Microsoft-signed binaries, enabling EDR bypass for…