

fleet
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
cloud-securityconfiguration-auditingdefensive-tools+4
6.9k
fleetdm/fleetOpen-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 itm4n/privesccheck
Privilege Escalation Enumeration Script for Windows
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
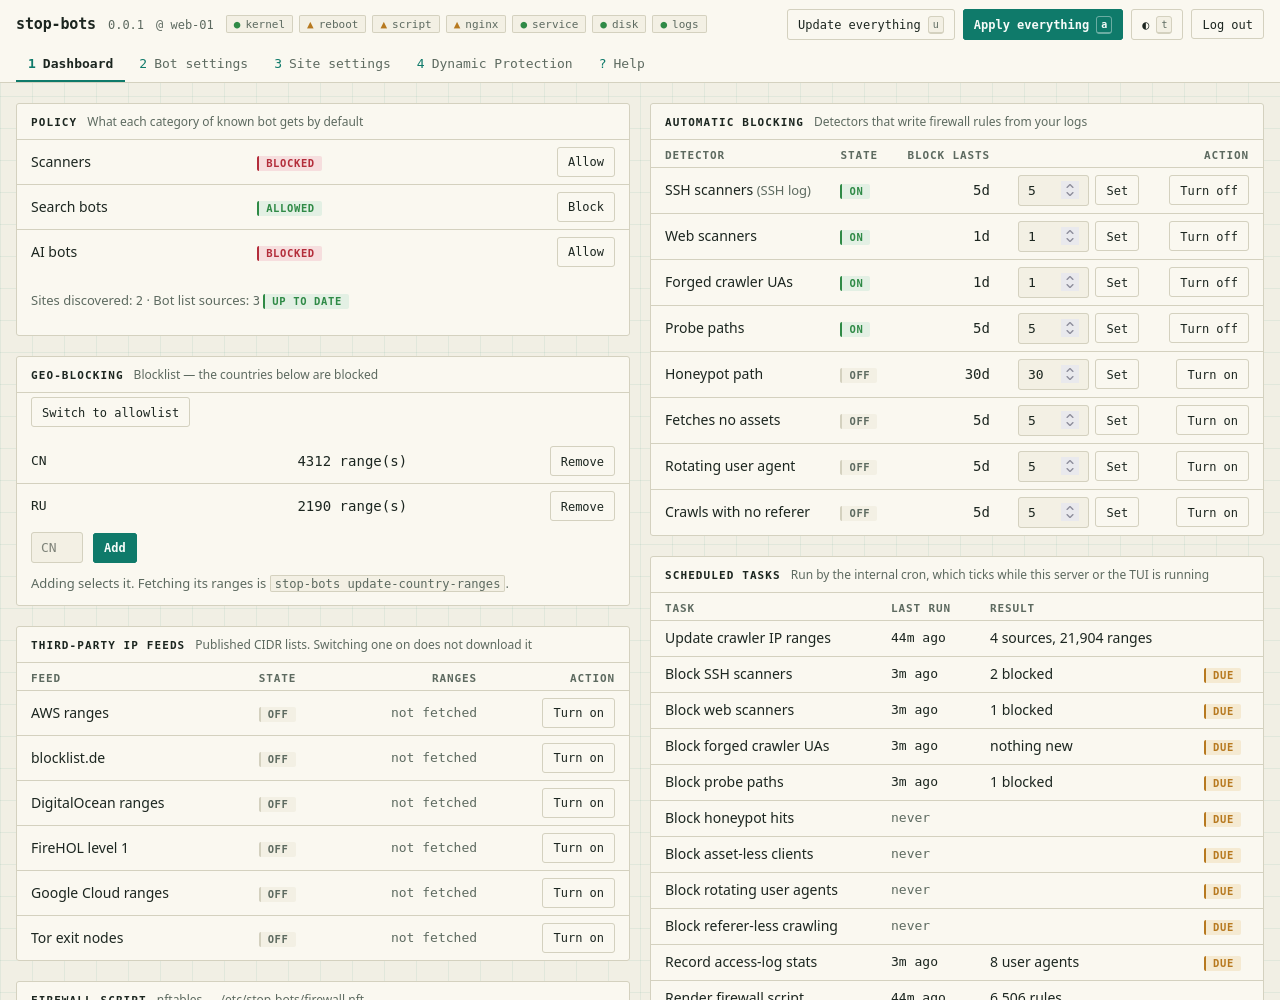 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 yellowkeybitlocker-cve/yellowkey-bitlocker-cve-2026-45585
YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…
 itskill-jp/wordpress-upgrade-check
Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…
 ssc-ict-innovatie/nl-kat-coordination
Modular network scanning framework that integrates diverse tools and external databases to detect vulnerabilities and configuration errors, producing…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 furkankayapinar/cve-2026-94127
Read-only defensive detector for CVE-2026-94127 in F5 BIG-IP APM. Fingerprints hosts, checks versions via iControl REST, and verifies OAuth…
 nocoderrandom/sunsetscan
Local-network security auditing with EOL, CVE, device identity, and HTML reports
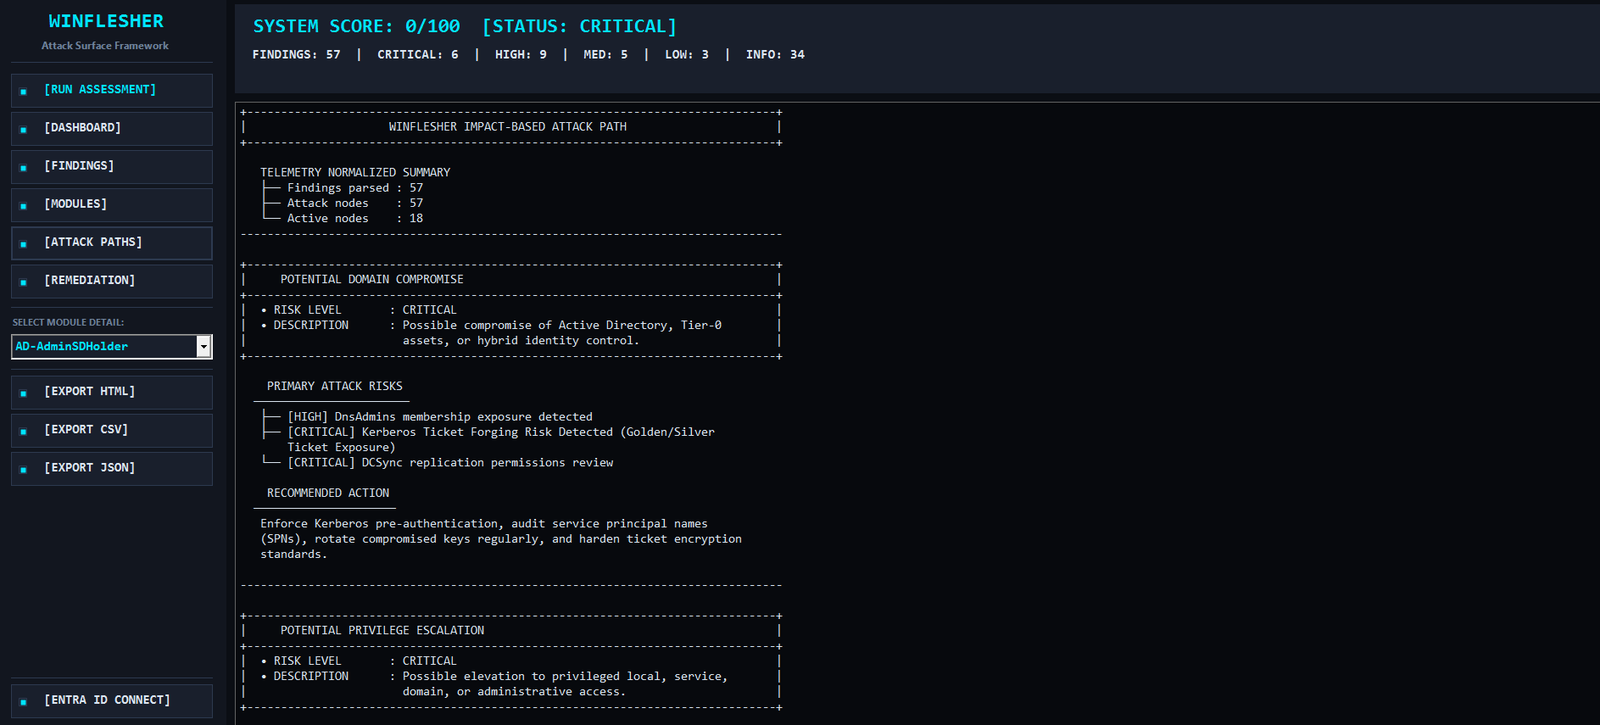 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
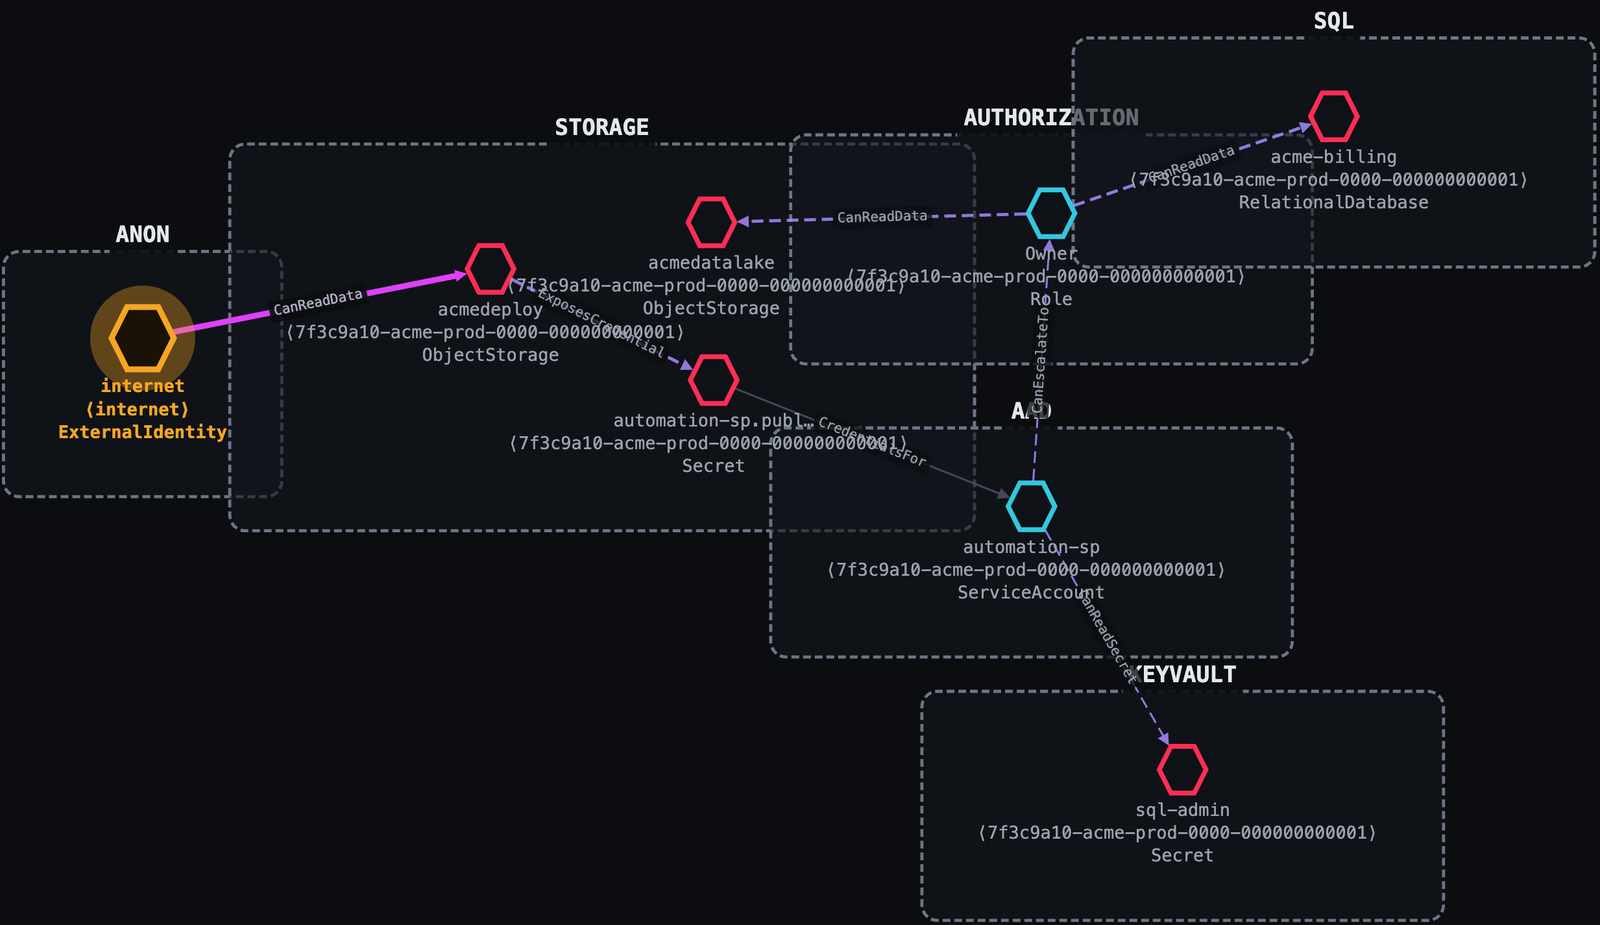 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
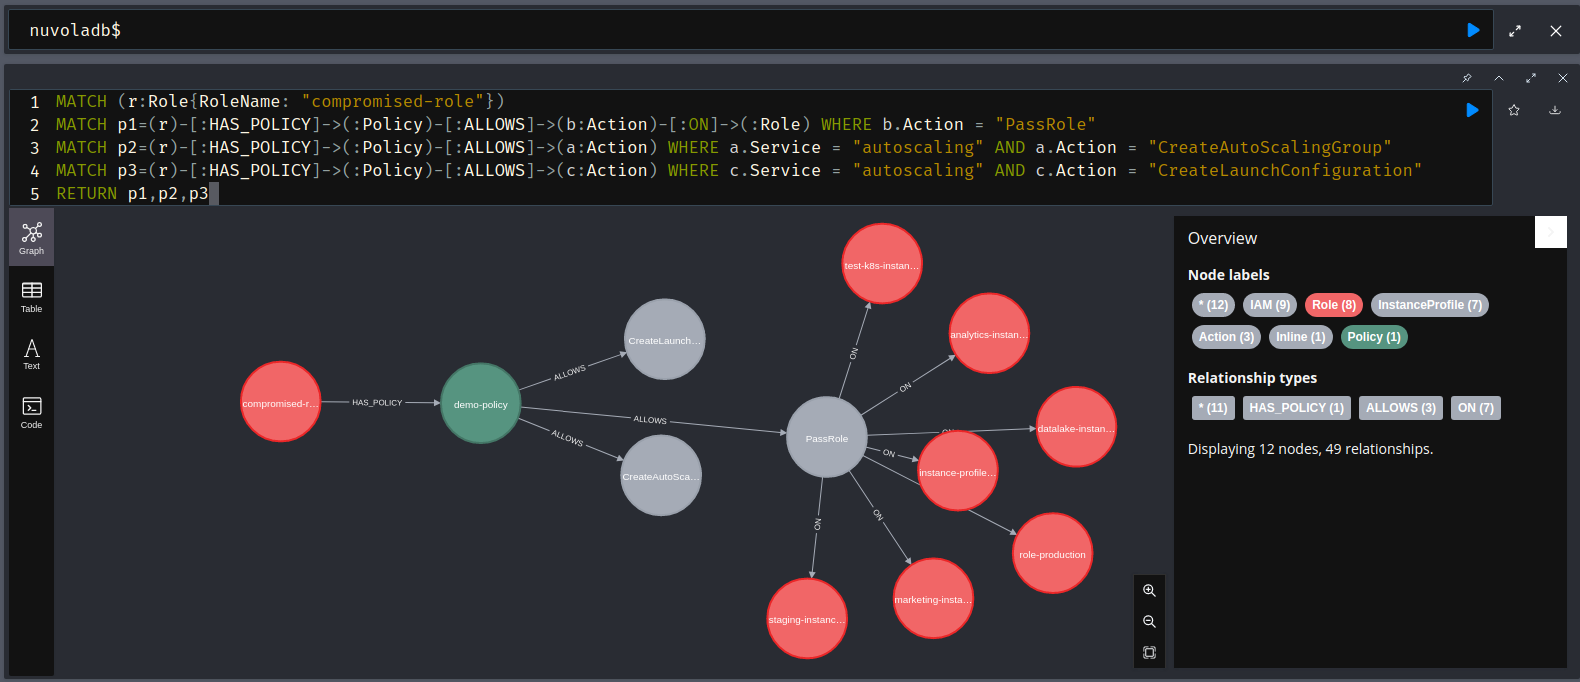 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…