
Locksmith2
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
configuration-auditingdefensive-toolseducation+8
126
jakehildreth/locksmith2An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 codesource/copyfail-check
Archived, moved to codesource/cve-check. Shell script to detect CVE-2026-31431 (Copy Fail) exposure and mitigations on Linux systems: kernel check,…
 krisiasty/vcheck
Vulnerability detection and mitigation tool for Copy Fail and Dirty Frag bugs (CVE-2026-31431, CVE-2026-43284, CVE-2026-43500)
 evotecit/gpozaurr
Group Policy Eater is a PowerShell module that aims to gather information about Group Policies but also allows fixing issues that you may find in…
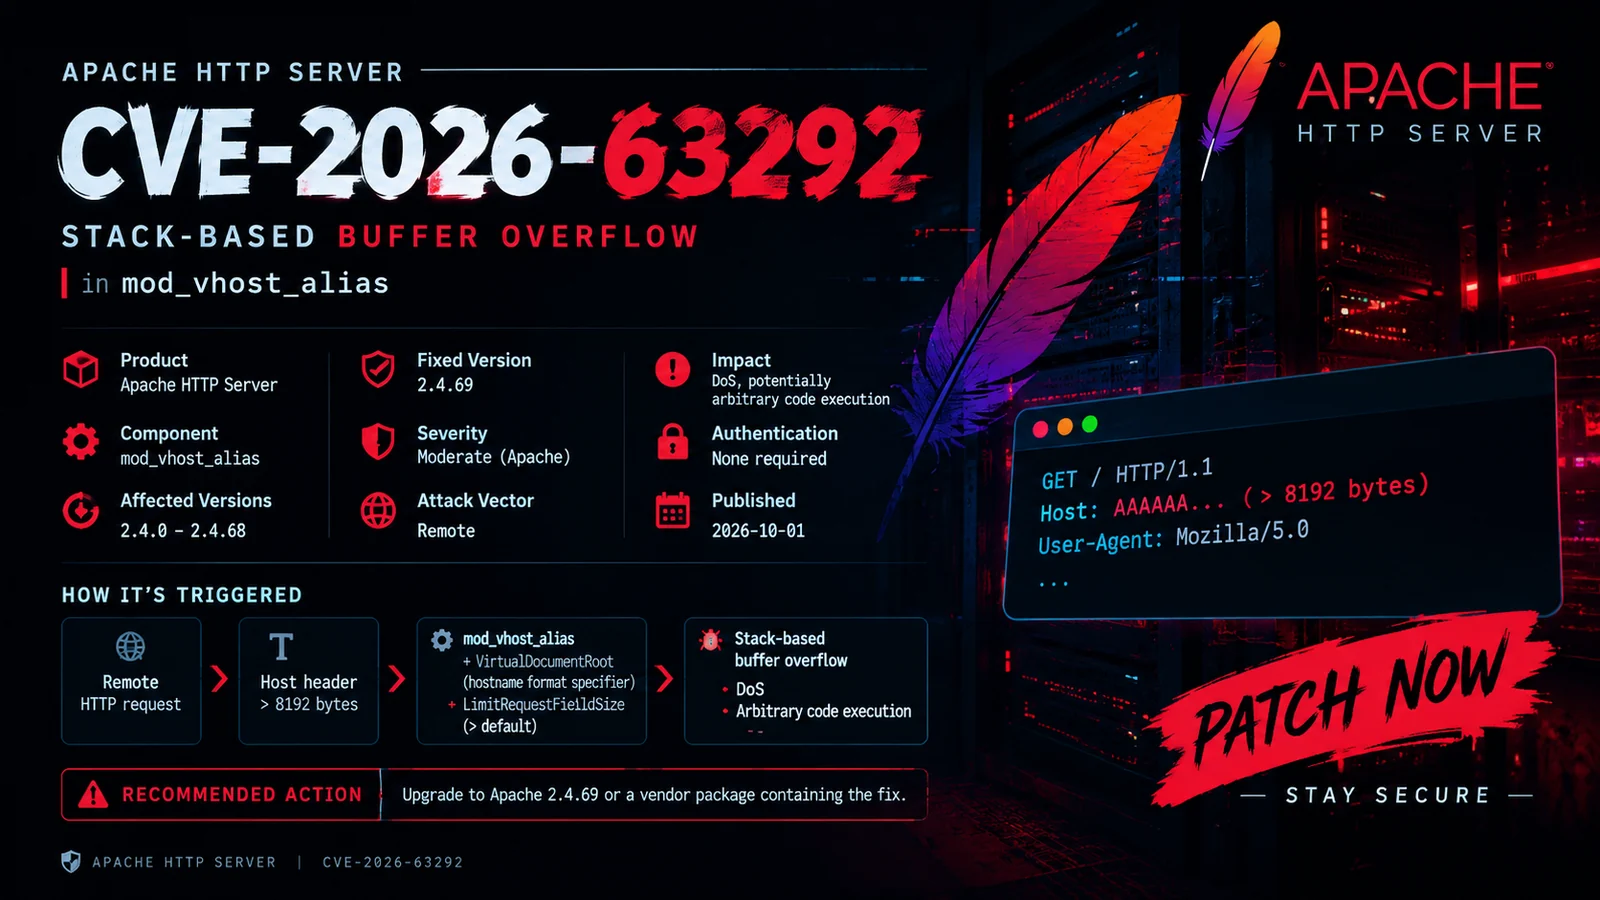 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 cynepmyx/nginx-rift-check
Detects the CVE-2026-42945 rewrite pattern in nginx configs: rewrite with ? in the replacement plus an unnamed capture consumed in the same location
 mahfuzreham/ovswrap-cve-2026-64531-mitigation-tool
Shell script that detects vulnerable Open vSwitch kernel modules, blocks automatic loading, removes the affected module, and verifies mitigation…
 fer1035_terraform/modules/terraform-aws-security-group
Terraform module to manage AWS Security Groups. Currently, the ingress and egress rules support IPv4, IPv6, and Security Group ID inputs.
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…
 friparia/nginx_rift_scan_cve_2026_42945
Nginx Rewrite CVE Scan(CVE-2026-42945 nginx-rift CVE-2026-9256)
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 yakovyakov/cve-2026-31431-mitigation
Detection and mitigation tooling for CVE-2026-31431 (Copy Fail) on Linux kernels. Includes Phalanx-CCS and Silent4Labs scripts plus an Ansible…
 gubiczap/cve-2026-31431-checker
Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 byezero/nginx-cve-2026-42945-check
Local read-only scanner for CVE-2026-42945 (NGINX Rift) that checks NGINX, OpenResty, and Tengine instances for vulnerable rewrite configurations…