CVE-2026-31431-Copy-Fail

Bash script to assess Linux host exposure to CVE-2026-31431, check kernel module status, apply mitigation by blocking algif_aead, and update kernel…

Bash script to assess Linux host exposure to CVE-2026-31431, check kernel module status, apply mitigation by blocking algif_aead, and update kernel…

Shell script that detects vulnerable Open vSwitch kernel modules, blocks automatic loading, removes the affected module, and verifies mitigation…

AWS Testing and Reporting Management Tool

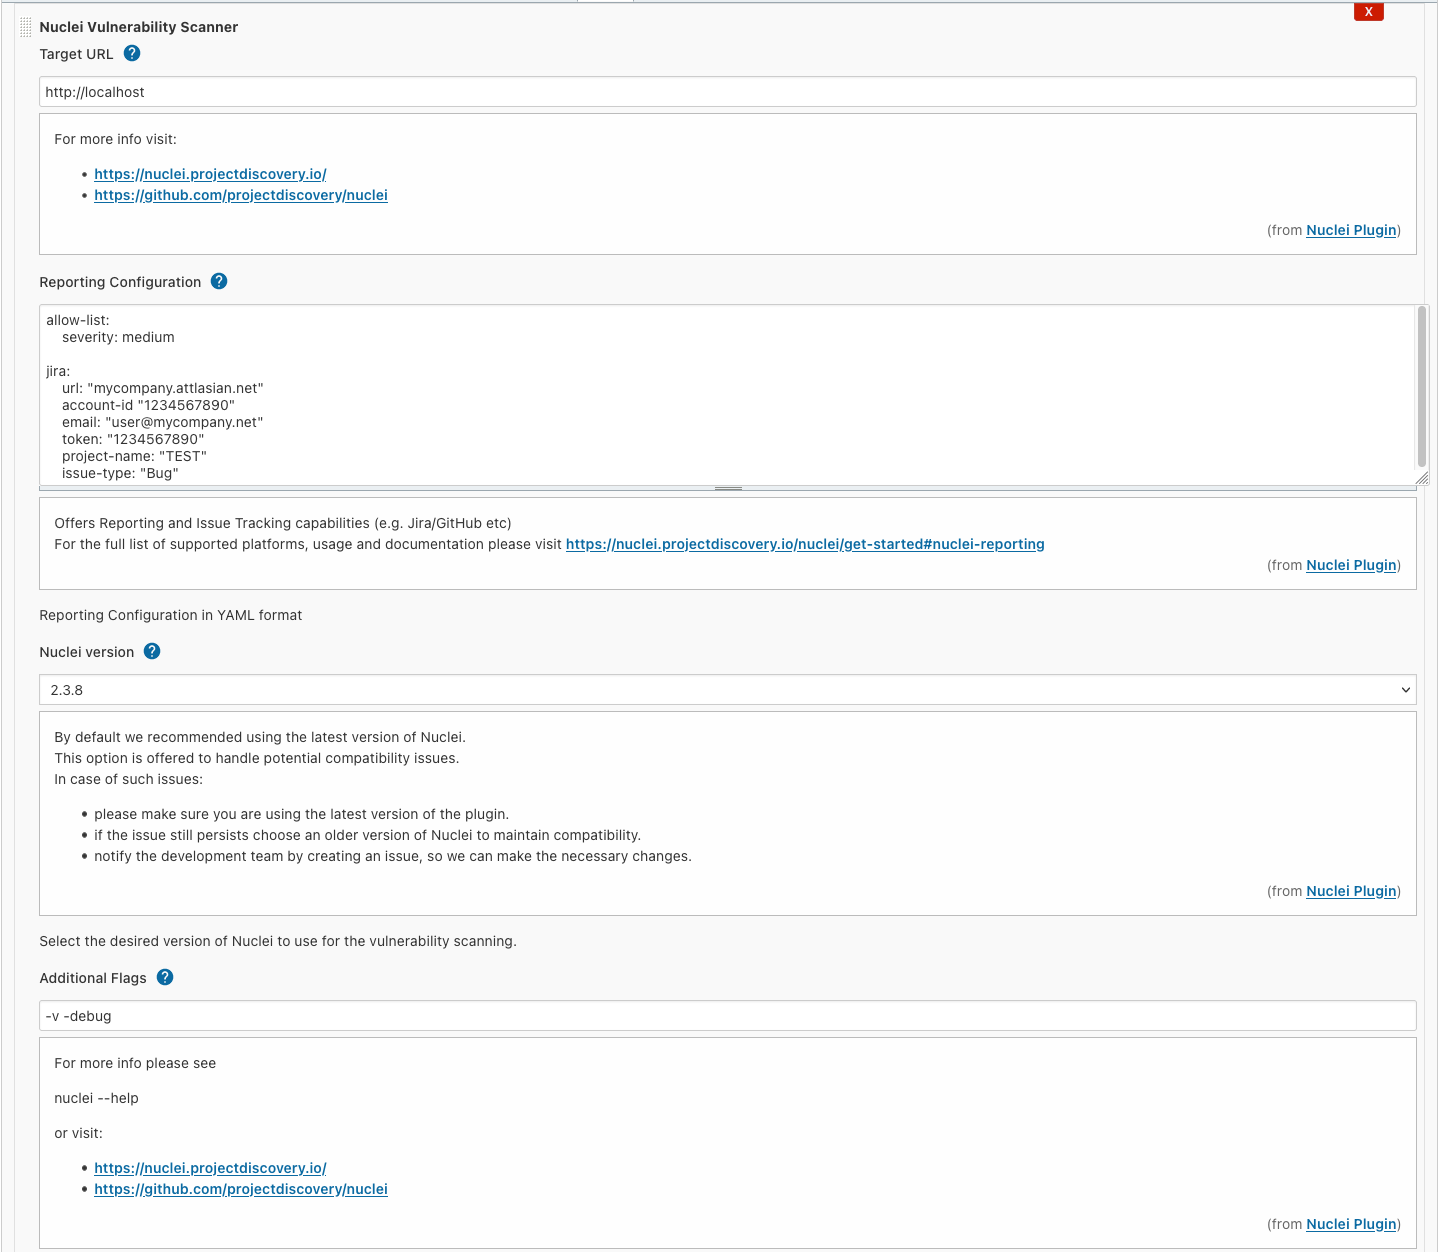
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.

The CVE-2022-30190-follina Workarounds Patch

Very simple Ansible playbook that scan filesystem for JAR files vulnerable to Log4Shell

Simple ansible playbook to patch mysql servers against CVE-2016-6662

Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…

Ansible playbook to detect and disable HTTP/HTTPS servers on Cisco IOS XE devices, mitigating CVE-2023-20198 vulnerability with automated…

test for the ioc described for FG-IR-22-398

Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…

Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.

A patch for PrintNightmare vulnerability that occurs to print spooler service for Windows machines [CVE-2021-34527]

Detect security issues in an Apache CouchDB server

Detect security issues, large or small, in a CouchDB server

A very simple way to find out which SSL ciphersuites are supported by a target.

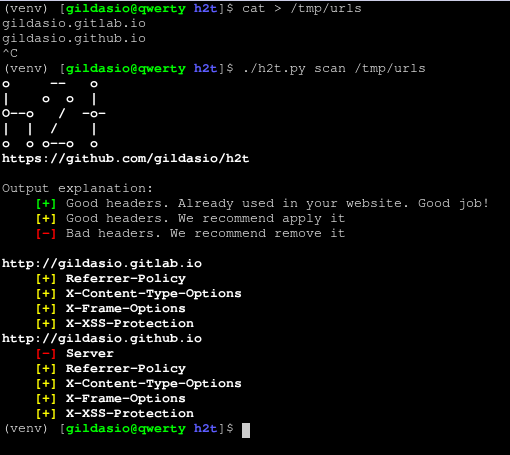
h2t (HTTP Hardening Tool) scans a website and suggests security headers to apply

Integration of Clair and Docker Registry