
CVE-2022-41404-DoS-Protection
 fdjy1234/cve-2022-41404-dos-protection
Windows Apache Tomcat resource limits implementation guide for CVE-2022-41404 DoS vulnerability protection
configuration-auditingdefensive-toolseducation+2
fdjy1234/cve-2022-41404-dos-protectionWindows Apache Tomcat resource limits implementation guide for CVE-2022-41404 DoS vulnerability protection
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 bohops/ultimatewdacbypasslist
A centralized resource for previously documented WDAC bypass techniques
 shoucheng3/fabric8io__kubernetes-client_cve-2021-4178_5-0-2
Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…
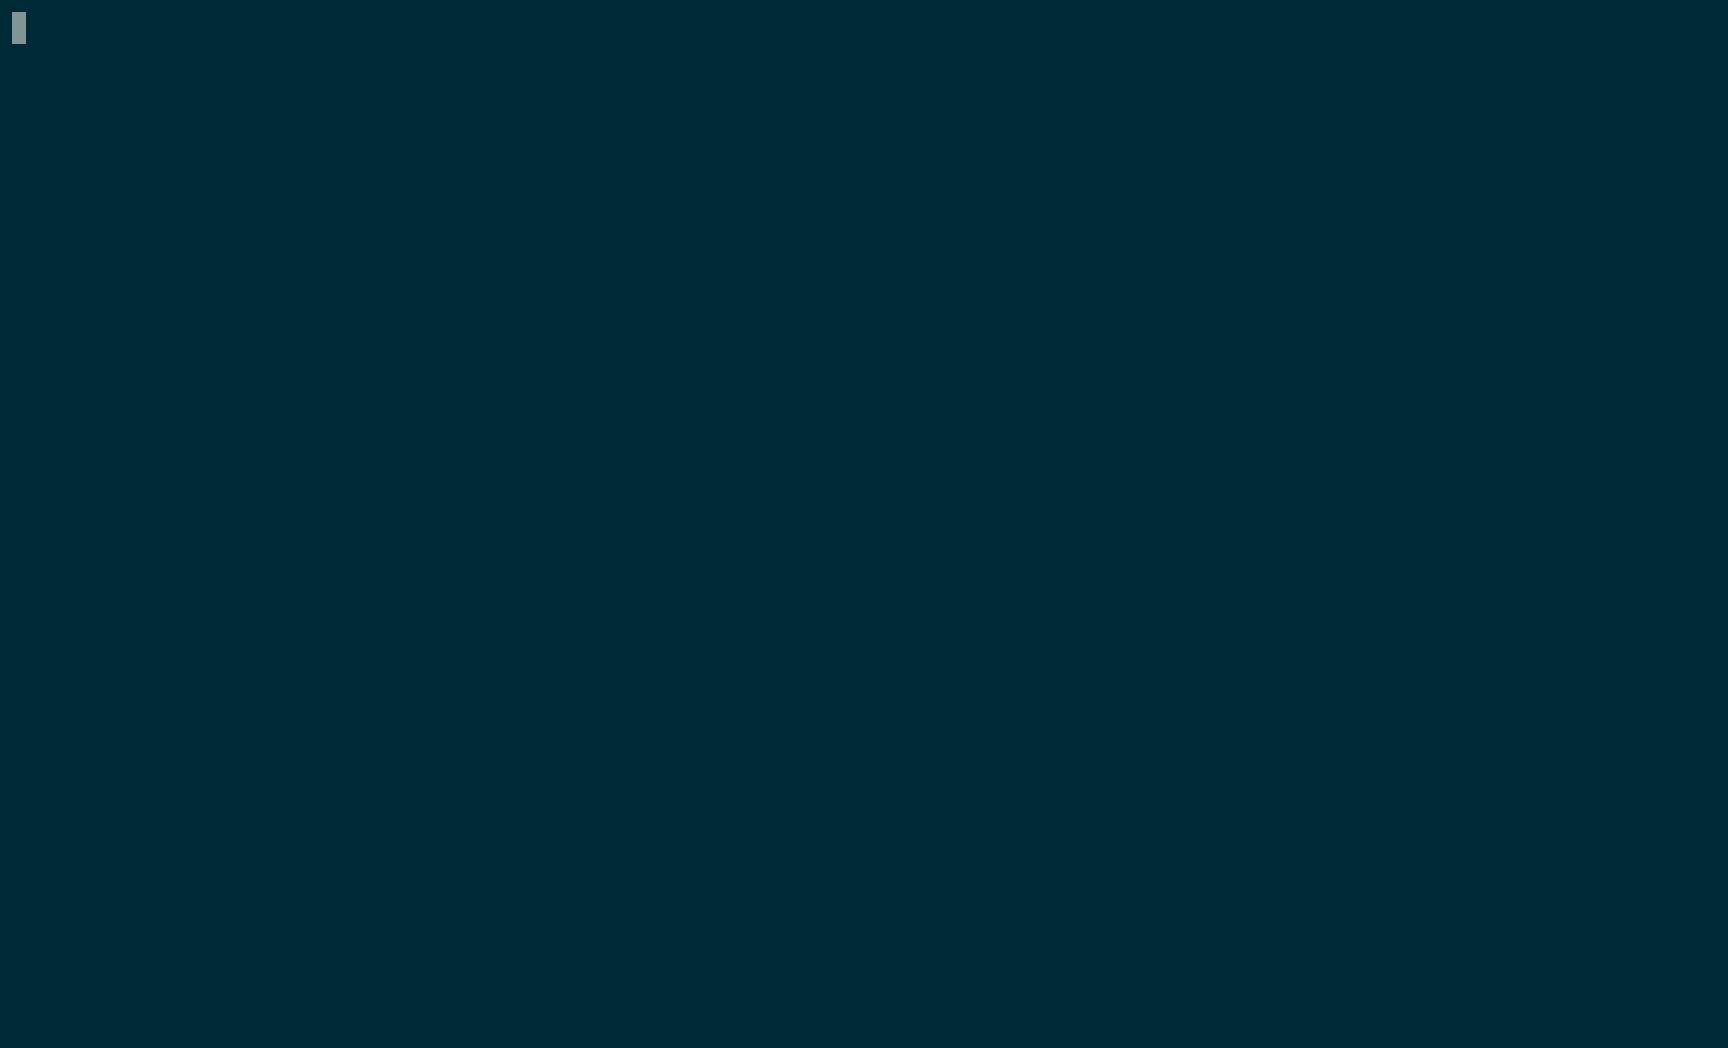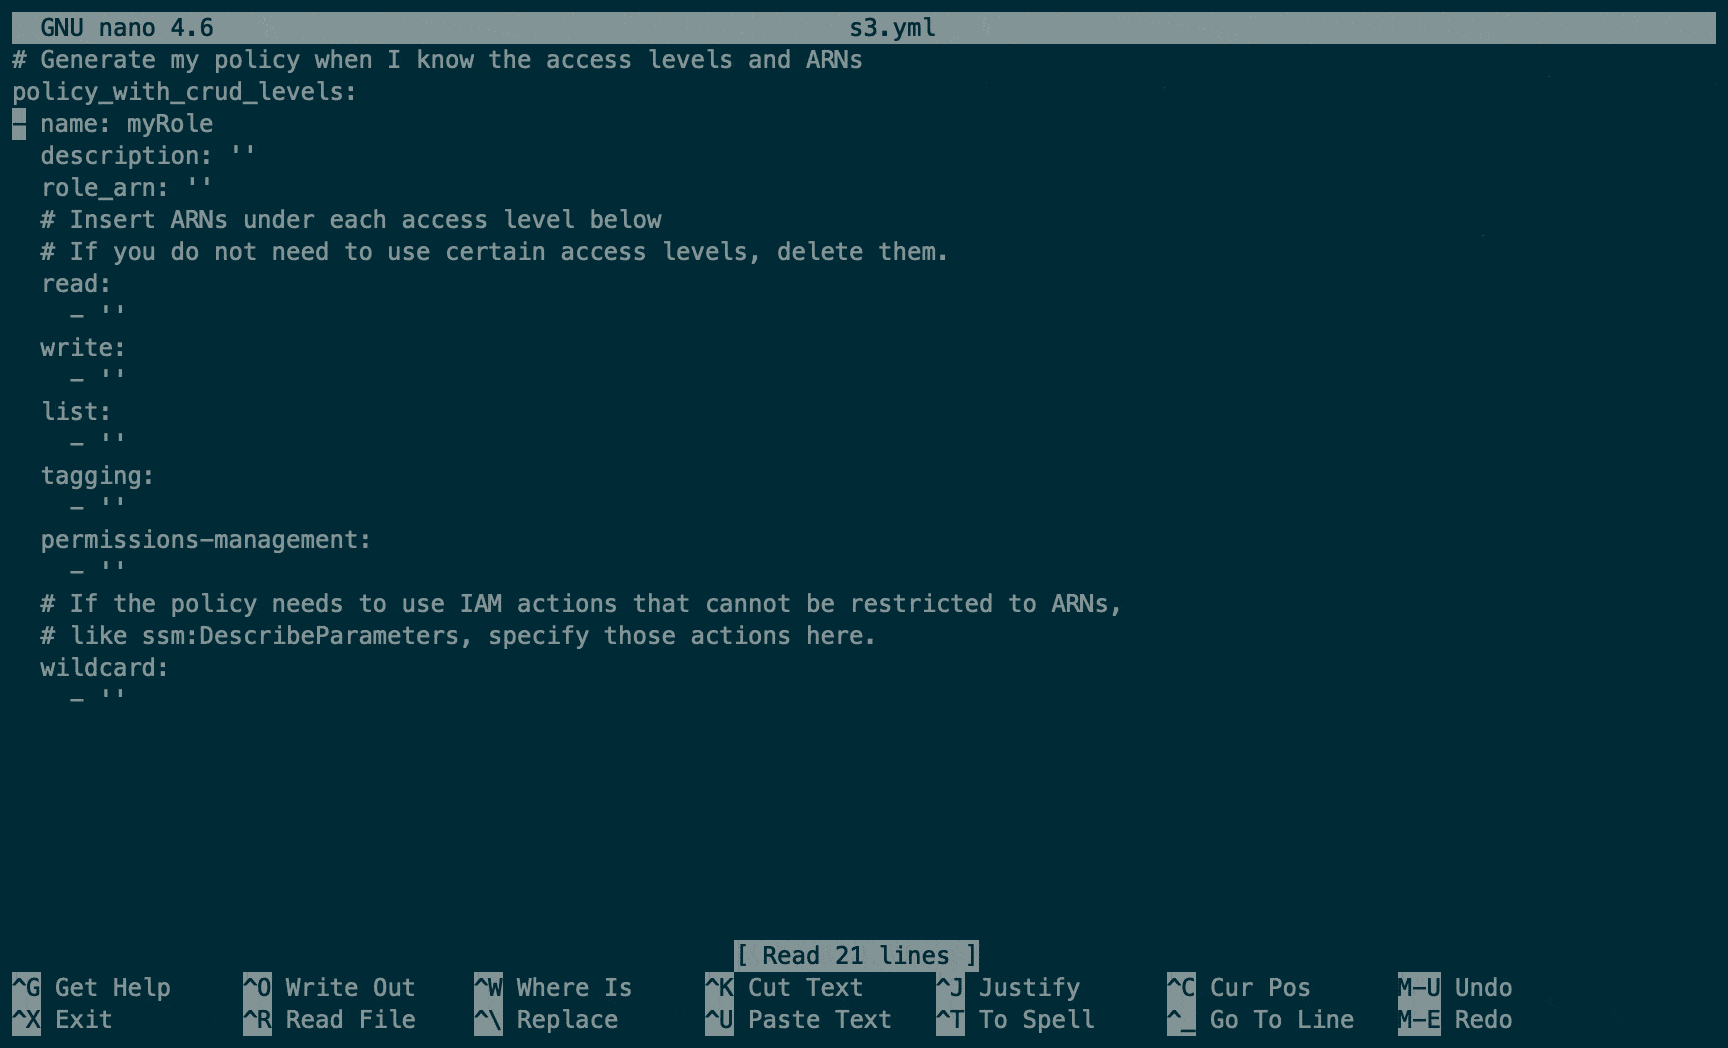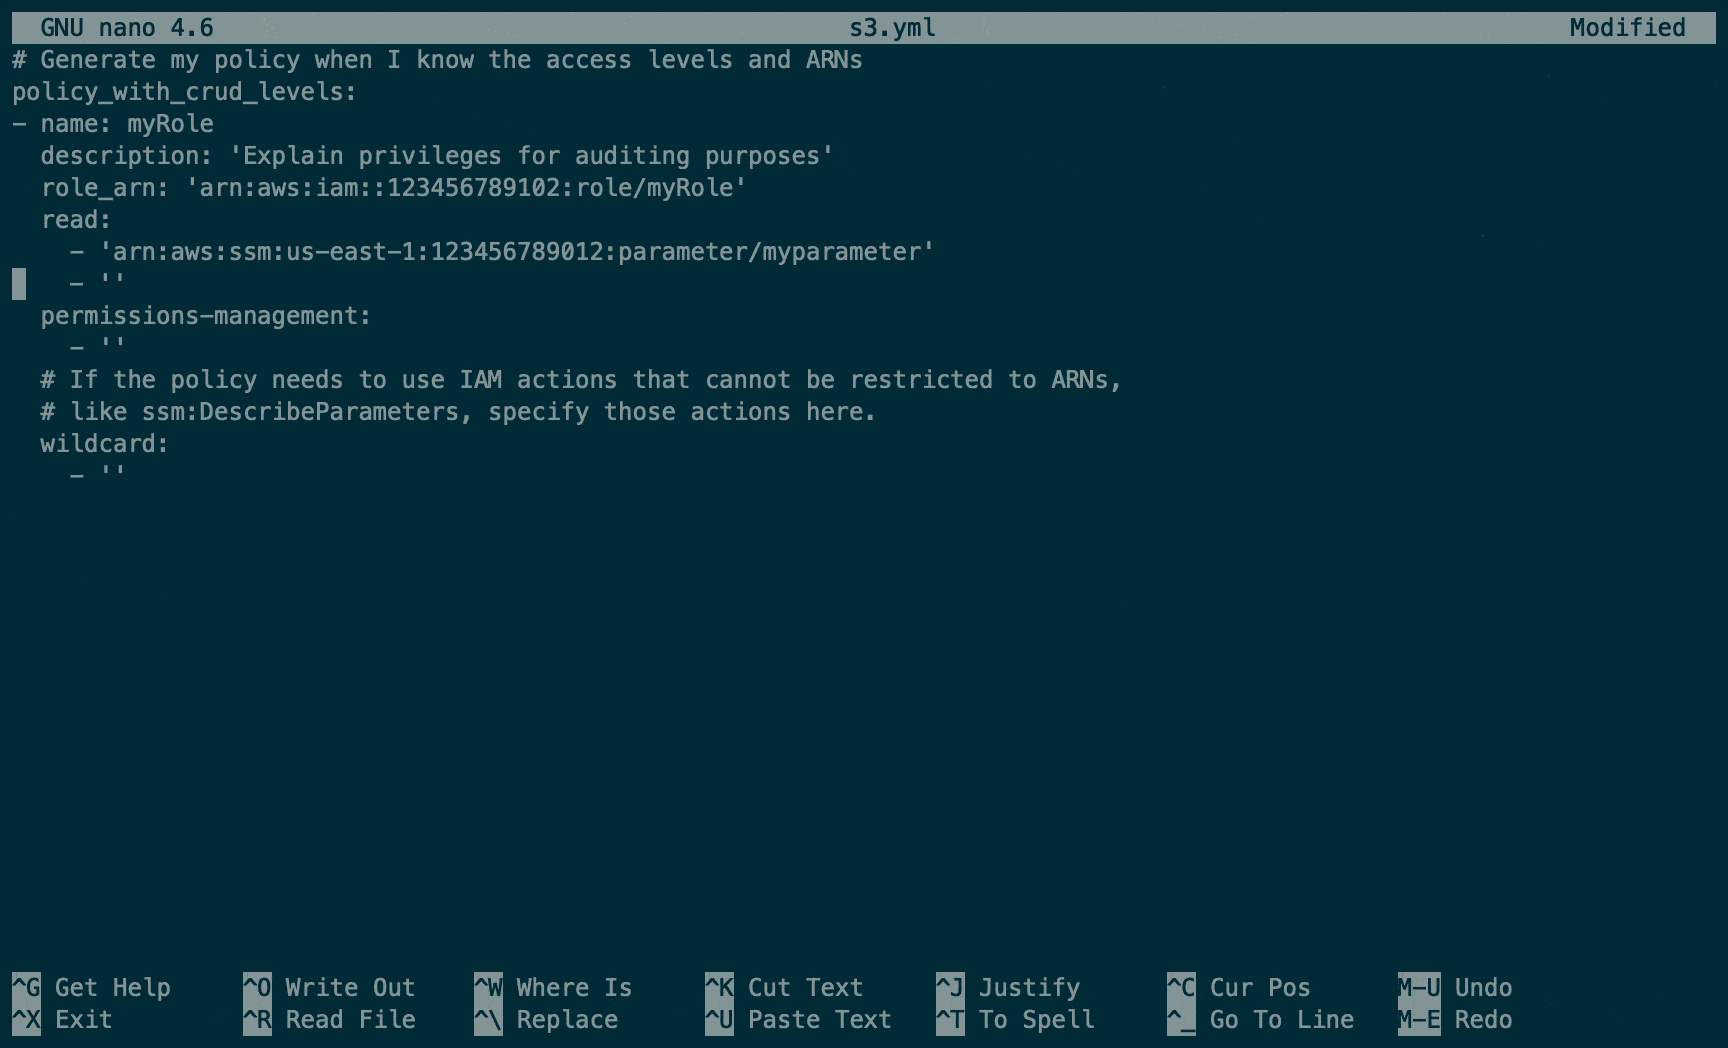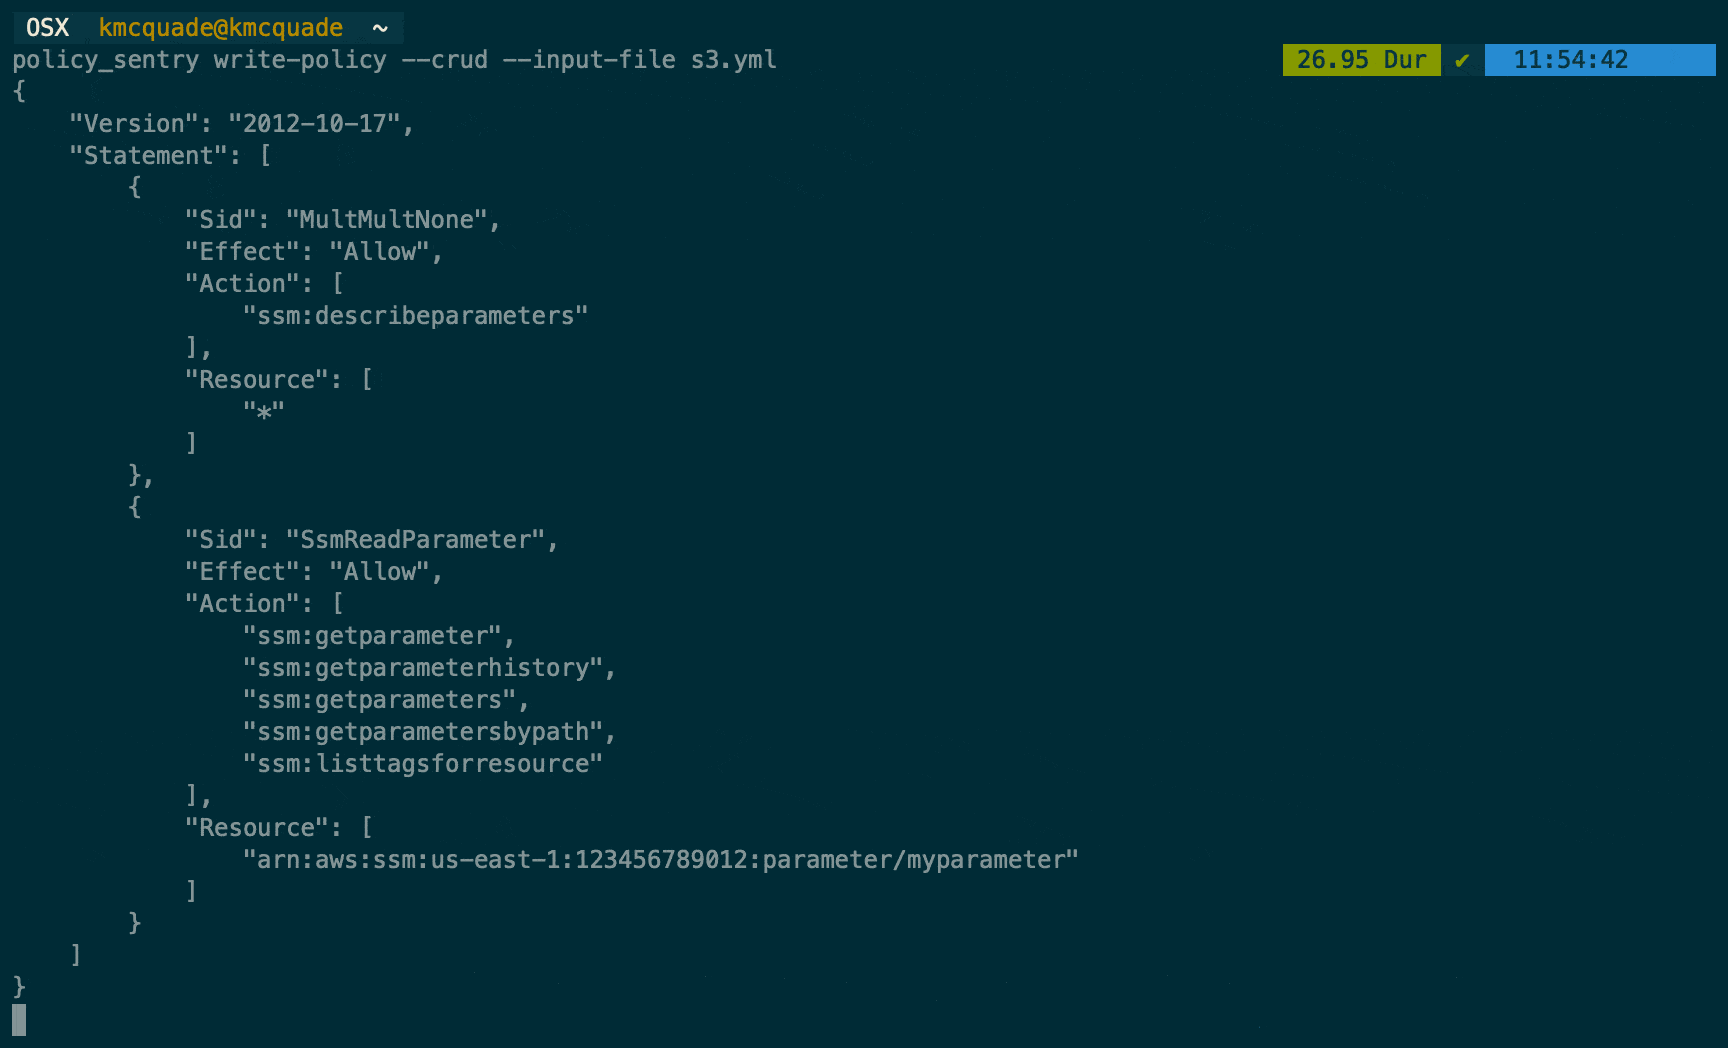 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 derailed/popeye
👀 A Kubernetes cluster resource sanitizer
 gabrielsoltz/metahub
Automated security findings enrichment and impact evaluation tool for AWS. Enriches vulnerability data with resource context, associations, and tags…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters