

kube-reaper
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
cloud-securityconfiguration-auditingcontainer-security+9
3
stillbigjosh/kube-reaperScans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 yellowkeybitlocker-cve/yellowkey-bitlocker-cve-2026-45585
YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…
 itskill-jp/wordpress-upgrade-check
Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…
 furkankayapinar/cve-2026-94127
Read-only defensive detector for CVE-2026-94127 in F5 BIG-IP APM. Fingerprints hosts, checks versions via iControl REST, and verifies OAuth…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
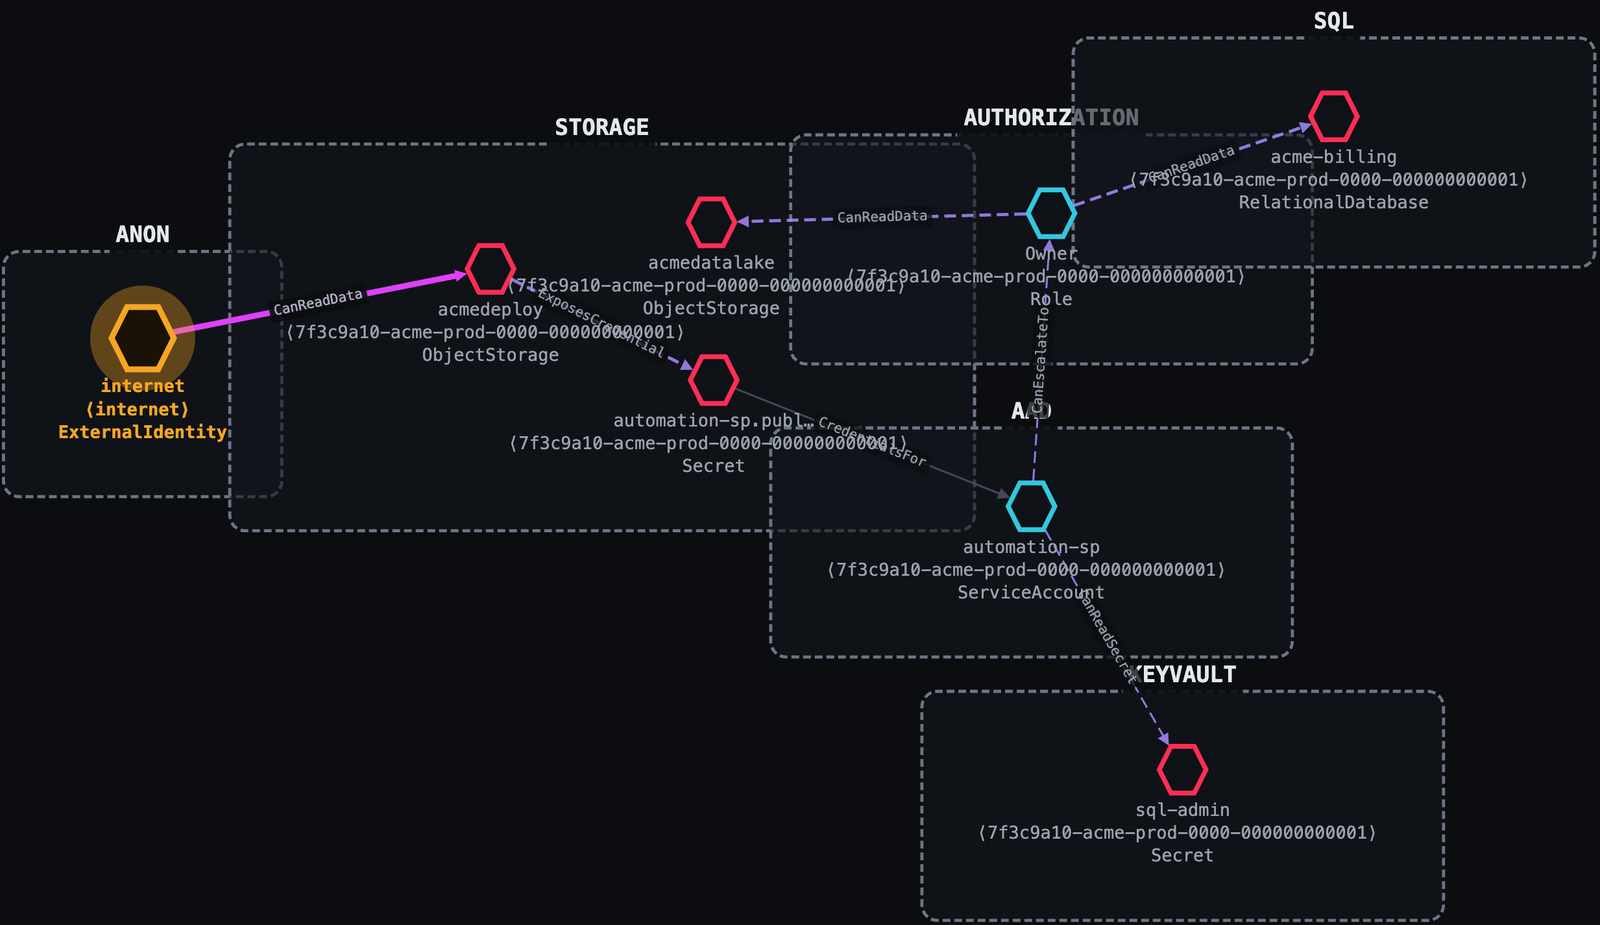 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
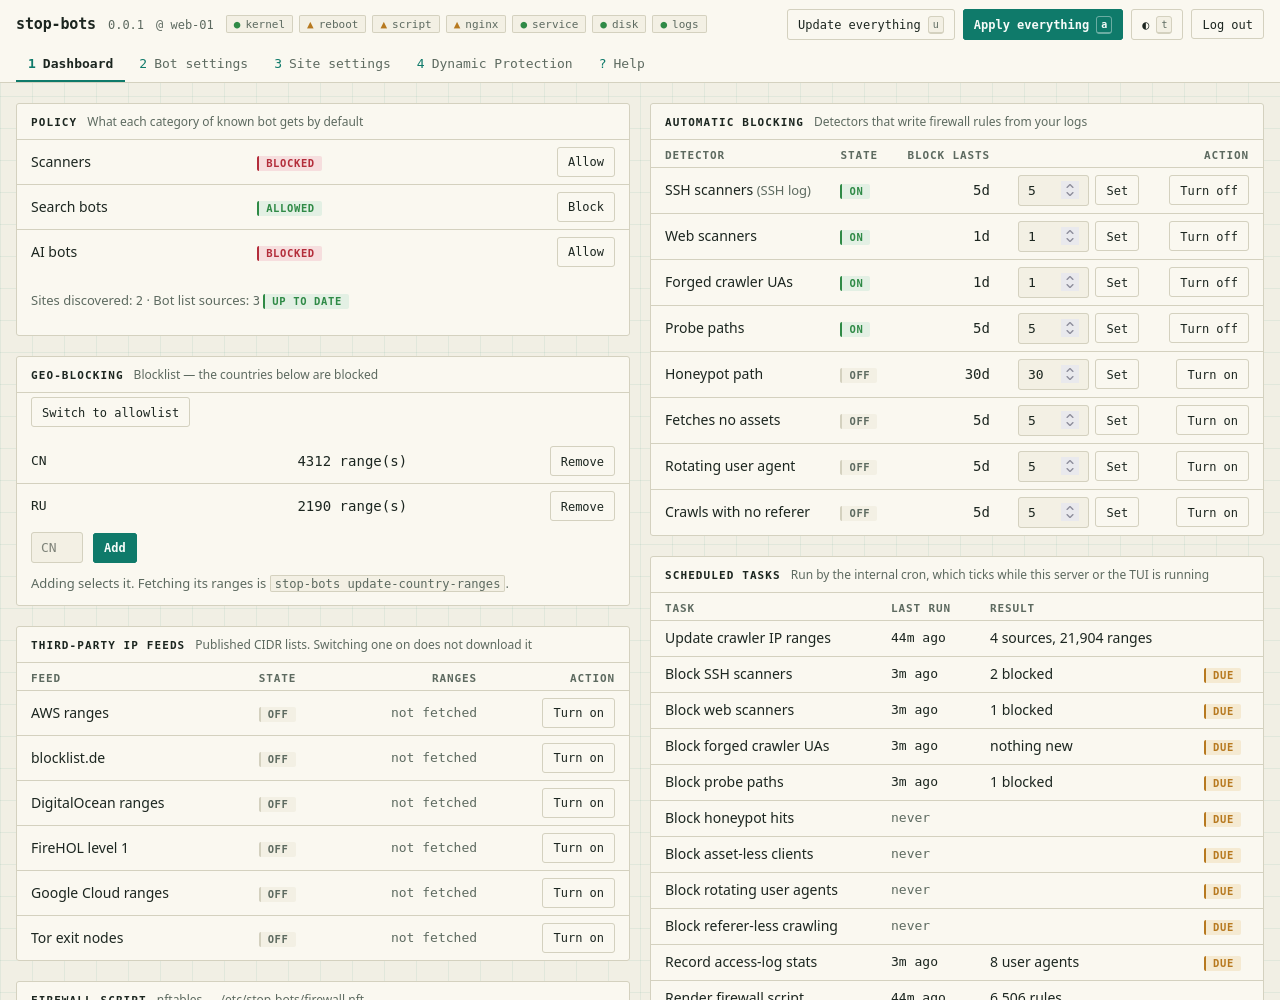 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 xcoy0te/cve-2026-83548-checker
Non-intrusive detector for SonicWall SMA 1000 exposure to CVE-2026-83548/-83549 (version/patch-state check; no exploitation)
 ssc-ict-innovatie/nl-kat-coordination
Modular network scanning framework that integrates diverse tools and external databases to detect vulnerabilities and configuration errors, producing…
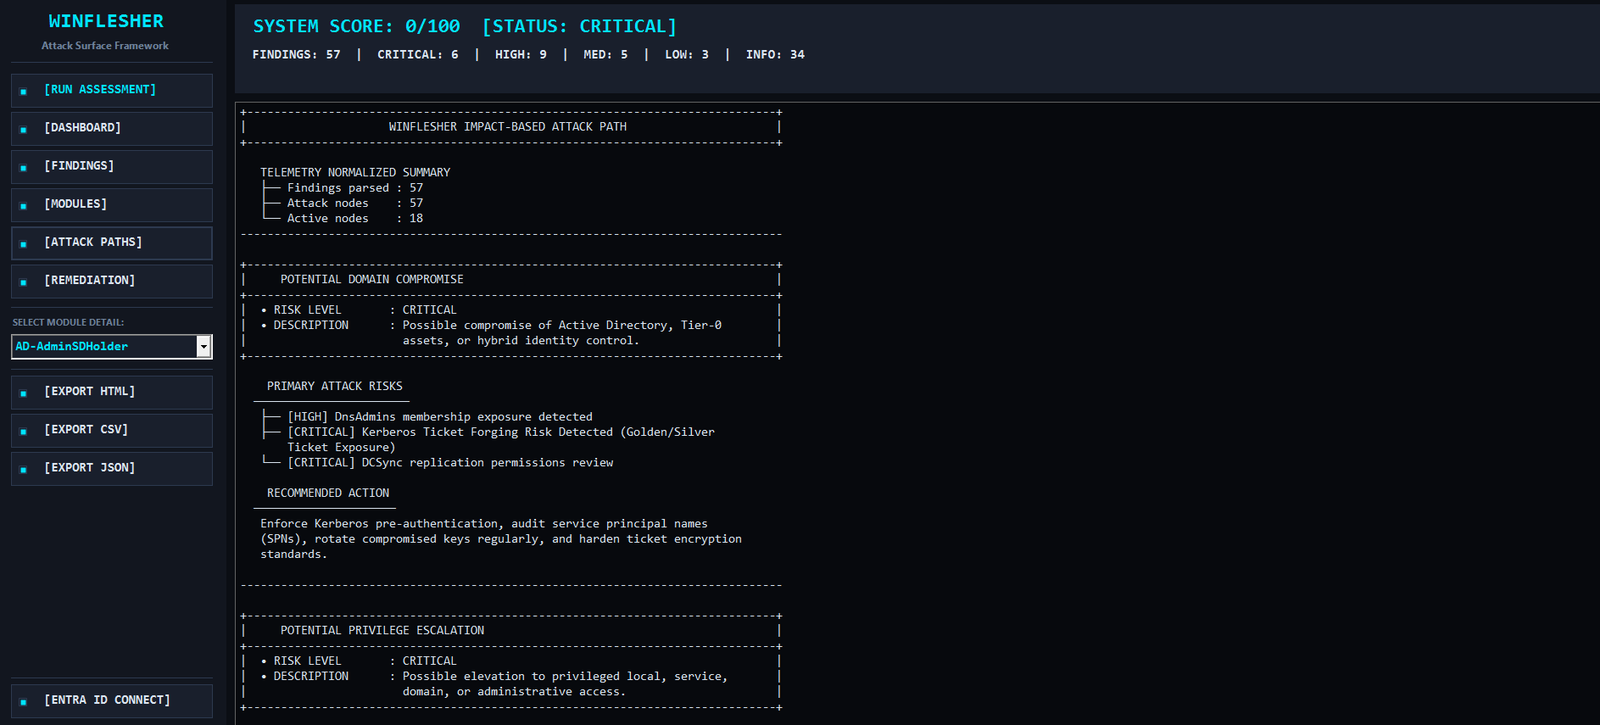 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 lamaper/cve-2026-52200
Security advisory detailing broken access control in UZ801/ES-U3TS MifiService web API, allowing unauthenticated data extraction, config…
 gopinaath/cve-2025-49844-discovery
Audits AWS ElastiCache Redis/Valkey clusters for network exposure, checking VPC, subnet, and internet gateway routes across multiple accounts and…
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 sreejaputhan/cpanel-control-plane-exposure-check
Defensive exposure assessment tool for identifying externally accessible cPanel, WHM, and Webmail management interfaces related to CVE-2026-41940.
 raptoratack/copyfail-scanner-cve-2026-31431
Scans systems for CVE-2026-31431 (CopyFile vulnerability), enumerates system details, evaluates exposure, reports vulnerable status, and optionally…