

cplt
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
121
navikt/cpltSandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 danaug23/detect_cve-2026-25177
Production-safe scanner that detects CVE-2026-25177 (AD SPN Unicode Collision) exploitation on Active Directory Domain Controllers. Read-only.
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 dnsviz/dnsviz
Analyzes DNS delegation and DNSSEC security by probing resolvers and authoritative servers, then validating, diagnosing, and visualizing zone…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 paulsec/awesome-windows-domain-hardening
A curated list of awesome Security Hardening techniques for Windows.
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
 bishopfox/spoofcheckselftest
Web application that lets you test if your domain is vulnerable to email spoofing
 jenderal92/s3-bucket-take-0v3r
AWS AMAZON S3 Bucket Takeover Scanner & Claim Tool
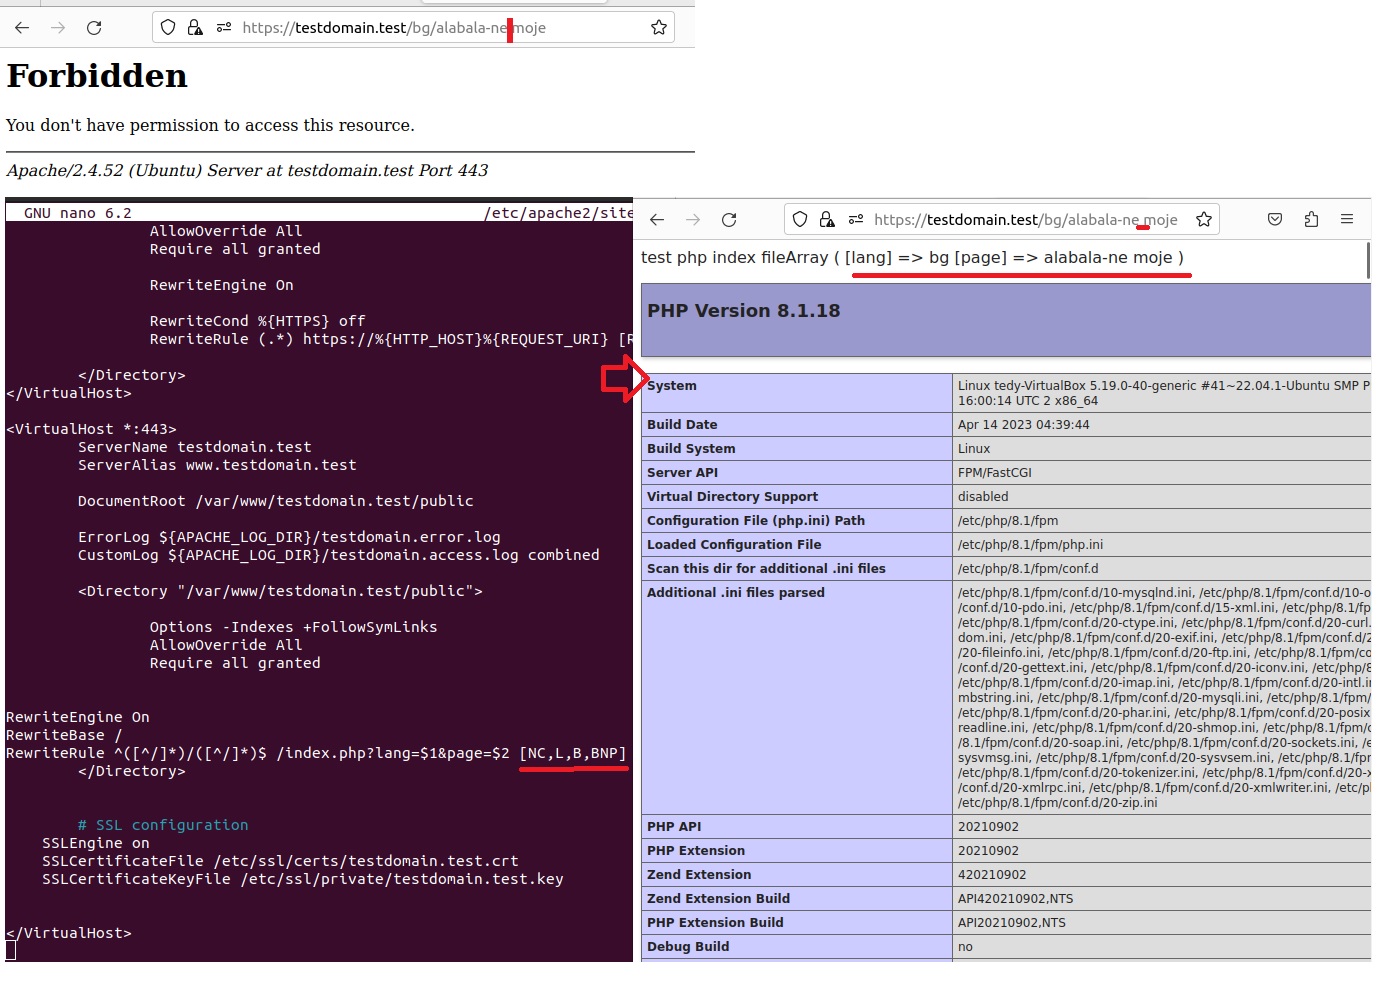 tbachvarova/linux-apache-fix-mod_rewrite-spaceinurl
Fix URL containing SPACES after Apache upgrade CVE-2023-25690
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
 keysau/get-log4j-windows.ps1
Identifying all log4j components across all windows servers, entire domain, can be multi domain. CVE-2021-44228