ndaal_public_auditd
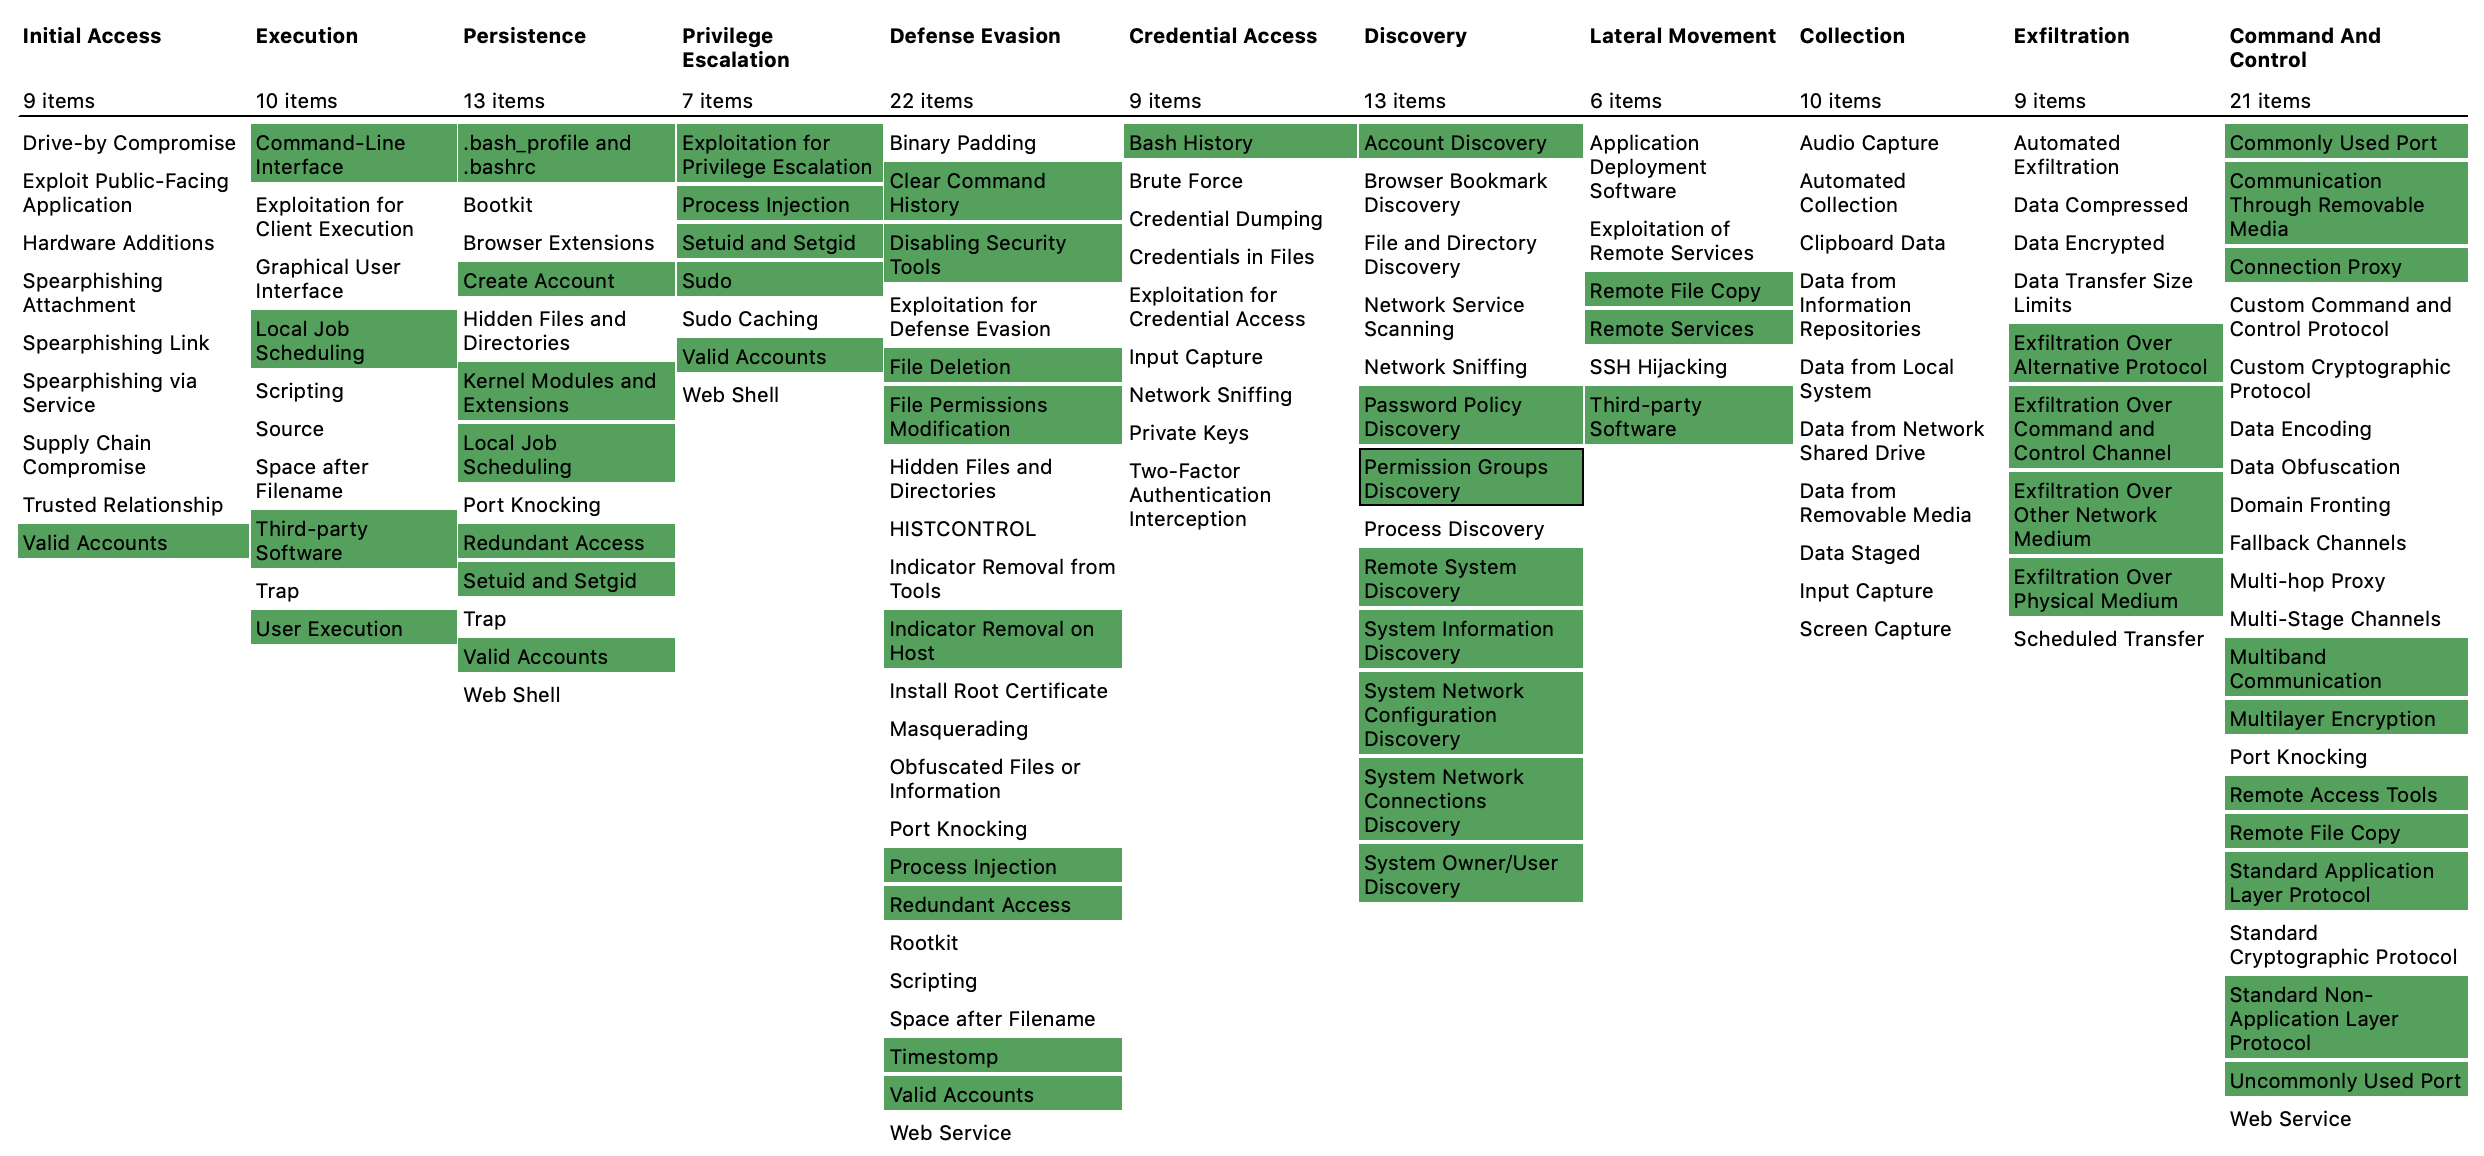
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Enumerate the permissions associated with AWS credential set

Comprehensive set of over 1500 AppArmor profiles to confine Linux system processes, desktops, and services, with support for multiple distributions…

GitHub App to set and enforce security policies

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

The Symfony PHP framework

A collection of scripts to help set the appropriate registry keys for CVE-2021-34527

Best Practice Auditd Configuration

This chef cookbook provides security configuration for mysql.

A Linux Auditd rule set mapped to MITRE's Attack Framework

Kubernetes RBAC static analysis & visualisation tool

Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…

provides a Firewall Manager API designed to centralize and streamline the management of firewall configurations

Configuration Hardening Assessment PowerShell Script (CHAPS)

Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…

Local read-only scanner for CVE-2026-42945 (NGINX Rift) that checks NGINX, OpenResty, and Tengine instances for vulnerable rewrite configurations…

Blue Team detection lab created with Terraform and Ansible in Azure.