

cplt
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
124
navikt/cpltSandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 rtvkiz/minimal
Minimal CVE Hardened container image collection
 codesource/copyfail-check
Shell script to detect CVE-2026-31431 (Copy Fail) exposure and mitigations on Linux systems: kernel check, module state, boot params, AF_ALG…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
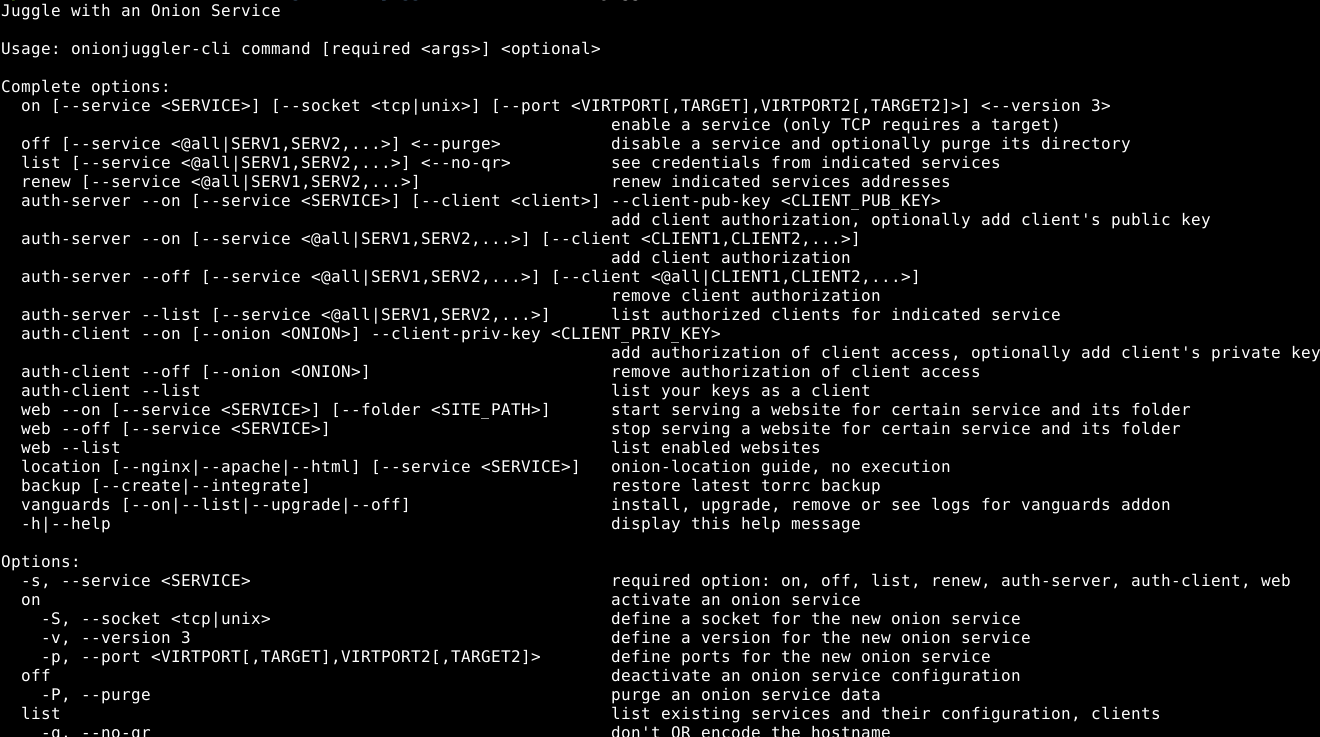 nyxnor/onionjuggler
Manage your Onion Services via CLI or TUI on Unix-like operating system with a POSIX compliant shell.
 sbeteta42/cve-2026-31431_je_sappelle_root
CVE-2026-31431 - Guide de Remédiation et Mesures de Protection
 fkj-src/fix_nginx_cve_2026_42945
Automated one-click shell script to detect and patch NGINX CVE-2026-42945 across major Linux distributions, with config backup, version validation,…
 k3rnix/portguard
USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 dgourillon/mitigate-cve-2024-6387
Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.
 mahfuzreham/ovswrap-cve-2026-64531-mitigation-tool
Shell script that detects vulnerable Open vSwitch kernel modules, blocks automatic loading, removes the affected module, and verifies mitigation…
 gubiczap/cve-2026-31431-checker
Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…
 jdmulloy/meltdown-aws-scanner
Naive shell script to verify Meltdown (CVE-2017-5754) patch status of EC2 instances
 ekamsinghwalia/mitigation-apache-cve-2021-41773-
Mitigation/fix of CVE-2021-41773 A Path Traversal And File Disclosure Vulnerability In Apache
 ikarolaborda/cve2026-42926
Controlled NGINX HTTP/2 frame injection lab for CVE-2026-42926 patch validation and defensive research
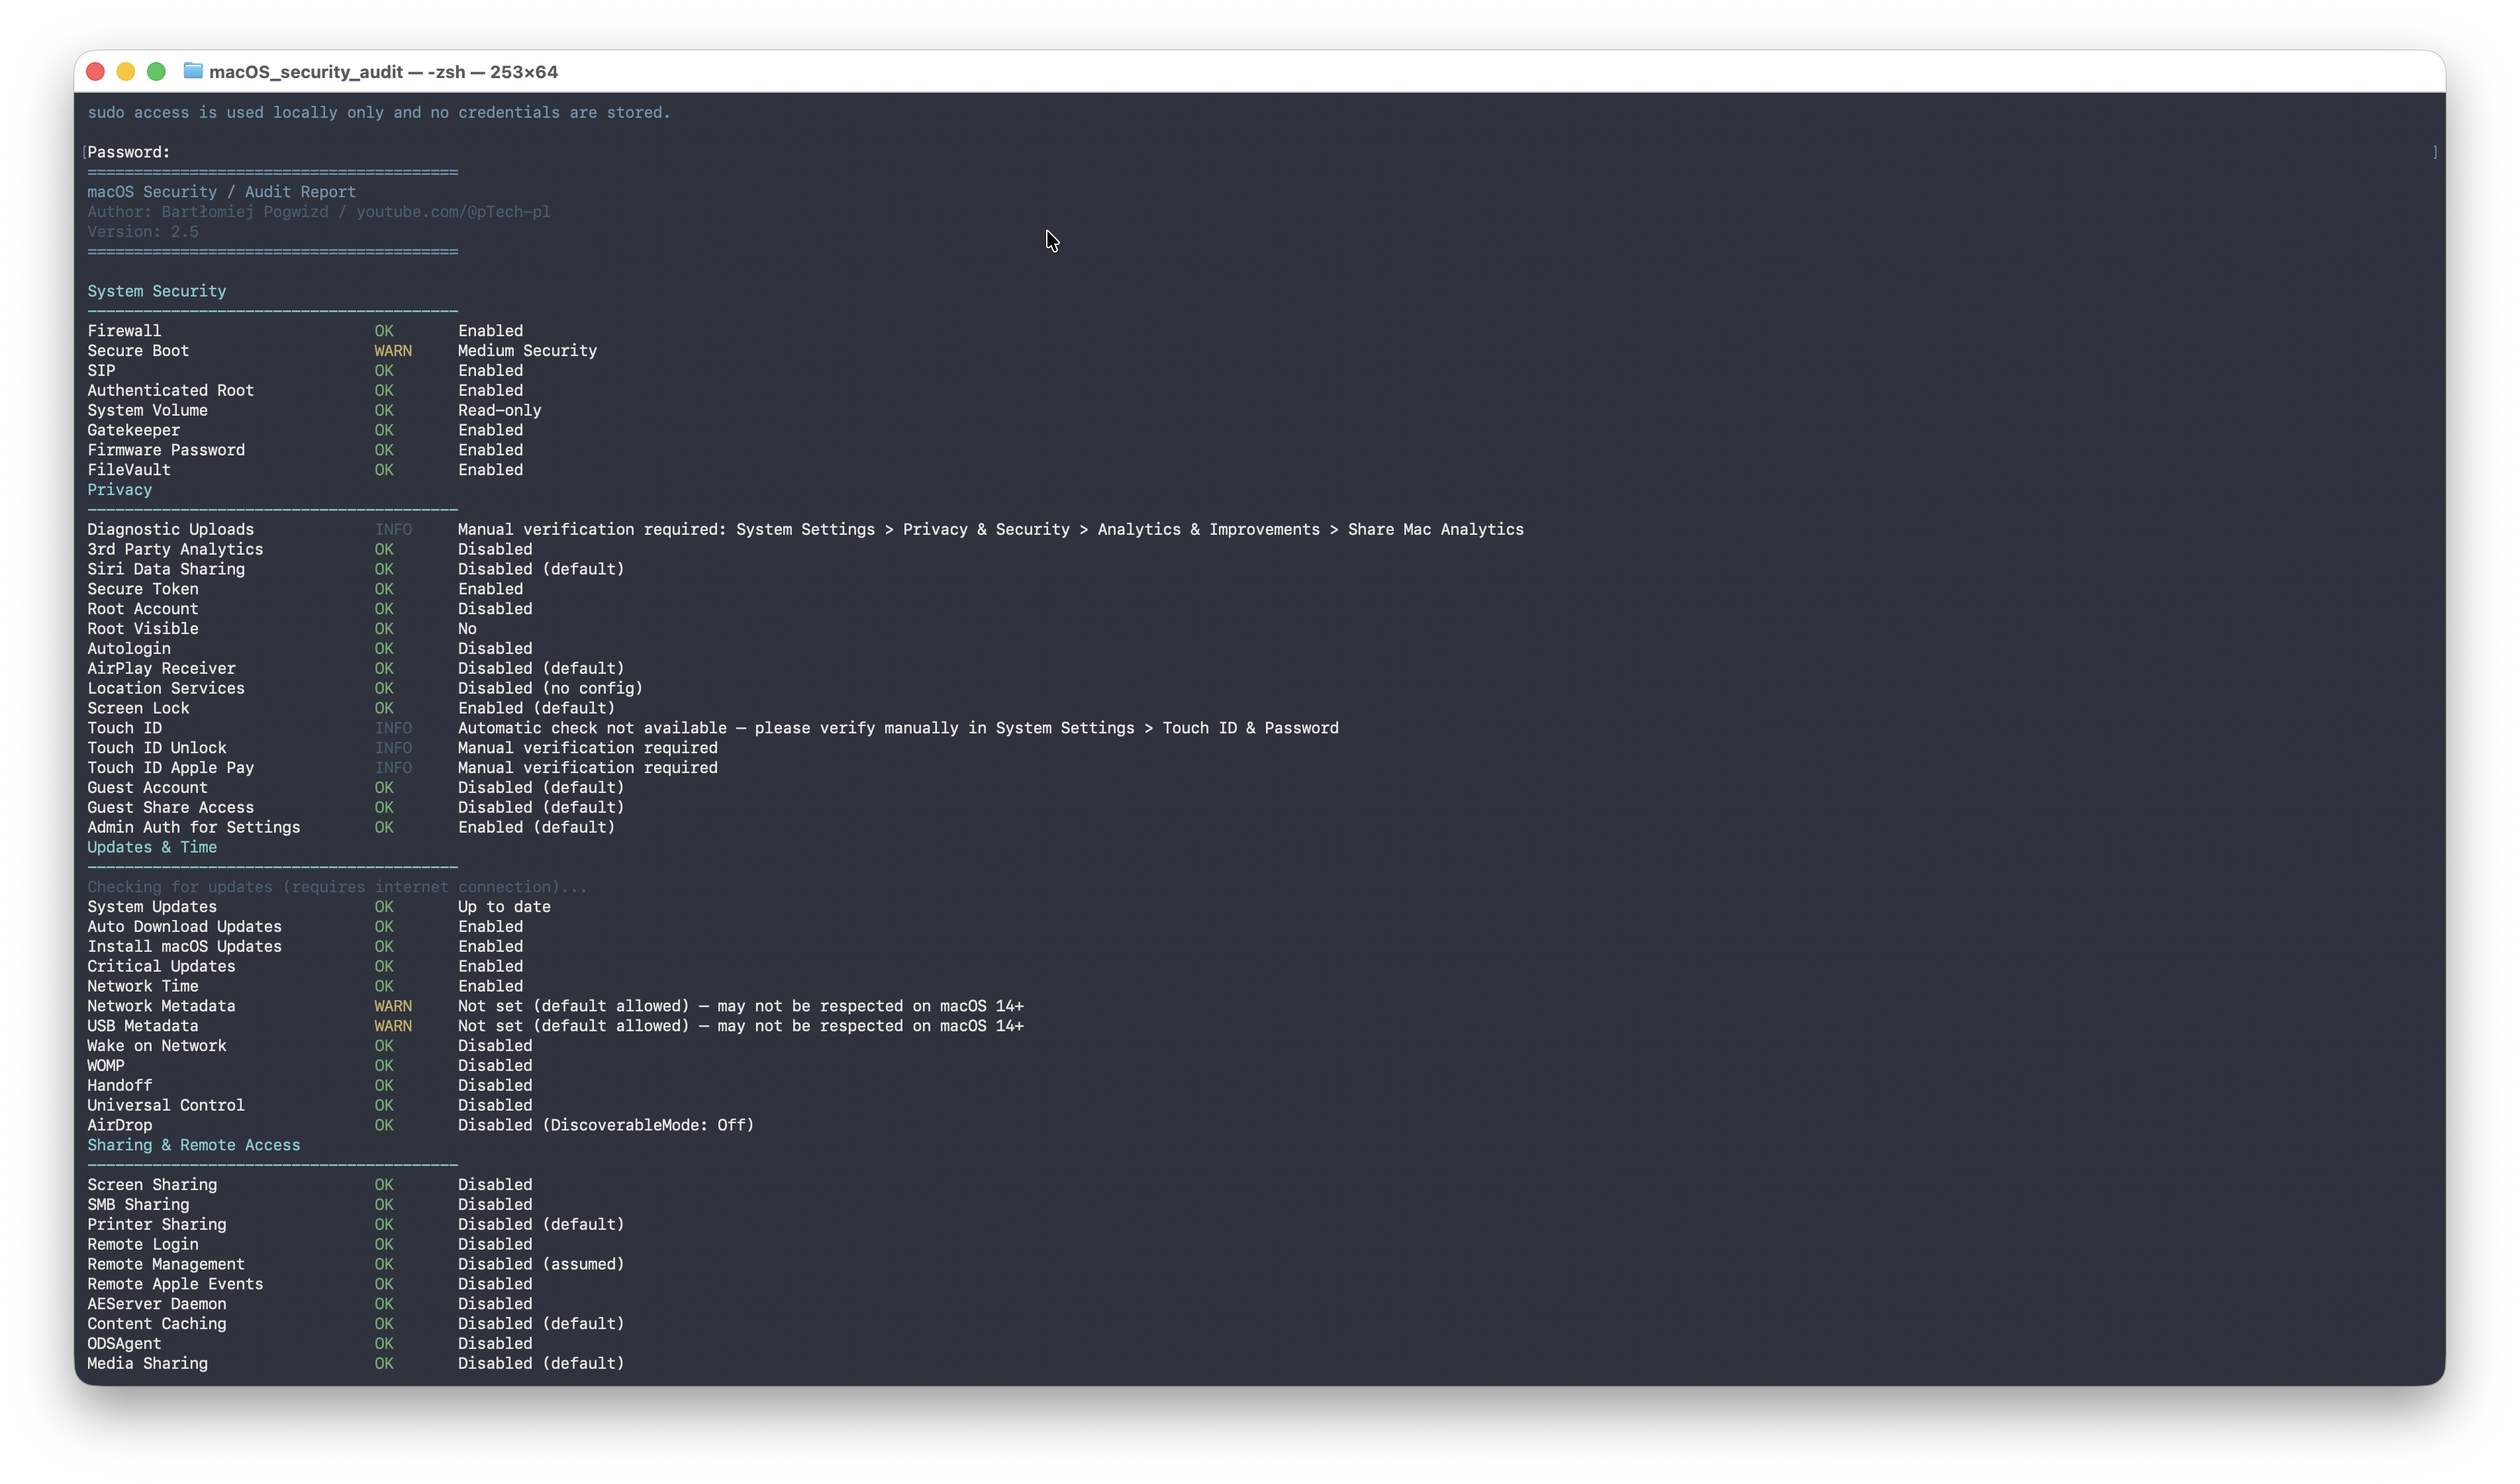 ptechpl/macos_security_audit
macOS script for auditing