

MSSQLand
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
configuration-auditingdatabase-securityimpersonation-tools+6
81
n3rada/mssqlandIn-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 aquasecurity/cloudsploit
Multi-cloud security posture scanner that audits AWS, Azure, GCP, and OCI for misconfigurations, compliance violations (HIPAA, PCI, CIS), and…
 soteria-security/365inspect
A PowerShell script that automates the security assessment of Microsoft 365 environments.
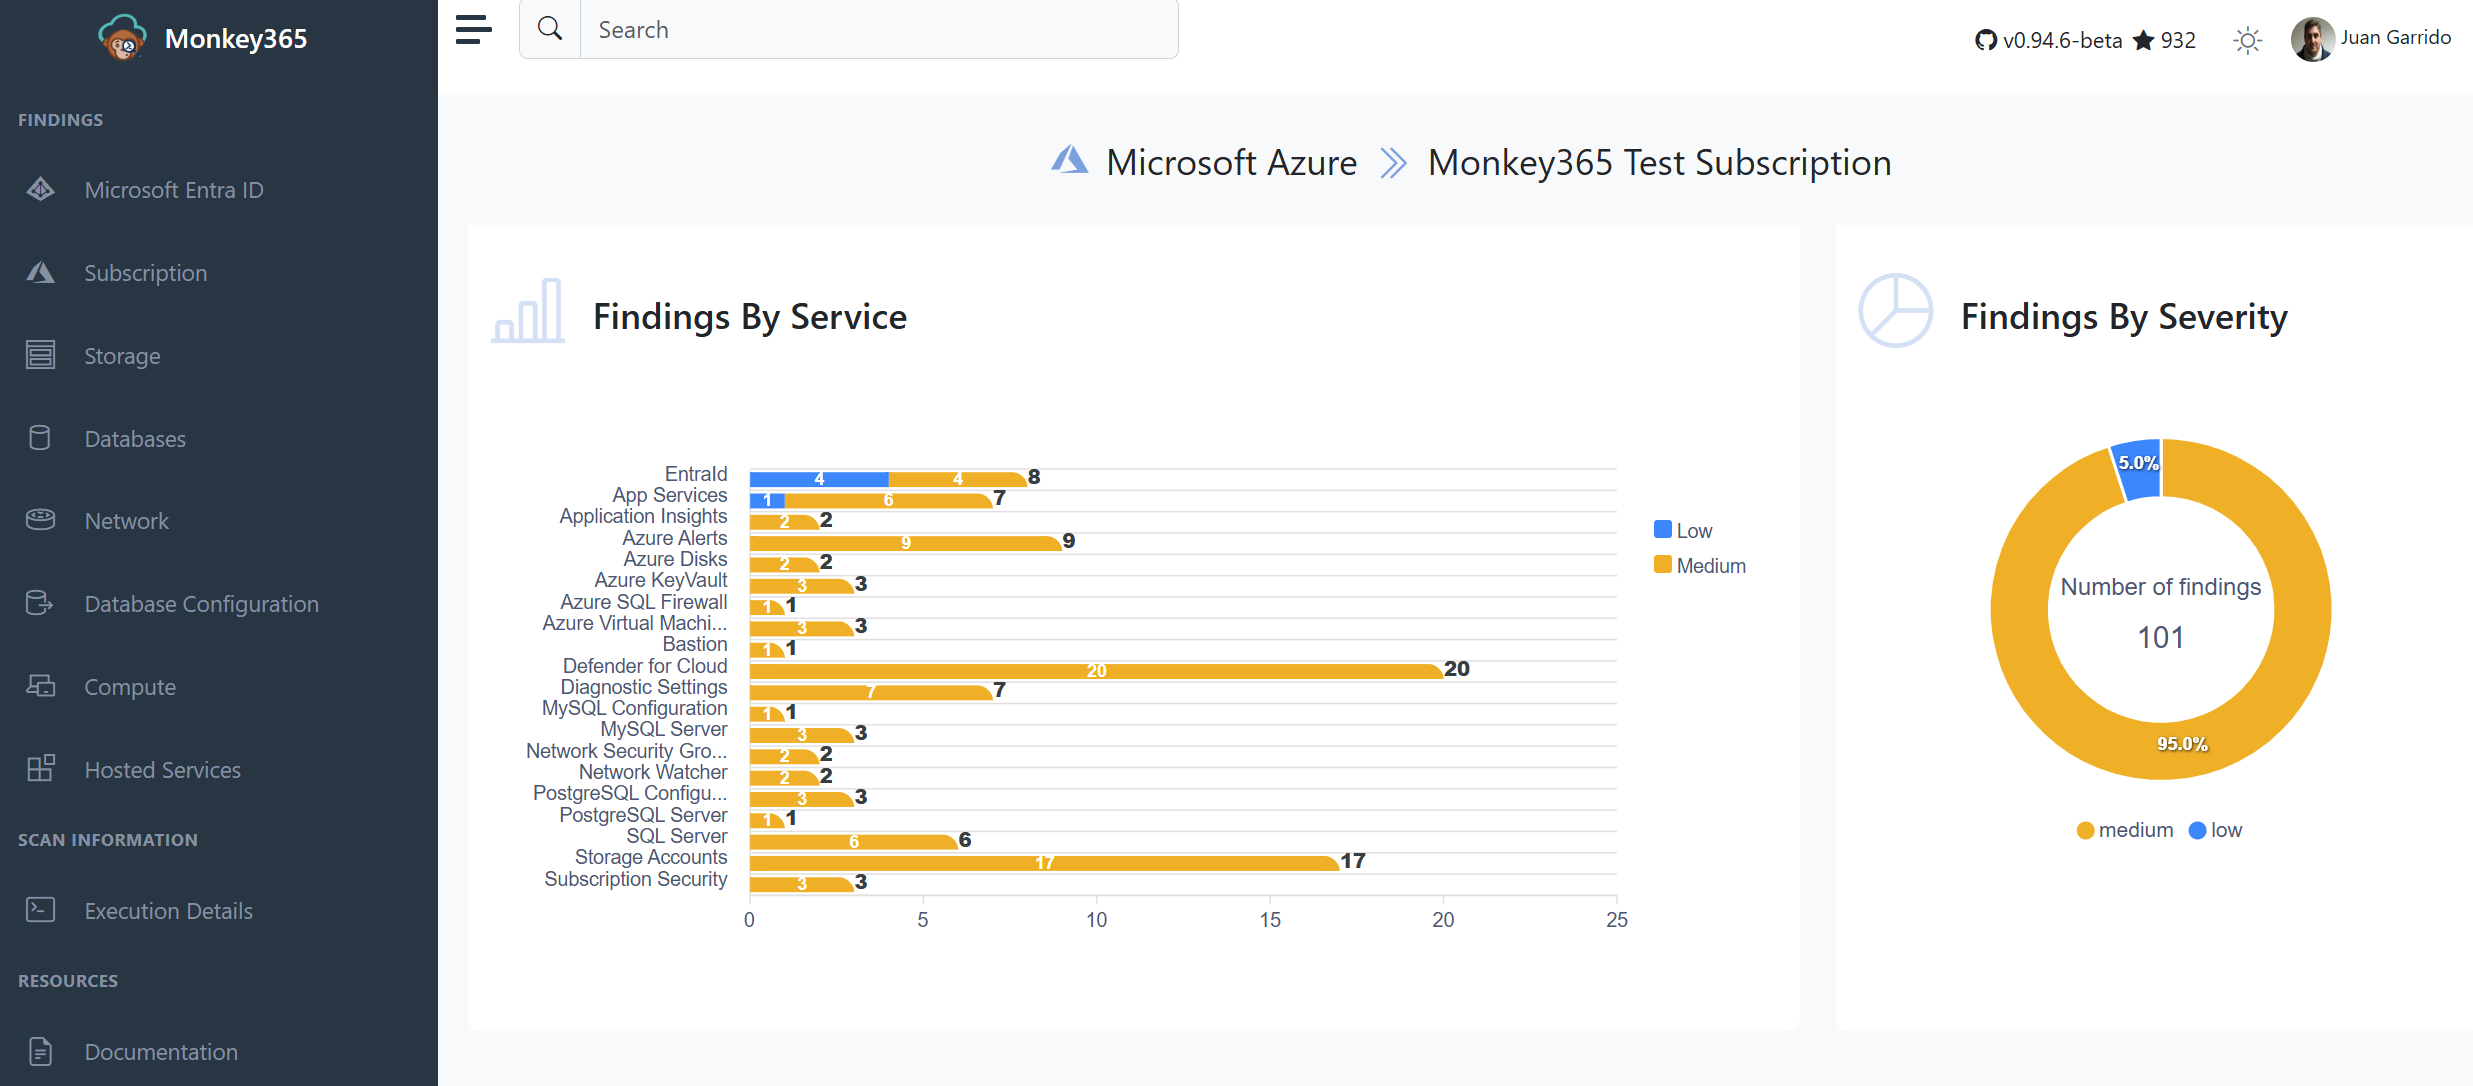 silverhack/monkey365
PowerShell-based security assessment framework for Microsoft 365, Azure, and Entra ID. Scans for misconfigurations, CIS benchmark compliance, and…
 keulenr01/remediate-adobeacrobat-cve-2026-34621
Intune Proactive Remediation scripts to enforce patched Adobe Acrobat/Reader versions and disable JavaScript to mitigate CVE-2026-34621 exploitation.
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
 bohops/ultimatewdacbypasslist
A centralized resource for previously documented WDAC bypass techniques
 phillips321/adaudit
Powershell script to do domain auditing automation
 daryllundy/cve-2025-32711
PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
 salihuahmad105-creator/vulnerability-scanner
DESIGN AND IMPLEMENTATION OF A VULNERABILITY SCANNER FOR CVE-2026-45498 IN MICROSOFT DEFENDER
 ridhinva/defender-privilege-escalation-scanner
Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
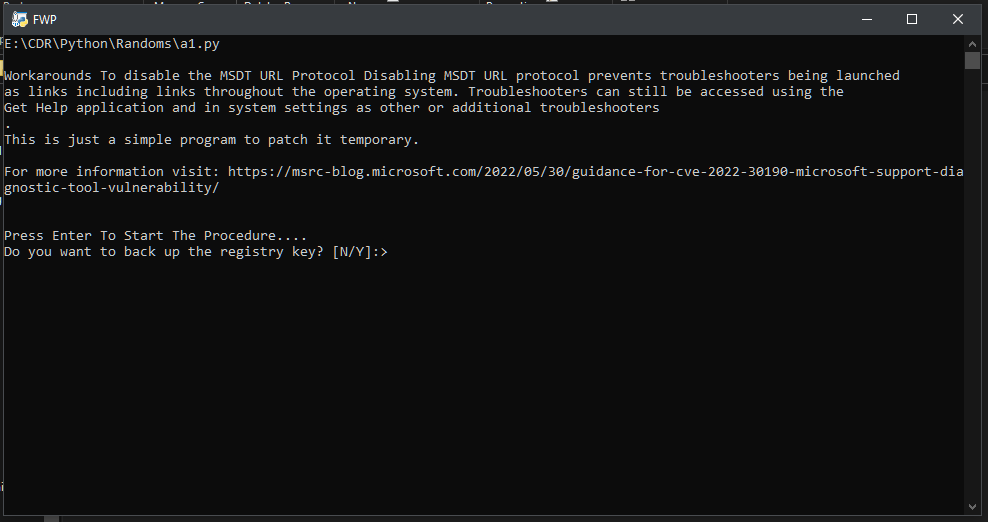 suenerve/cve-2022-30190-follina-patch
The CVE-2022-30190-follina Workarounds Patch
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 sec-consult/msiscan
Scanning tool for identifying local privilege escalation issues in vulnerable MSI installers