

thingsboard
 thingsboard/thingsboard
Open-source IoT Platform - Device management, data collection, processing and visualization.
anomaly-detectioncloud-infrastructure-securityconfiguration-auditing+3
22.4k
thingsboard/thingsboardOpen-source IoT Platform - Device management, data collection, processing and visualization.
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
 abdullahaligun/reachability-check
Browser-based network connectivity checker for testing firewall rules, access restrictions, and corporate policy compliance. Supports HTTP Fetch and…
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5410_2-1-8-release
Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…
 cynepmyx/nginx-rift-check
Detects the CVE-2026-42945 rewrite pattern in nginx configs: rewrite with ? in the replacement plus an unnamed capture consumed in the same location
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5405_2-1-6-release
Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…
 al0ne/linuxcheck
Linux应急处置/信息搜集/漏洞检测工具,支持基础配置/网络流量/任务计划/环境变量/用户信息/Services/bash/恶意文件/内核Rootkit/SSH/Webshell/挖矿文件/挖矿进程/供应链/服务器风险等13类70+项检查
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 friparia/nginx_rift_scan_cve_2026_42945
Nginx Rewrite CVE Scan(CVE-2026-42945 nginx-rift CVE-2026-9256)
 rshosting/apache-cve-2026-23918-fix
Upgrade to Apache 2.4.67 to fix CVE-2026-23918 vulneribility
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 riramar/hsecscan
A security scanner for HTTP response headers.
 byezero/nginx-cve-2026-42945-check
Local read-only scanner for CVE-2026-42945 (NGINX Rift) that checks NGINX, OpenResty, and Tengine instances for vulnerable rewrite configurations…
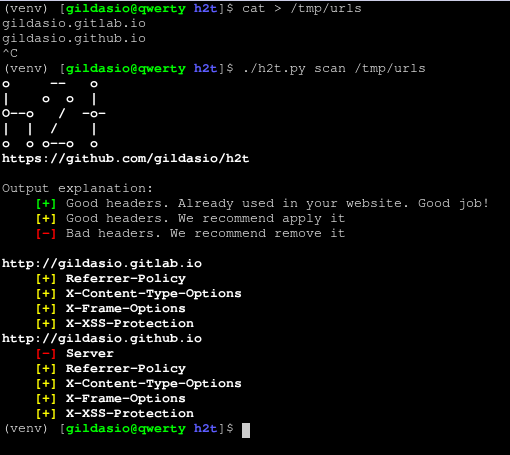 gildasio/h2t
h2t (HTTP Hardening Tool) scans a website and suggests security headers to apply
 fatlan/haproxy-keepalived-sec-highloads
✨ HAProxy ve Keepalived konusunu load balancer ve cluster'a ek olarak güvenlik(zayıf SSL/Kripto Kullanımı (LOGJAM) (CVE-2015-4000) zafiyeti önlemi)…
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
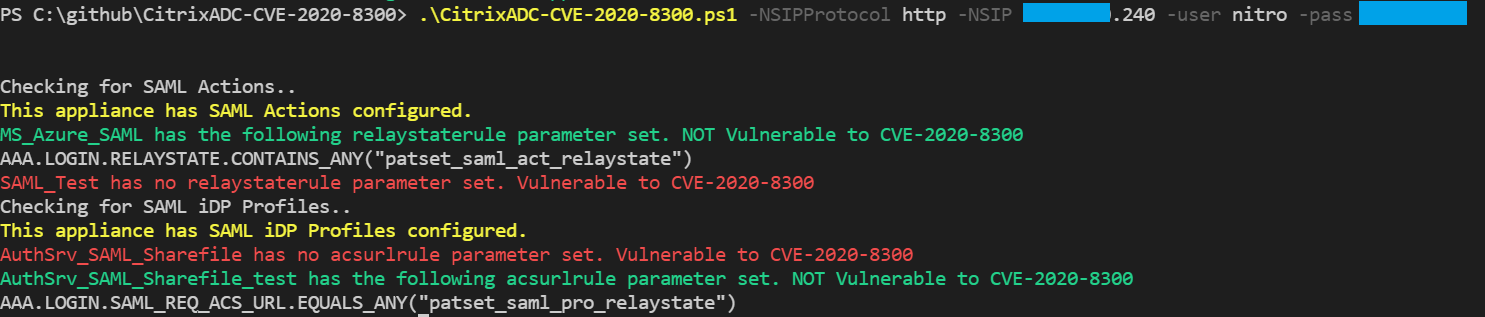 stuartcarroll/citrixadc-cve-2020-8300
Detect Citrix ADC SAML action or SAML iDP Profile config vulnerable to CVE-2020-8300 using Citrix ADC NITRO API