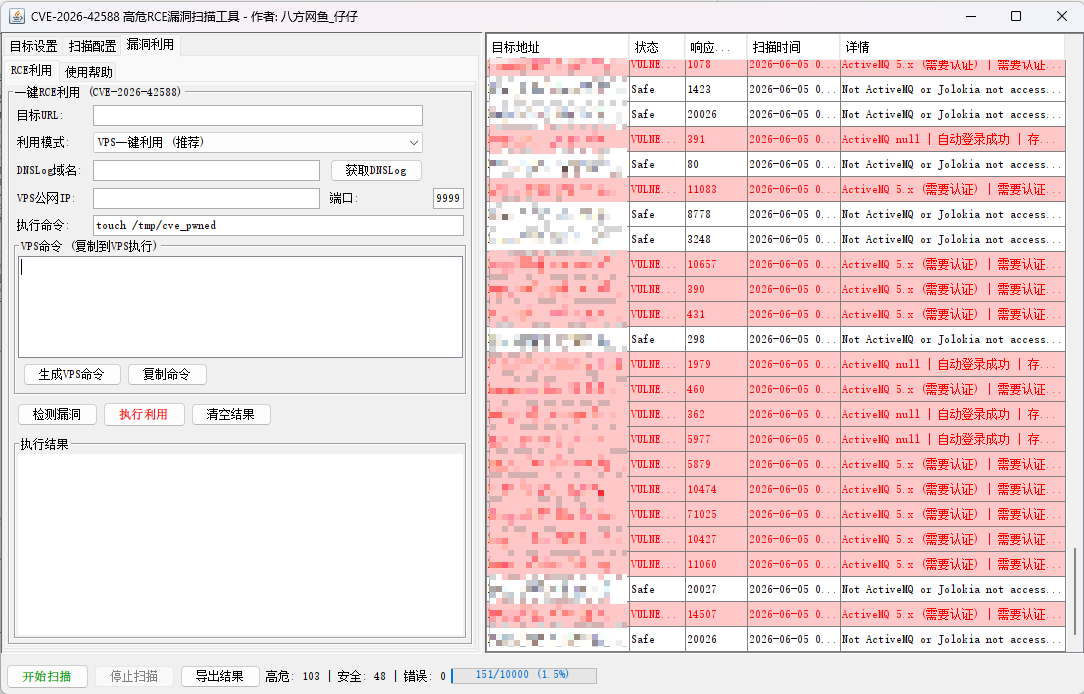
ActiveMQ-cve-2026-42588-scanner-gui

GUI-based scanner and exploit tool for CVE-2026-42588 (ActiveMQ RCE). Supports VPS payload delivery and DNSLog-based vulnerability verification with…

GUI-based scanner and exploit tool for CVE-2026-42588 (ActiveMQ RCE). Supports VPS payload delivery and DNSLog-based vulnerability verification with…

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.

CVE-2025-66034 exploit and documentation

This repository contains a PoC exploit for CVE-2025-69212.

Unauthenticated remote code execution exploit for Oracle WebLogic CVE-2017-10271. Provides XML payload and endpoint list for penetration testing of…

Proof-of-concept exploit for CVE-2019-0193 targeting Apache Solr's DataImportHandler, enabling remote code execution via crafted XML data sources…

Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…

freeswitch all version remote command execute (cve-2018-19911)

CVE-2020-26217 XStream反序列化的poc