
iodine
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
command-and-controldata-exfiltrationids-ips-evasion+4
yarrick/iodineTunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 h4x0r-dz/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, a Palo Alto OS command injection in GlobalProtect VPN. Demonstrates file creation and outbound command…
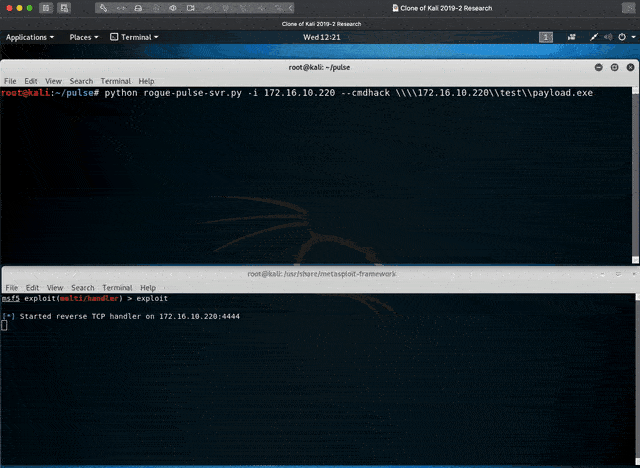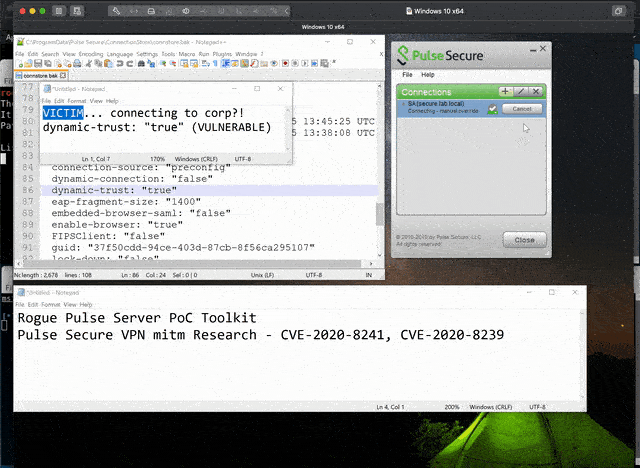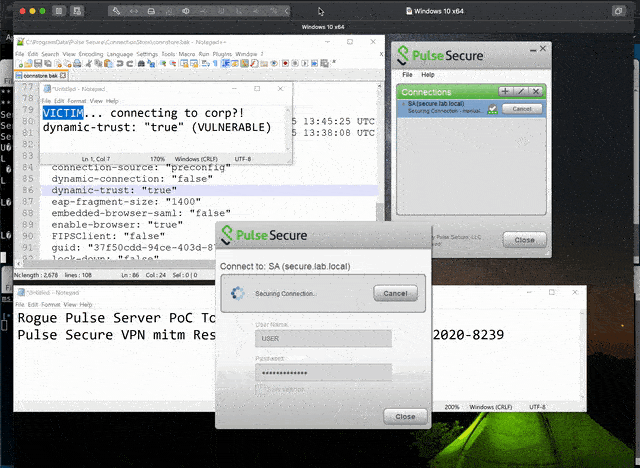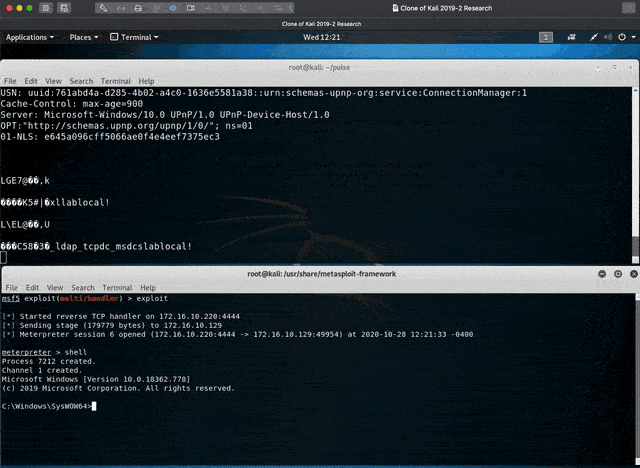 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
 mr-xn/cve-2023-43482
TP-Link ER7206 Omada Gigabit VPN Router uhttpd freeStrategy Command injection Vulnerability
 ibrahimzx/cve-2019-1653
A vulnerability in the web-based management interface of Cisco Small Business RV320 and RV325 Dual Gigabit WAN VPN Routers could allow an…
 vesperp/cve-2021-20038-sonicwall-rce
Python exploit for CVE-2021-20038 targeting SonicWall SSL VPN with command-line URL/file input for remote code execution.
 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 mbadanoiu/cve-2020-8250
CVE-2020-8250: Privilege Escalation via Command Injection in Pulse Secure VPN Linux Client
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 savior-only/cve-2022-30525
Zyxel 防火墙未经身份验证的远程命令注入
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 k0sf/cve-2022-30525
Proof-of-concept exploit for CVE-2022-30525, a remote command injection vulnerability in Zyxel firewalls, with netcat reverse shell and DNS log…
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226