metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…

app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…

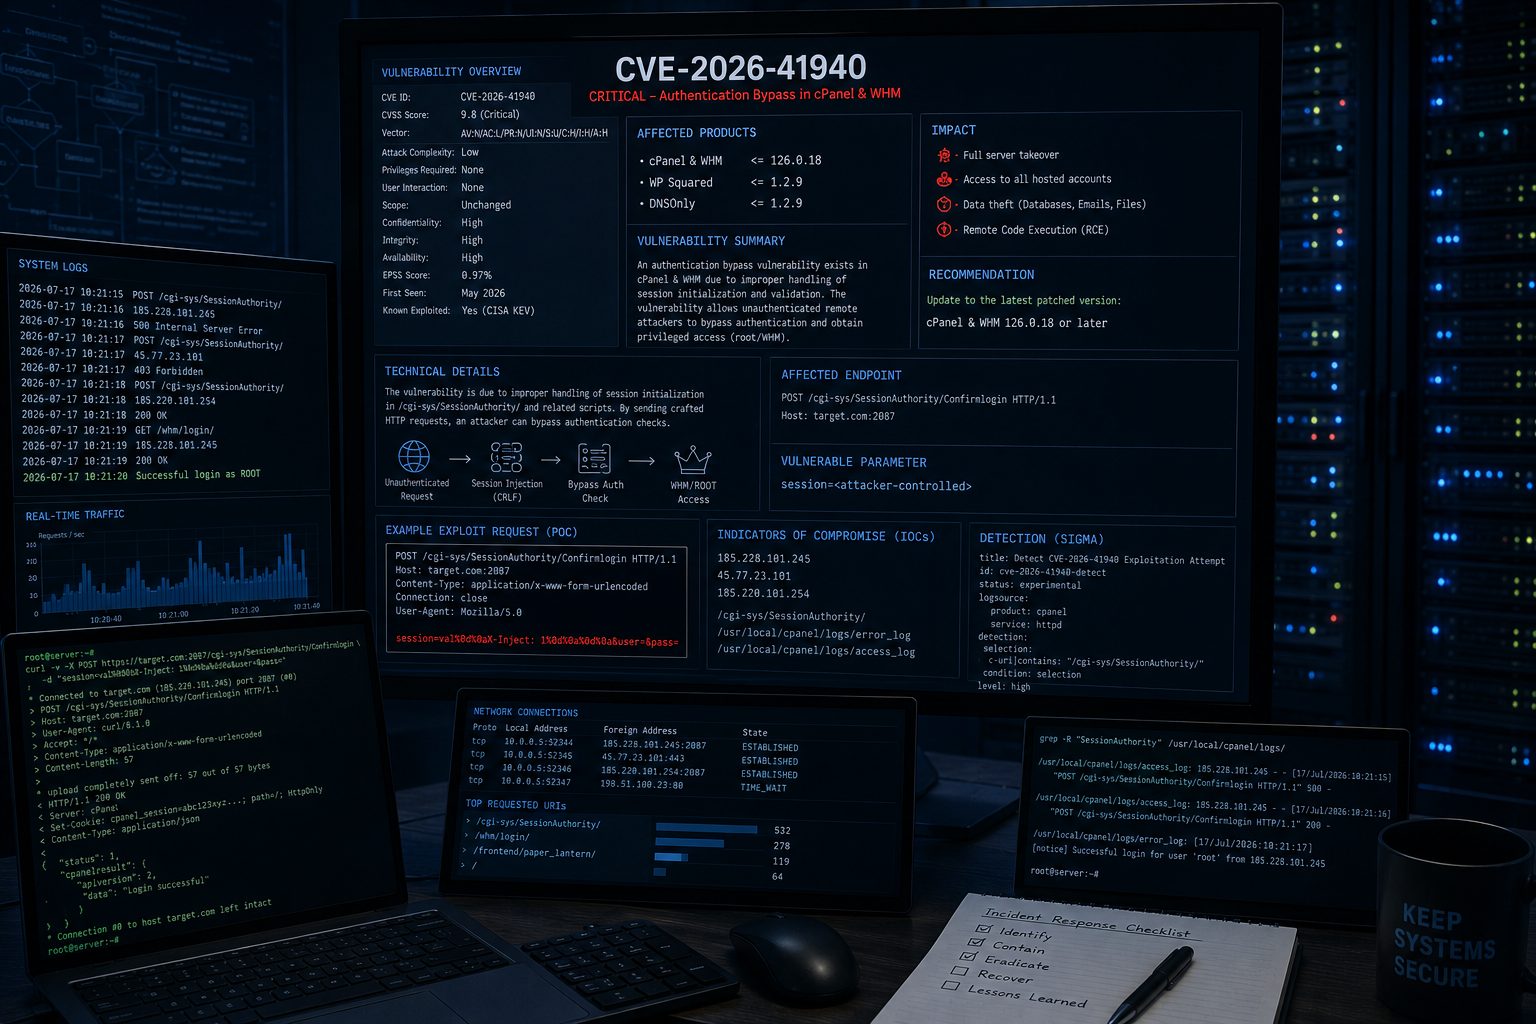
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…

Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection

Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…

GitHub Self-Hosted Runner Enumeration and Attack Tool

CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection

BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…

Authenticated RCE exploit for ASUS ExpertWiFi and RT-AX57 Go routers via command injection in splash_page_SDN.cgi. Requires a valid login token to…

Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE

Git Web Hook Tunnel for C2

A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.

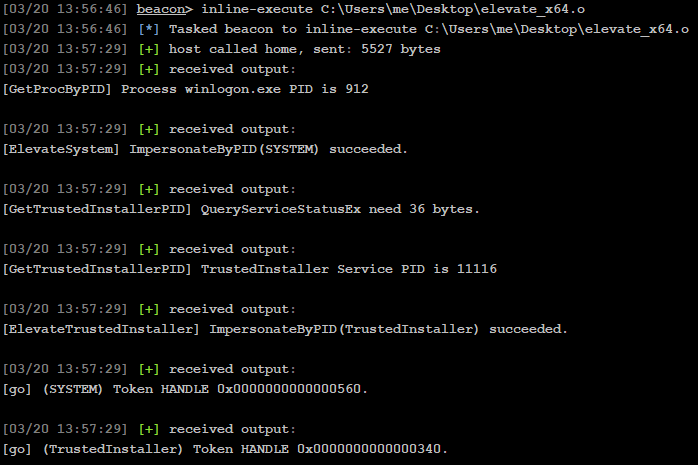
Cobalt Strike Beacon Object File that elevates an active beacon to SYSTEM and grants TrustedInstaller privileges through SetThreadToken token…

Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…

Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…

Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…

Python script for CVE-2024-0012 / CVE-2024-9474 exploit

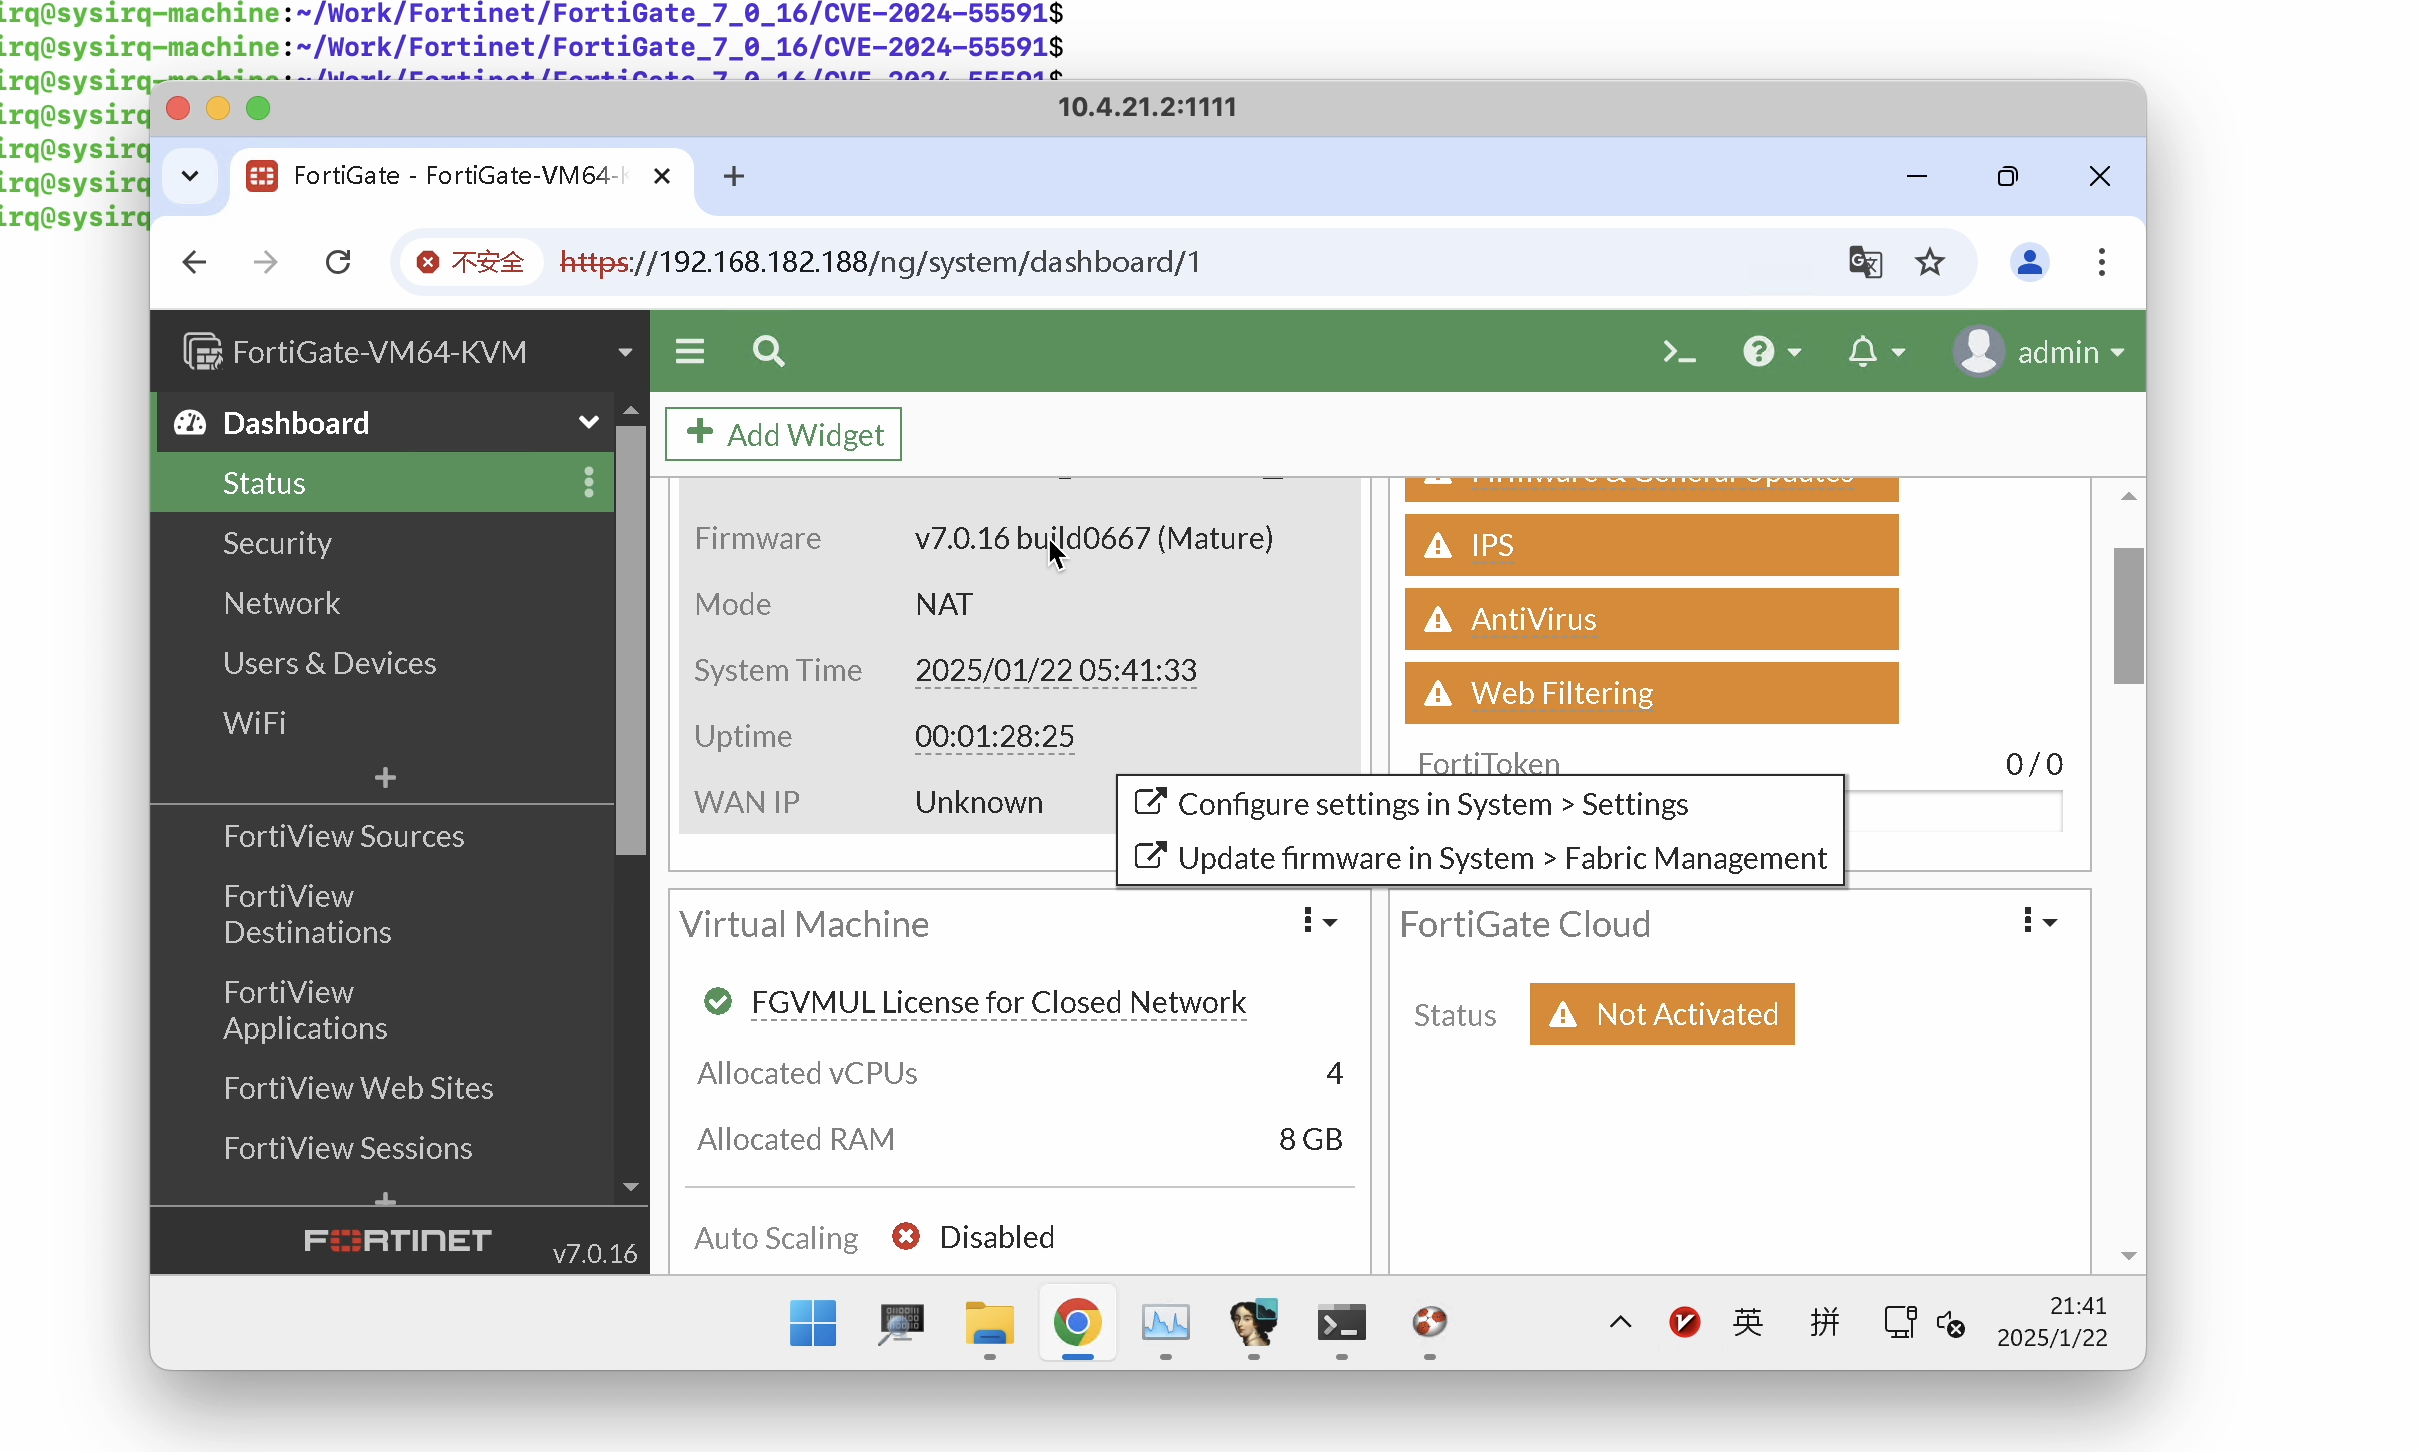
Python exploit for CVE-2024-55591, bypassing FortiOS authentication to execute remote commands on vulnerable FortiGate and FortiProxy devices.

Admin-only terminal bootstrap routes checked only for login state, which let a normal team member drive Coolify's realtime terminal backend and…