
UltraRealy_with_CVE-2019-1040
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
authenticationcommand-and-controlexploitation+7
19
lazaars/ultrarealy_with_cve-2019-1040Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 gagaltotal/cve-2026-10523-ivanti-sentry
Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 xltj/nopac
Go implementation of NoPac, exploiting CVE-2021-42278 and CVE-2021-42287
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
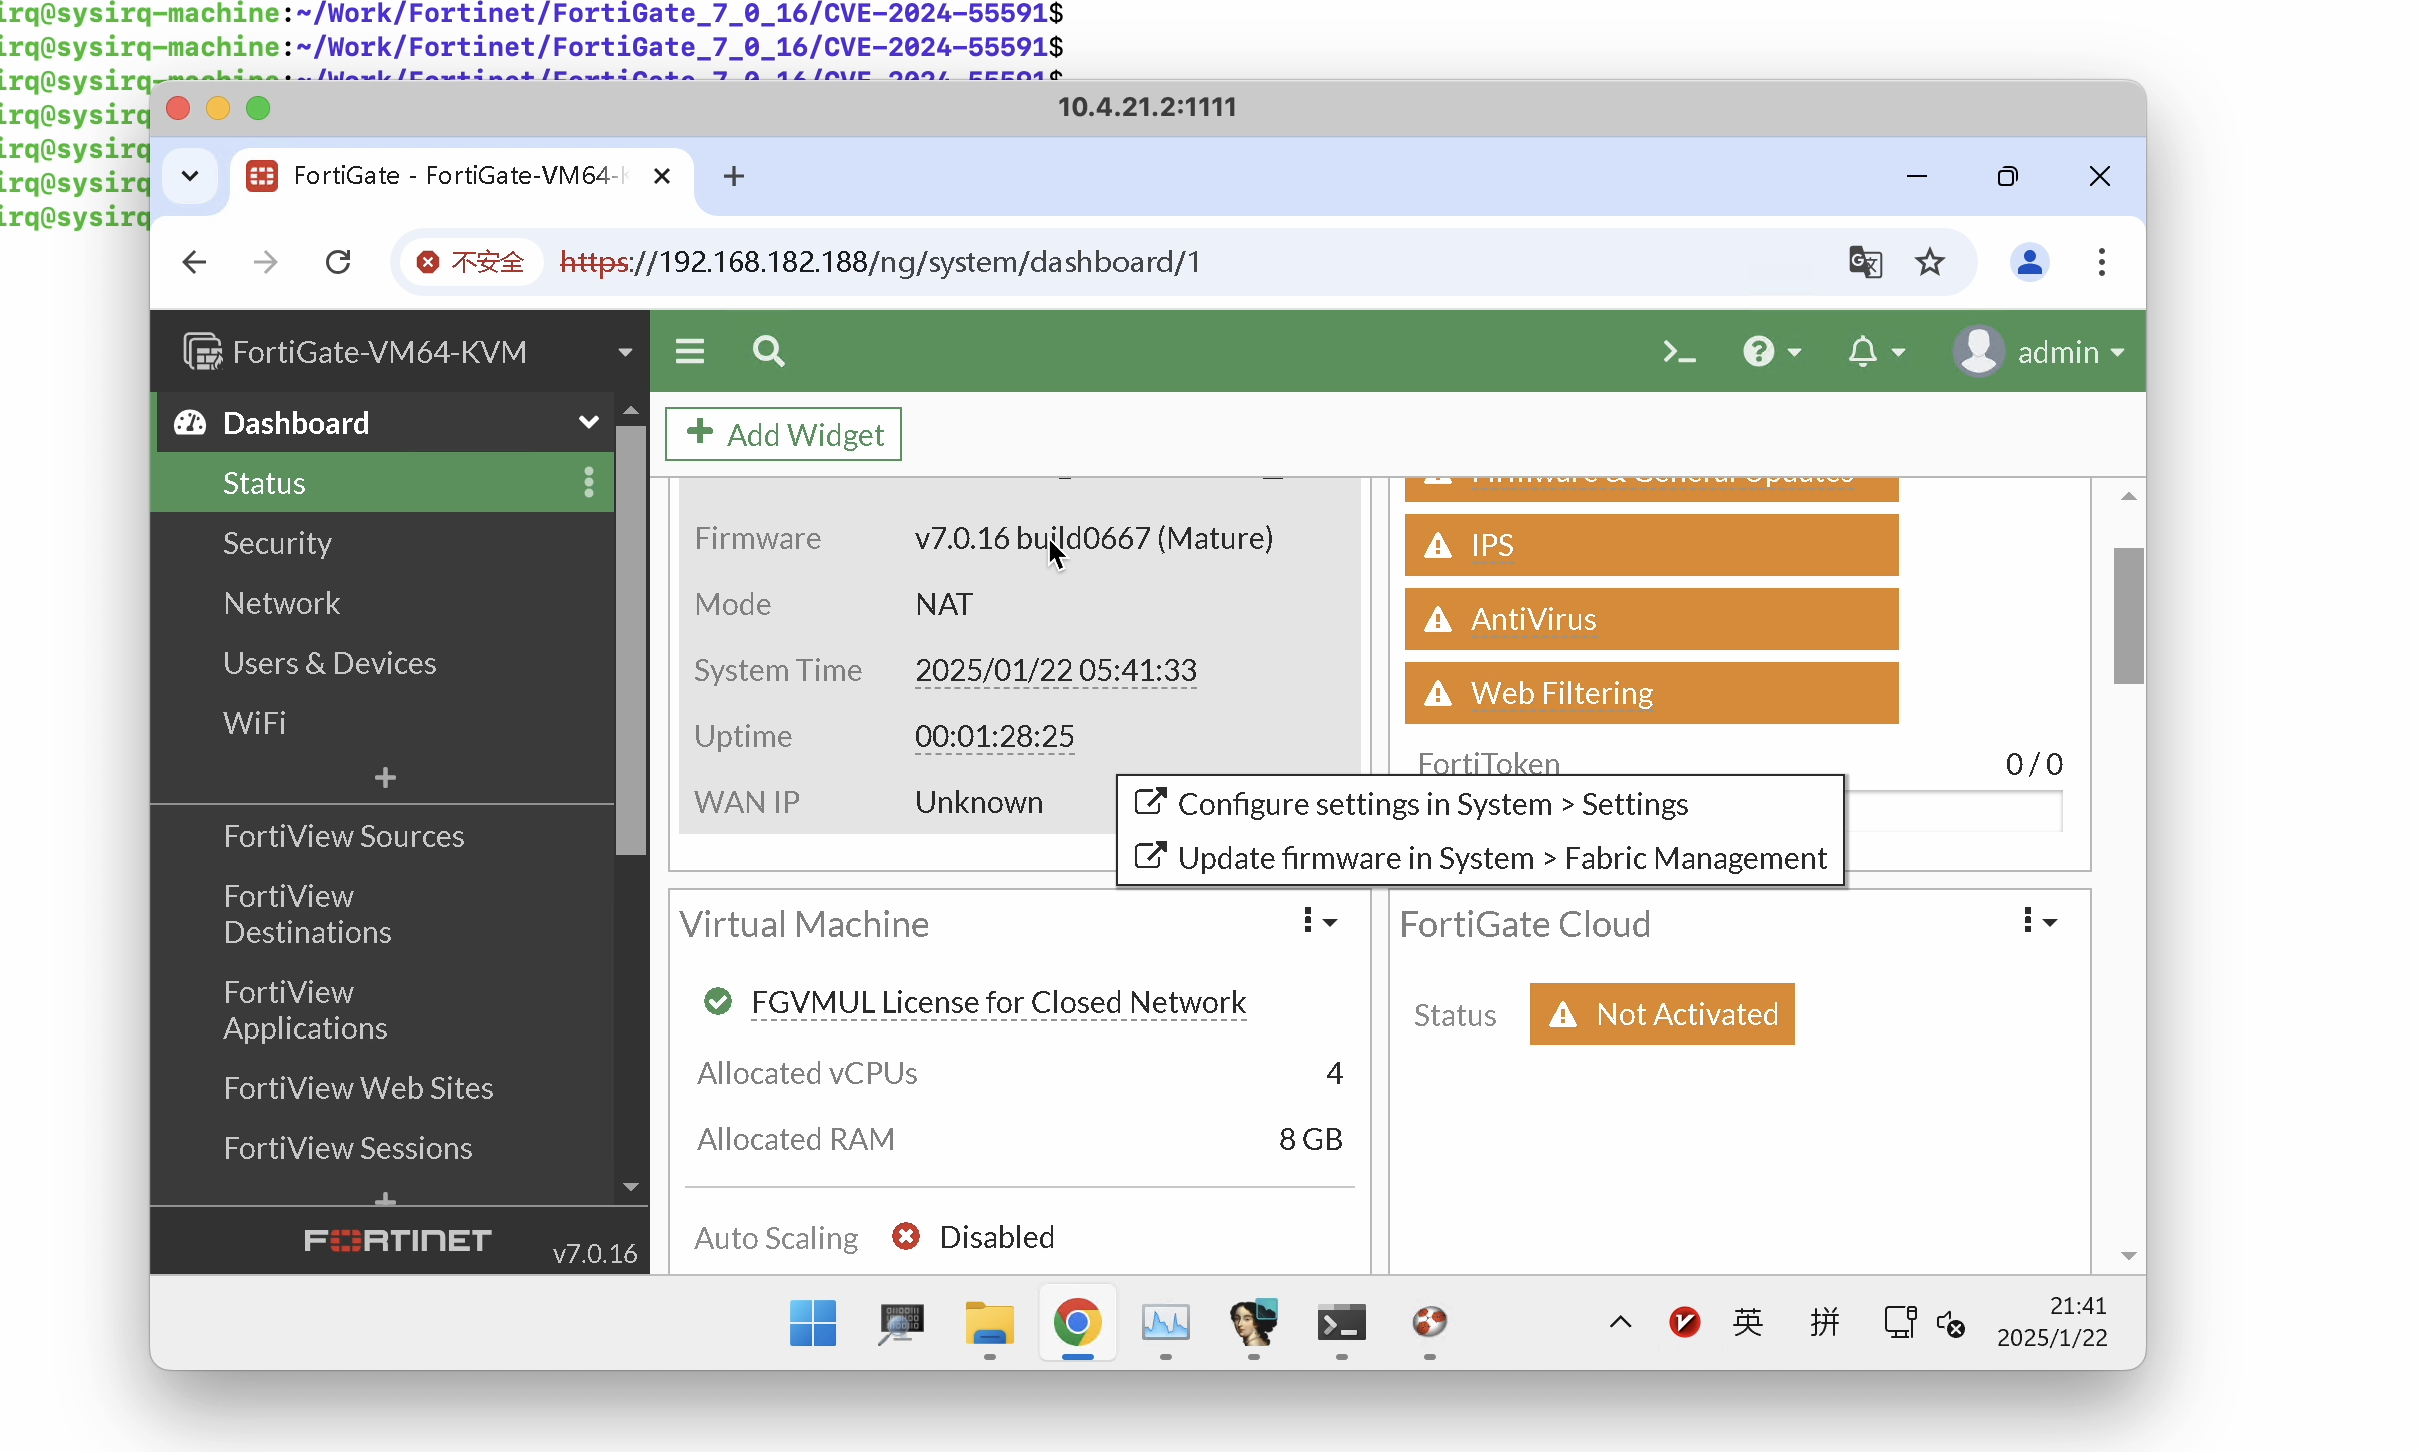 sysirq/fortios-auth-bypass-exploit-cve-2024-55591
Python exploit for CVE-2024-55591, bypassing FortiOS authentication to execute remote commands on vulnerable FortiGate and FortiProxy devices.
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 lutfifakee-project/cve-2026-41940
cPanel/WHM CVE-2026-41940 - Mass Scanner & Exploiter
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 livehybrid/poc-cribl-rce
CVE-2019-11076 - Cribl UI 1.5.0 allows remote attackers to run arbitrary commands via an unauthenticated web request
 drew-alleman/cve-2020-11651
A script that exploits SaltStack CVE-2020-11651 and CVE-2020-11652 to add new users to a vulnerable Salt master by injecting entries into /etc/passwd…
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
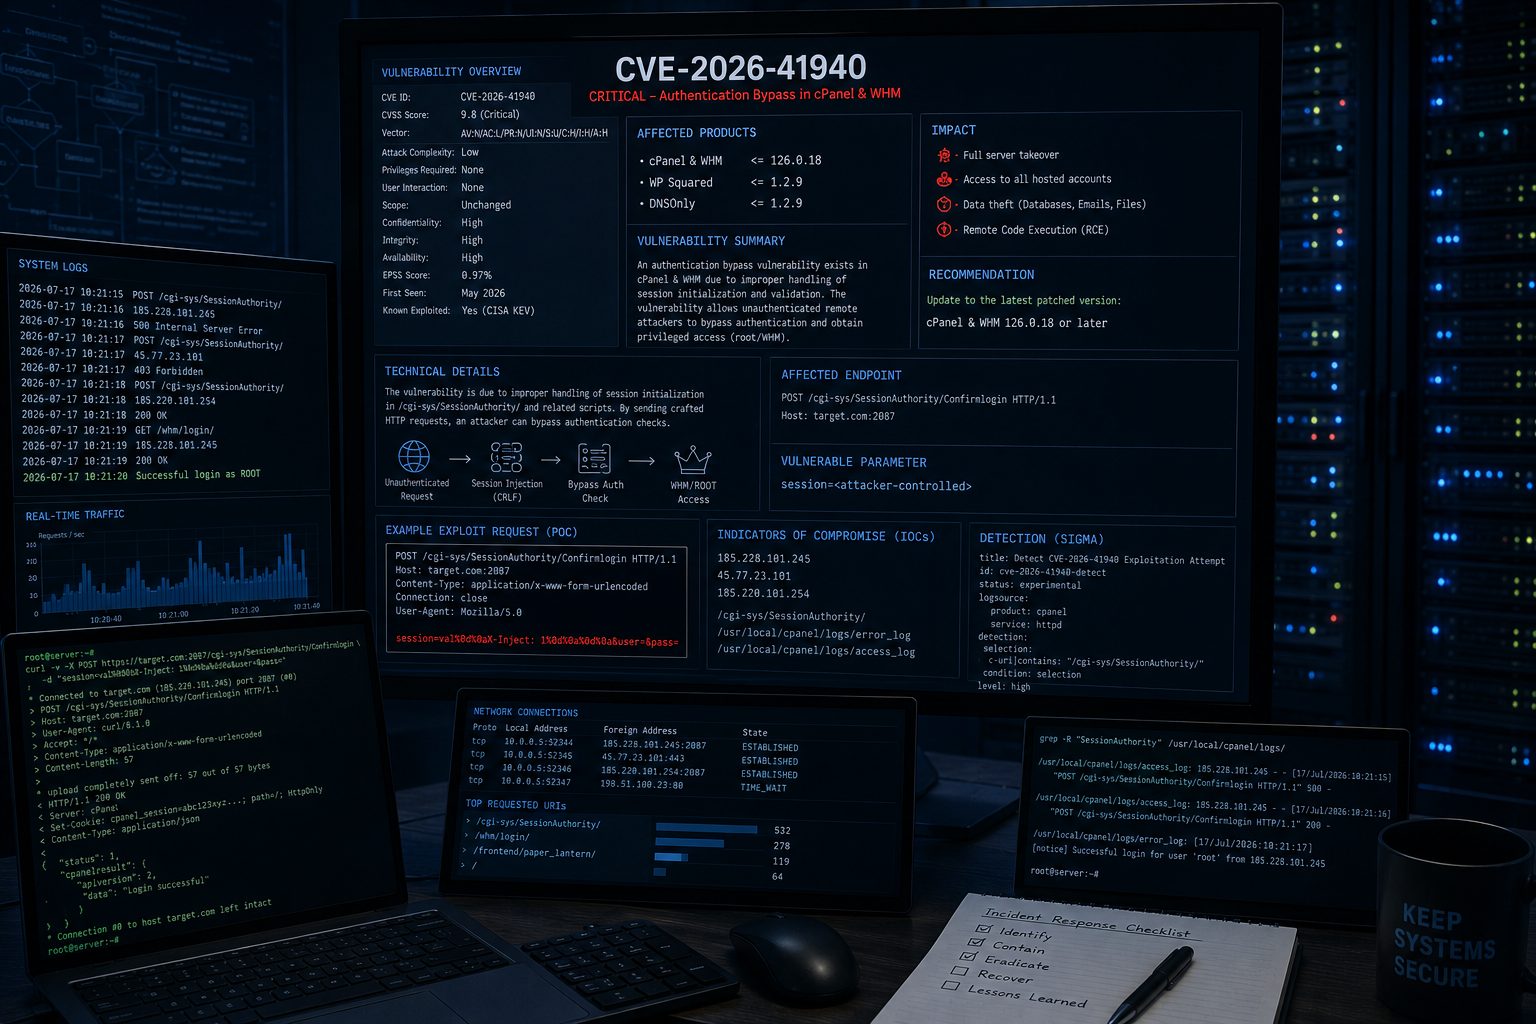 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 svchost9913/cve-2022-46169_unauth_remote_code_execution
Unauthenticated Remote Code Execution through authentication bypass and command injection in Cacti < 1.2.23 and < 1.3.0
 duy-31/cve-2023-46805_cve-2024-21887
An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…