CVE-2025-32433-Erlang-OTP-SSH-RCE-PoC

The vulnerability allows an attacker with network access to an Erlang/OTP SSH server to execute arbitrary code without prior authentication.

The vulnerability allows an attacker with network access to an Erlang/OTP SSH server to execute arbitrary code without prior authentication.

Python exploit for CVE-2025-32433 targeting Erlang OTP SSH server. Sends crafted SSH packets to open a reverse shell and gain root access.

CVE-2025-32433 Erlang/OTP SSH RCE Exploit SSH远程代码执行漏洞EXP

SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)

Missing Authentication for Critical Function (CWE-306)-Exploit

CVE-2025-32433 Summary and Attack Overview

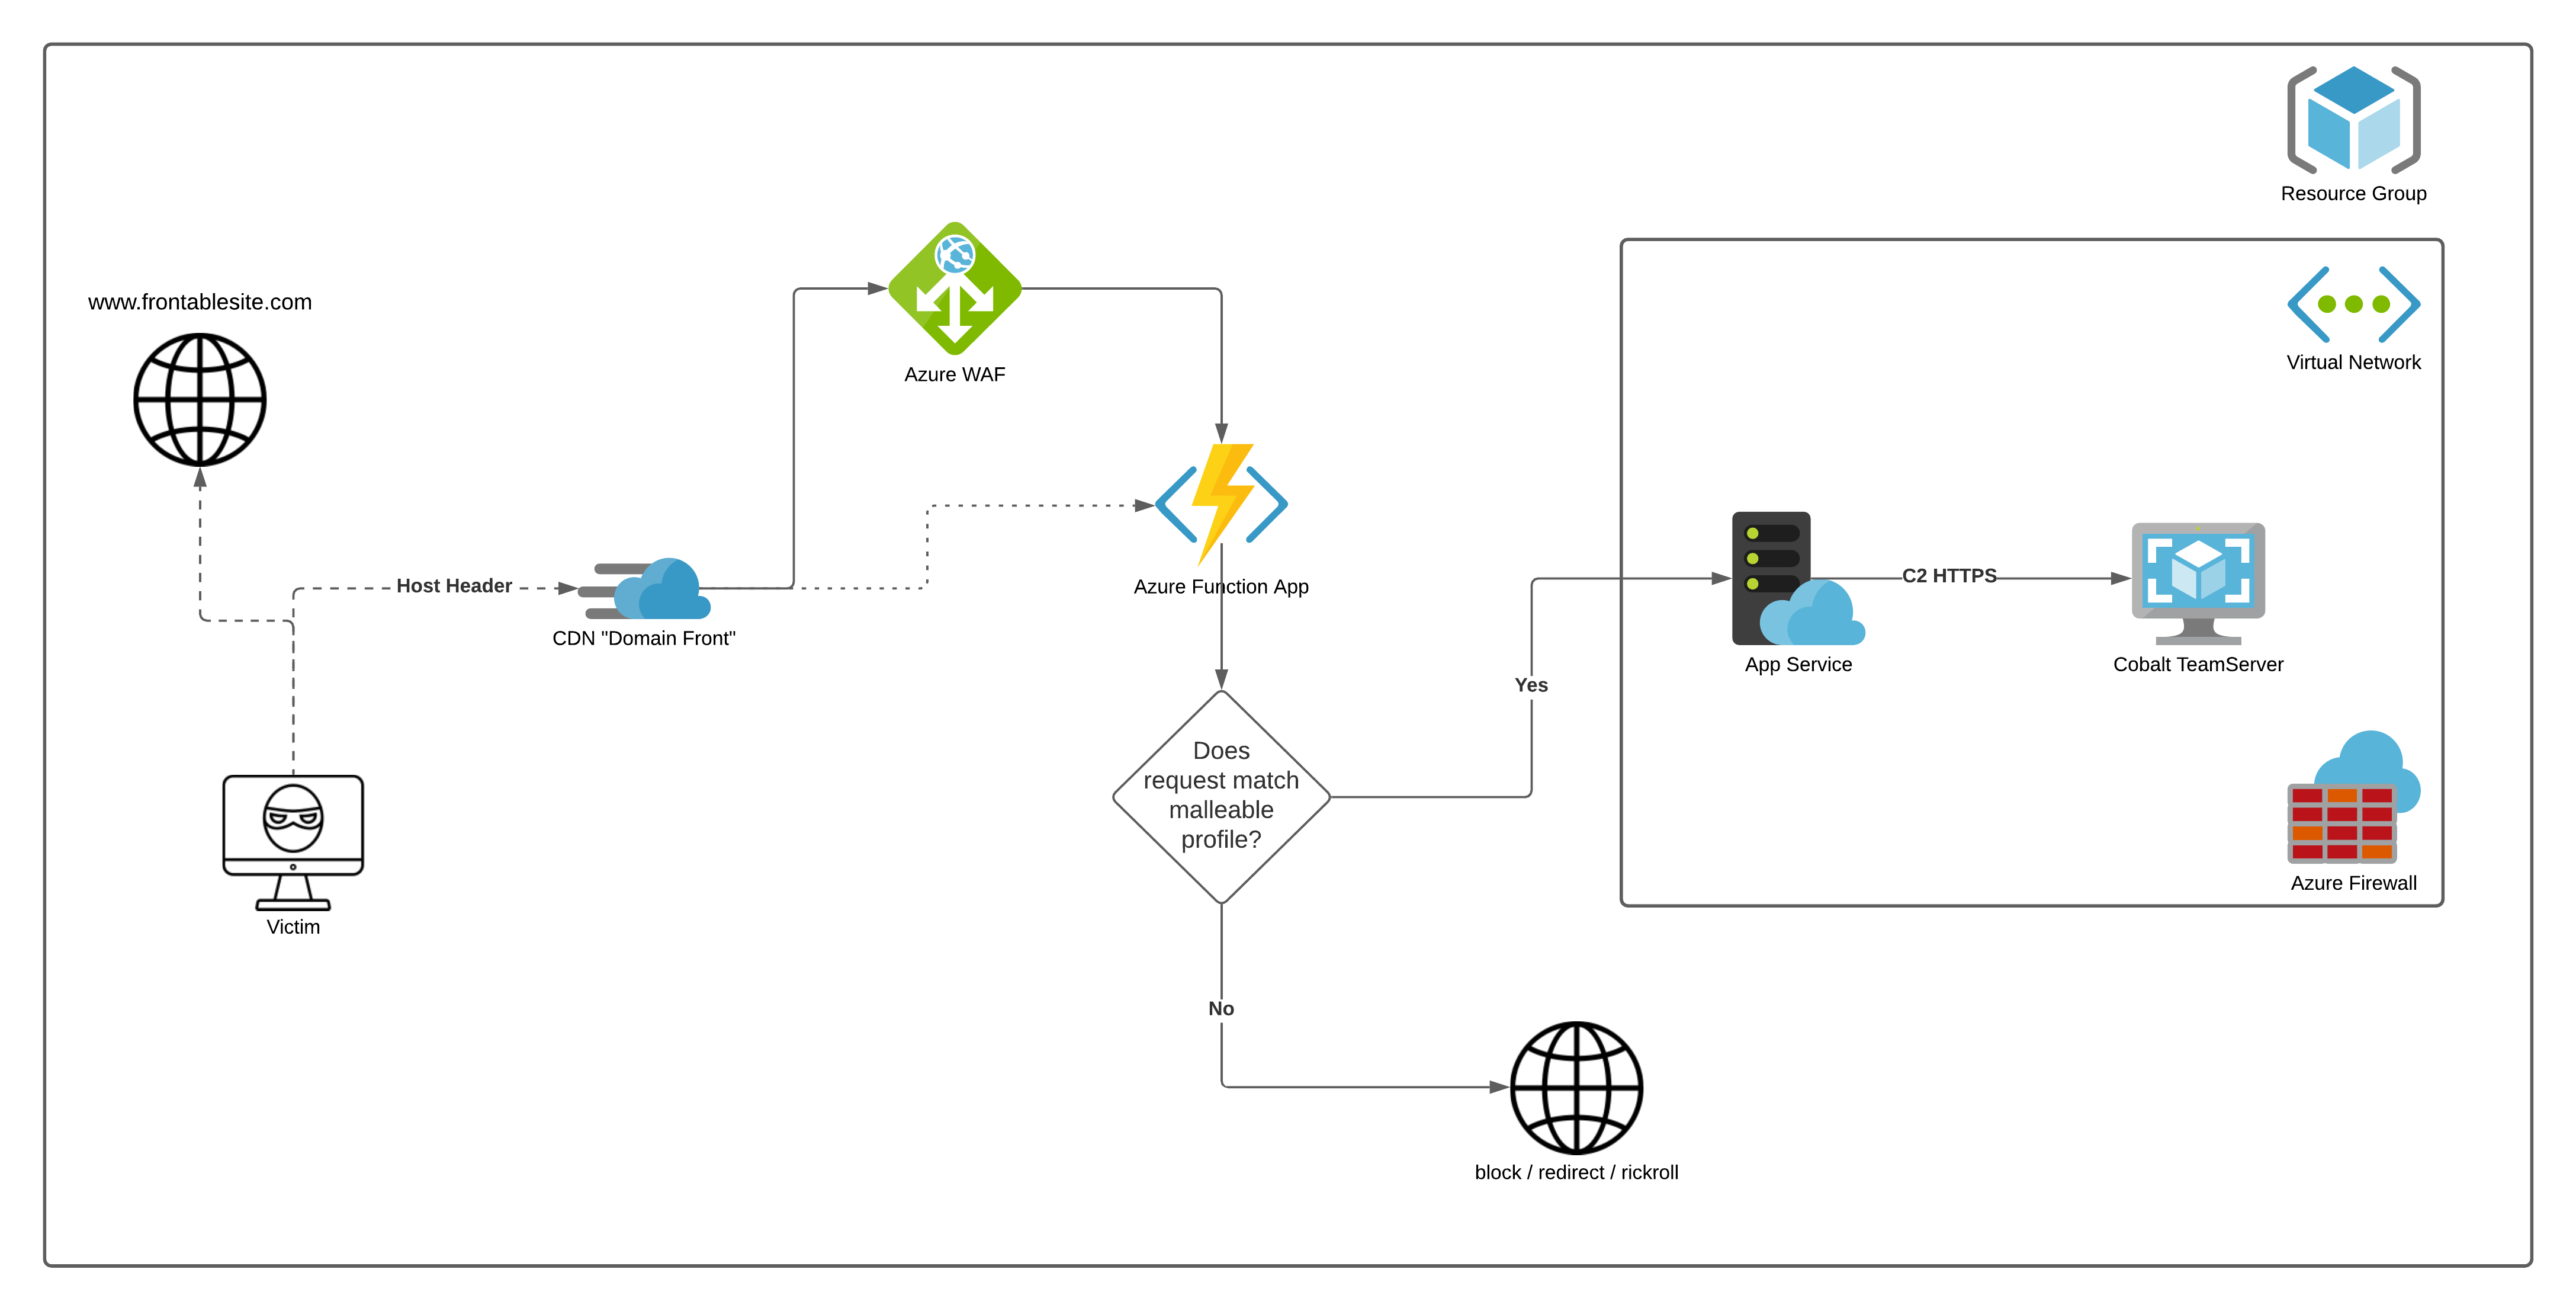
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…

PHP Webshell with handy features

🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…

Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…

Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…

SSHPry v2 - Spy & Control os SSH Connected client's TTY

Chisel new generation, written in rust. SSH under WSS with some customization.

Proof of conept to exploit vulnerable proxycommand configurations on ssh clients (CVE-2023-51385)