
CVE-2018-20250
 lamsonbinh/cve-2018-20250
Exploit script for CVE-2018-20250 (WinRAR ACE path traversal) with integrated Metasploit payload generation and reverse shell delivery for…
command-and-controlexploitationpayload-generation+3
lamsonbinh/cve-2018-20250Exploit script for CVE-2018-20250 (WinRAR ACE path traversal) with integrated Metasploit payload generation and reverse shell delivery for…
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 tannlh/cve-2018-20250
Exploit for CVE-2018-20250 (WinRAR ACE path traversal) with automated payload generation and Metasploit reverse shell integration for penetration…
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.
 exploit-install/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 nulltrace1336/samba-exploit-cve-2007-2447
Step-by-step guide to exploiting Samba 3.0.20 (CVE-2007-2447) using Metasploit, including Nmap scanning, payload setup, and reverse shell execution.
 afifudinmtop/cve-2009-3103
Exploit for CVE-2009-3103, a Windows SMB remote code execution vulnerability, with a Python script and Metasploit handler for reverse shell.
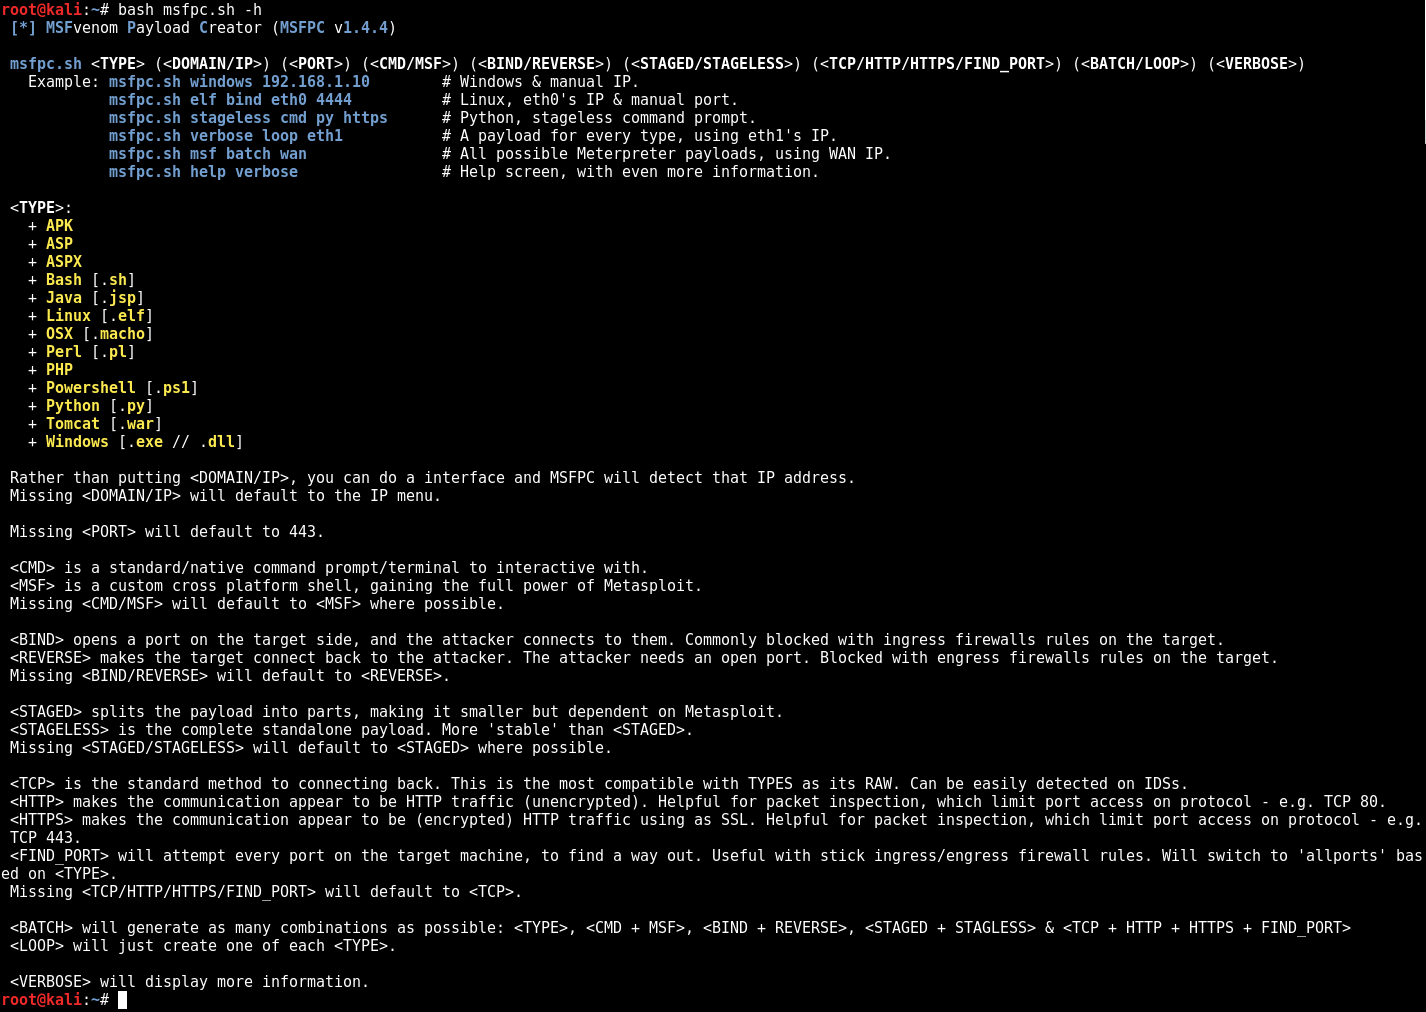 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
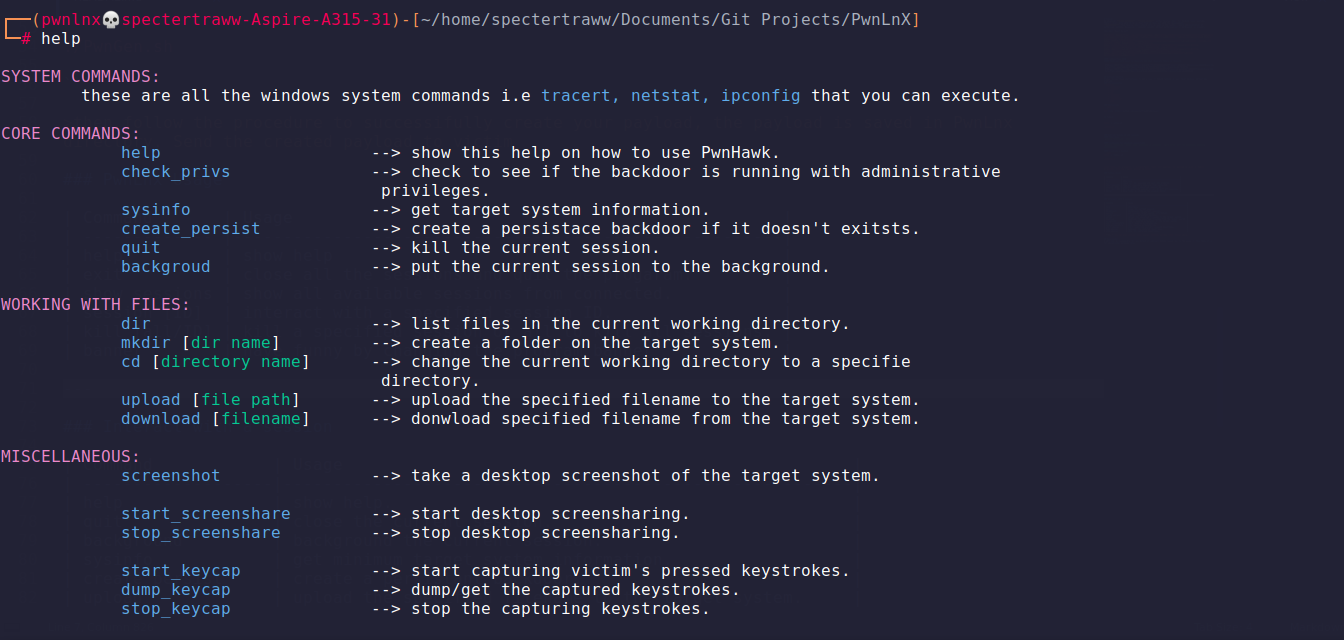 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
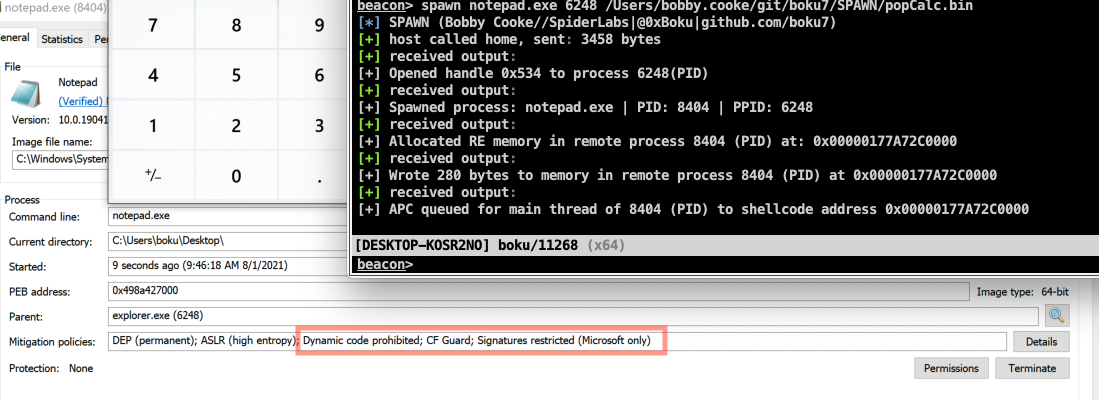 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 d00mfist/mystikal
macOS Initial Access Payload Generator