
sh4d0wup
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
command-and-controlexploitationpayload-development+3
kpcyrd/sh4d0wupSigning-key abuse and update exploitation framework
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
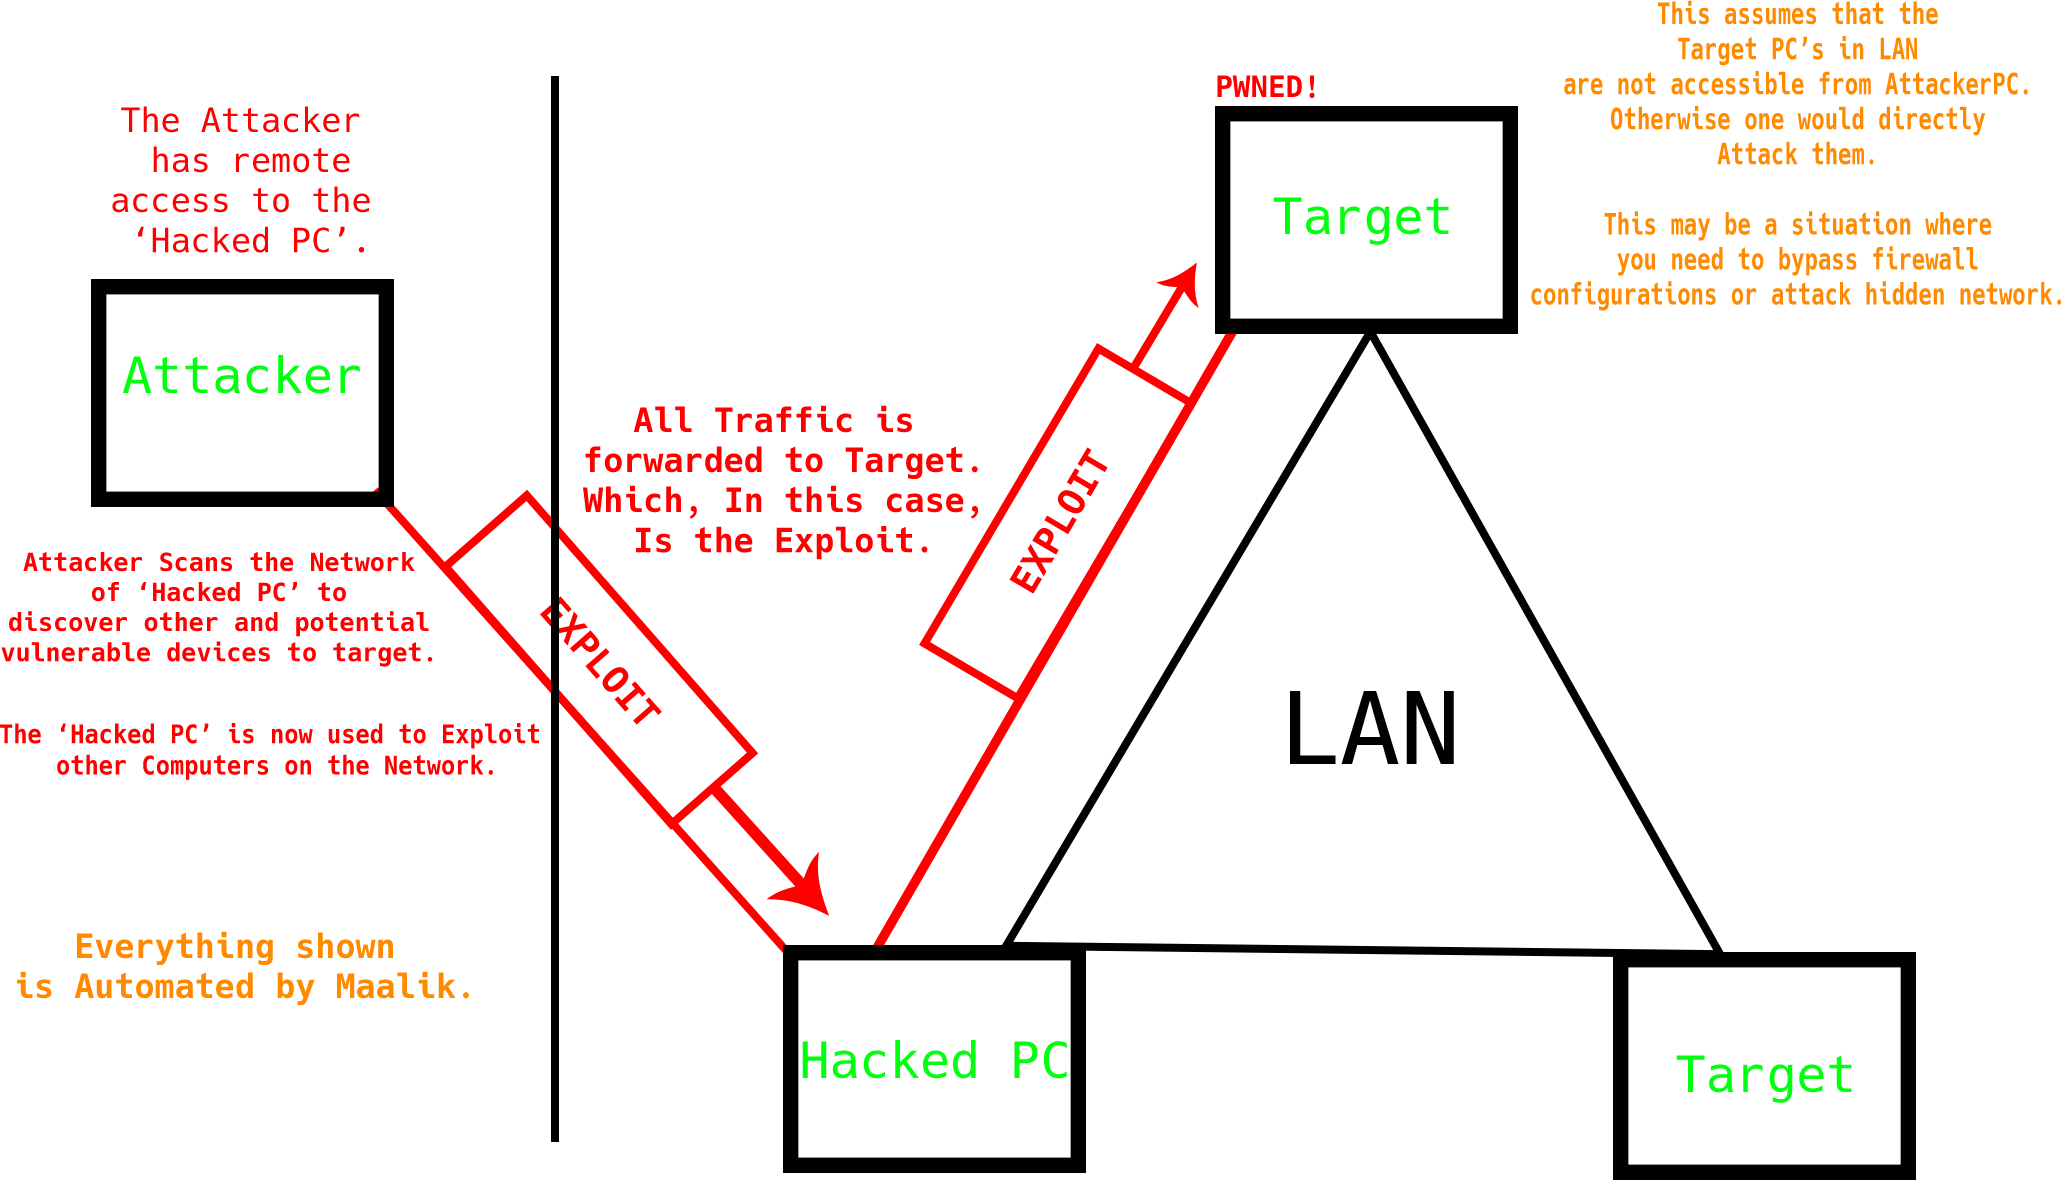 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 beefproject/beef
The Browser Exploitation Framework Project
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 vulncheck-oss/go-exploit
Go-based exploit development framework with built-in phases for target verification, version scanning, exploitation, and C2. Supports multiple…
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
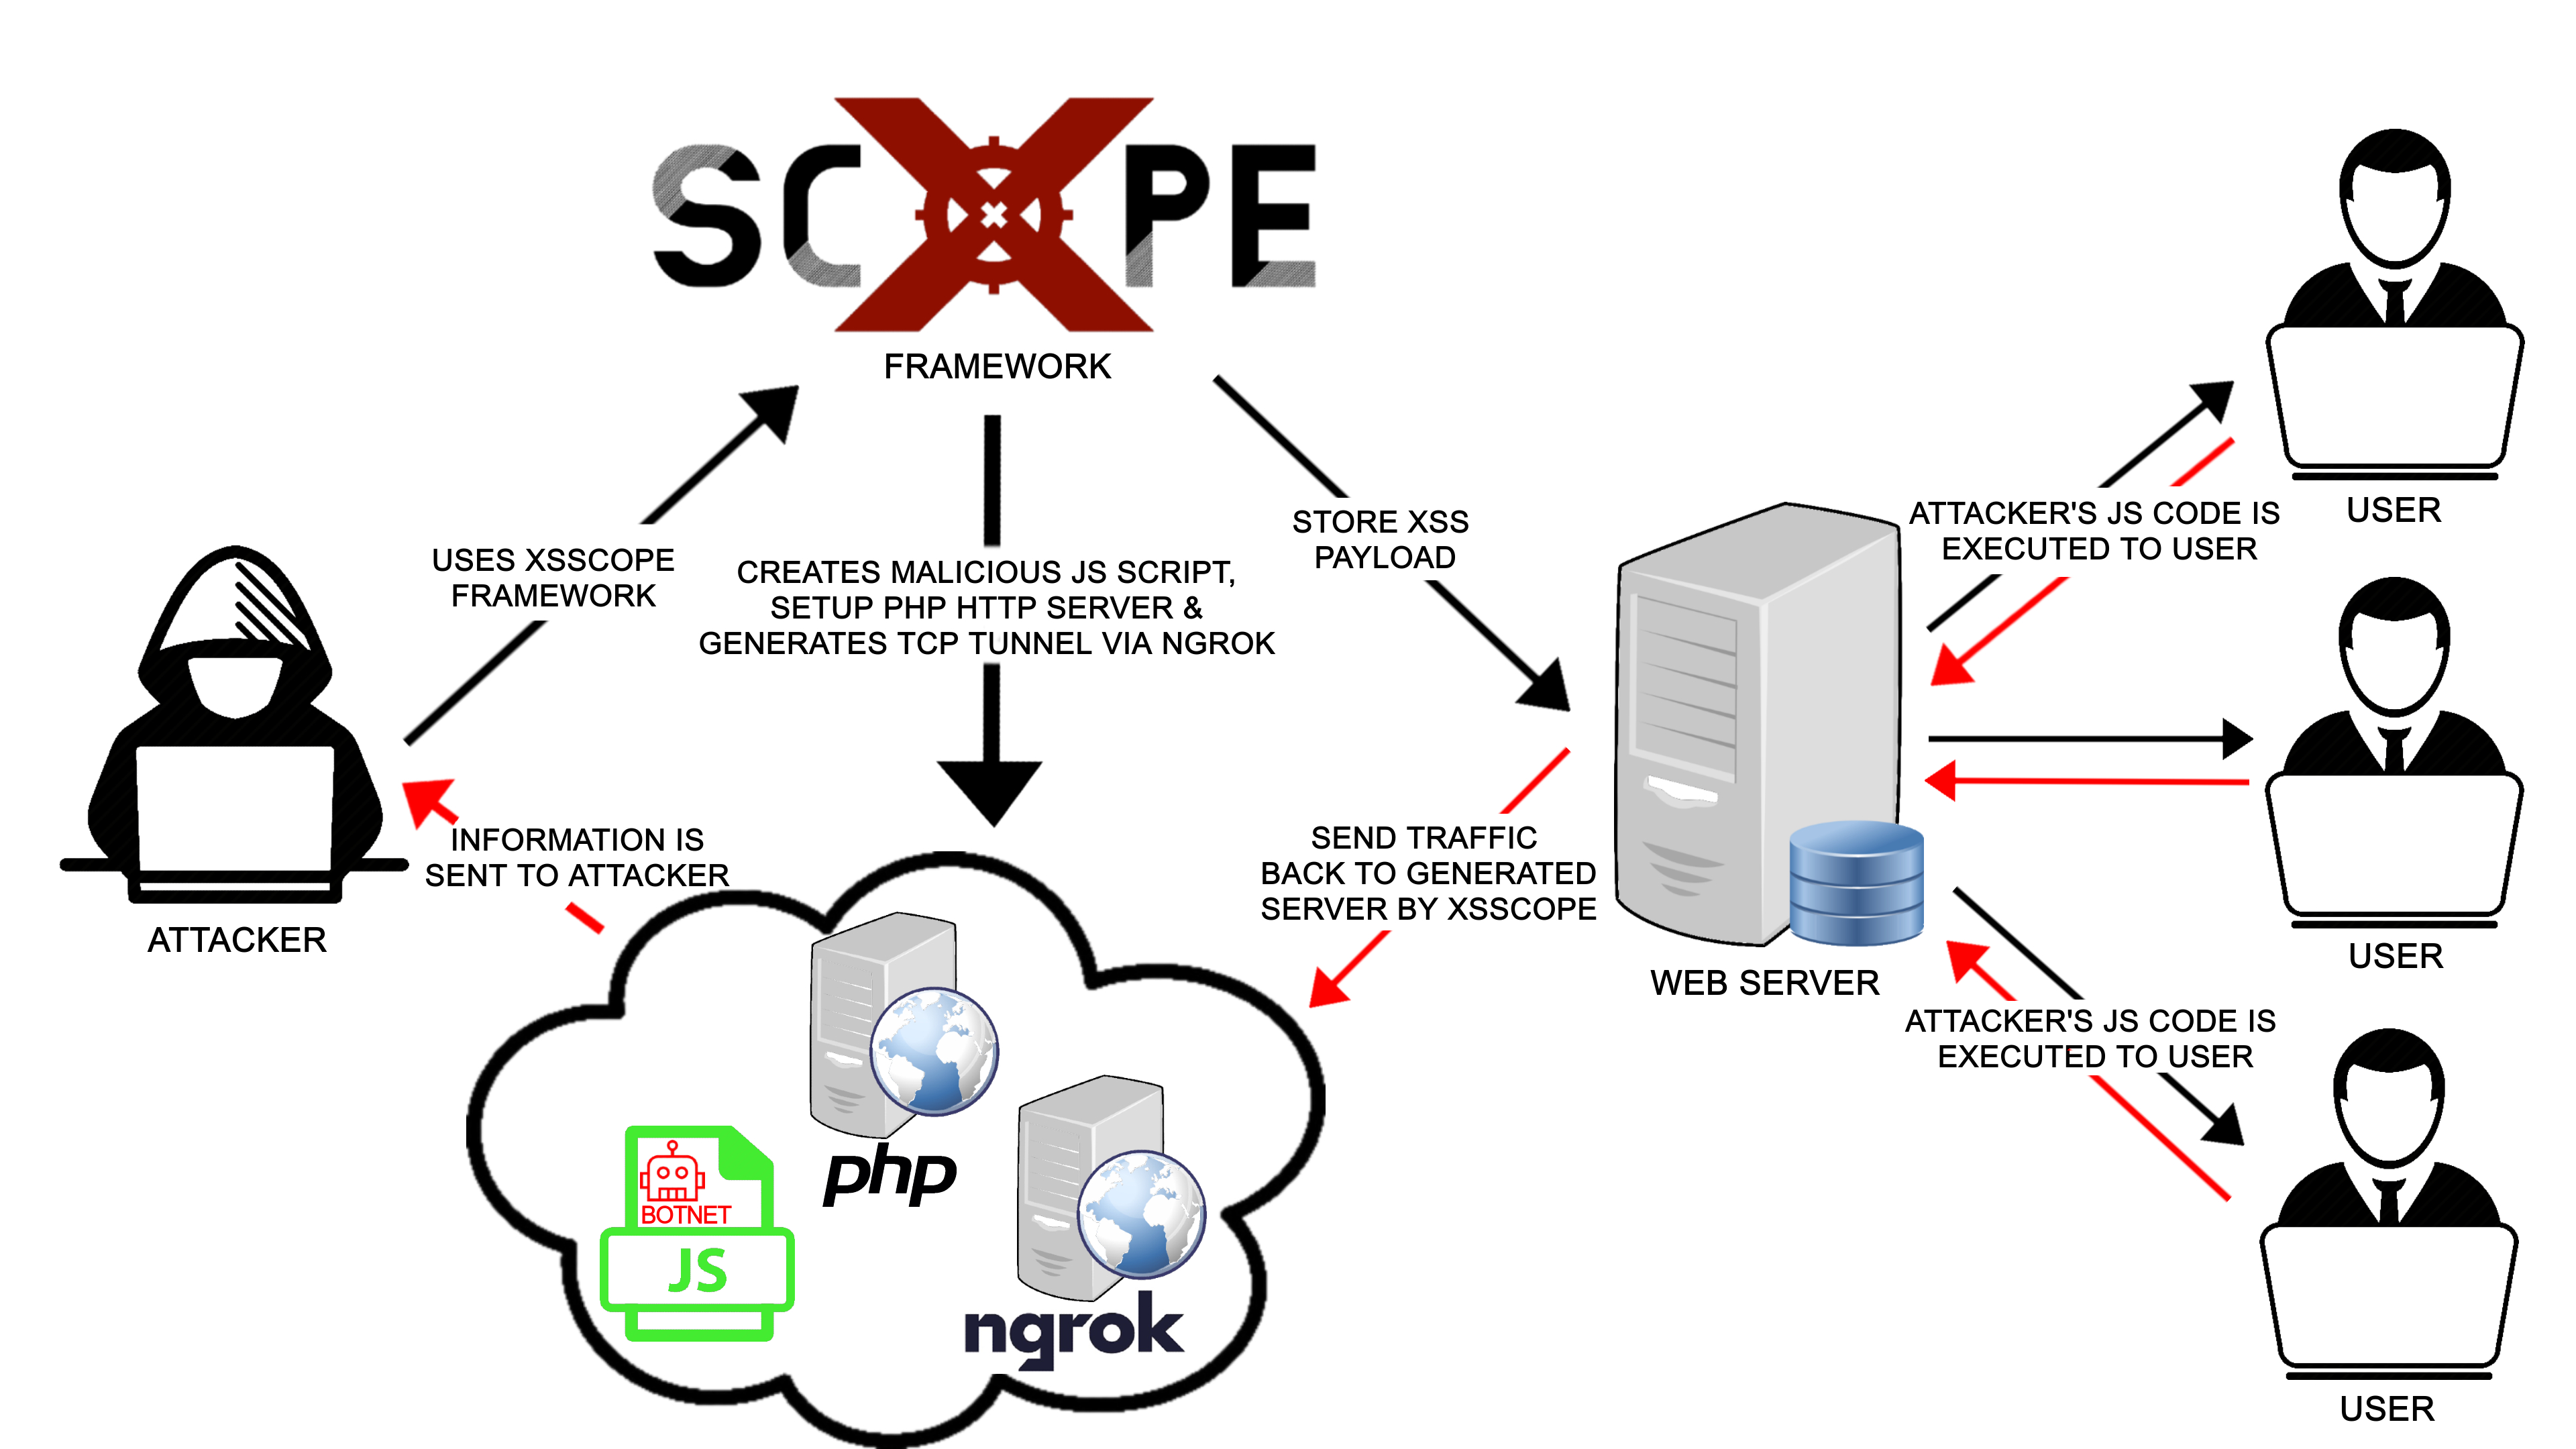 kleiton0x00/xsscope
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 luc10/struts-rce-cve-2017-9805
Go-based remote code execution tool targeting Apache Struts CVE-2017-9805 with single-target and batch-file scanning modes for automated exploitation.
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
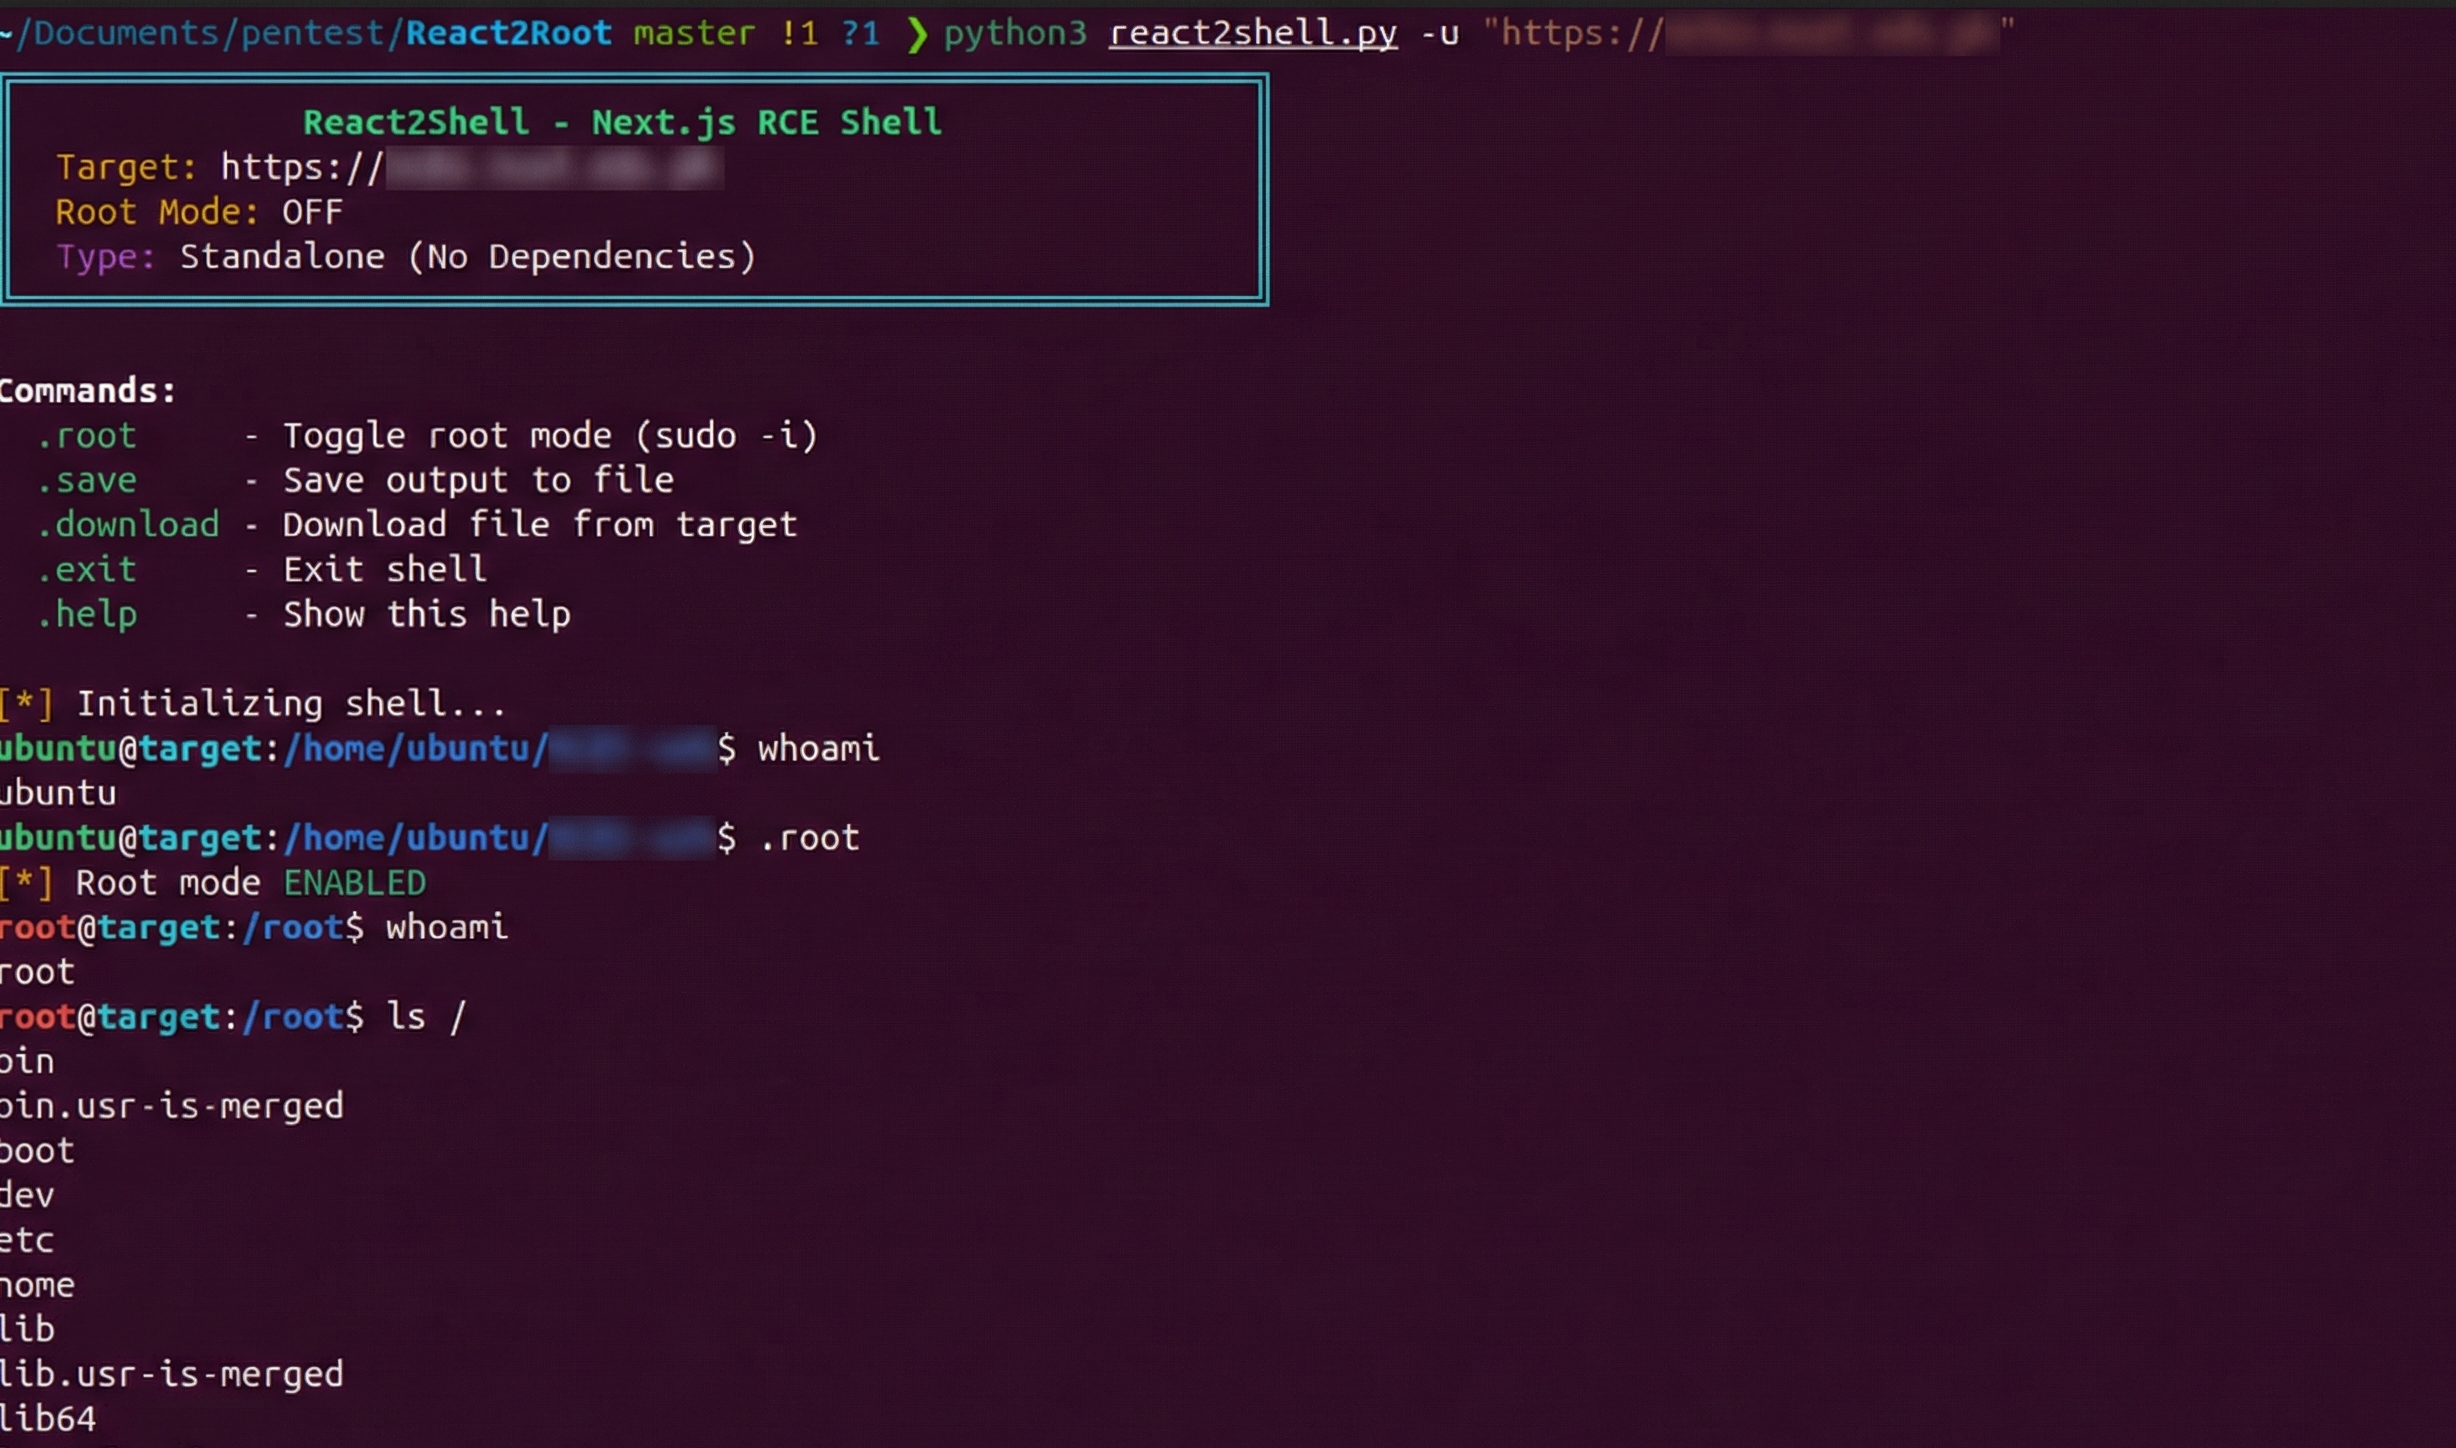 xalgord/react2shell
Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)
 7h30th3r0n3/ollamahound
Mass reconnaissance, version fingerprinting, CVE tester and live exploitation framework for Ollama open instances.
 sumanrox/rschunter
Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…