

r77-rootkit
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k
bytecode77/r77-rootkitFileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 samybaiwir/dnslivery
Easy files and payloads delivery over DNS
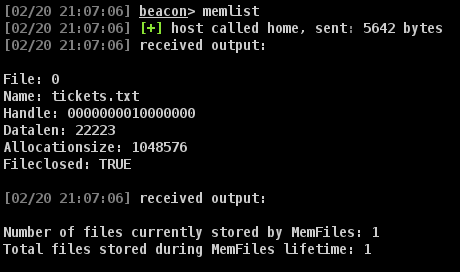 octoberfest7/memfiles
A CobaltStrike toolkit to write files produced by Beacon to memory instead of disk
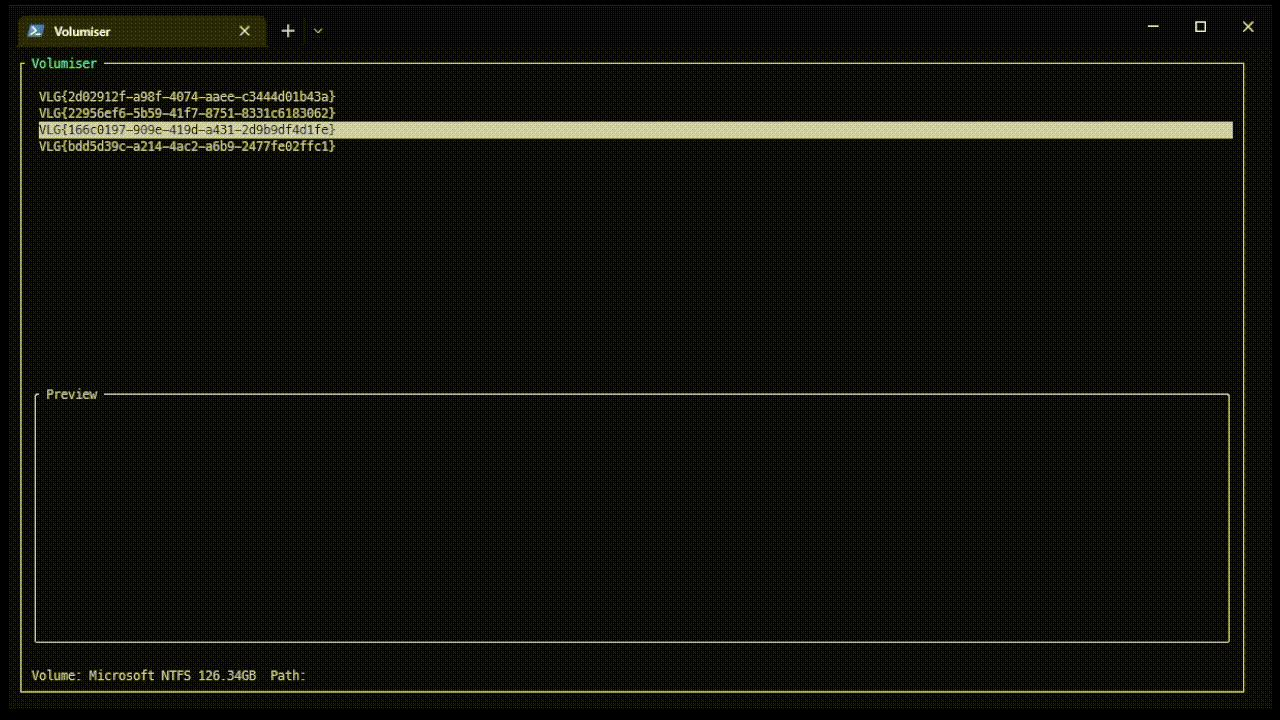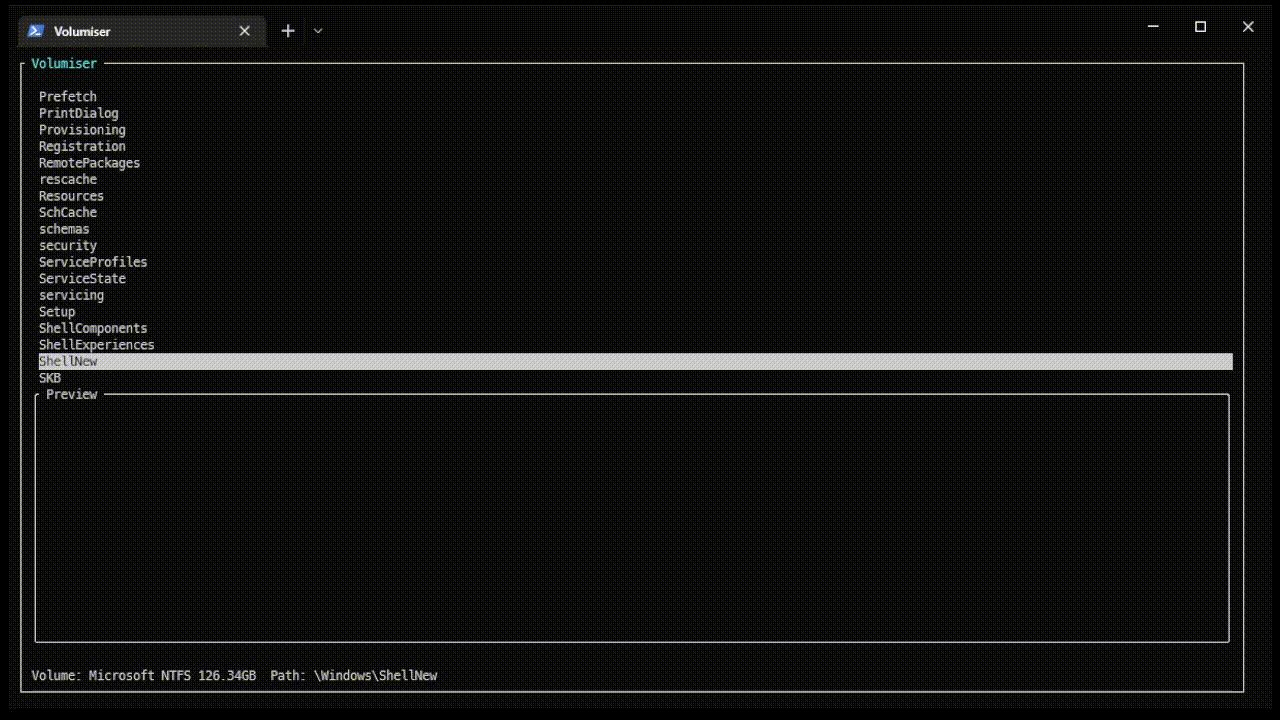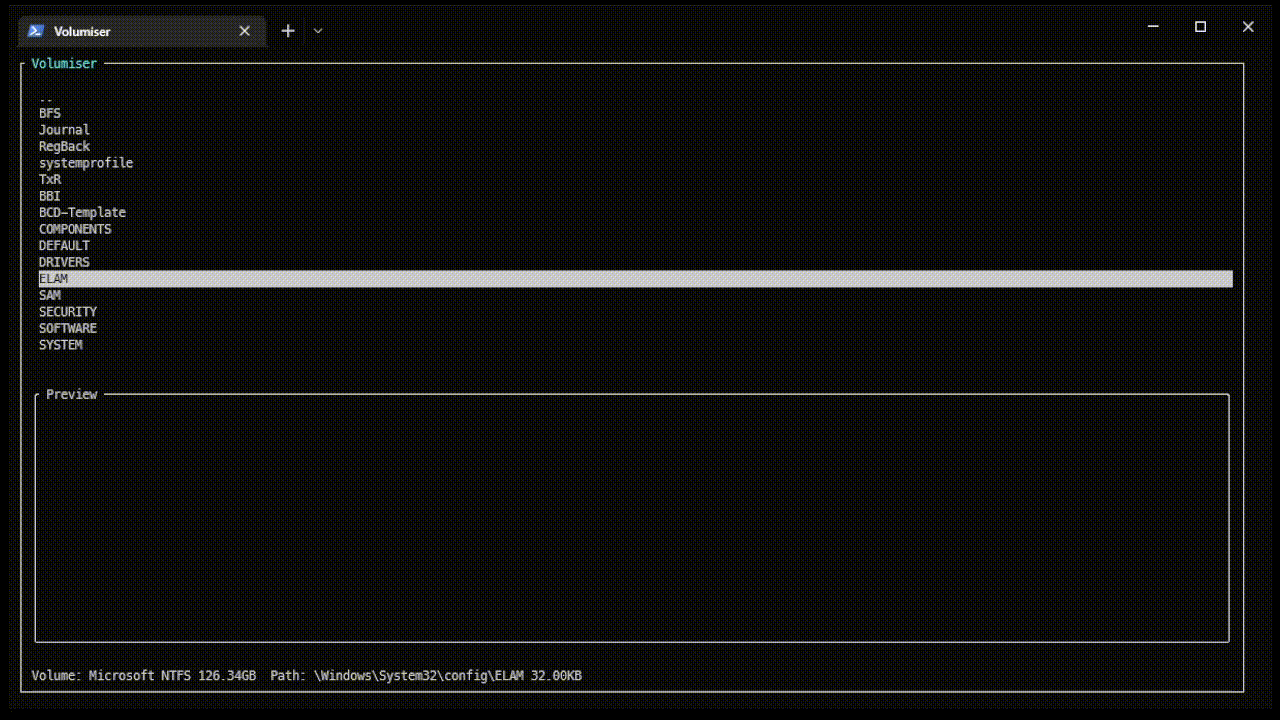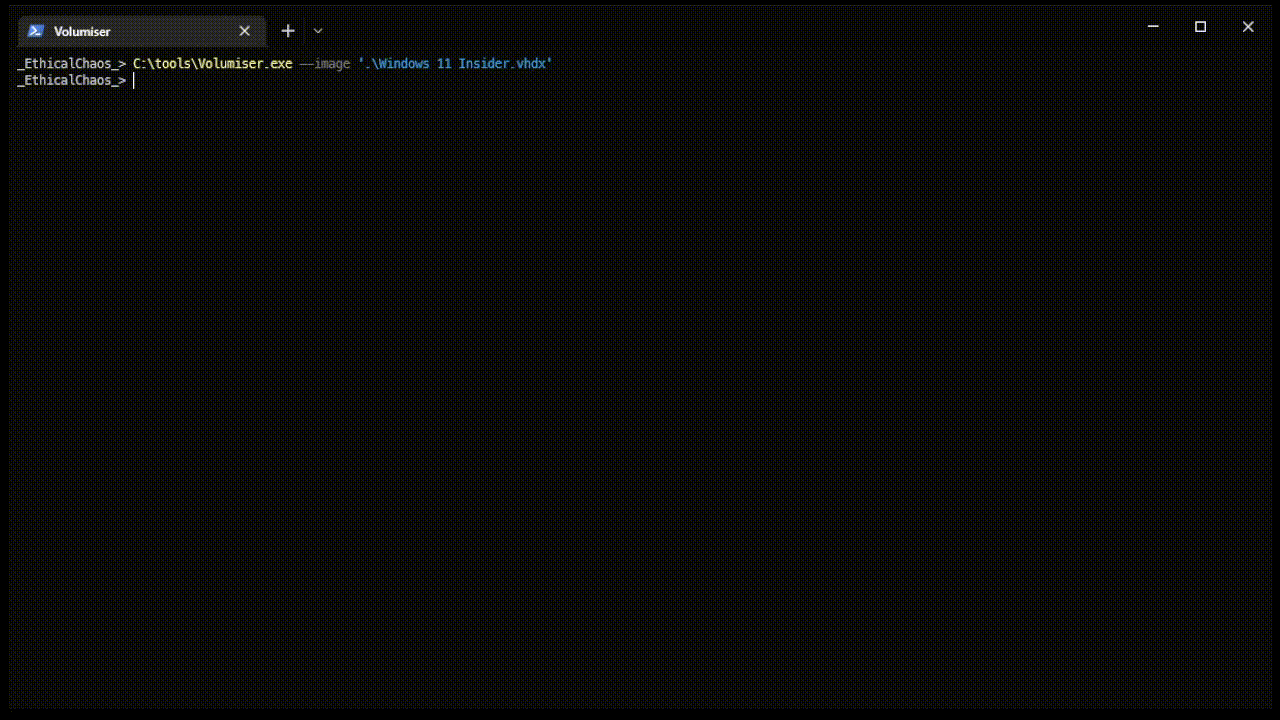 ccob/volumiser
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
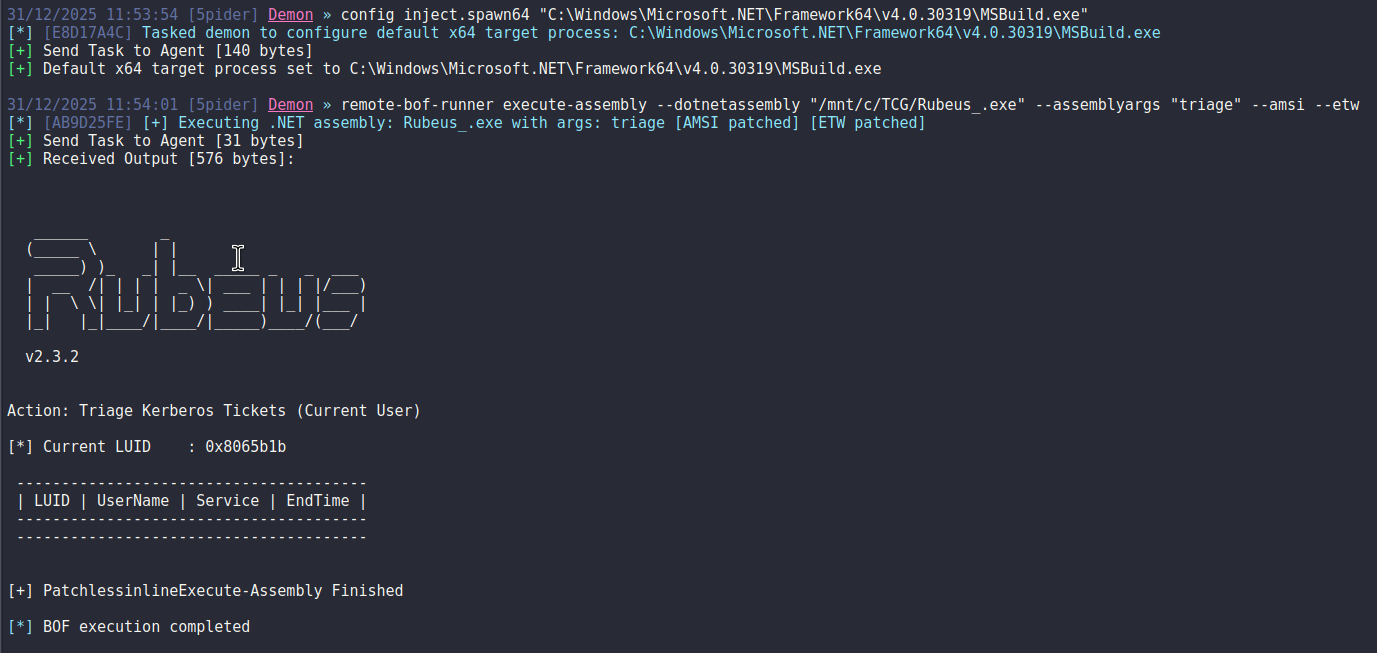 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 ricardojoserf/covert-control
Google Drive, OneDrive and Youtube as covert-channels - Control systems remotely by uploading files to Google Drive, OneDrive, Youtube or Telegram
 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
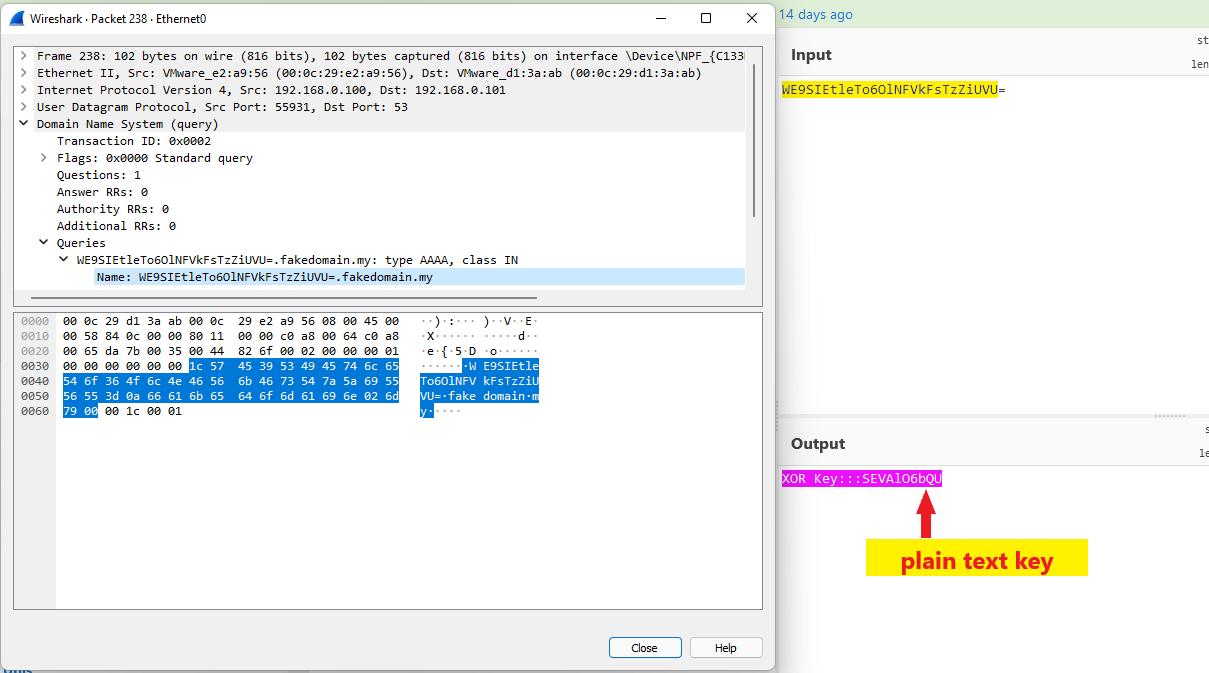 aniqfakhrul/sharpdnsexfil
C# tool for exfiltrating files over DNS using XOR and asymmetric encryption, designed for red team engagements with restricted outbound connections.
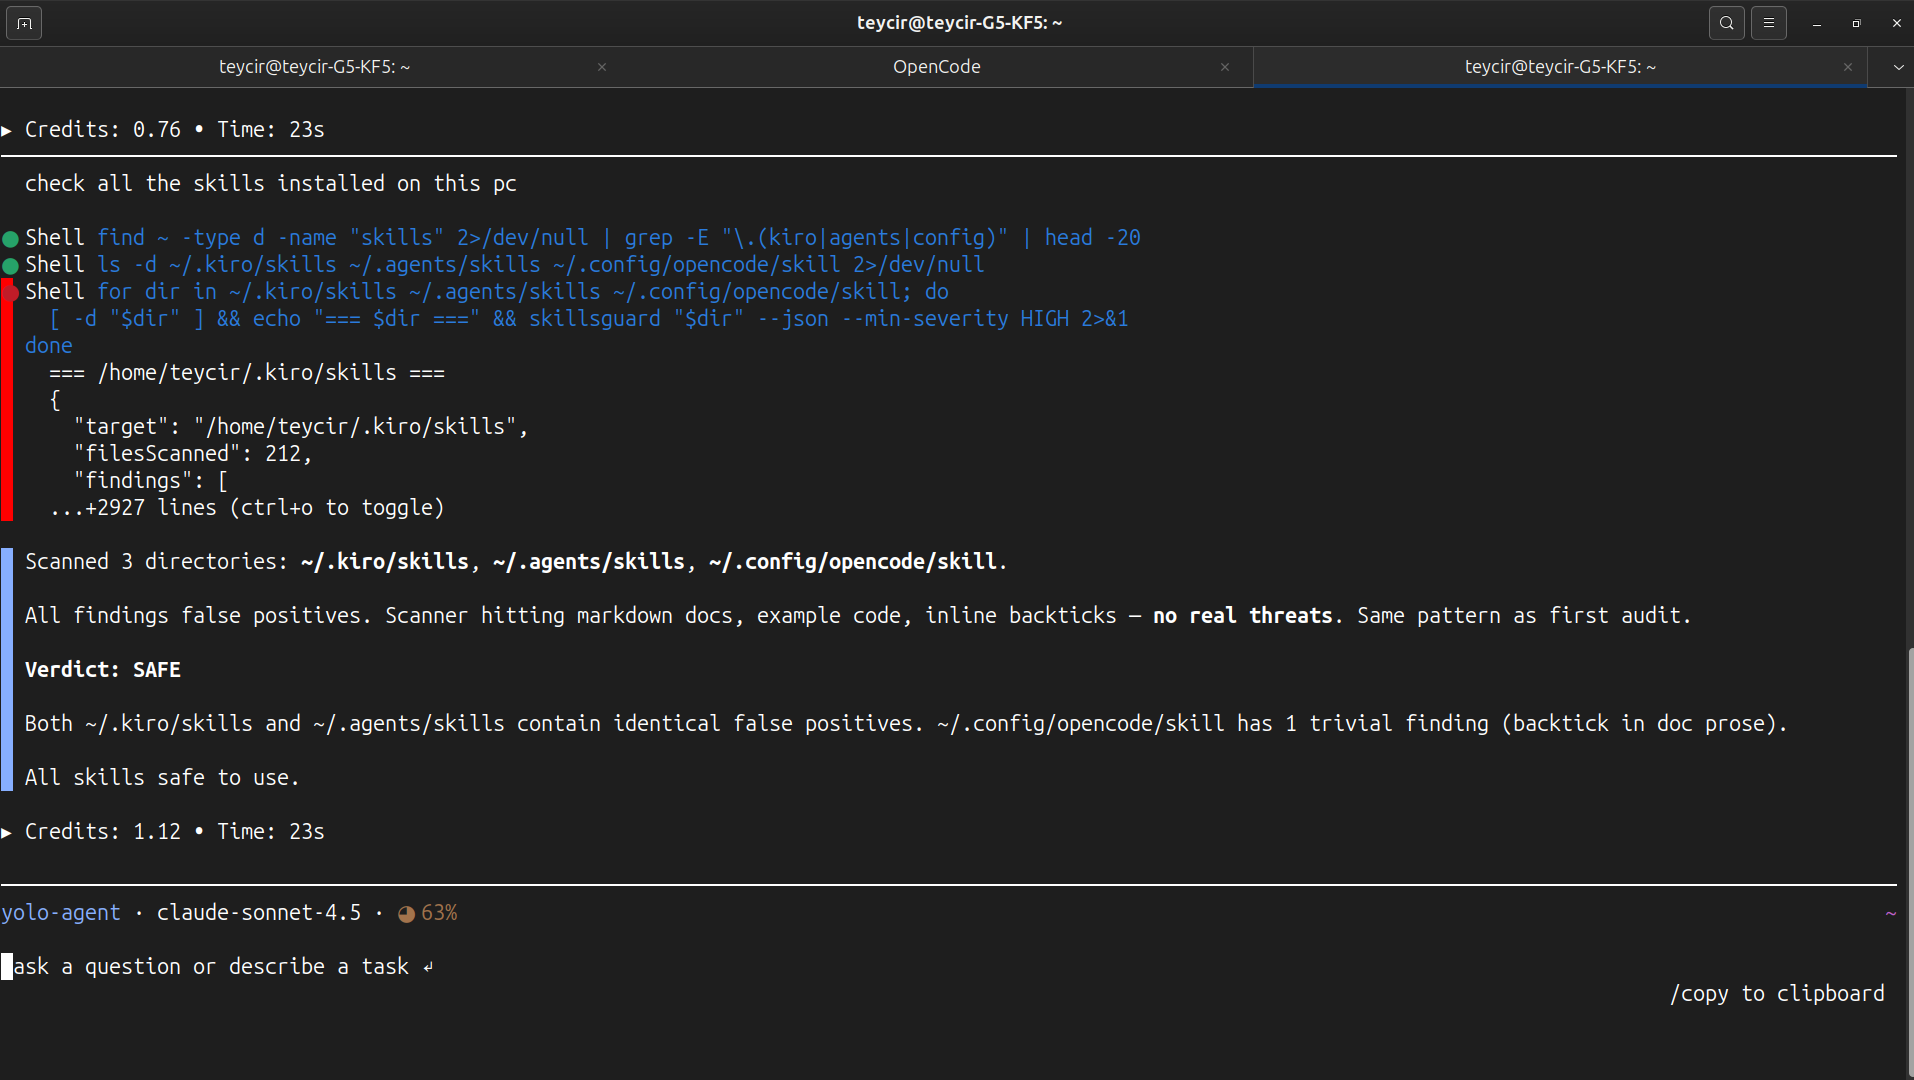 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 gerbsec/cve-2020-24572-poc
Proof-of-concept exploit for CVE-2020-24572 targeting RaspAP's misconfigured web console to execute arbitrary OS commands and upload files with…
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444