

CobaltWhispers
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
adversarial-attackcommand-and-controlids-ips-evasion+4
243
nvisosecurity/cobaltwhispersCobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 yaxser/cobaltstrike-bof
Collection of beacon BOF written to learn windows and cobaltstrike
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
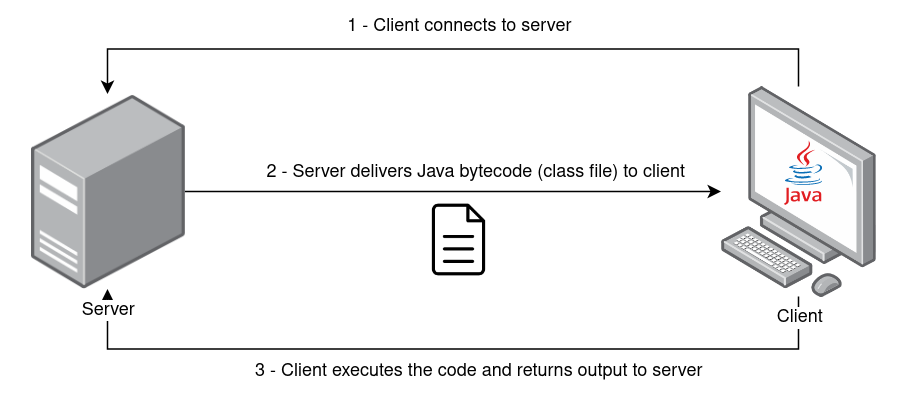 joaovarelas/java-remote-class-loader
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 rohitberiwala/cve-2025-60787-motioneye-rce
Professional PoC for CVE-2025-60787: Remote Code Execution in MotionEye (<= 0.43.1b4). This exploit demonstrates an OS Command Injection…
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
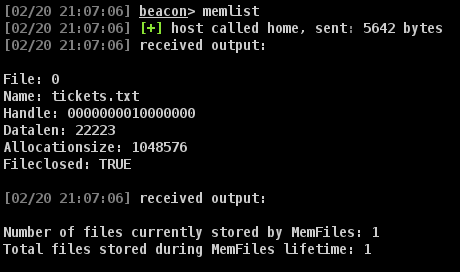 octoberfest7/memfiles
A CobaltStrike toolkit to write files produced by Beacon to memory instead of disk
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 hackfaiz/cve-2026-20841-poc
Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 mrcl0wnlab/nuclei-template-exploit-f5-big-ip-icontrol-rest-auth-bypass-rce-command-parameter
CVE-2022-1388 is an authentication bypass vulnerability in the REST component of BIG-IP’s iControl API that was assigned a CVSSv3 score of…
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)