
React2Shell
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
command-and-controlexploit-frameworkspayload-development+3
khadafigans/react2shellReact2Shell - CVE-2025-66478 RCE Exploit
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 cobbr/covenant
Covenant is a collaborative .NET C2 framework for red teamers.
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
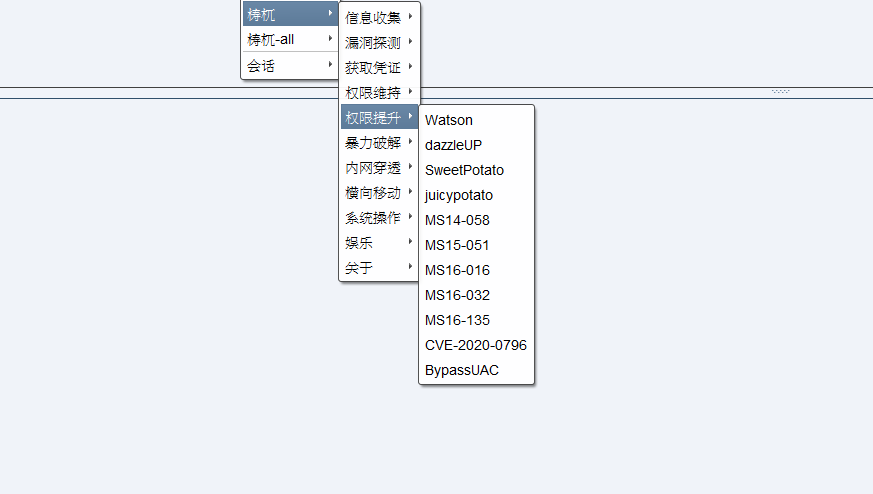 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
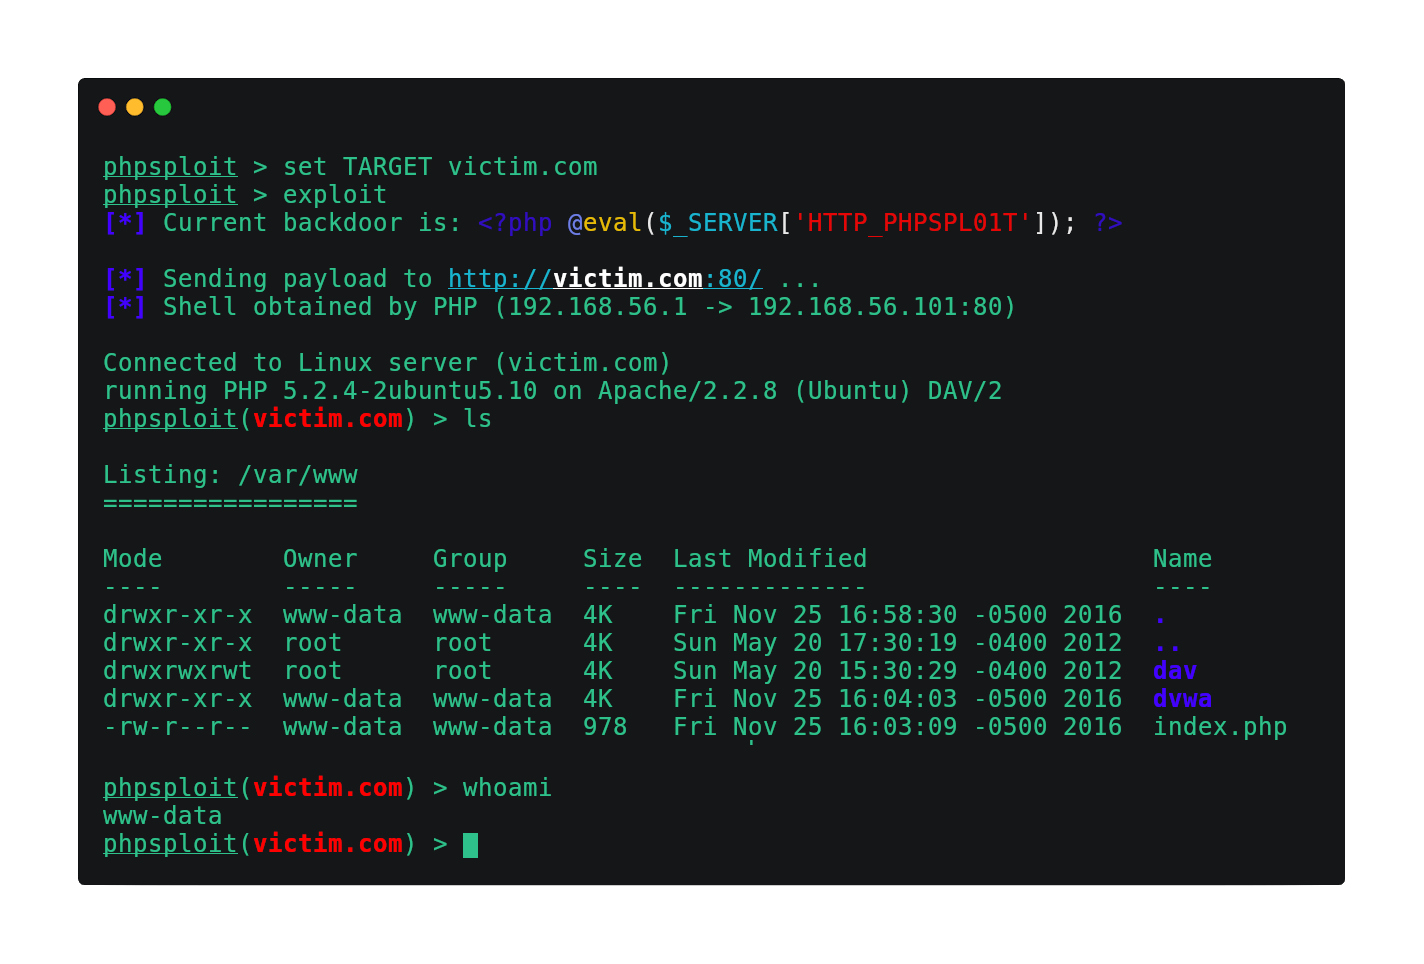 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
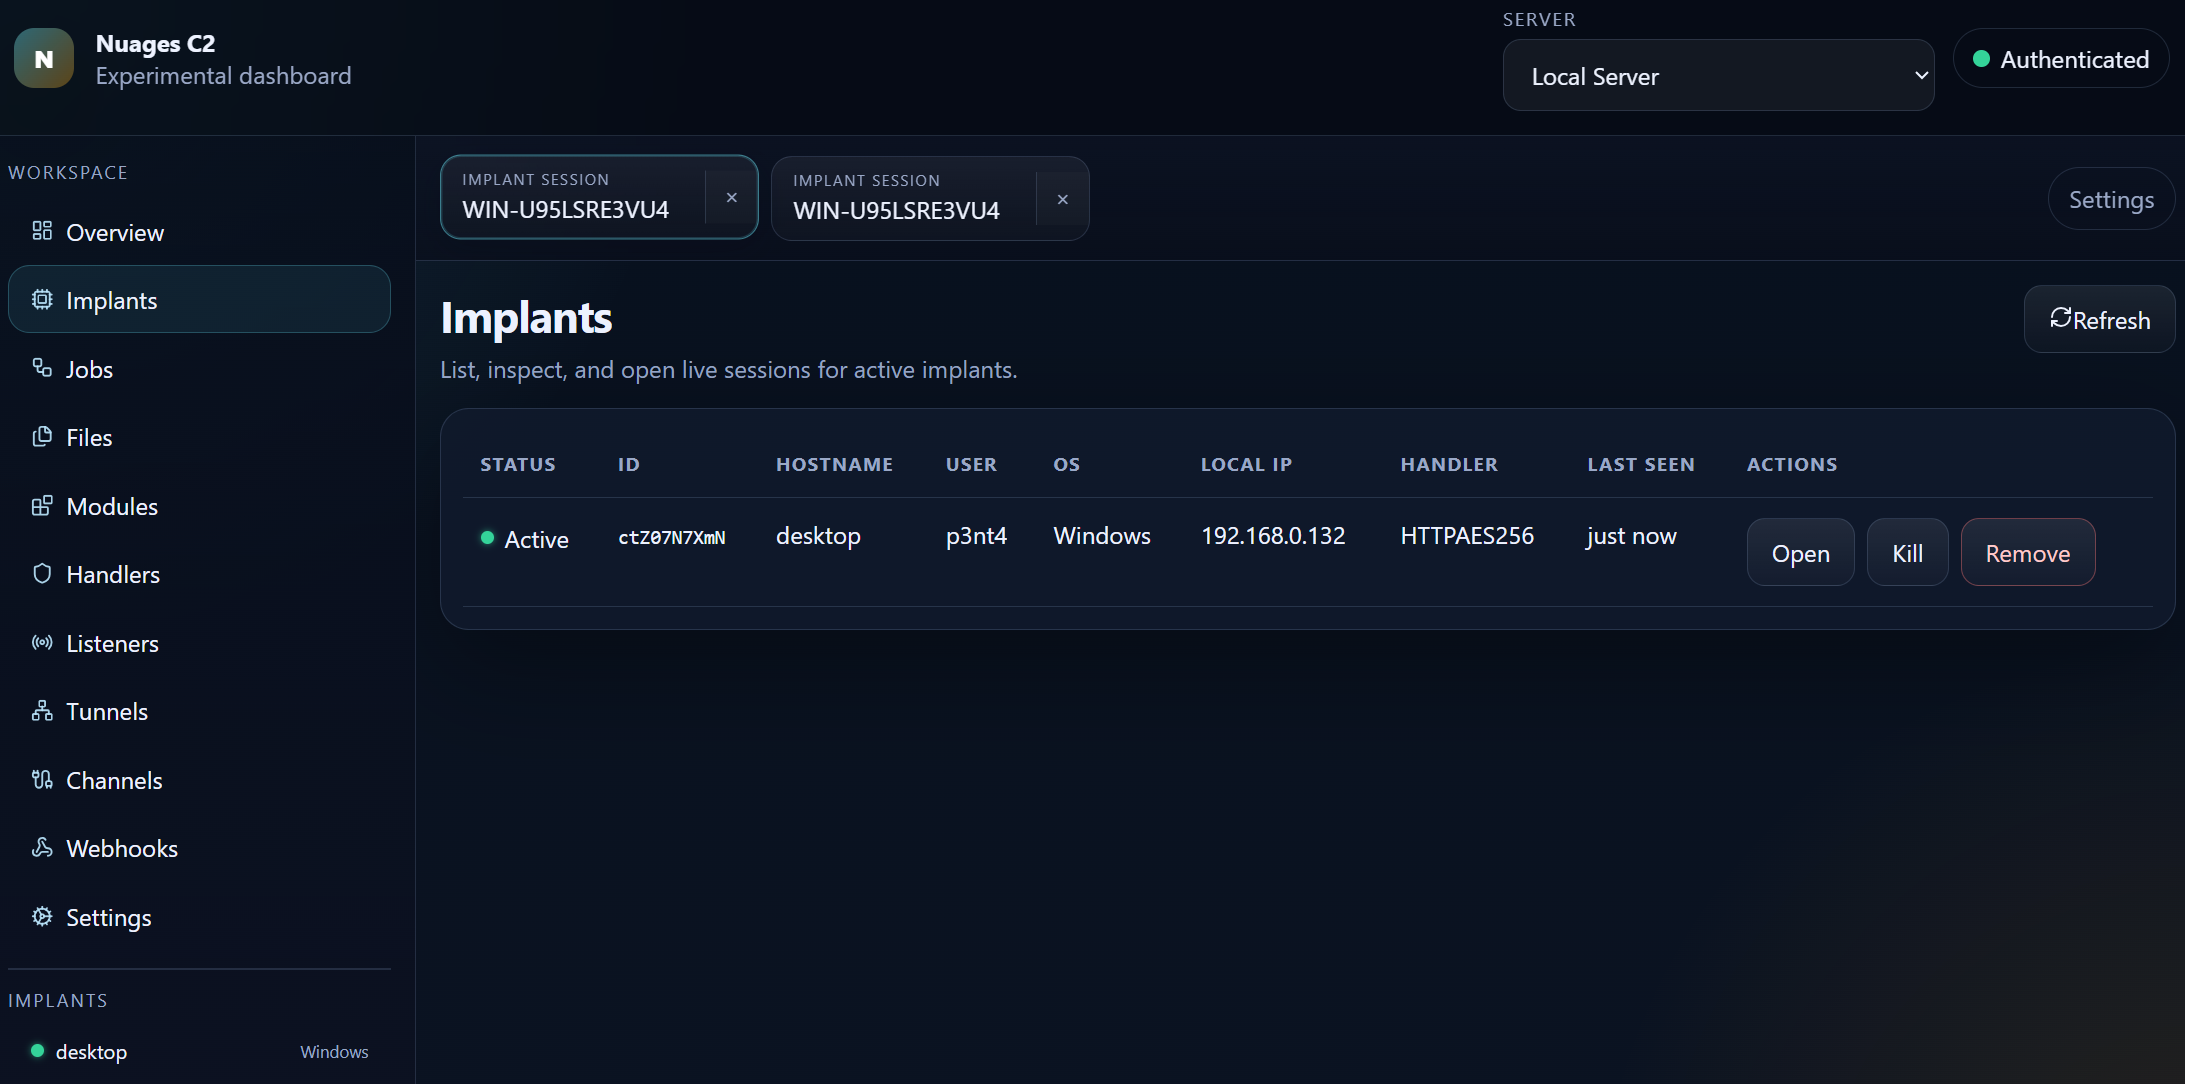
 deimosc2/deimosc2
DeimosC2 is a Golang command and control framework for post-exploitation.
 postrequest/link
link is a command and control framework written in rust
 dragoqcc/cruciblec2
A C# Command & Control framework
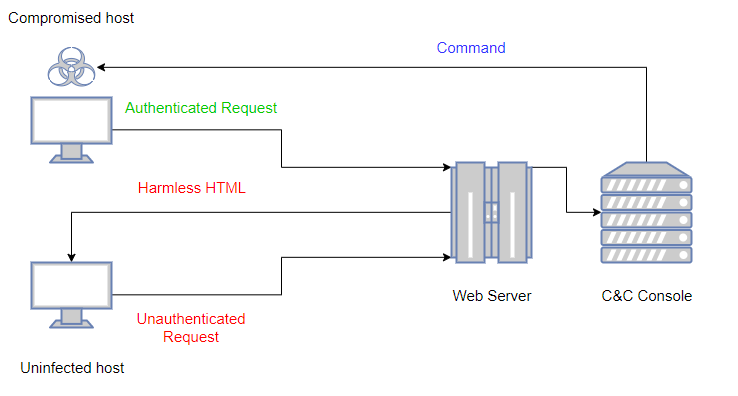 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
 gr1mmie/atlasc2
C# C2 Framework centered around Stage 1 operations
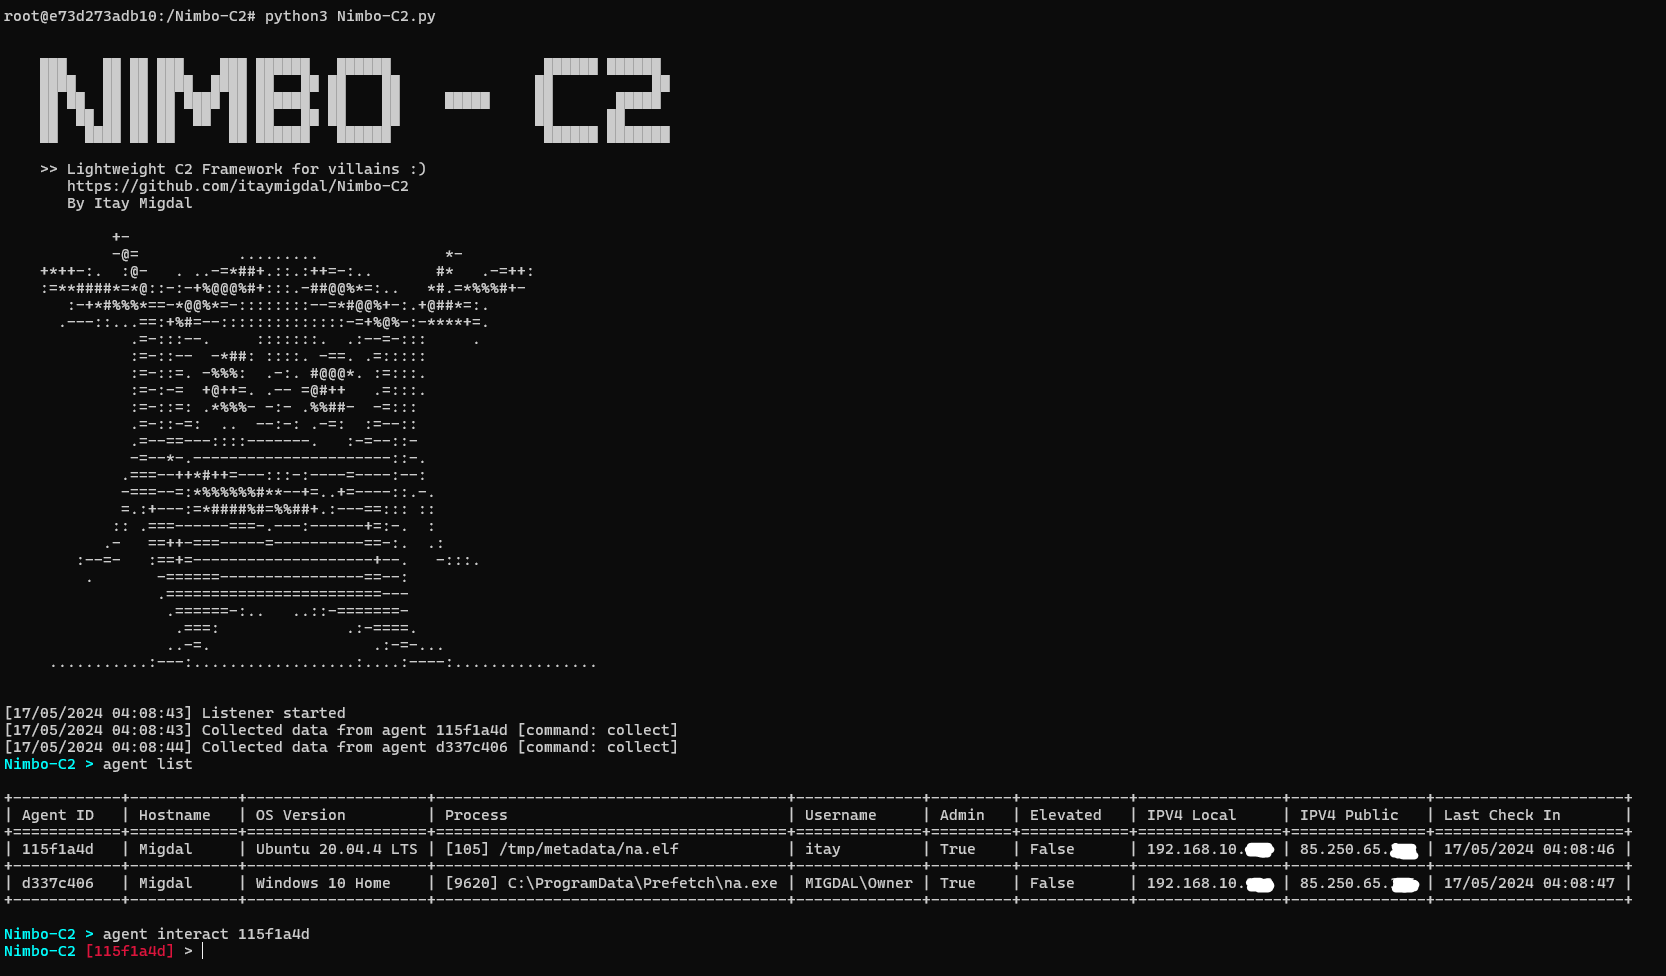 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
 darmado/atomic-red-team-c2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
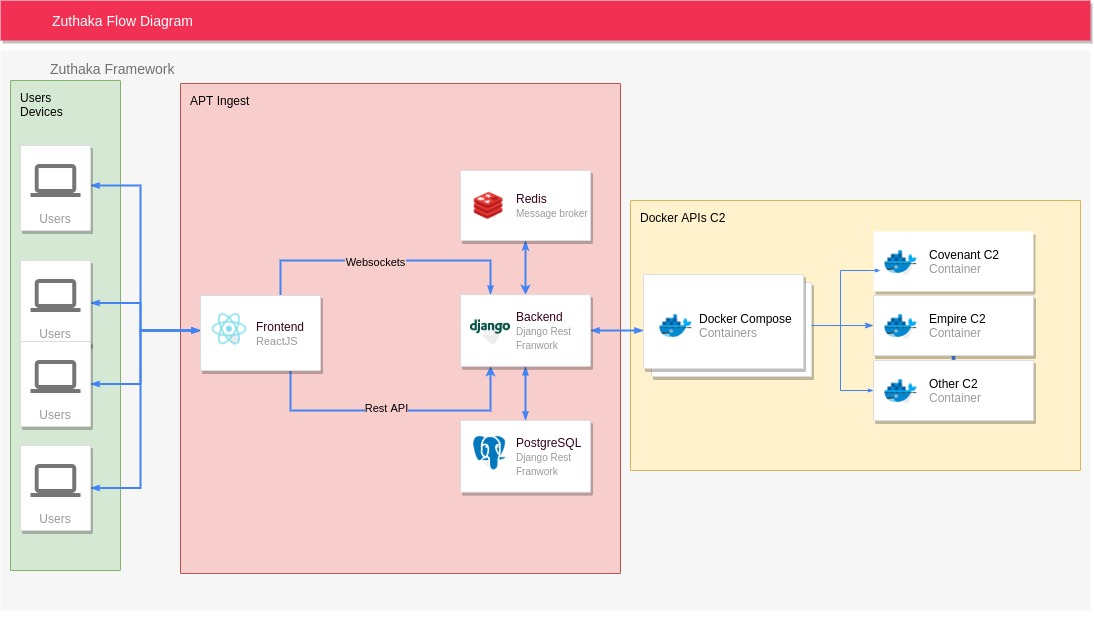 pucarasec/zuthaka
Open-source C2 integration framework providing a unified web interface for managing multiple command-and-control instances, listeners, agents, and…