Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
690 results
Log4Shell-CVE-2021-44228-PoC preview

Log4Shell-CVE-2021-44228-PoC

GitHubpierpaolosestito-dev/log4shell-cve-2021-44228-poc

CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.
command-and-controlexploitationpayload-development+3
1
3 years ago
follina-spring preview

follina-spring

GitHubdsibilio/follina-spring

Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)

command-and-controlexploitationpayload-generation+3
44 years ago
CVE-2018-2380 preview

CVE-2018-2380

GitHuberpscanteam/cve-2018-2380

PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
command-and-controlexploitationpayload-generation+3
528 years ago
Log4j-Exploit-CVE-2021-44228 preview

Log4j-Exploit-CVE-2021-44228

GitHubwillian-2-0-0-1/log4j-exploit-cve-2021-44228

Exploit tool for CVE-2021-44228 (Log4Shell) that sets up a malicious LDAP server and delivers a Java payload to achieve remote code execution on…
command-and-controlexploitationpayload-generation+3
4 years ago
Exploit-CVE-2019-2725 preview

Exploit-CVE-2019-2725

GitHubcalegarimindsec/exploit-cve-2019-2725

Exploit for CVE-2019-2725 in Oracle WebLogic Server, using crafted SOAP requests to achieve remote code execution via Java deserialization.
command-and-controlexploitationpayload-generation+2
2 years ago
Expoitation-de-la-vuln-rabilit-CVE-2022-22965 preview

Expoitation-de-la-vuln-rabilit-CVE-2022-22965

GitHubguigui237/expoitation-de-la-vuln-rabilit-cve-2022-22965

Python exploit for CVE-2022-22965 (Spring4Shell) RCE vulnerability in Java Spring Core. Injects a JSP webshell via Tomcat log configuration to…
command-and-controlexploitationpayload-generation+3
1 year ago
CVE-2018-3191 preview

CVE-2018-3191

GitHublibraggbond/cve-2018-3191

CVE-2018-3191 反弹shell

command-and-controlexploitationpayload-generation+3
637 years ago
CVE-2022-26134_Behinder_MemShell preview

CVE-2022-26134_Behinder_MemShell

GitHubmaskcybersecurityteam/cve-2022-26134_behinder_memshell

Java-based exploit for CVE-2022-26134 that deploys a Behinder memory shell on vulnerable Atlassian Confluence servers for remote command execution.
command-and-controlexploitationpayload-generation+3
83 years ago
struts2-tool preview

struts2-tool

GitHubgu-007/struts2-tool

Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
command-and-controlexploitationpayload-development+5
126 days ago
log4j-rce-test preview

log4j-rce-test

GitHubjeffli1024/log4j-rce-test

Quick test environment for CVE-2021-44228 Log4j RCE vulnerability with a built-in exploit server and customizable payload execution.
command-and-controlexploitationpayload-generation+2
24 years ago
Jmeter-CVE-2018-1297- preview

Jmeter-CVE-2018-1297-

GitHub48484848484848/jmeter-cve-2018-1297-

Dockerized vulnerable Apache JMeter RMI environment for CVE-2018-1297 deserialization RCE, with ysoserial exploit commands, verification, and…
command-and-controlexploitationpayload-generation+3
2 years ago
CVE-2022-30190-follina-Office-MSDT-Fixed preview

CVE-2022-30190-follina-Office-MSDT-Fixed

GitHubkomomon/cve-2022-30190-follina-office-msdt-fixed

Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
command-and-controlexploitationpayload-generation+3
3903 years ago
outis preview

outis

GitHubsyss-research/outis

outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…

command-and-controldns-analysispayload-generation+3
1269 years ago
CVE-2019-3980 preview

CVE-2019-3980

GitHubwarferik/cve-2019-3980

Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
command-and-controlexploitationpayload-generation+3
185 years ago
async-pico-hub preview

async-pico-hub

GitHubnccgroup/async-pico-hub

Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
command-and-controlpayload-developmentpenetration-testing-frameworks+2
273 months ago
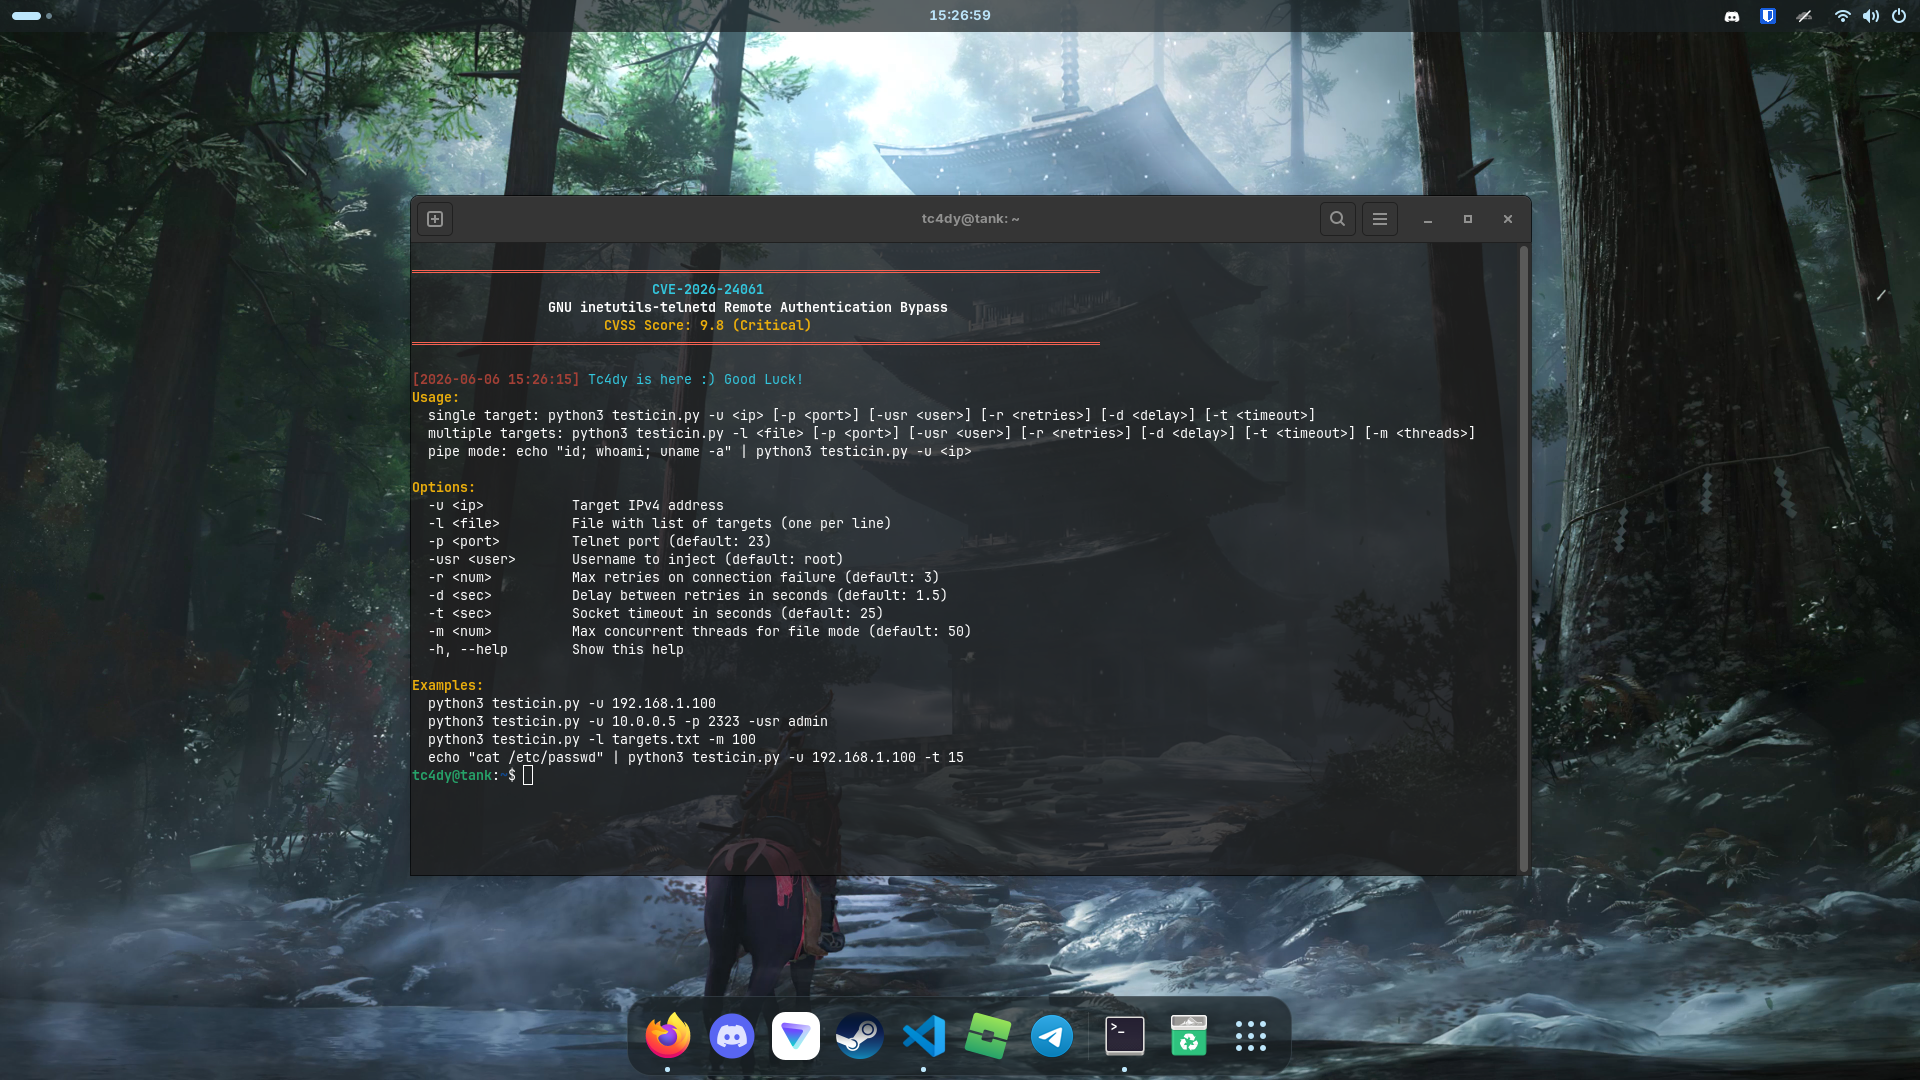
CVE-2026-24061-PoC-Exploit preview

CVE-2026-24061-PoC-Exploit

GitHubtc4dy/cve-2026-24061-poc-exploit

Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…
command-and-controlexploitationpayload-development+3
718h 17m ago
CVE-2026-33017 preview

CVE-2026-33017

GitHubdynamo2k1/cve-2026-33017

PoC exploit for CVE-2026-33017: unauthenticated remote code execution in Langflow via malicious Python Custom Component injection, with built-in…
command-and-controlexploitationpayload-generation+4
2 months ago
CVE-2022-30190 preview

CVE-2022-30190

GitHubjoshuavanderpoll/cve-2022-30190

Python script generating Microsoft Office documents that exploit CVE-2022-30190 for remote code execution via HTML payloads, supporting custom…

command-and-controlexploitationpayload-generation+2
24 years ago
Previous12…39Next