Rig-Exploit-for-CVE-2018-8174

Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…

Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…

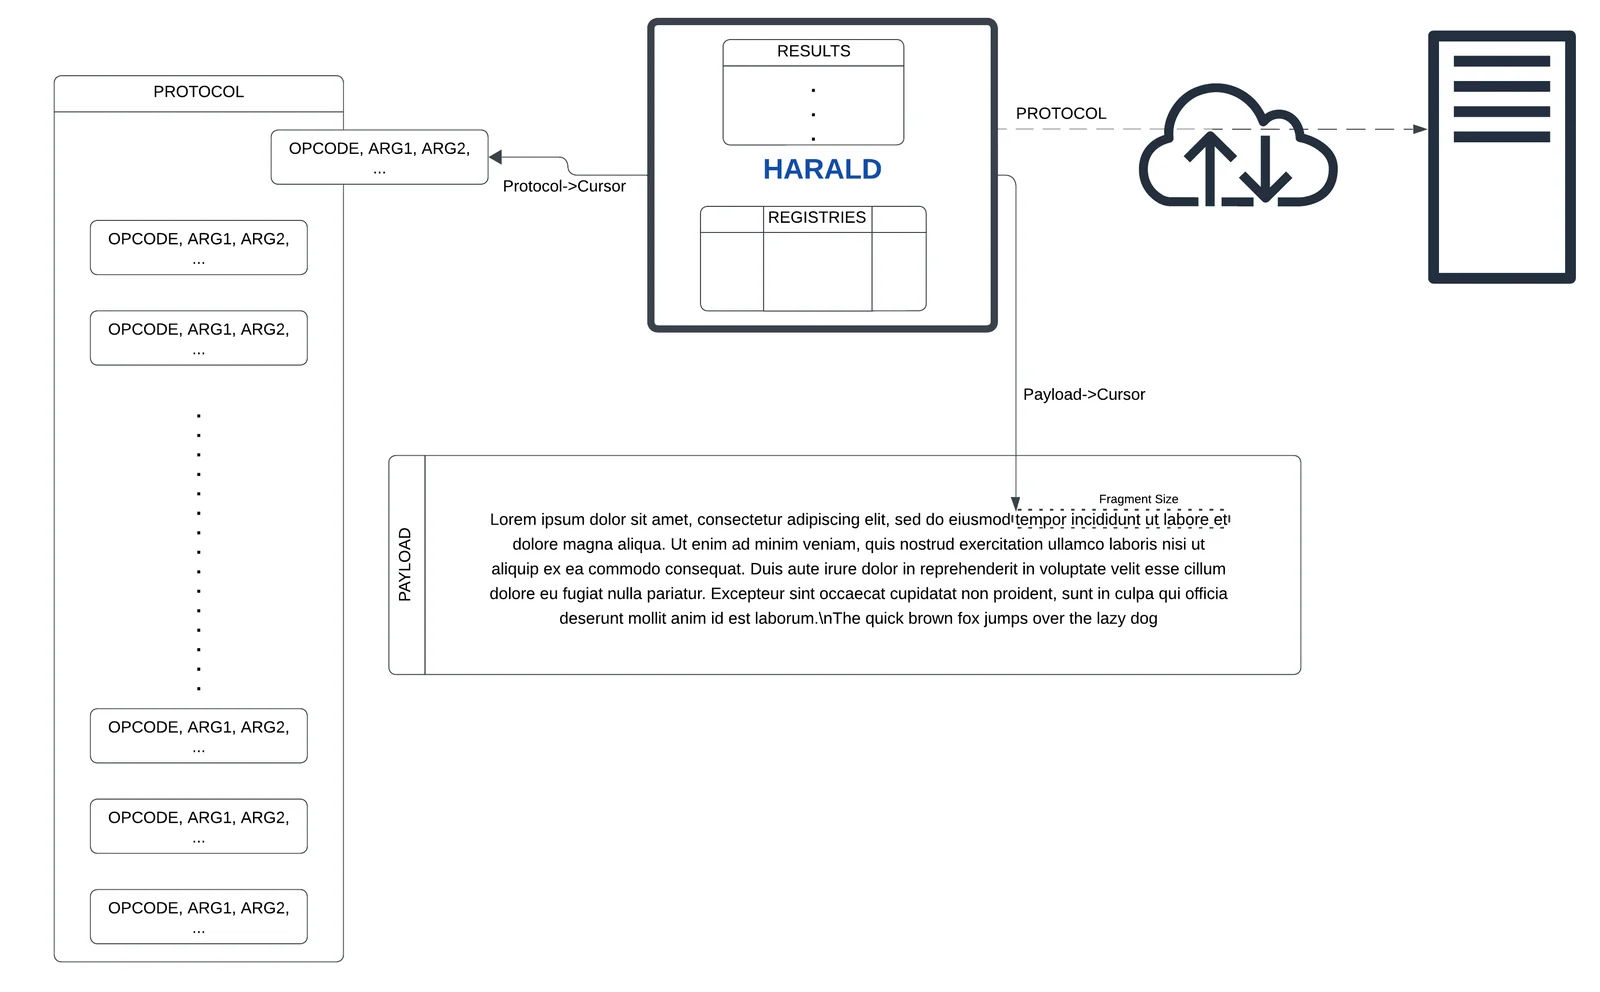
An in-memory minimal CPU for agnostic on-the-fly protocols creation

Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.

Remote Access Trojan(RAT), Miner, DDoS

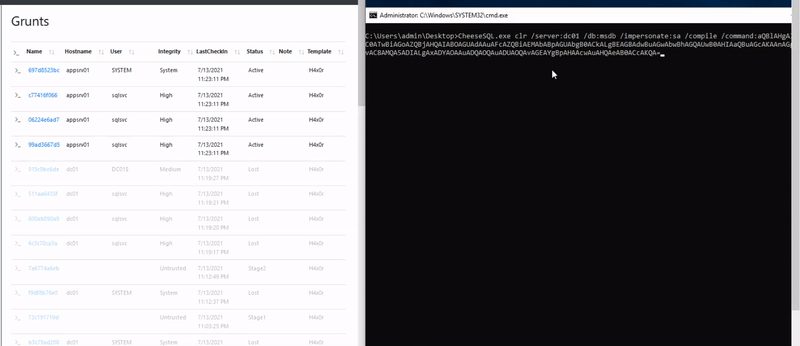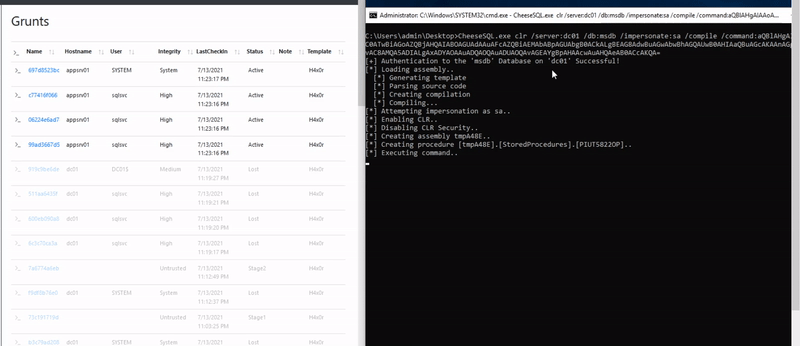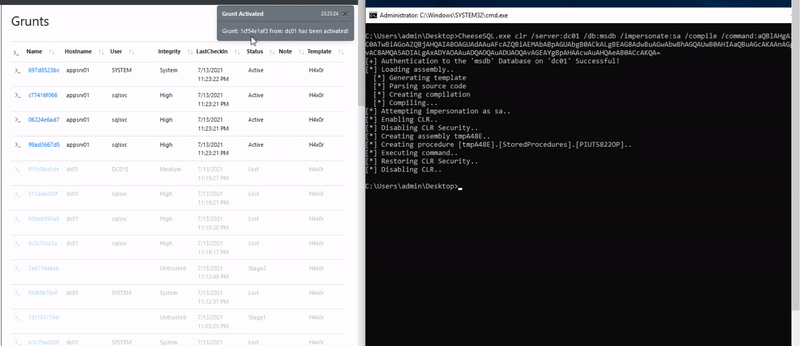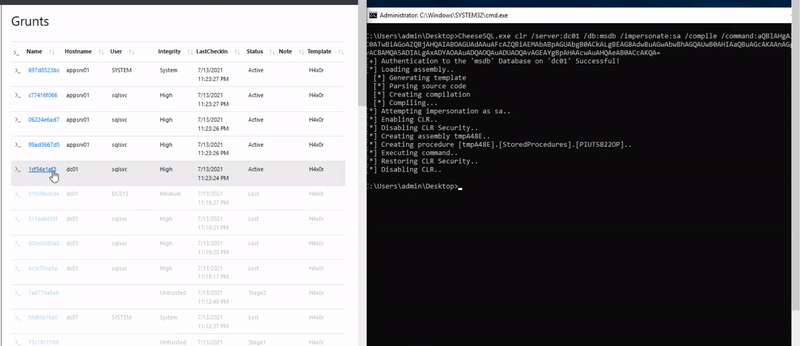
Self-developed tools for Lateral Movement/Code Execution

Arsenal is just a quick inventory and launcher for hacking programs

Checks expired domains for categorization/reputation and Archive.org history to determine good candidates for phishing and C2 domain names

Post-exploitation platform automating enumeration, privilege escalation, persistence, and C2 operations via reverse/bind shells with cross-platform…

Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.

Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…

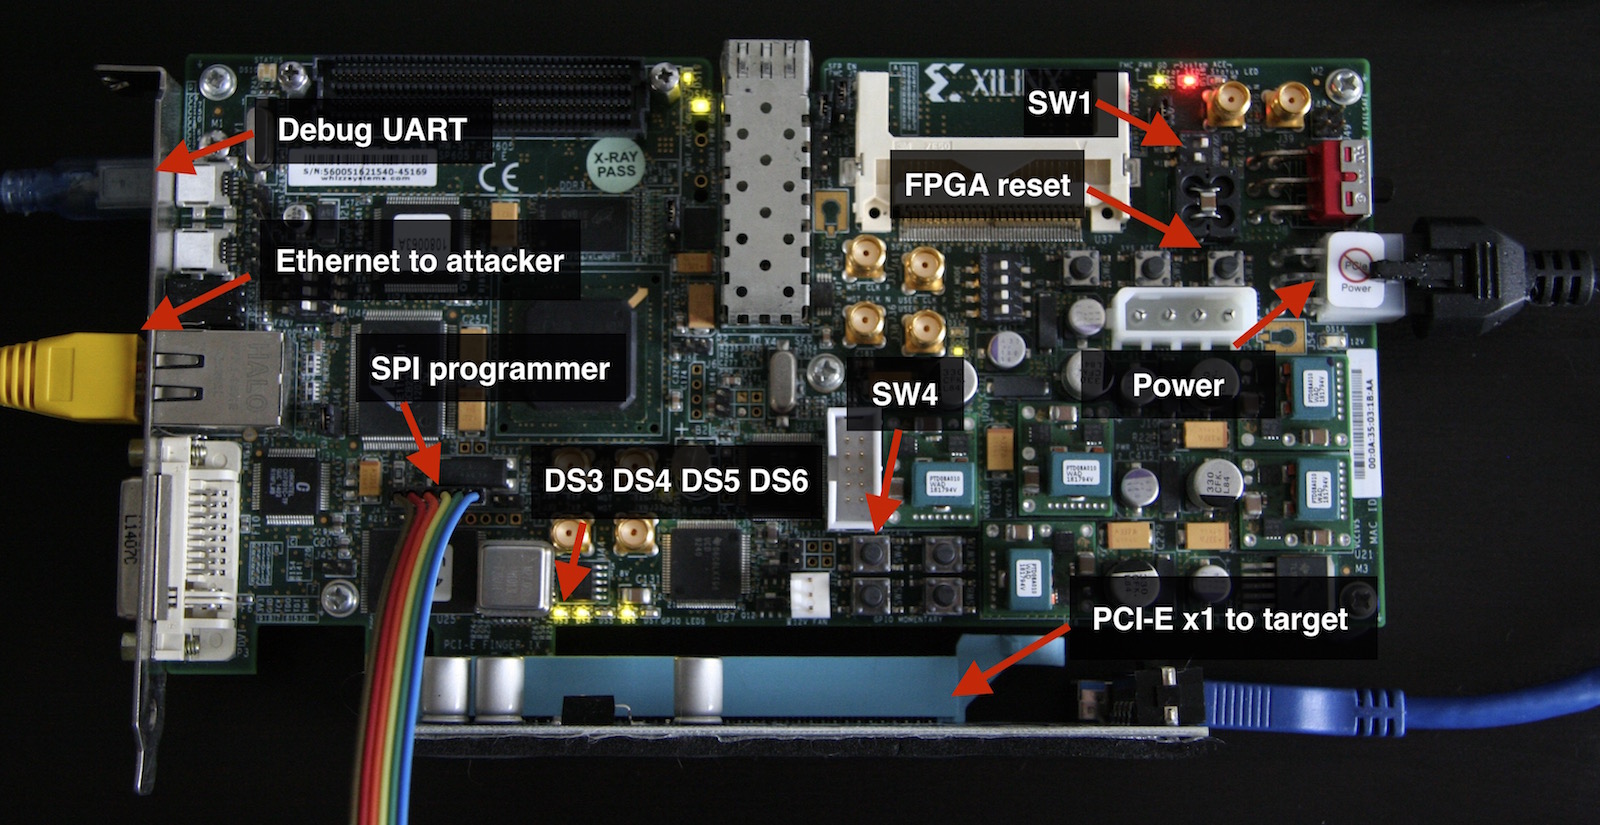
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles

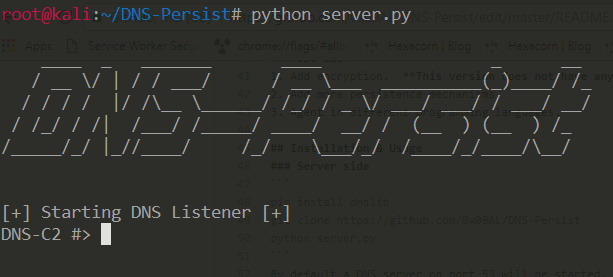
DNS-Persist is a post-exploitation agent which uses DNS for command and control.

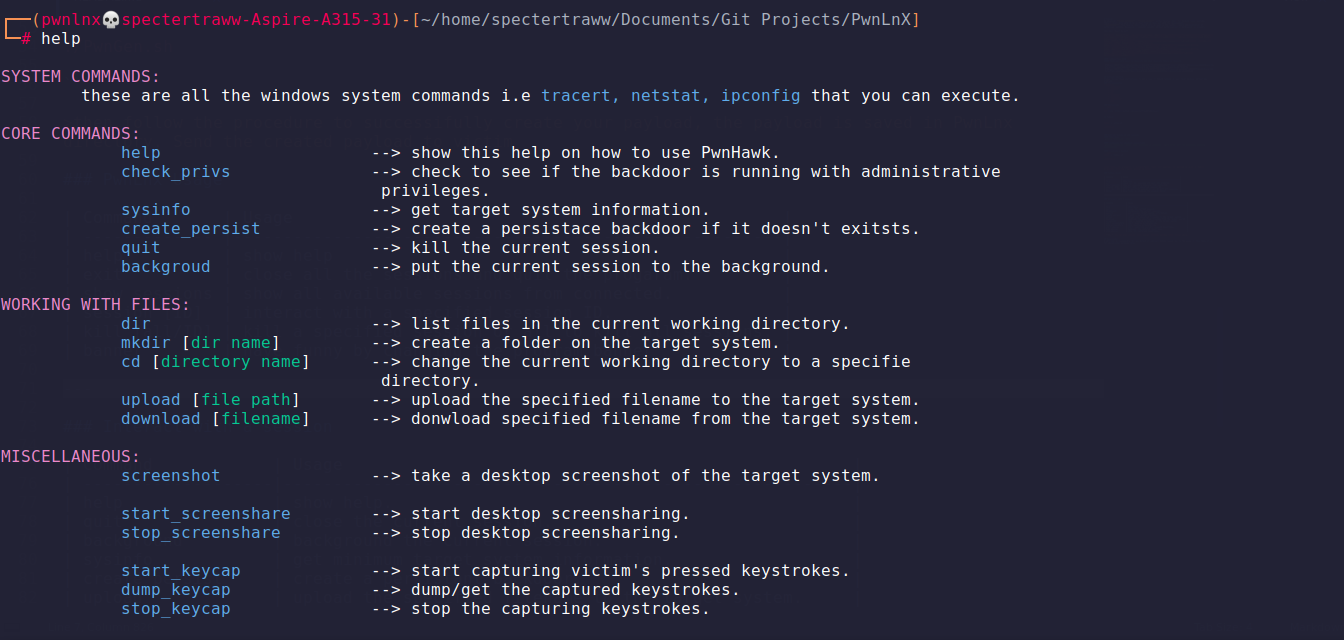
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…

A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models

DropboxC2C is a post-exploitation agent which uses Dropbox Infrastructure for command and control operations.

C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…

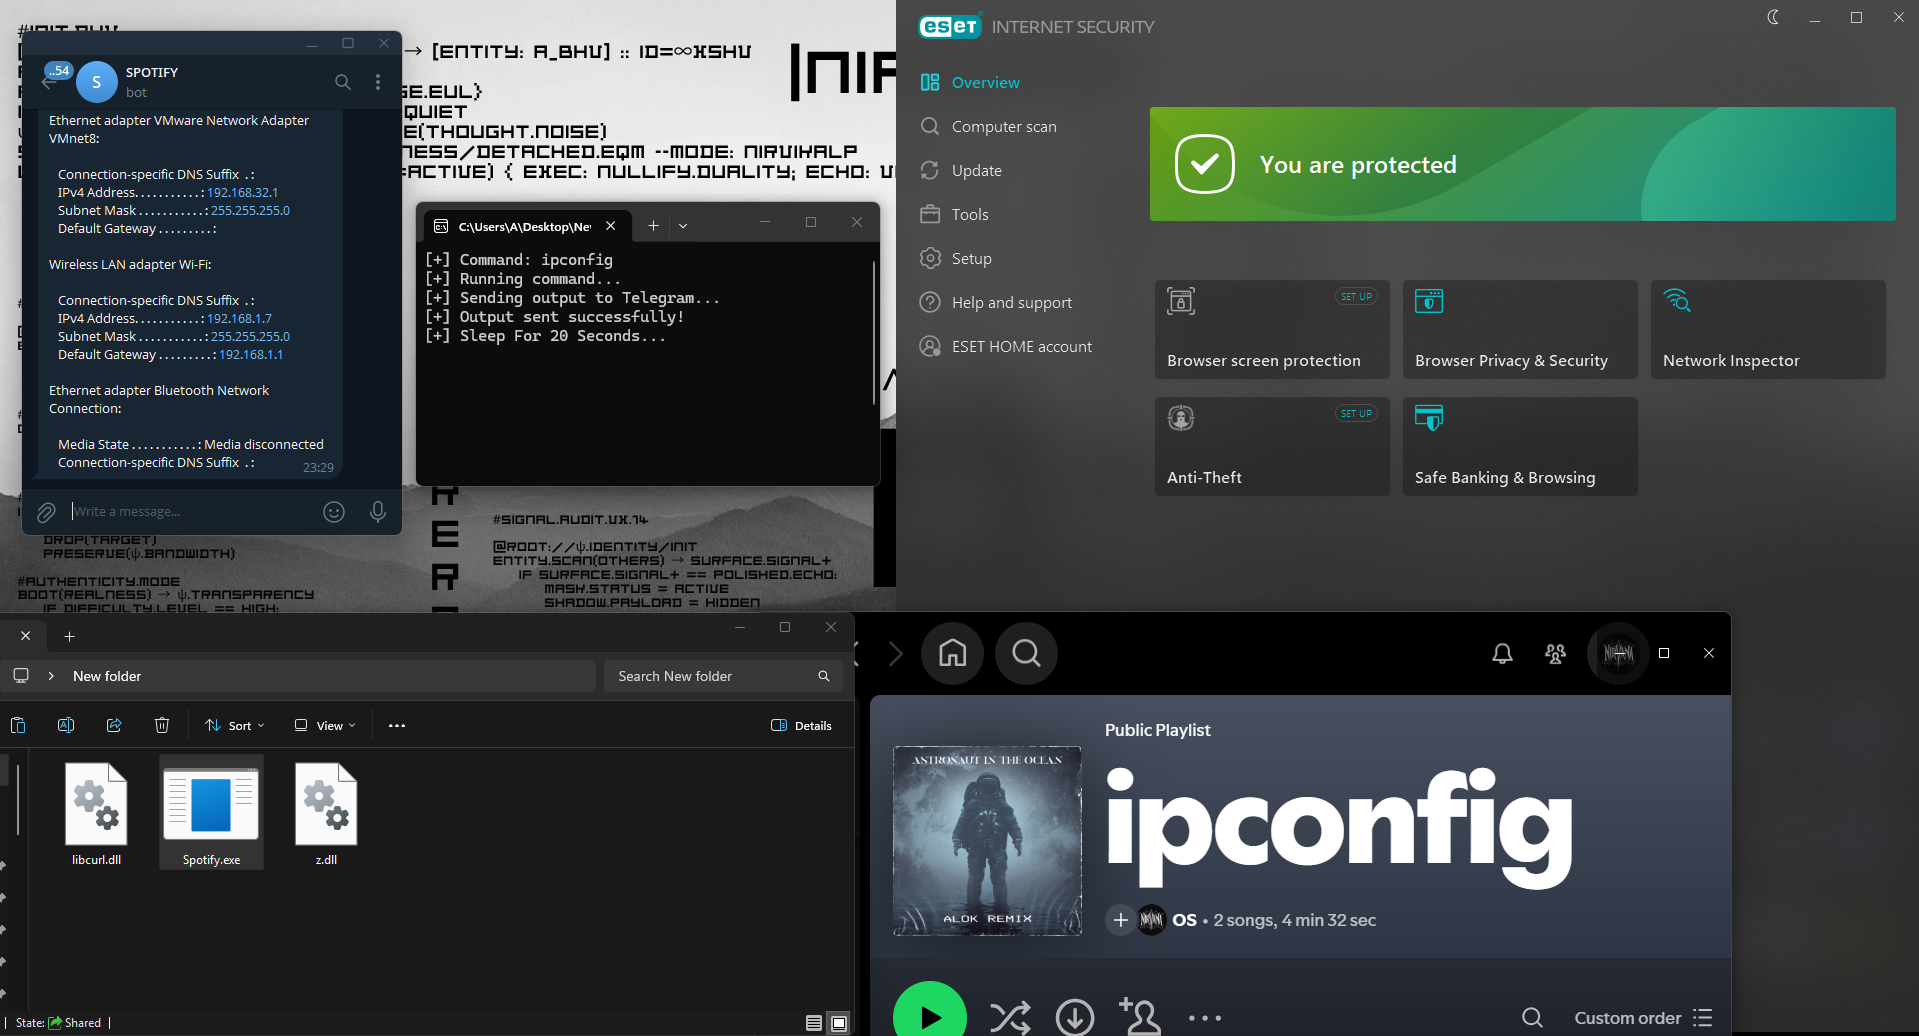
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…