

ProxyLogon-CVE-2021-26855
 mil1200/proxylogon-cve-2021-26855
RCE exploit for ProxyLogon vulnerability in Microsoft Exchange
command-and-controlexploitationpenetration-testing+3
9
mil1200/proxylogon-cve-2021-26855RCE exploit for ProxyLogon vulnerability in Microsoft Exchange
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
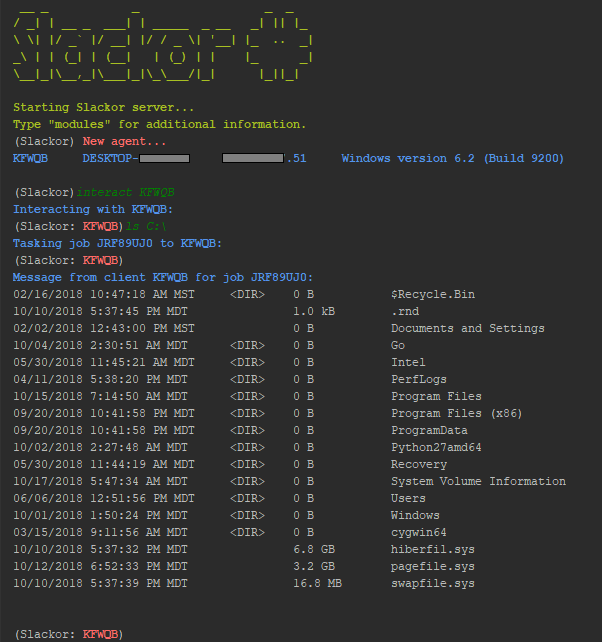 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 fkasler/dolos_cloak
Automated 802.1x Bypass
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
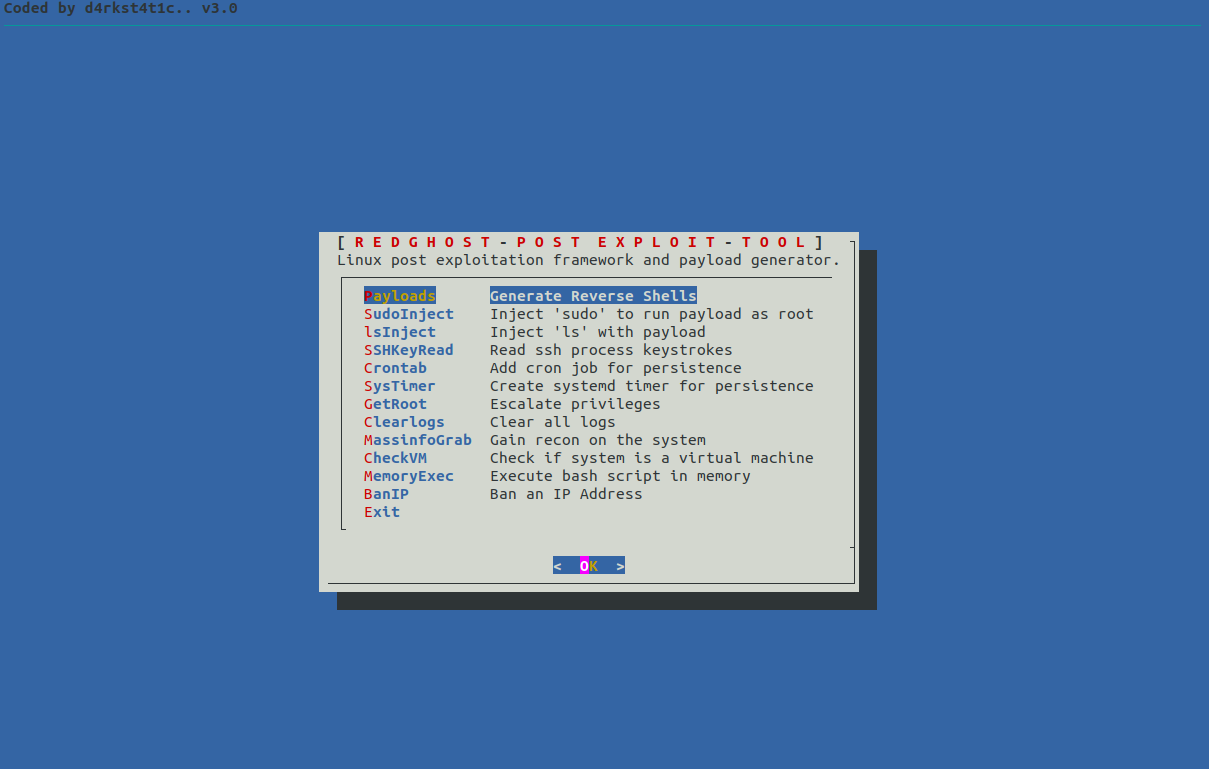 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
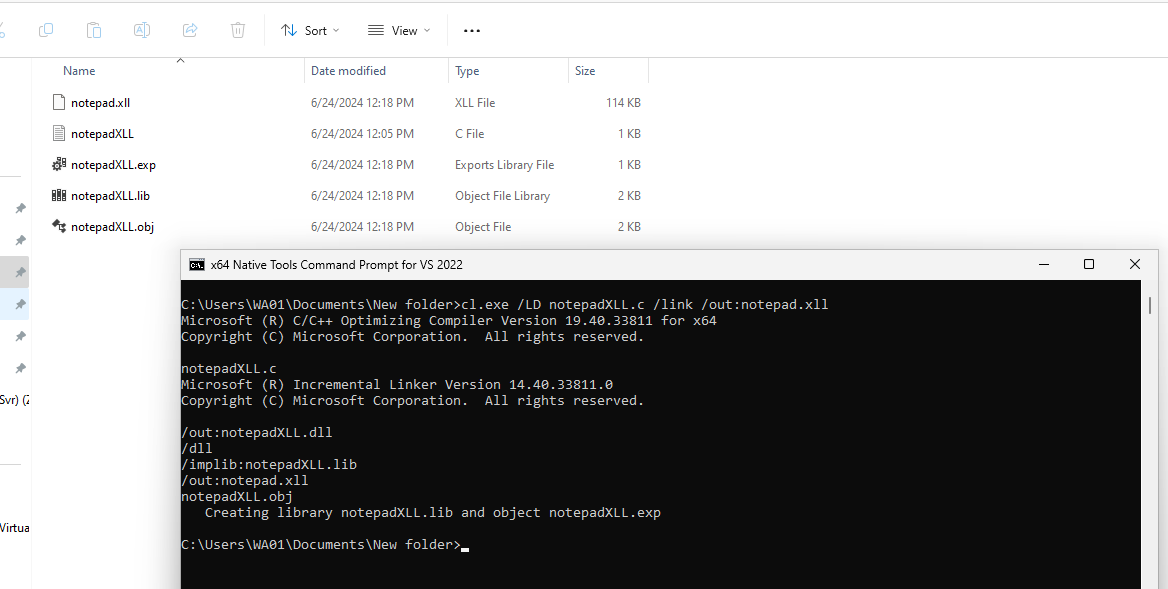 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 0nyx-my7h/cve-2025-43920
PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
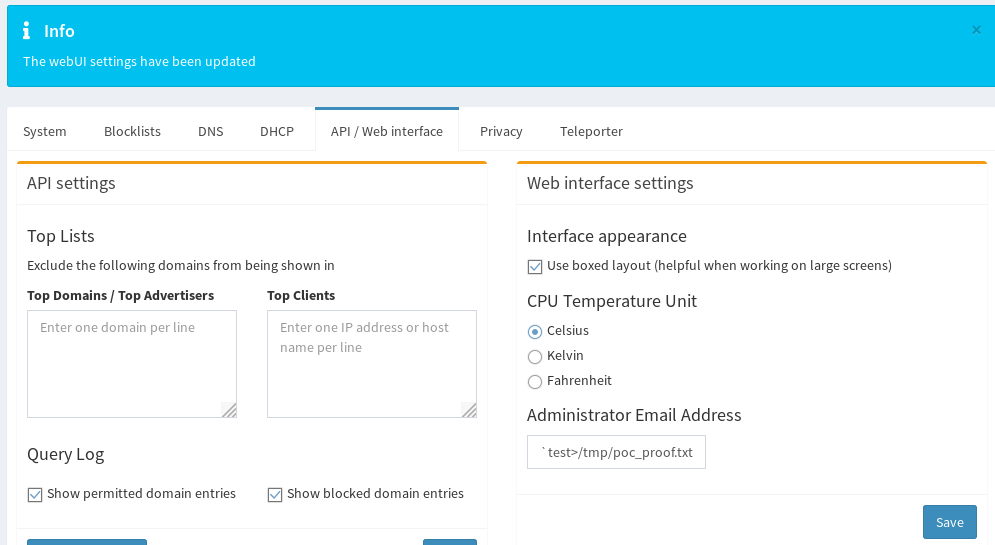 pr0tean/cve-2019-13051
Proof-of-concept exploit for Pi-Hole AdminLTE command injection (CVE-2019-13051) enabling remote root access via email field injection and cron-based…
 noraj/atmail-exploit-toolchain
AtMail Email Server Appliance 6.4 - Exploit toolchain (XSS > CSRF > RCE)
 ly1g3/proofpoint-cve-2023-0089
Proofpoint Email Gateway: Low level authenticated user to admin RCE
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.