CVE-2025-20029-simulation
 schoi1337/cve-2025-20029-simulation
Simulated environment for CVE-2025-20029 using Docker. Includes PoC and auto-reporting.
command-and-controleducationlabs-practice+3
3
schoi1337/cve-2025-20029-simulationSimulated environment for CVE-2025-20029 using Docker. Includes PoC and auto-reporting.
 jstjep00/cve-2023-22496-poc
PoC for CVE-2023-22496: Netdata Agent <1.37 OS Command Injection via registry_hostname

 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
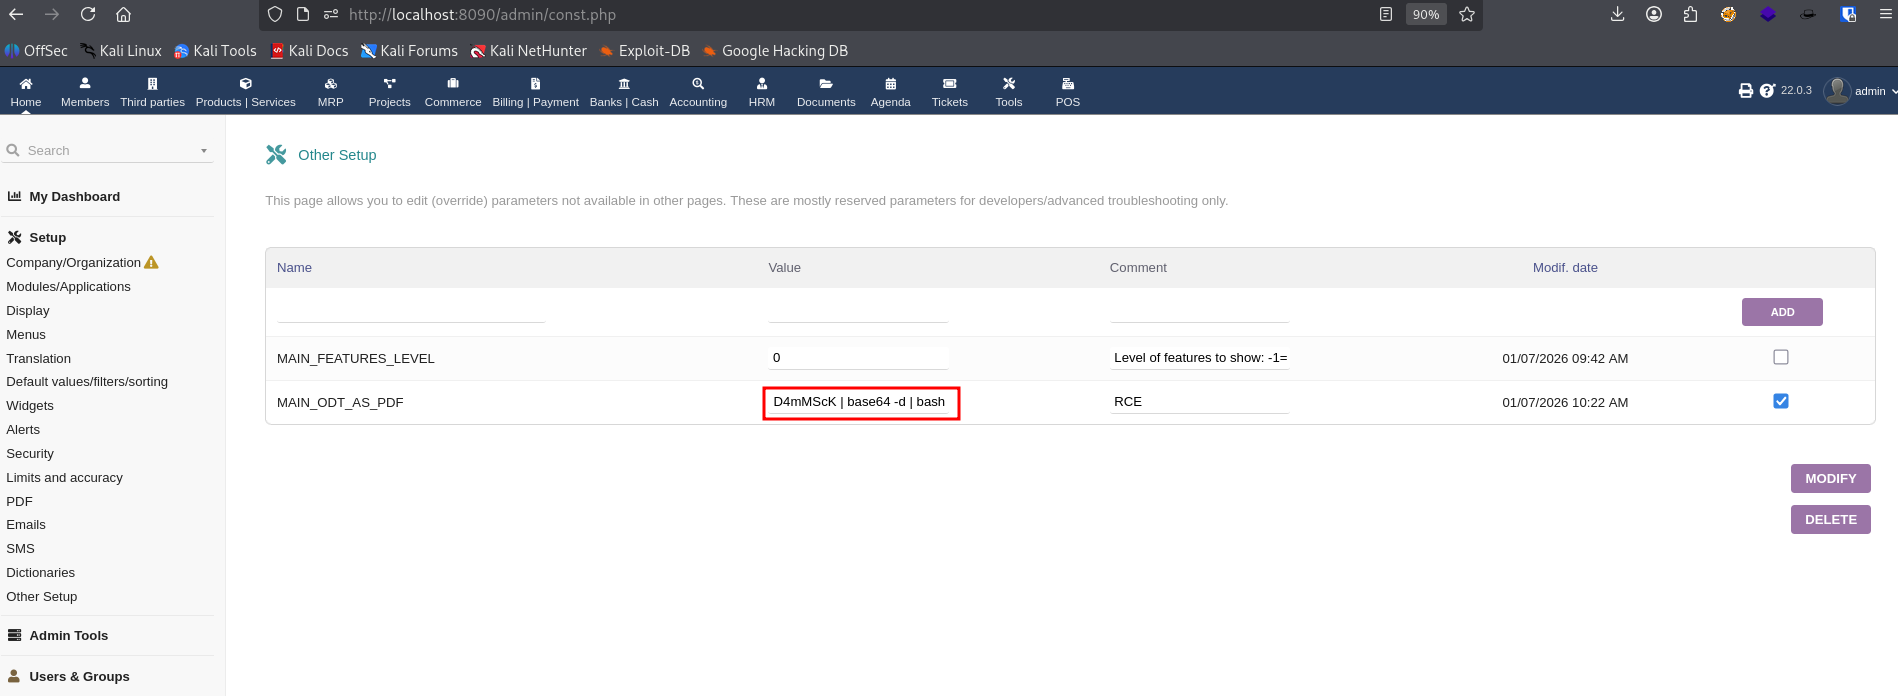 lukasz-rybak/cve-2026-23500
CVE-2026-23500 - OS Command Injection (RCE) via MAIN_ODT_AS_PDF configuration in Dolibarr
 daviddoctor/samba-cve-2007-2447-exploit-username-map-script
Samba CVE-2007-2447 Exploit
 davidzzo23/cve-2025-54123
Python exploit script for CVE-2025-54123 targeting Hoverfly RCE with command execution and reverse shell capabilities for authorized security testing.
 0x00phantom-hat/hoverfly-1.11.3-rce-cve-2025-54123-exploit
Exploit for CVE-2025-54123, an authenticated OS command injection in Hoverfly's middleware API, providing check-only, single-command, interactive…
 abhayclasher/cve-2026-39866
Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…

 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 askhatov21/best-practices-cybersecurity-otanata-project
CVE-2024-3273 — Authorized Penetration Test Report D-Link DNS-320L NAS | Client: Otonata
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 bixipro/drupalgeddon2-cve-2018-7600
Python exploit for CVE-2018-7600 (Drupalgeddon 2) enabling remote code execution on Drupal 7 with multiple injection methods and predefined commands…
 atastycookie/cve-2025-55182
Python CLI exploit and scanner for CVE-2025-55182, a critical RCE in React Server Components, with command execution and nuclei-based detection.
 fevar54/cve-2026-20245---cisco-sd-wan-privilege-escalation-exploit
**Este código es SOLO para fines educativos y pruebas de seguridad autorizadas.**