APT-Individual-Combat-Guide

Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

Simple PoC Python agent to showcase Havoc C2's custom agent interface. Not operationally safe or stable. Released with accompanying blog post as a…

Removed according to regulations

Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…

Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…

Proof-of-concept exploit for CVE-2023-34992 enabling unauthenticated blind command injection as root on vulnerable Fortinet FortiSIEM appliances.

Exploit for CVE-2022–25765 (pdfkit) - Command Injection

simple c2 written in python to demonstrate security concepts

Android remote administration client

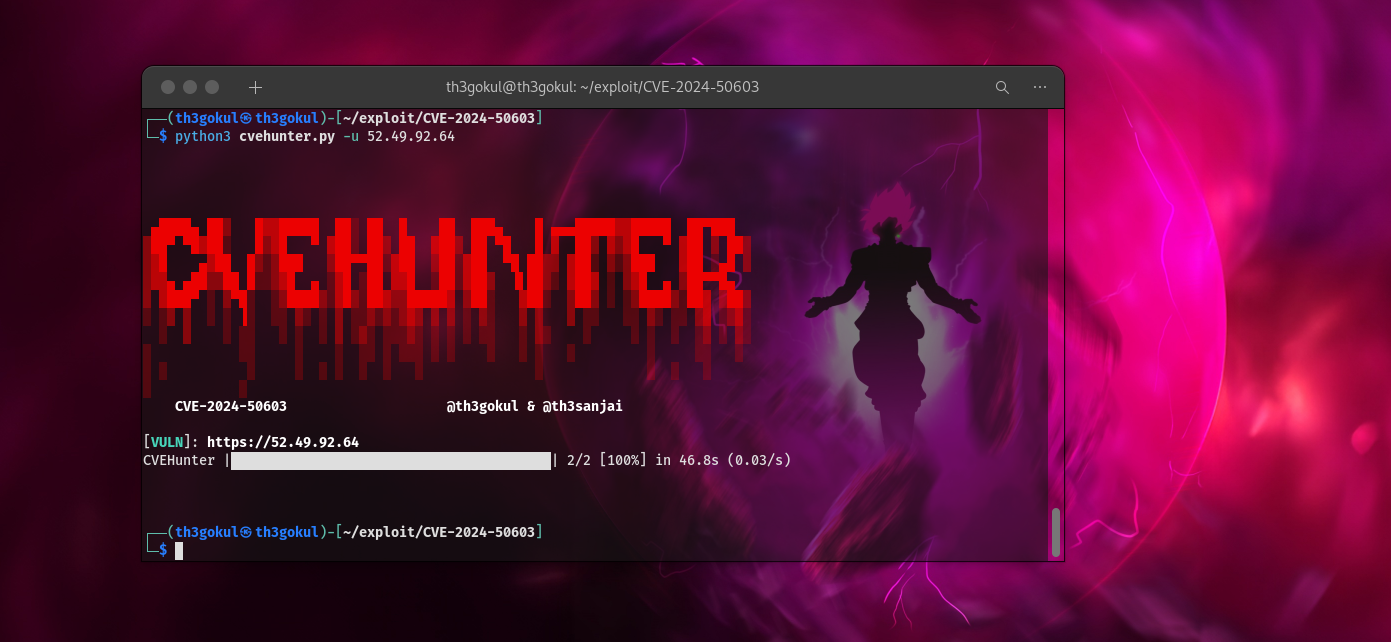
CVE-2024-50603: Aviatrix Controller Unauthenticated Command Injection

Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…

Python-based exploit generator for CVE-2021-40444 (MSHTML RCE) with template-driven payload delivery via malicious Office documents, CAB archives,…

CVE-2024-10914 is a critical command injection vulnerability affecting several legacy D-Link Network Attached Storage (NAS) devices.

CVE-2025-55182 React2Shell PoC - Critical RCE in React Server Components / Next.js. CVSS 10.0. Error-based exfil, reverse shell, interactive mode.

FreeBSD rtsold DNSSL Command Injection (RCE)

apache路径穿越漏洞poc&exp