
CVE-2026-118238
 cushz/cve-2026-118238
Proof-of-concept for unauthenticated root OS command injection in the Tenda W18E AP httpd diagnose module, with a self-verifying exploit script and…
command-and-controlembedded-systems-securityexploitation+5
1
cushz/cve-2026-118238Proof-of-concept for unauthenticated root OS command injection in the Tenda W18E AP httpd diagnose module, with a self-verifying exploit script and…
 frostb1ten/cve-2024-24576-poc
Example of CVE-2024-24576 use case.
 daemoncibsec/mcpexec
POC for CVE-2026-23744 for a python revshell
 j-baines/tippa-my-tongue
F5 BIG-IP Exploit Using CVE-2022-1388 and CVE-2022-41800
 yassinebk/cve-2022-46169
CVE-2022-46169
 mbadanoiu/java-servlets-shell
JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz
 amoloht/cve-2022-33891
「💥」CVE-2022-33891 - Apache Spark Command Injection
 shamo0/cve-2022-1388
BIG-IP iControl REST vulnerability CVE-2022-1388 PoC
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 eatonchips/wsh
Web shell generator and command line interface.
 golden-secure/cve-2025-55182
Interactive RCE Web Shell (CVE-2025-55182) BY Golden-Security
 cyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
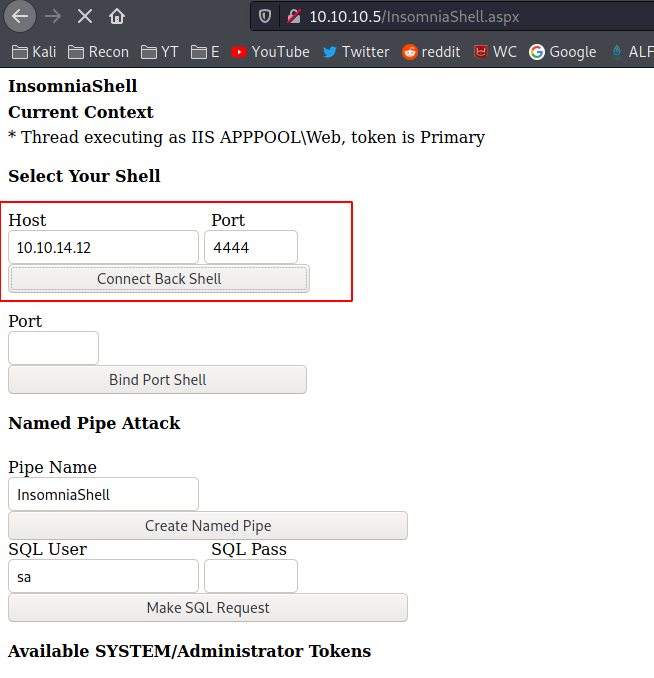 h3x0v3rl0rd/insomniashell
ASP.NET-based web shell for remote command execution and post-exploitation on Windows servers.
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
 sanan2004/cve-2018-17431-comodo
Comodo
 th3gl0w/cve-2025-24893-poc
Exploit for CVE-2025-24893 enabling remote command execution and reverse shell on vulnerable web applications. Includes CLI options for targeting…
 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
 ungabunga-ctf/cve-2023-26039
CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.