
XeytanWin32-RAT
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
207 years ago
melardev/xeytanwin32-ratWORK IN PROGRESS. RAT written in C++ using Win32 API
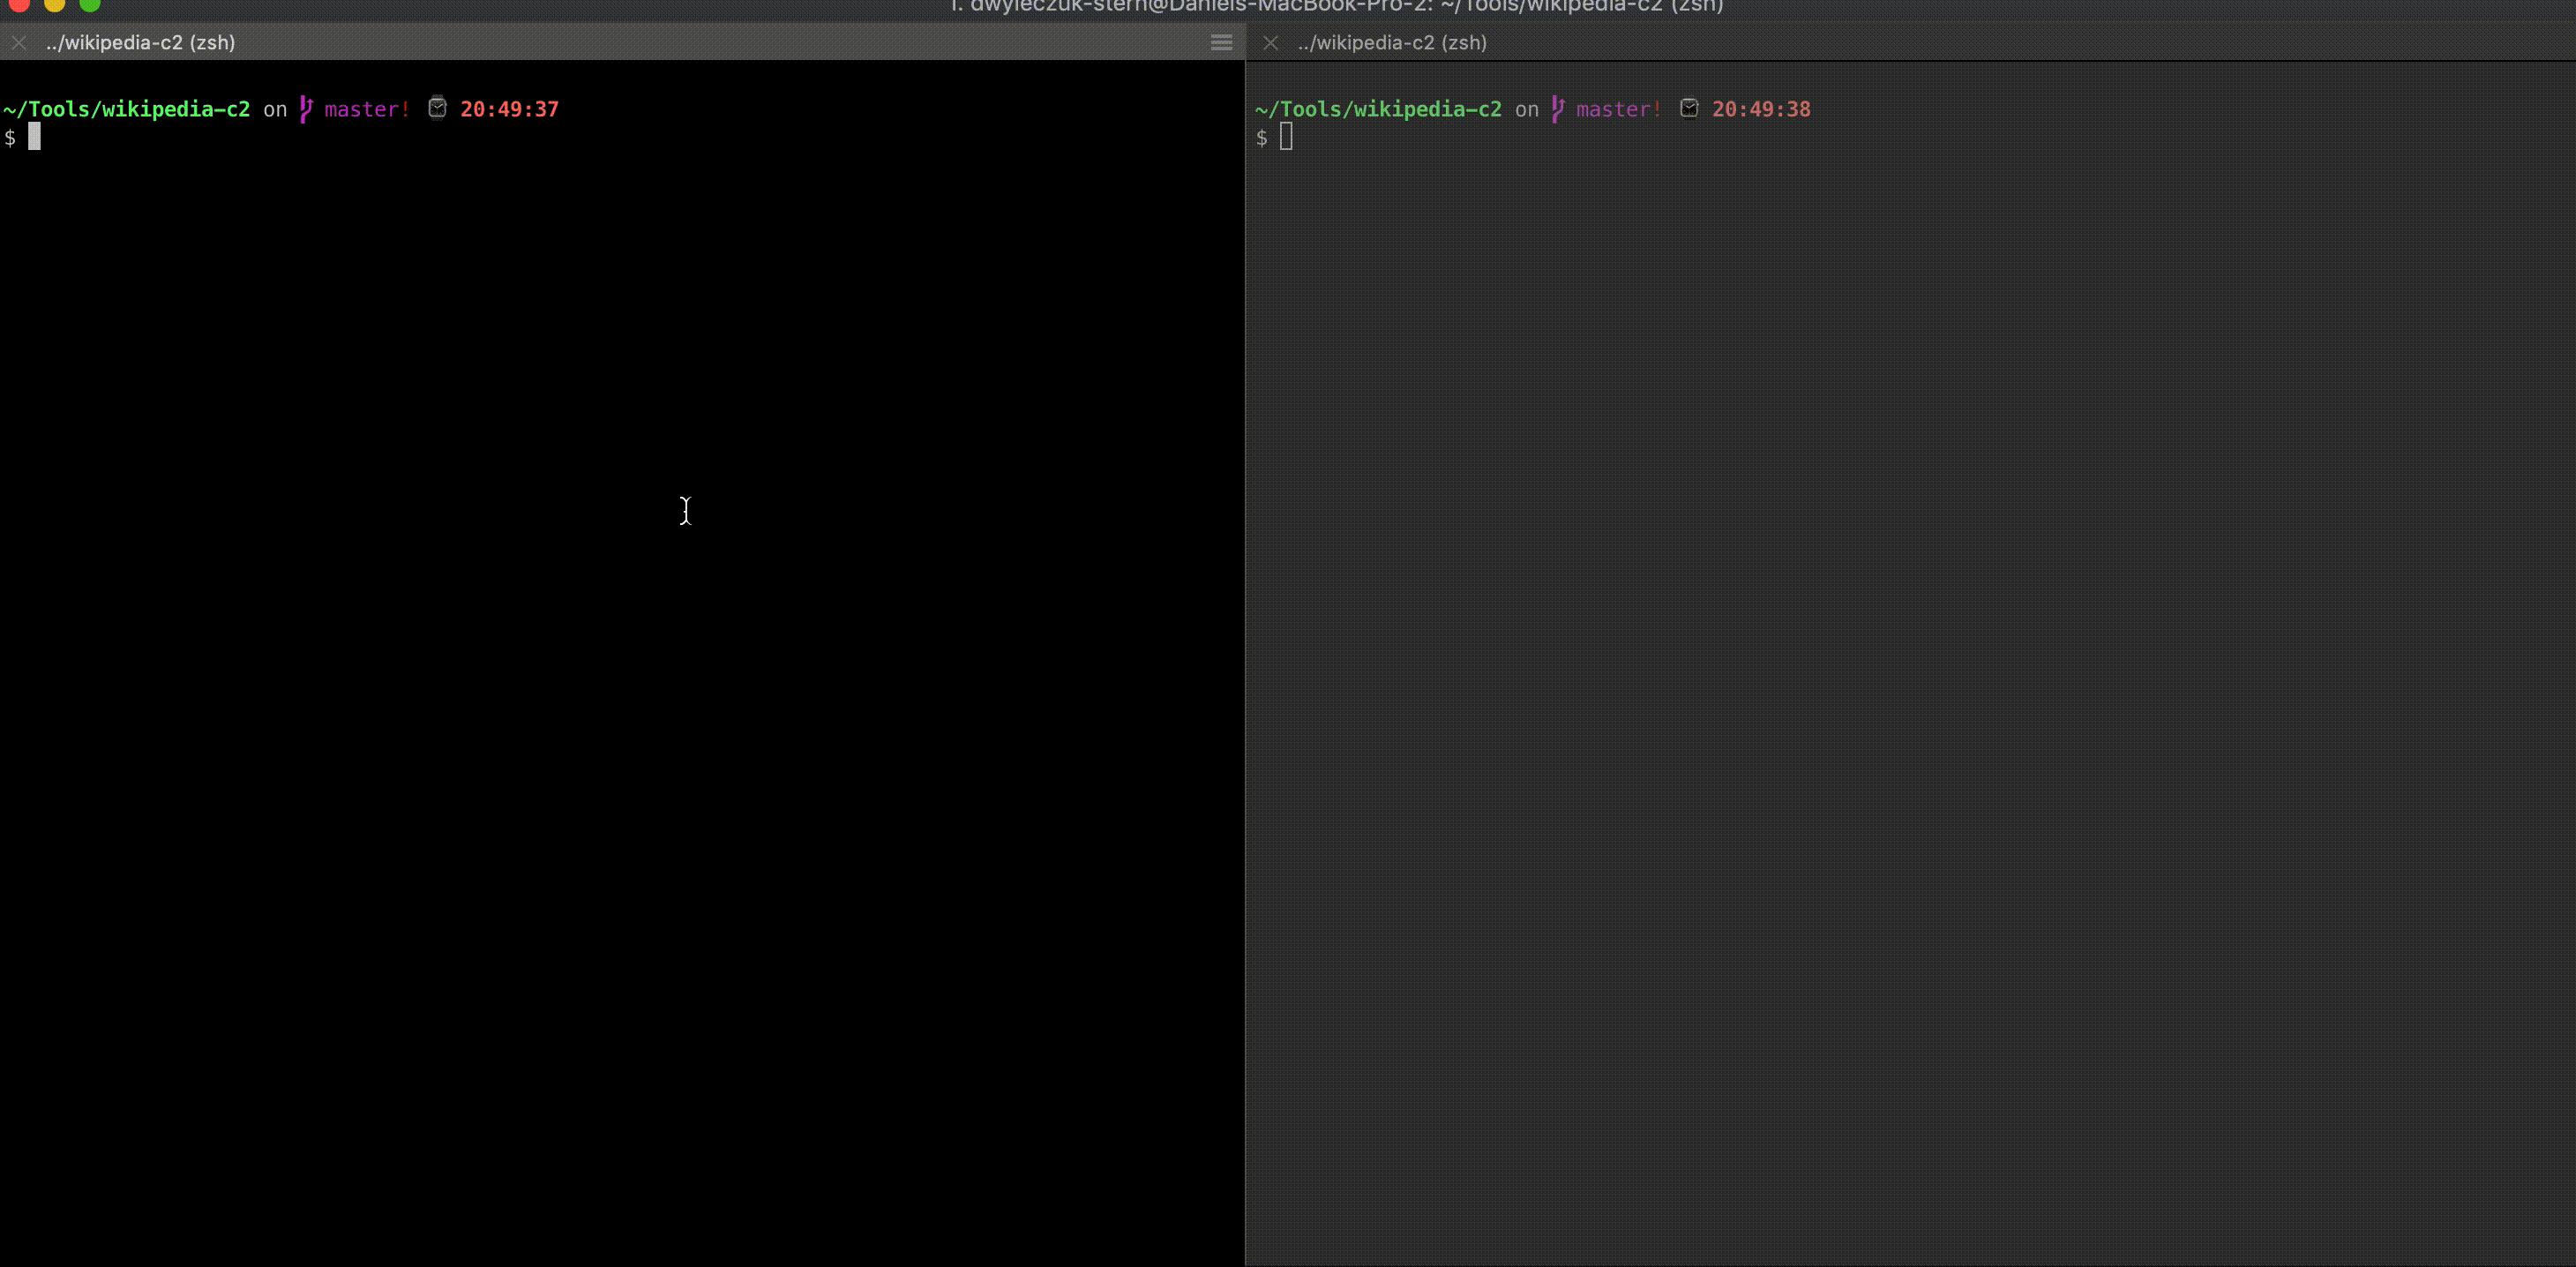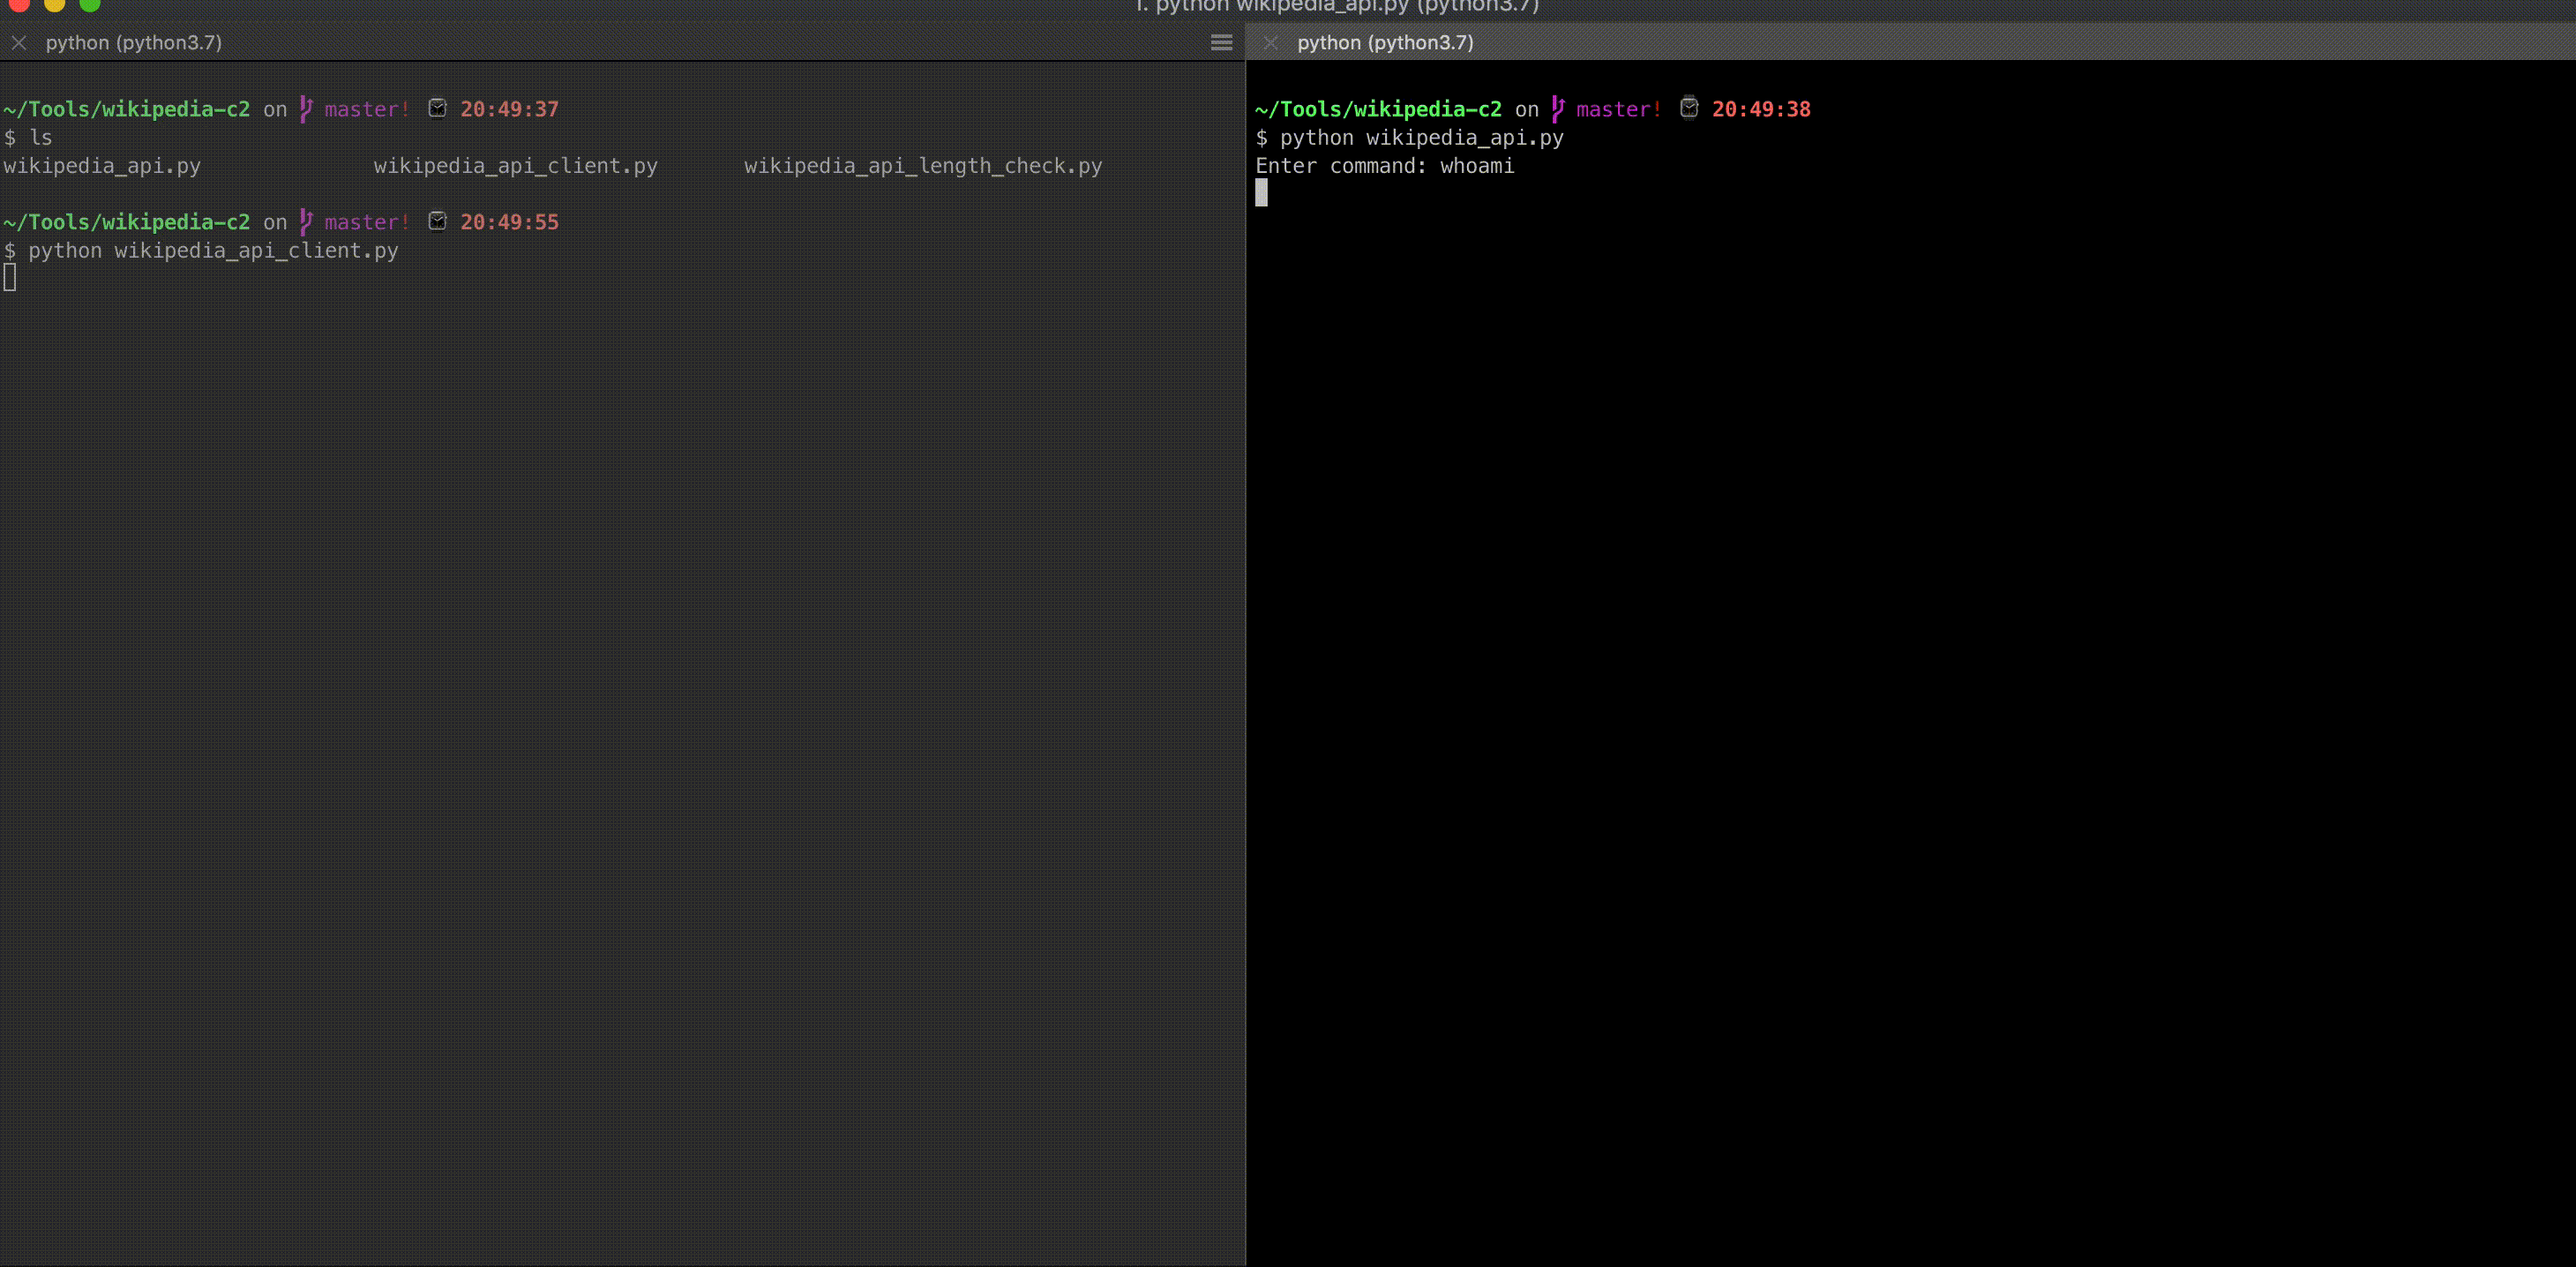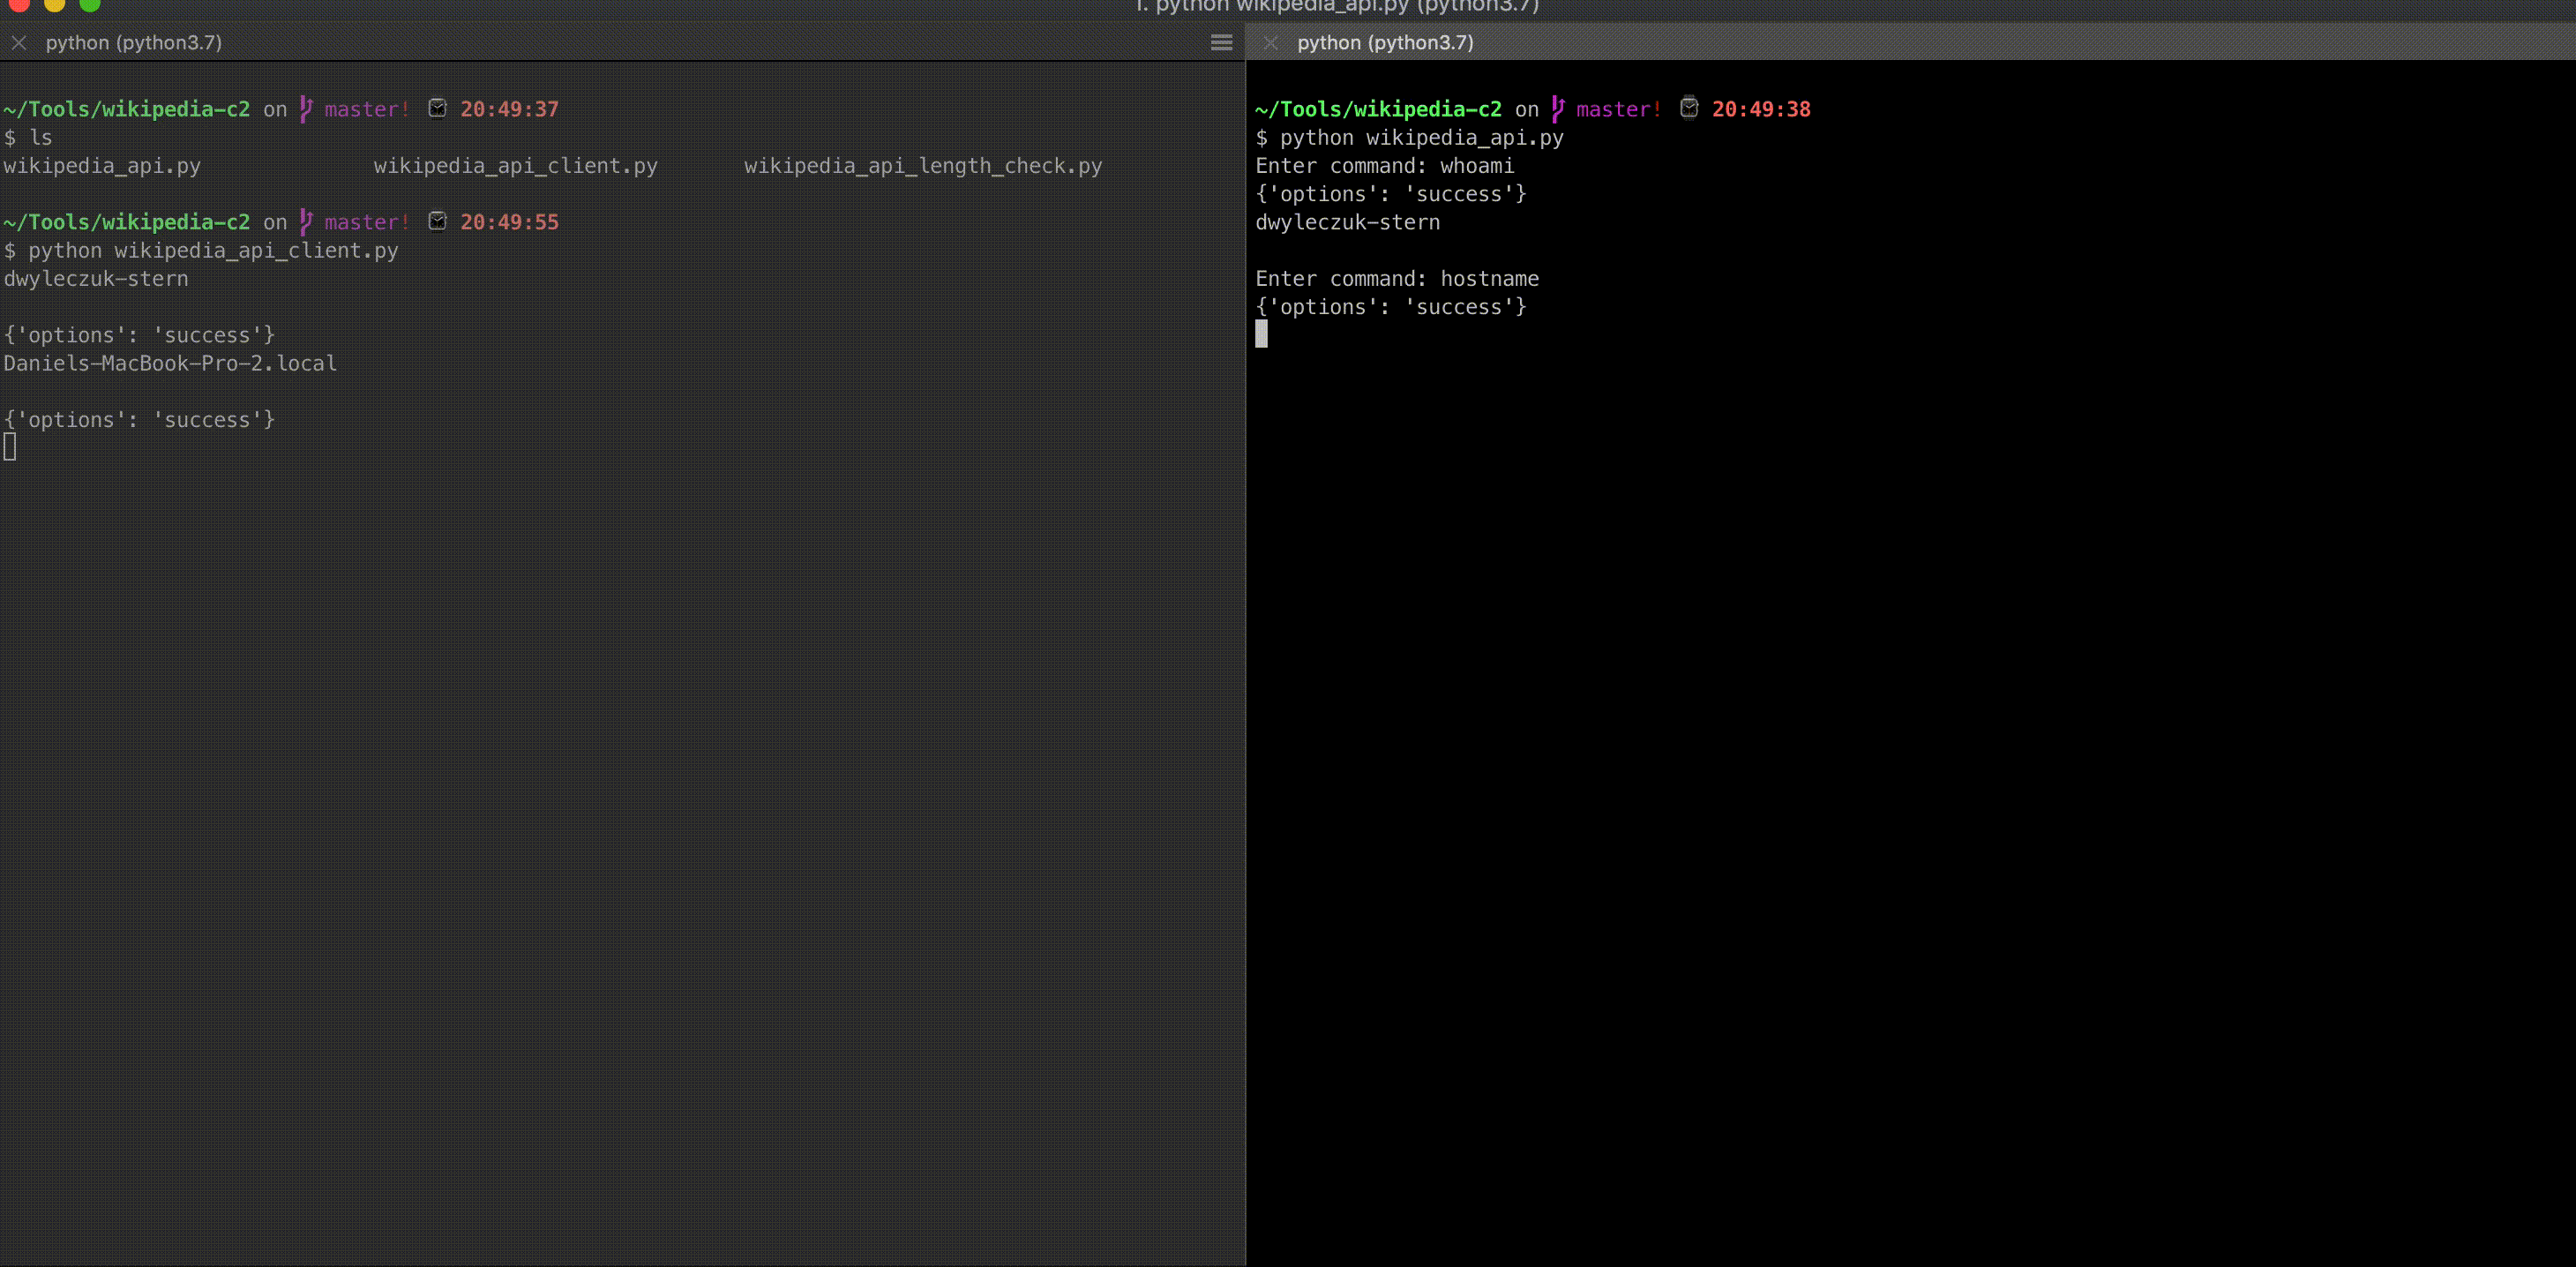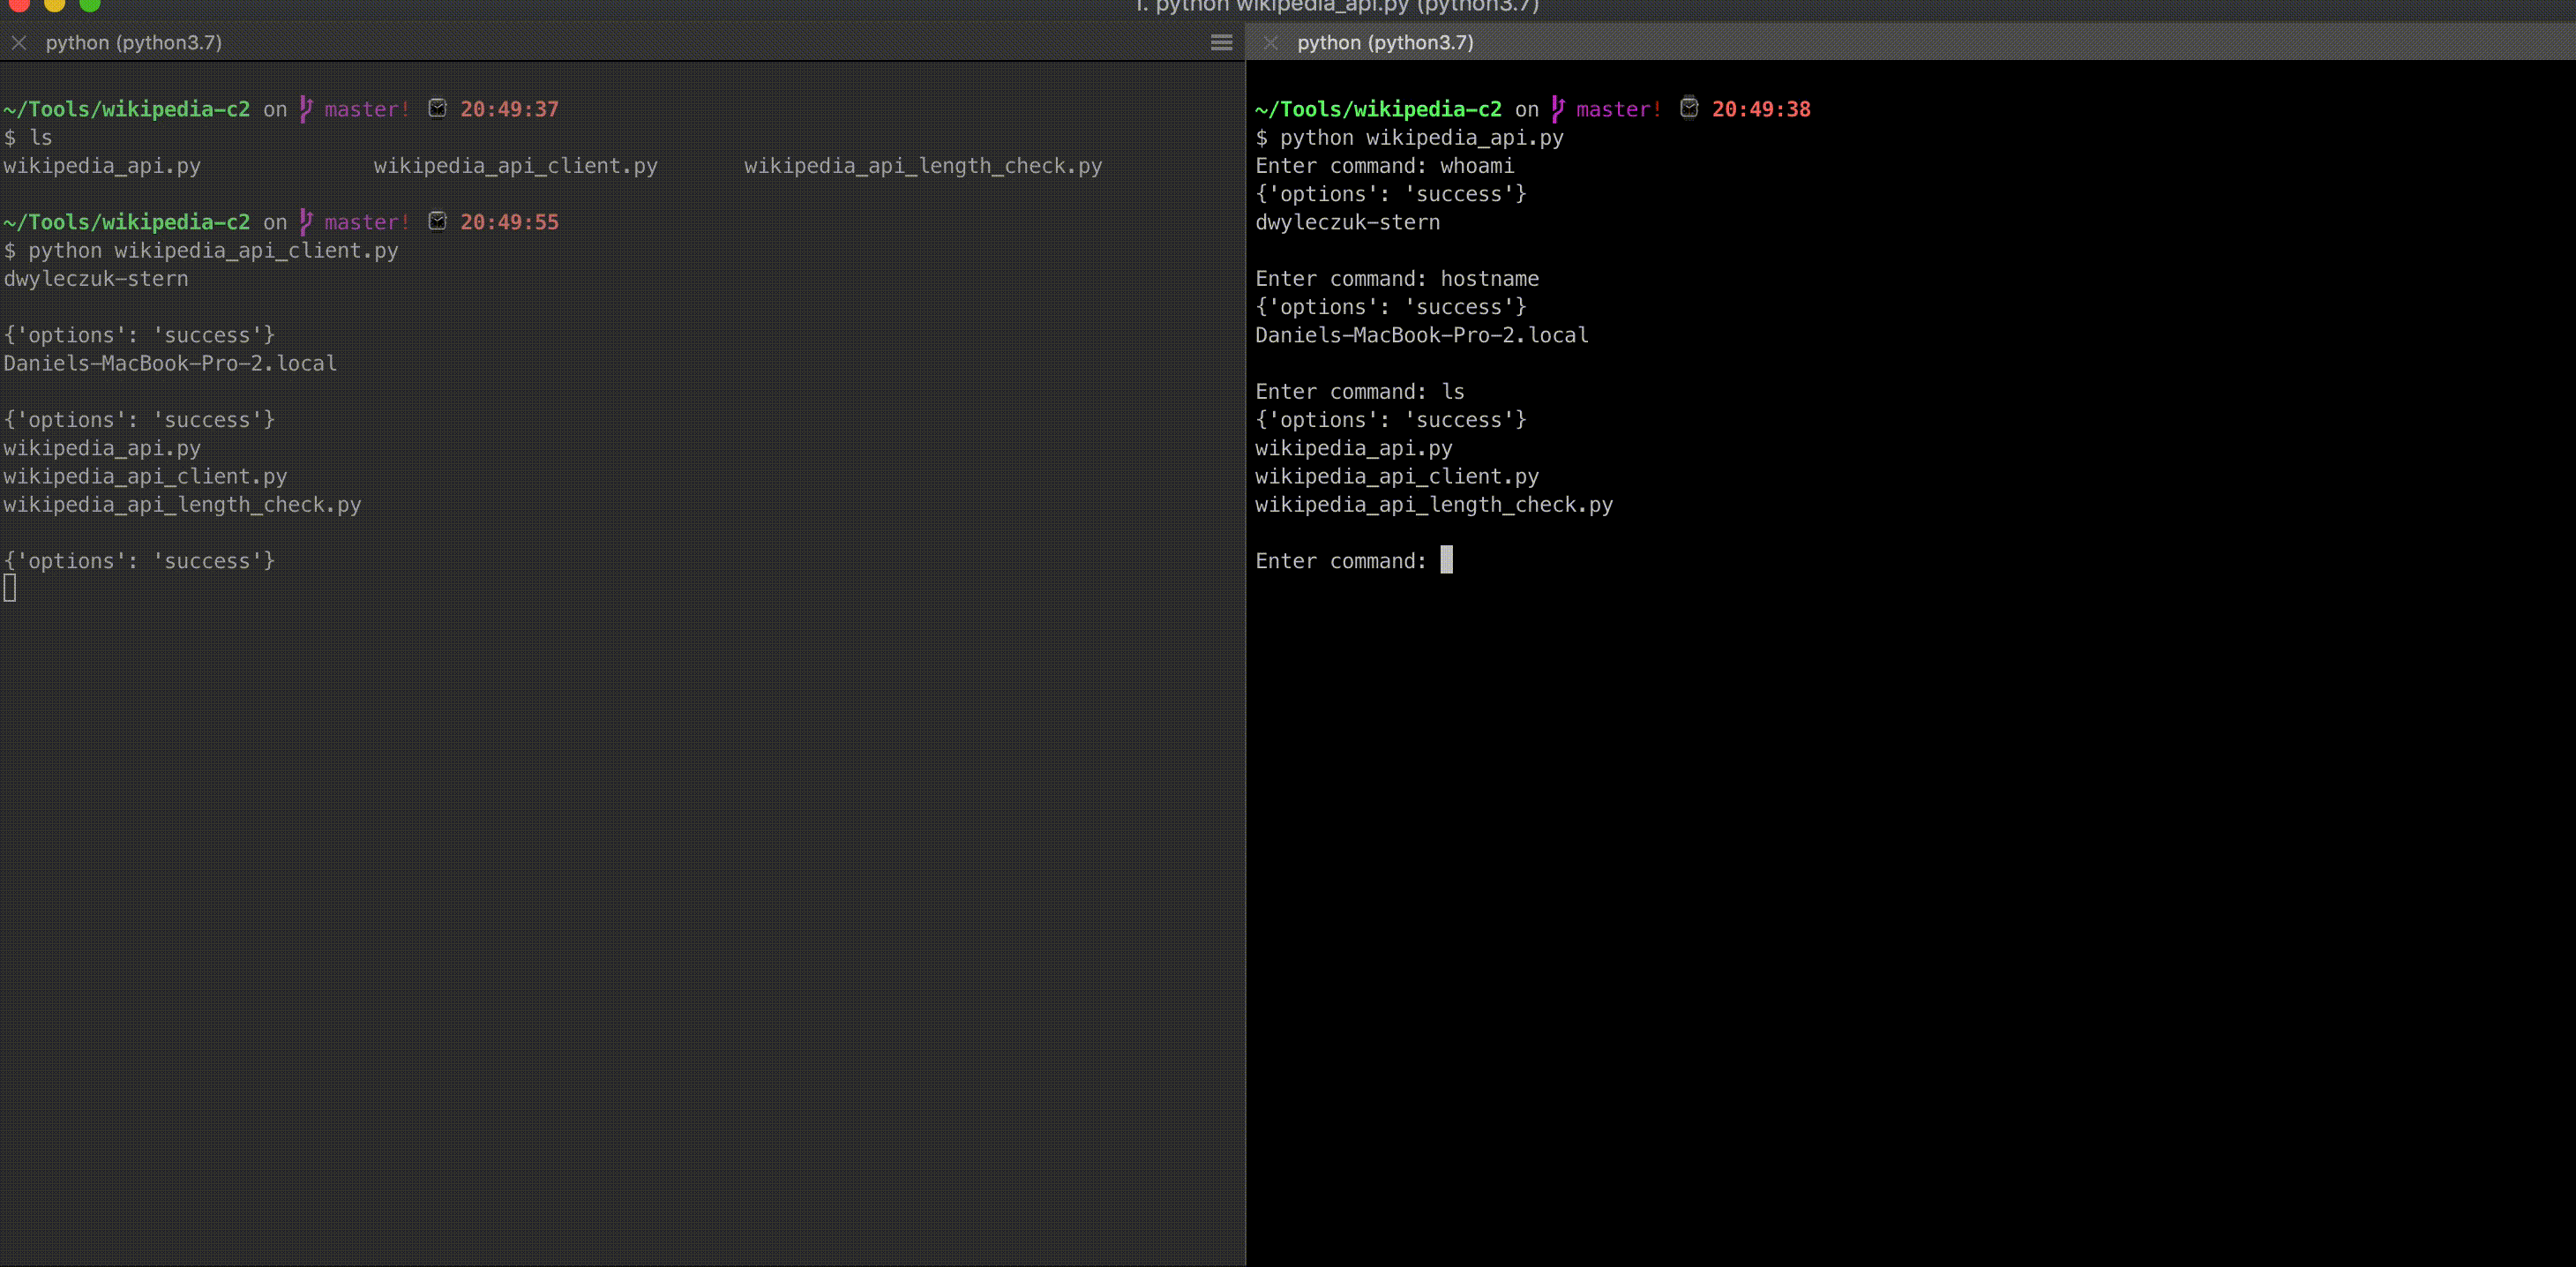 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
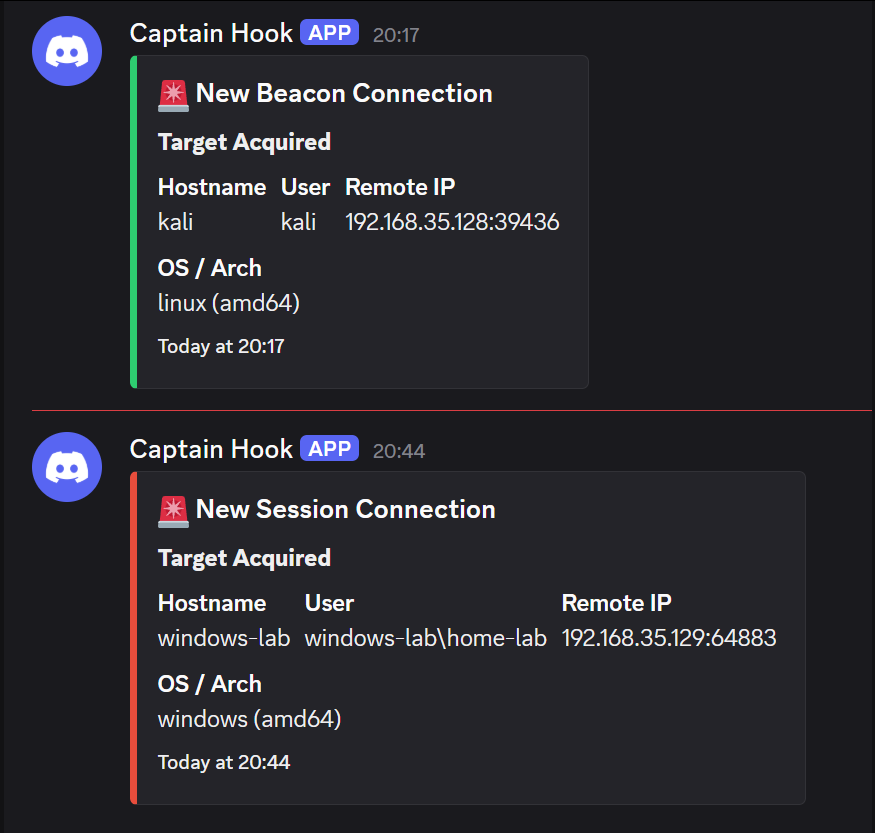 0x0trace/sliver-n8n-notifications
Real-time notification system for Sliver C2 implant callbacks, integrating n8n workflows to deliver color-coded alerts to Discord and Slack with…
 diemoeve/cve-2024-41570
Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 kra1t0/cve-2025-33053-webdav-rce-poc-and-c2-concept
Proof-of-Concept for CVE-2025-33053 Exploiting WebDAV with .url file delivery to demonstrate realistic remote code execution. Includes a decoy PDF…

 cyberbelly/poc-cve-2019-1003030
PoC for jenkins 2.63 CVE-2019-1003030

 th3gl0w/cve-2025-24893-poc
Exploit for CVE-2025-24893 enabling remote command execution and reverse shell on vulnerable web applications. Includes CLI options for targeting…